

MicroTrick
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
authenticationembedded-systems-securityexploitation+7
digiprosec/microtrickSelf-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 ivanesk315/cve-2026-53519
Docker lab reproducing CVE-2026-53519, a pre-auth path traversal in Nezha Dashboard that leaks jwt_secret_key and enables JWT forgery and admin…
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 vxssroott/cve-2026-78905-facebook-account-takeover
Social Media Infrastructure Vulnerability Research. CVE-2026-78905: OAuth token reuse and session hijacking in Facebook's Graph API.
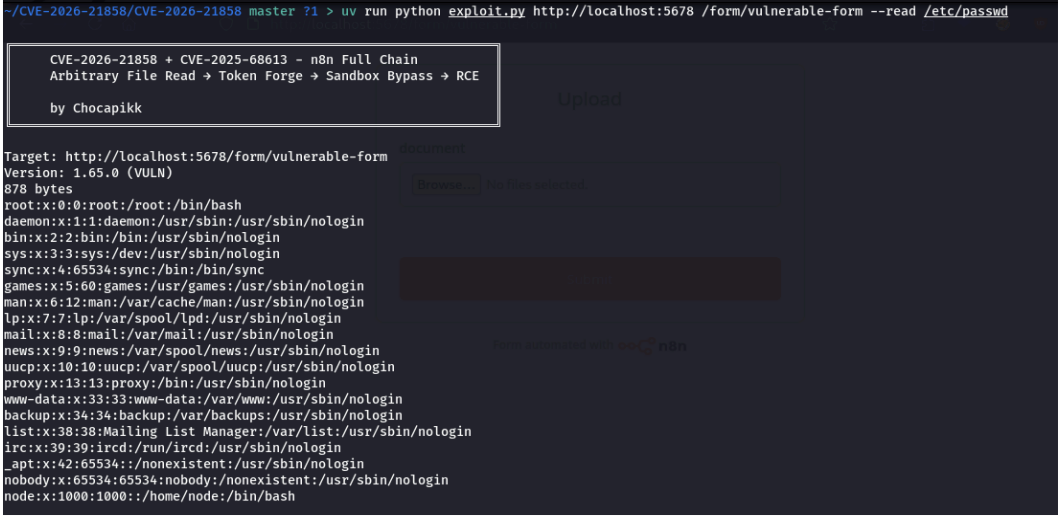 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
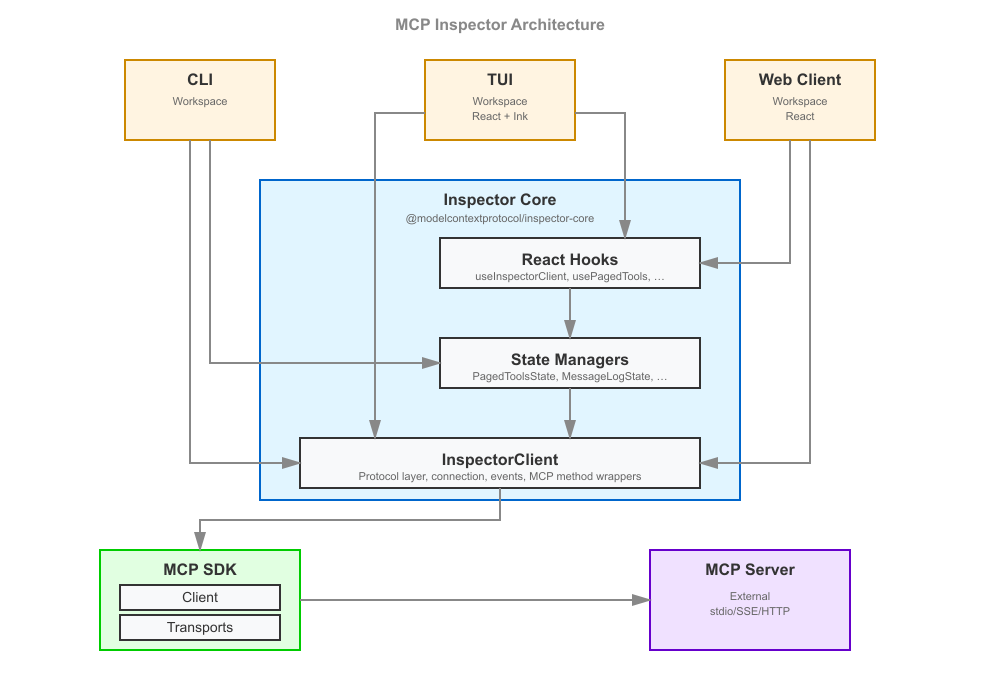 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 bunnie/dc34-vault
Vault app for DC34 badge
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 chpratik/cve-2026-9830
Threat intelligence report repository for CVE-2026-9830, an authentication bypass vulnerability in BookingPress Pro WordPress plugin, with detailed…
 razureink/cve-2024-1708-connectwise_rce_reproduction
Reproduction of cve-2024-1708-connectwise_rce_reproduction
 razureink/cve-2025-24472-fortinet_authbypass_reproduction
CVE Reproduction: cve-2025-24472-fortinet_authbypass_reproduction
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
 zeoday/cobaltstrike4.5_cdf-1
cobaltstrike4.5版本破/解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等