

SafeLine
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.7k
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 fabdotnet/cve-2023-27100
Exploit for CVE-2023-27100 bypassing pfSense anti-brute force protection via crafted X-Forwarded-For headers and anti-CSRF tokens to evade sshguard…
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 flaviupopescu/cve-2022-28601
A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
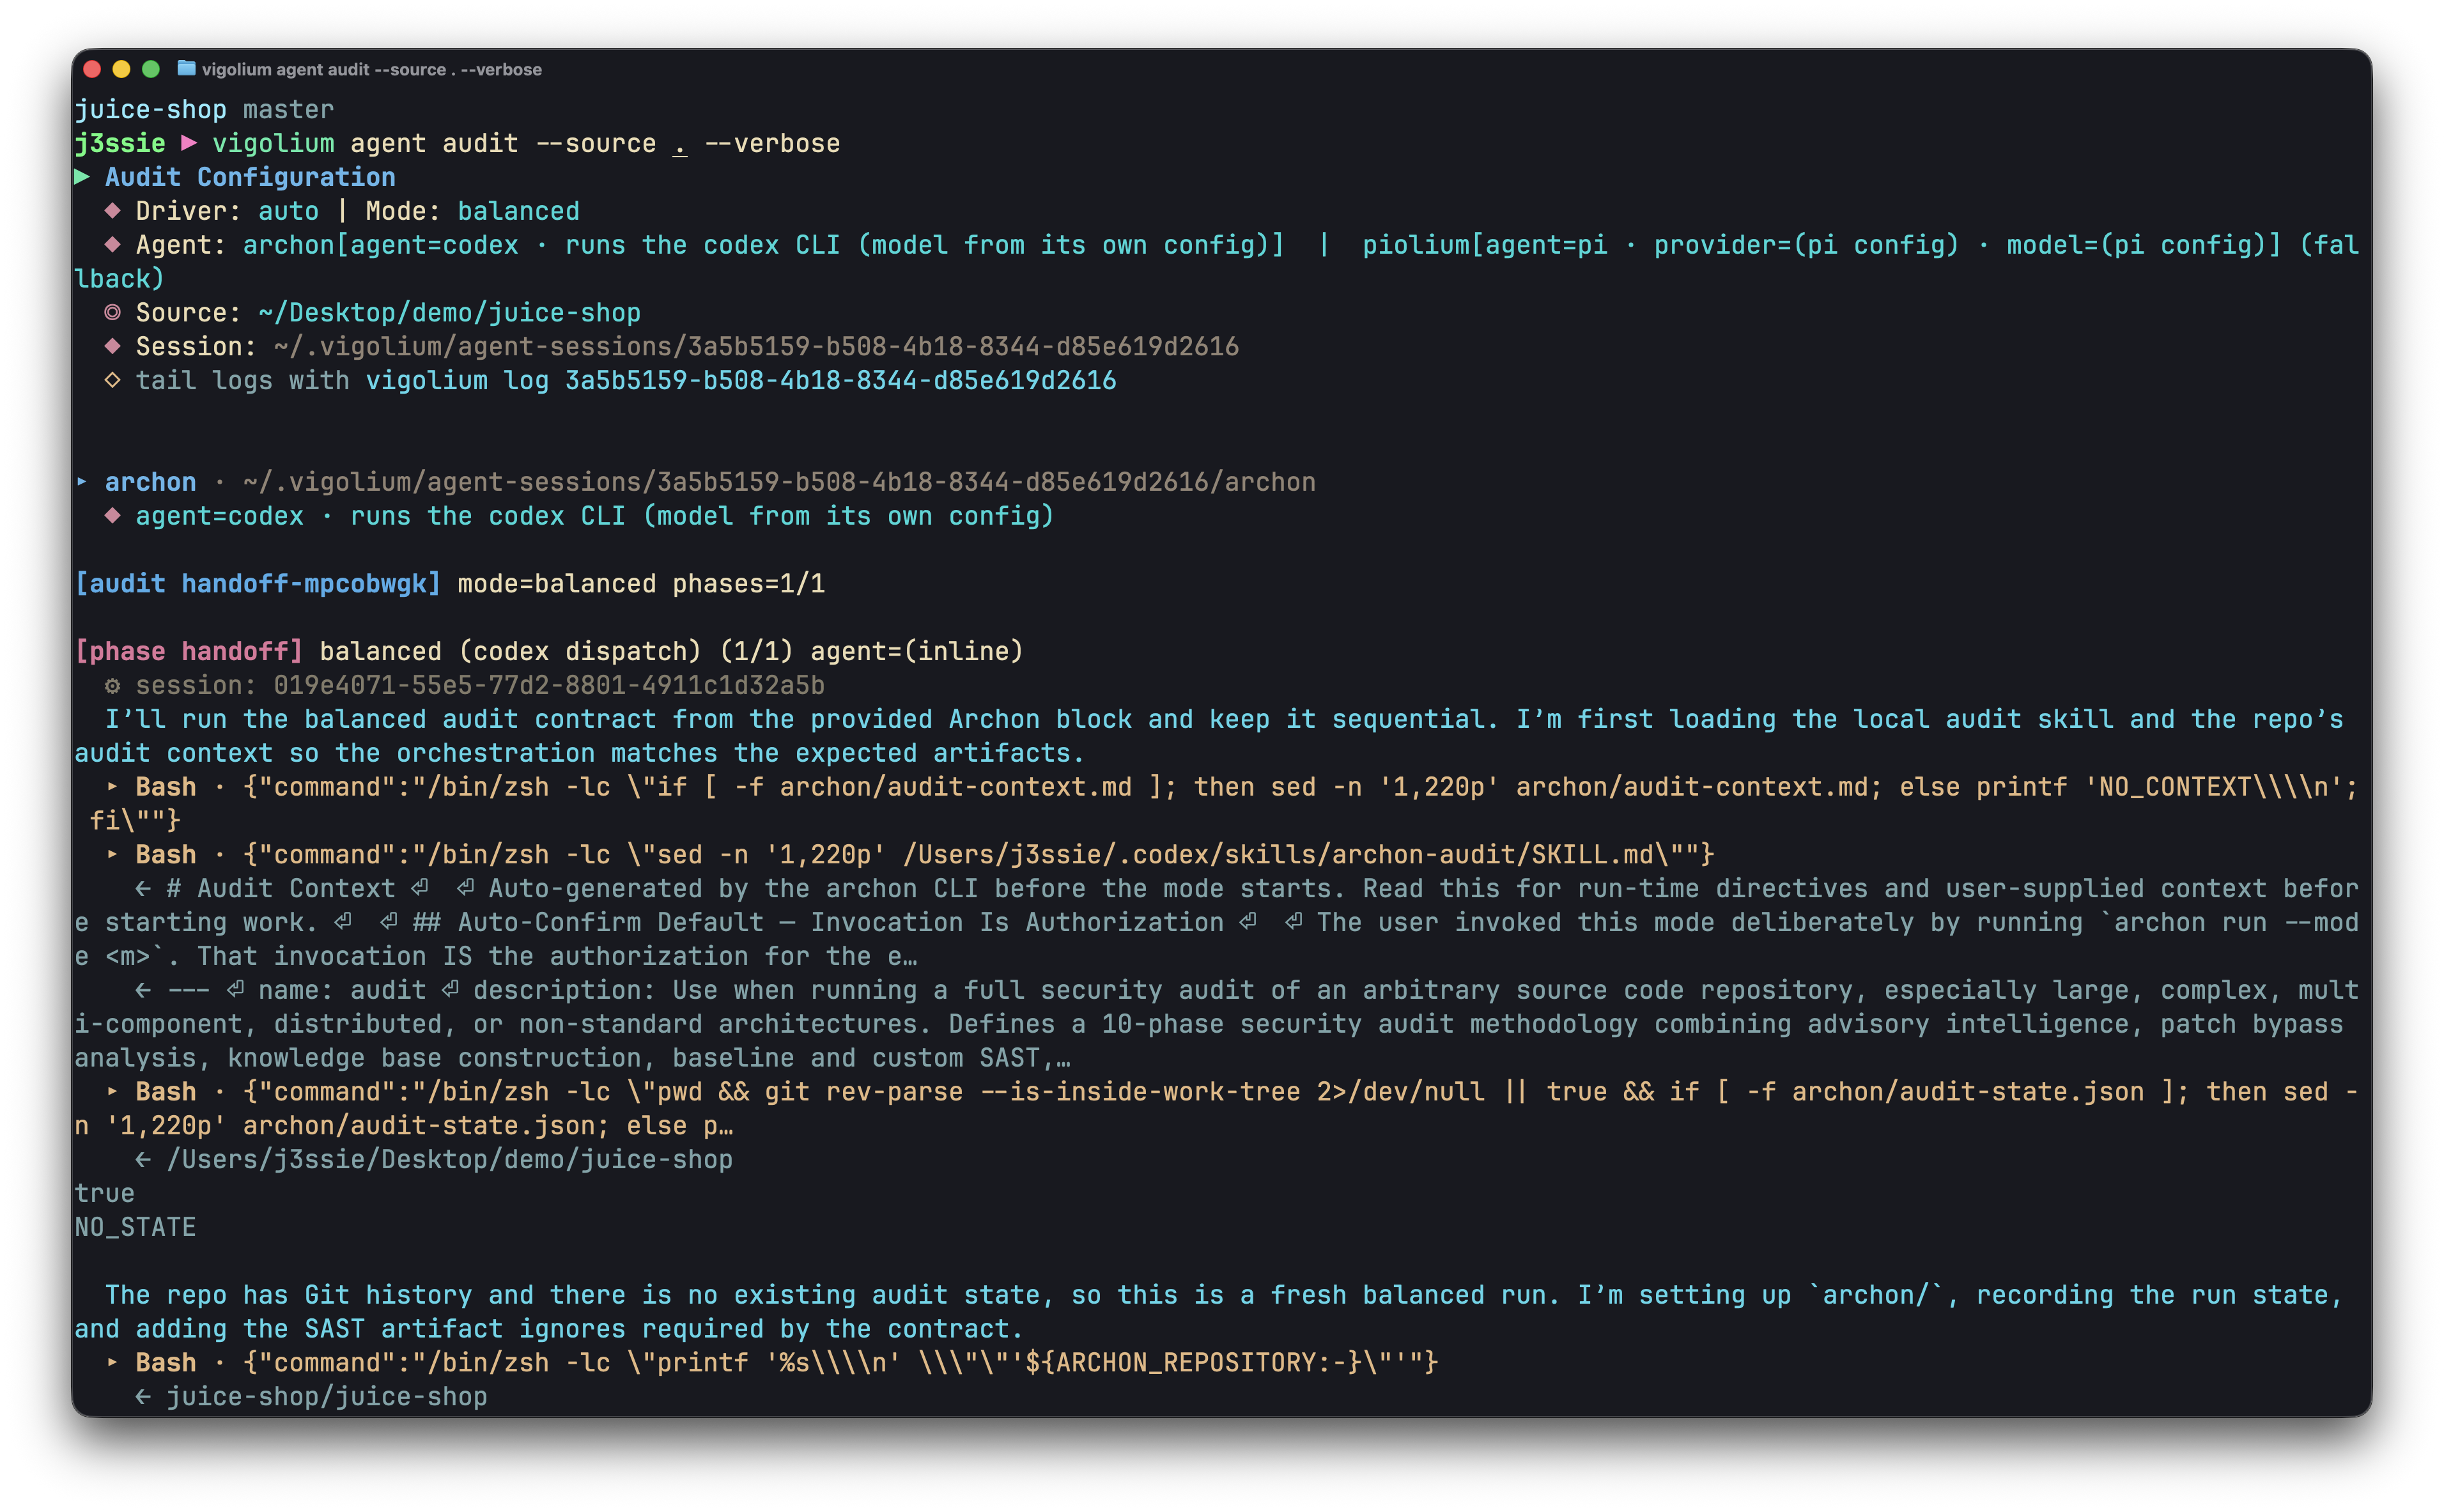 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
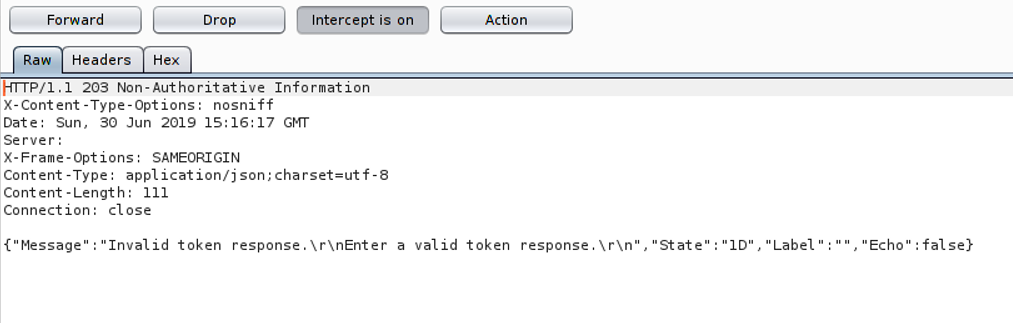 furqankhan1/cve-2019-13496
Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
 pilfer/idictpy
A salty-ass 100% verified hacker status python script to turn apple id's into apple crisp #nicememe
 dante01yoon/cve-2025-29927
Demonstration of CVE-2025-29927: Next.js middleware authentication bypass via x-middleware-subrequest header spoofing. Includes vulnerable and fixed…
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 yuriisanin/cve-2022-25262
PoC + vulnerability details for CVE-2022-25262 / JetBrains Hub single-click SAML response takeover
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.