
exploit-mikrotik-2026
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
authenticationexploitationinformation-gathering+4
14
blackhatexploitation/exploit-mikrotik-2026CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 nccgroup/carnivore
Tool for assessing on-premises Microsoft servers authentication such as ADFS, Skype, Exchange, and RDWeb
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
 evilsocket/legba
The fastest and more comprehensive multiprotocol credentials bruteforcer / password sprayer and enumerator. 🥷
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 urbanesec/zackattack
Unveiled at DEF CON 20, NTLM Relaying to ALL THE THINGS!
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 pilfer/idictpy
A salty-ass 100% verified hacker status python script to turn apple id's into apple crisp #nicememe
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 yzee00/cve-2018-15473
Fix for CVE-2018-15473
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
 praetorian-inc/adfsrelay
Proof of Concept Utilities Developed to Research NTLM Relaying Attacks Targeting ADFS
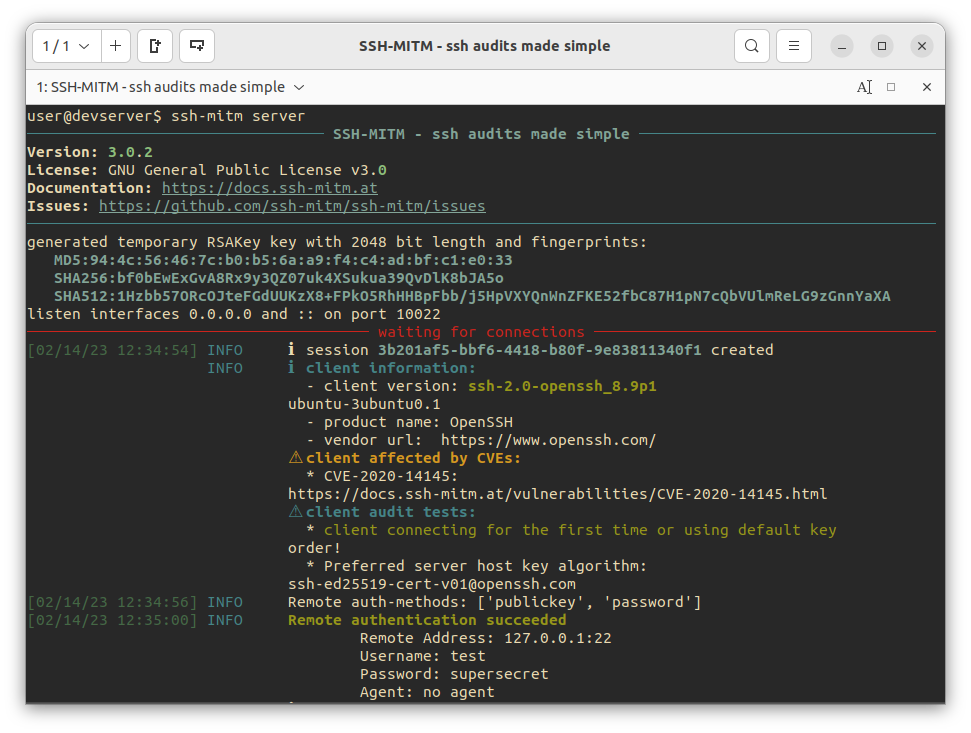 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
 affolter-engineering/ldapin
CLI tool to perform basic LDAP task for security assessments