

Responder
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
authenticationdns-analysisdns-fuzzing+10
6.5k
lgandx/responderResponder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 dani-garcia/vaultwarden
Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
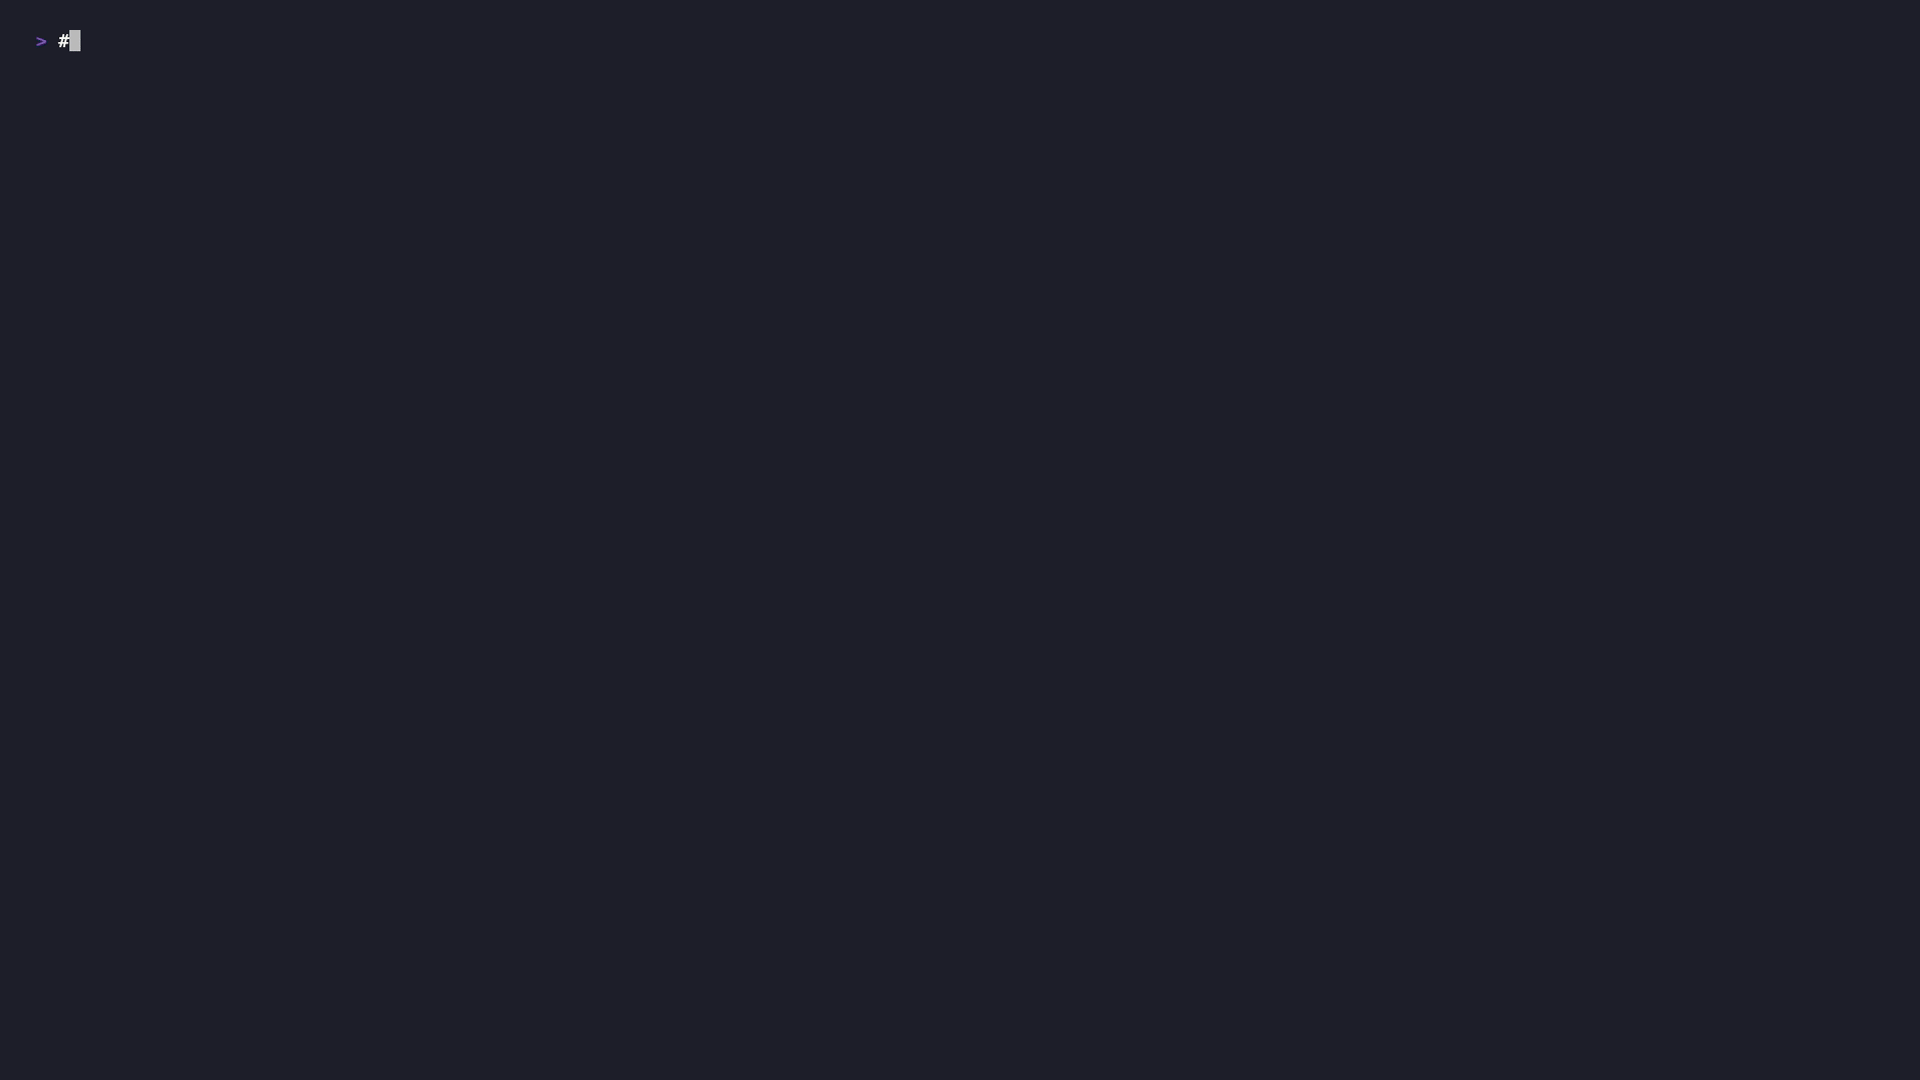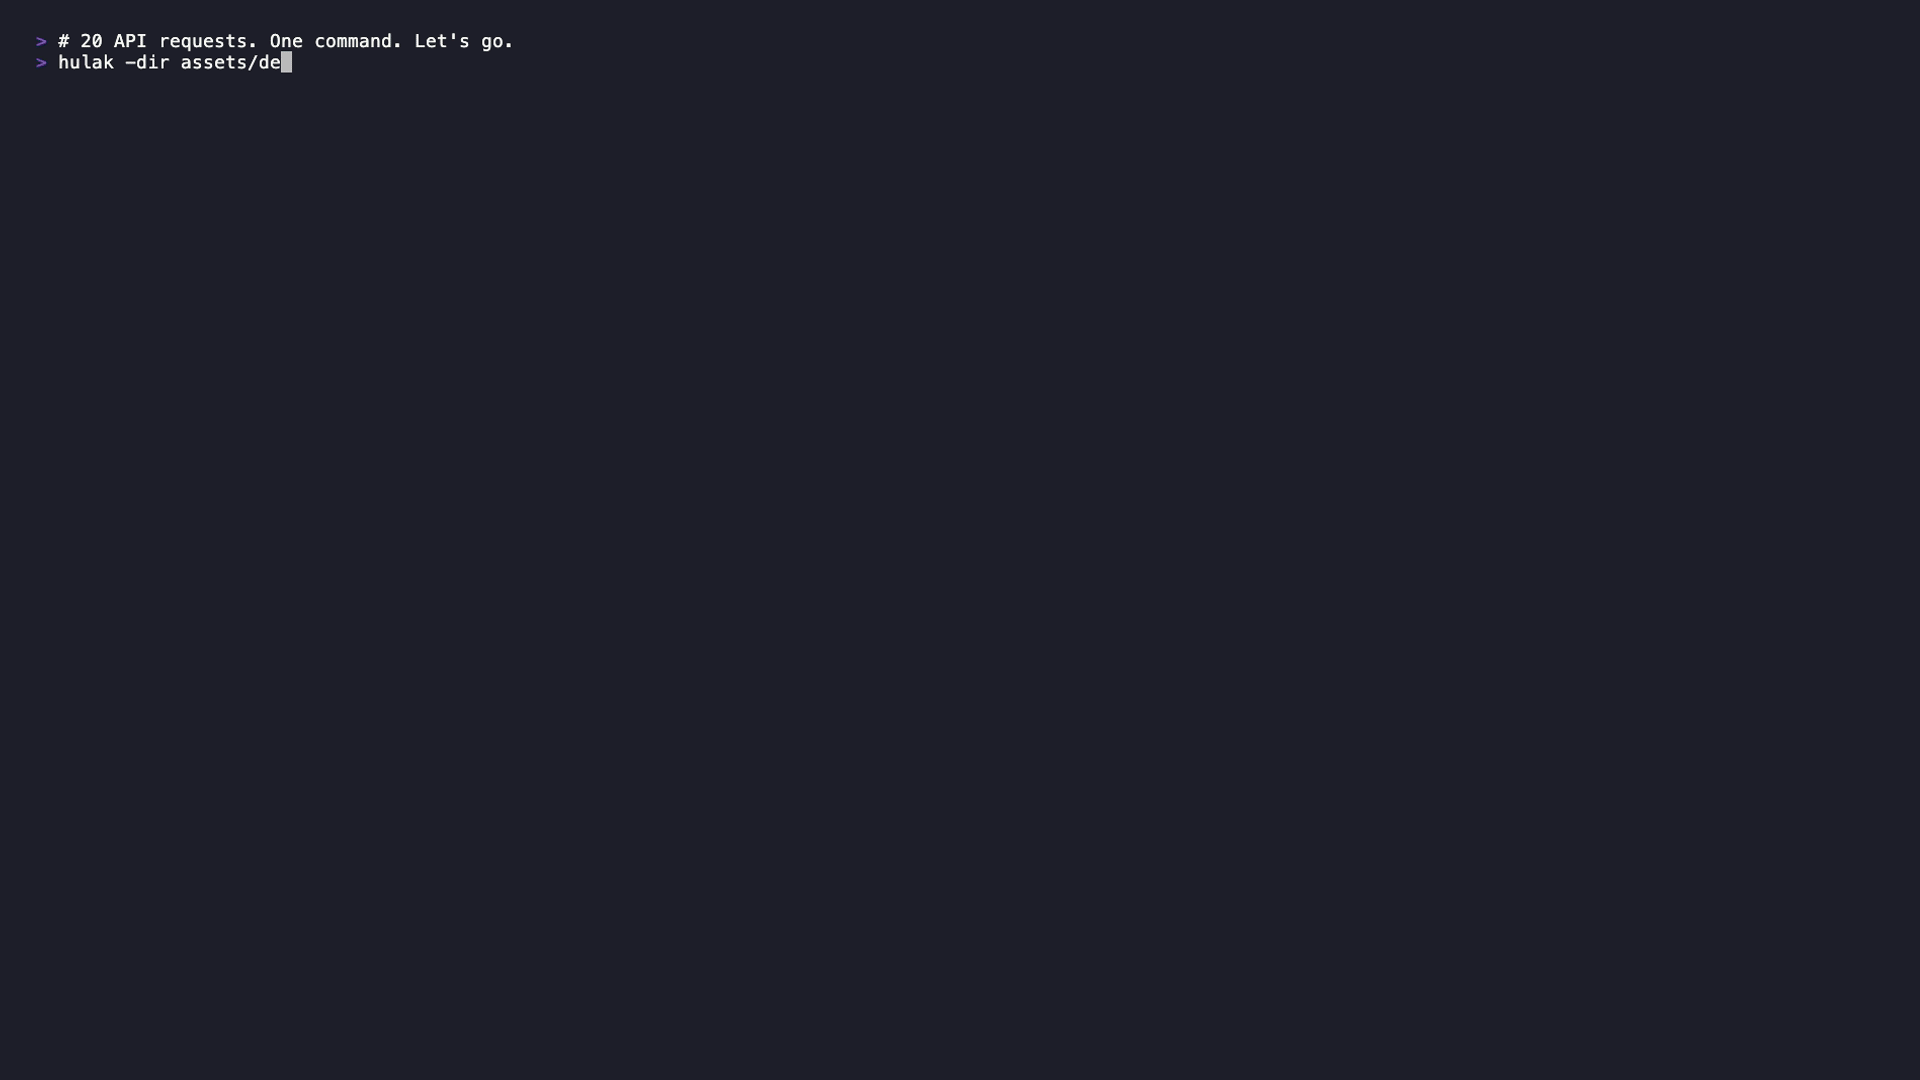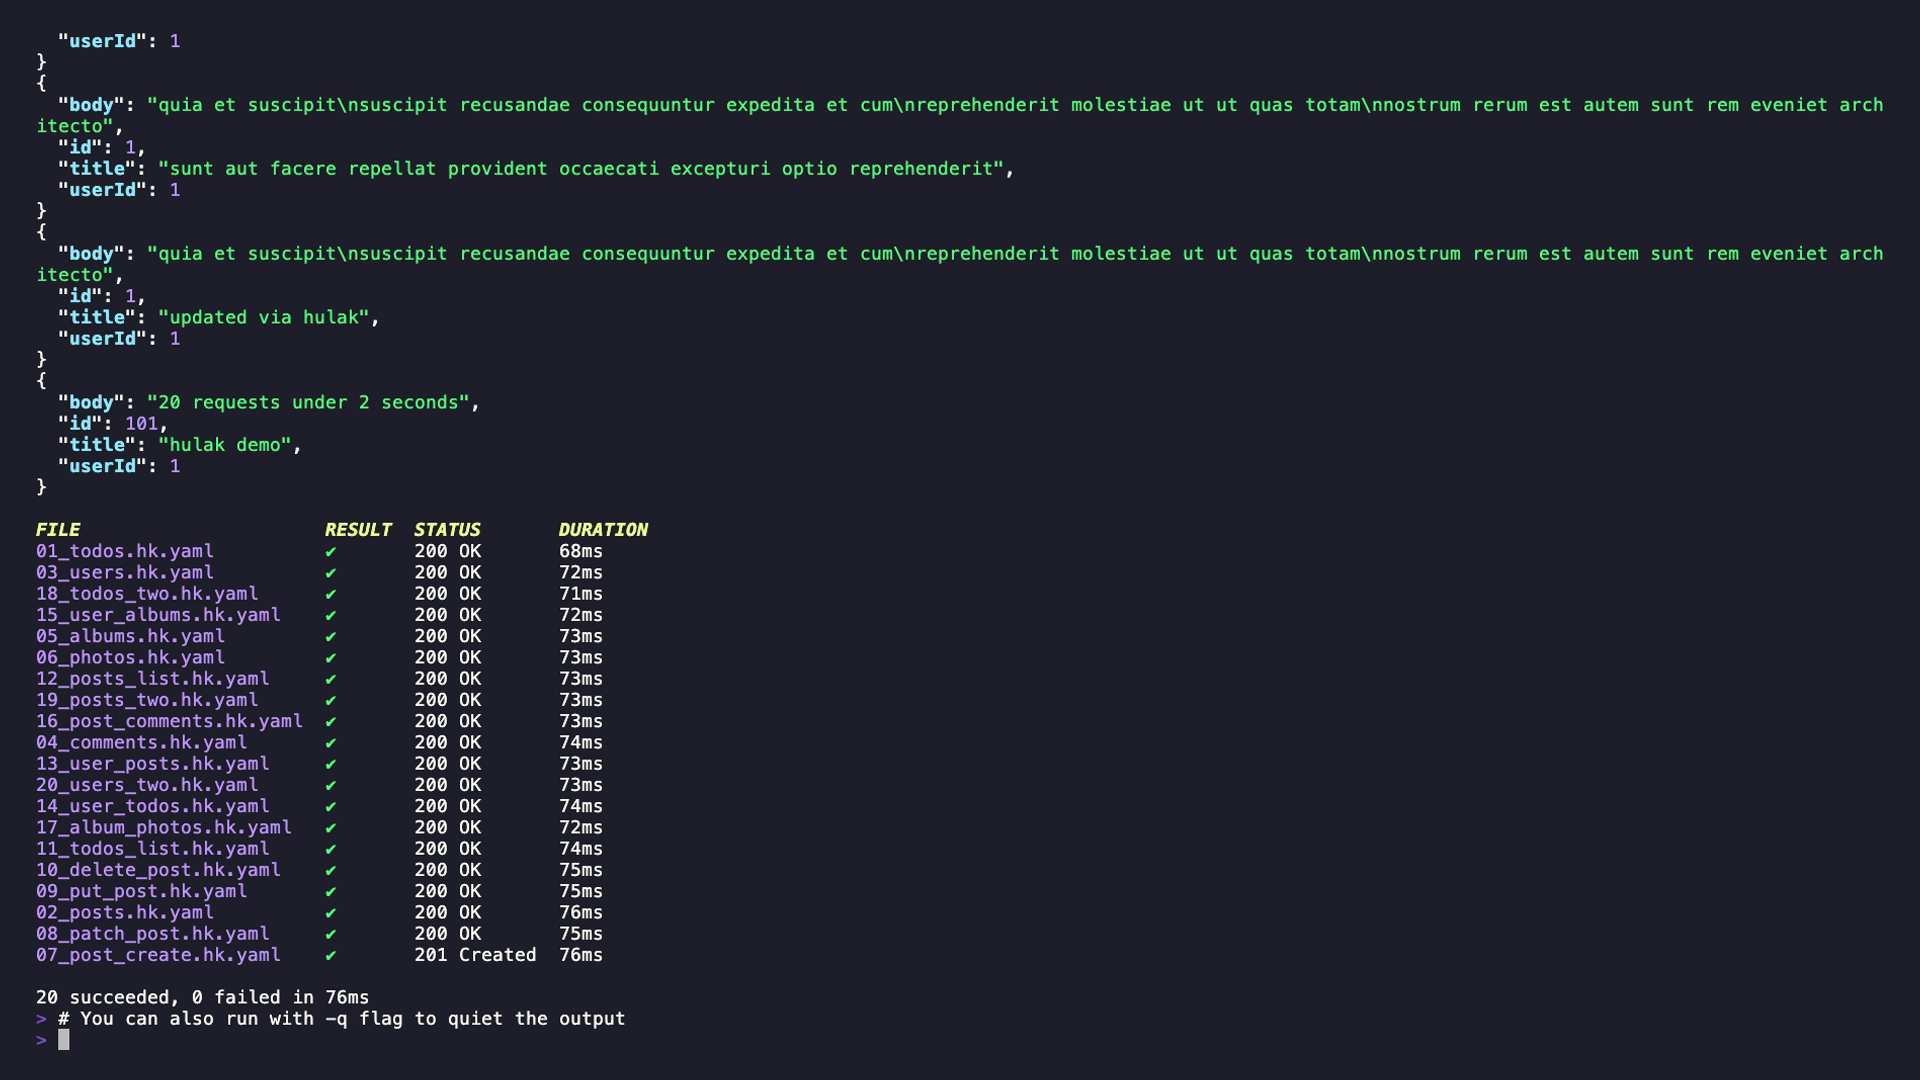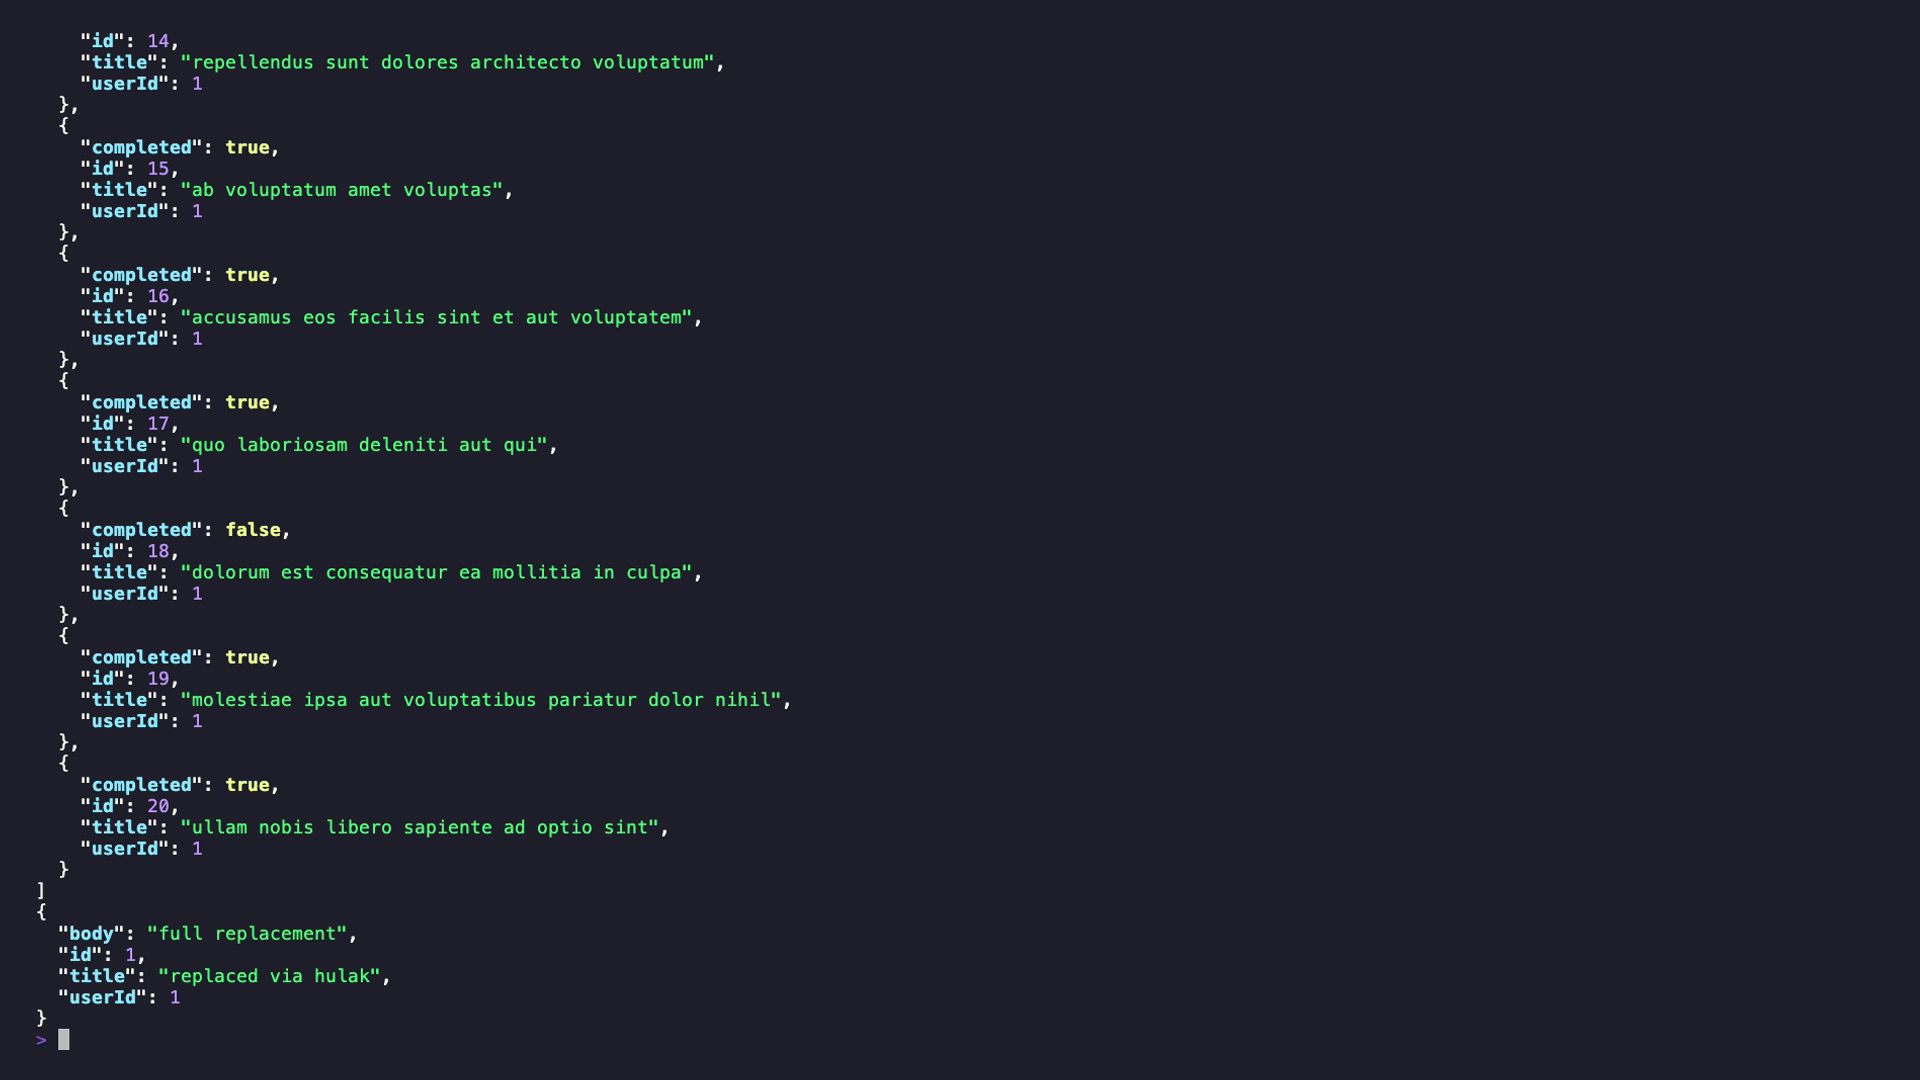 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 p0dalirius/coercer
A python script to automatically coerce a Windows server to authenticate on an arbitrary machine through 12 methods.
 wantasticapp/wantasticcore
AIO Cloud Managment Server

 aa22396584/synology-nas-cli
nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 shoucheng3/asf__james-project_cve-2022-22931_3-6-0
Modular Java mail server supporting IMAP, SMTP, POP3, and JMAP with Docker deployment, distributed architecture, and CLI management for secure…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
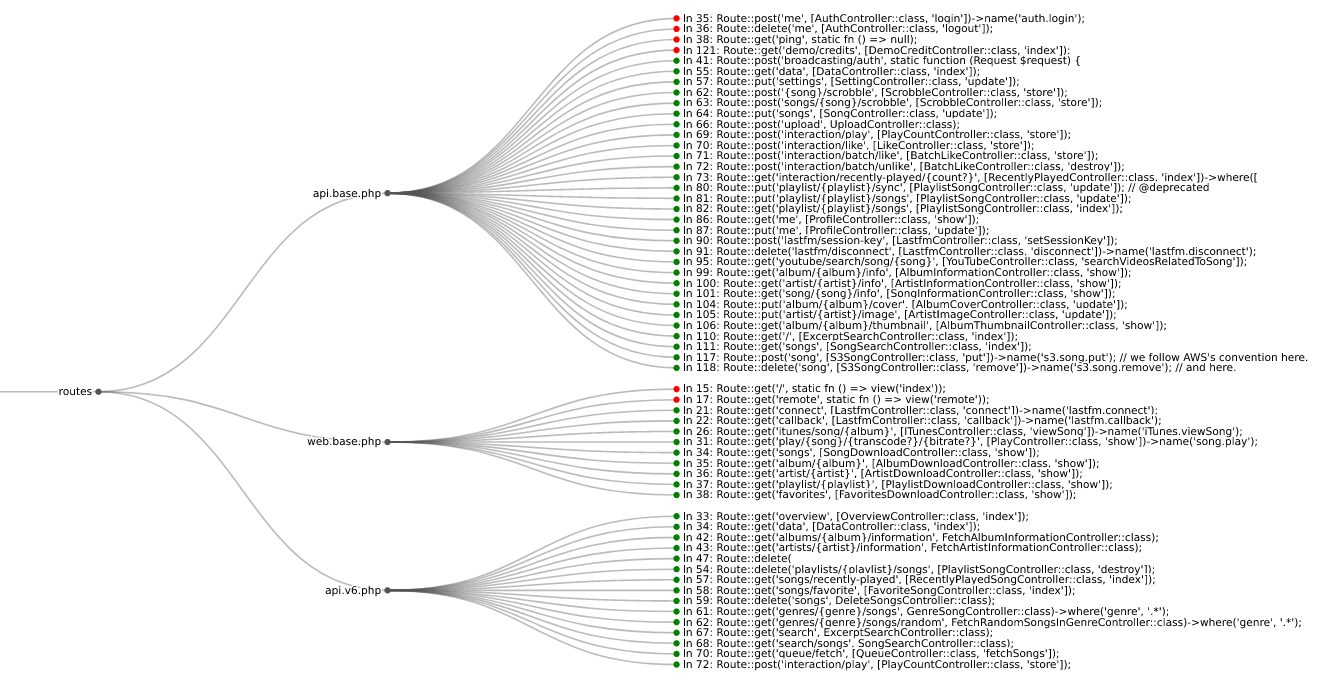 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 shivshantp/cve-2025-2825-crushftp-authbypass
Authentication Bypass PoC for CVE-2025-2825 – Exploiting CrushFTP 10.x