the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass

Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…

Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…

Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…

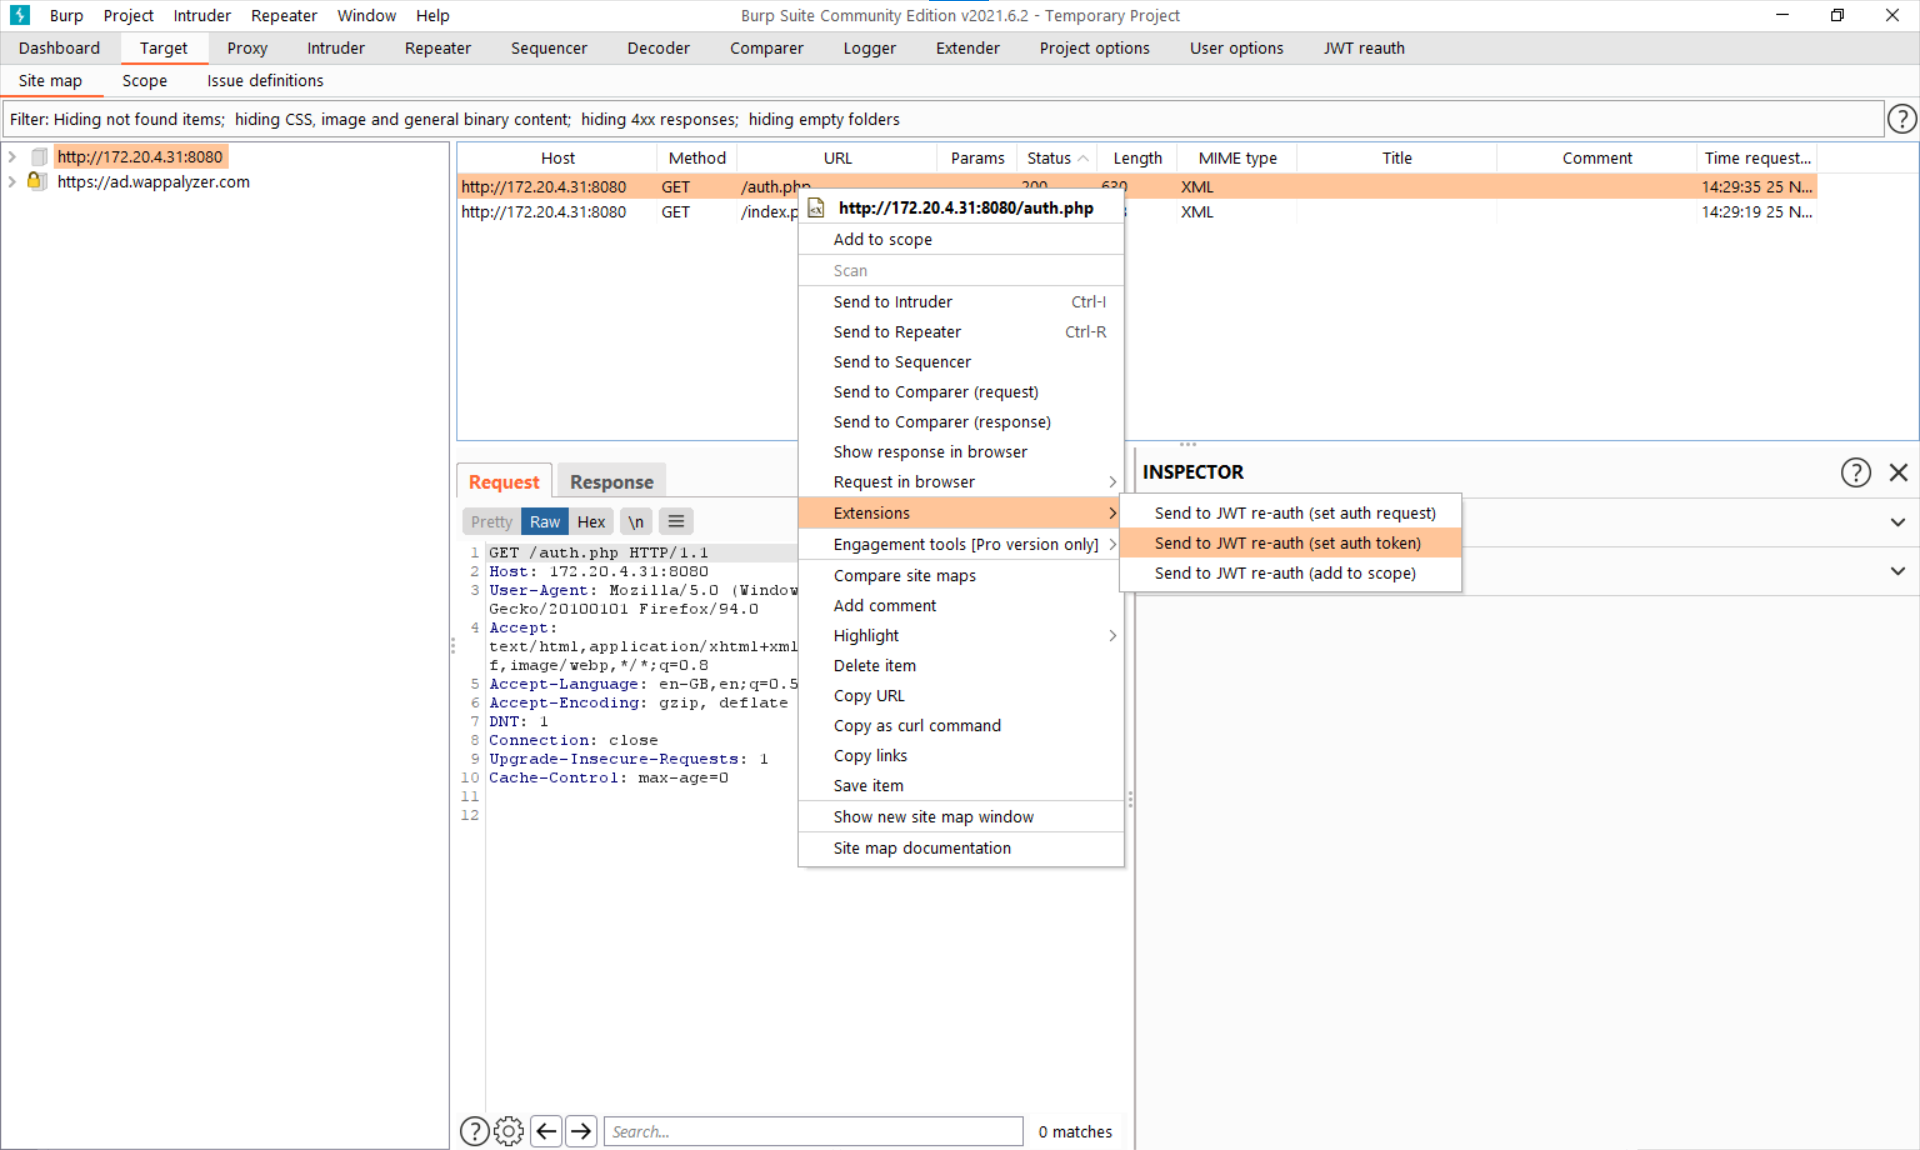
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.

Proof-of-concept exploit for CVE-2023-47504 targeting Elementor WordPress plugin. Requires subscriber credentials and wp-config.php access to delete…

Runnable Spring Boot and Quarkus reproducer for CVE-2026-94386, demonstrating cross-scope OAuth token reuse in Apache Camel camel-oauth's static…