
CVE-2023-34051
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
authenticationcommand-and-controlexploitation+7
603 years ago
horizon3ai/cve-2023-34051VMware Aria Operations for Logs CVE-2023-34051
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 digital-dev/keepass-triggerless
KeePass 2.53.1 with removed ECAS Trigger System Remediating CVE-2023-24055
 itzvenom/cve-2023-6329
Python PoC exploit for CVE-2023-6329 authentication bypass in Control iD iDSecure. Reconstructs admin credentials via predictable password derivation…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
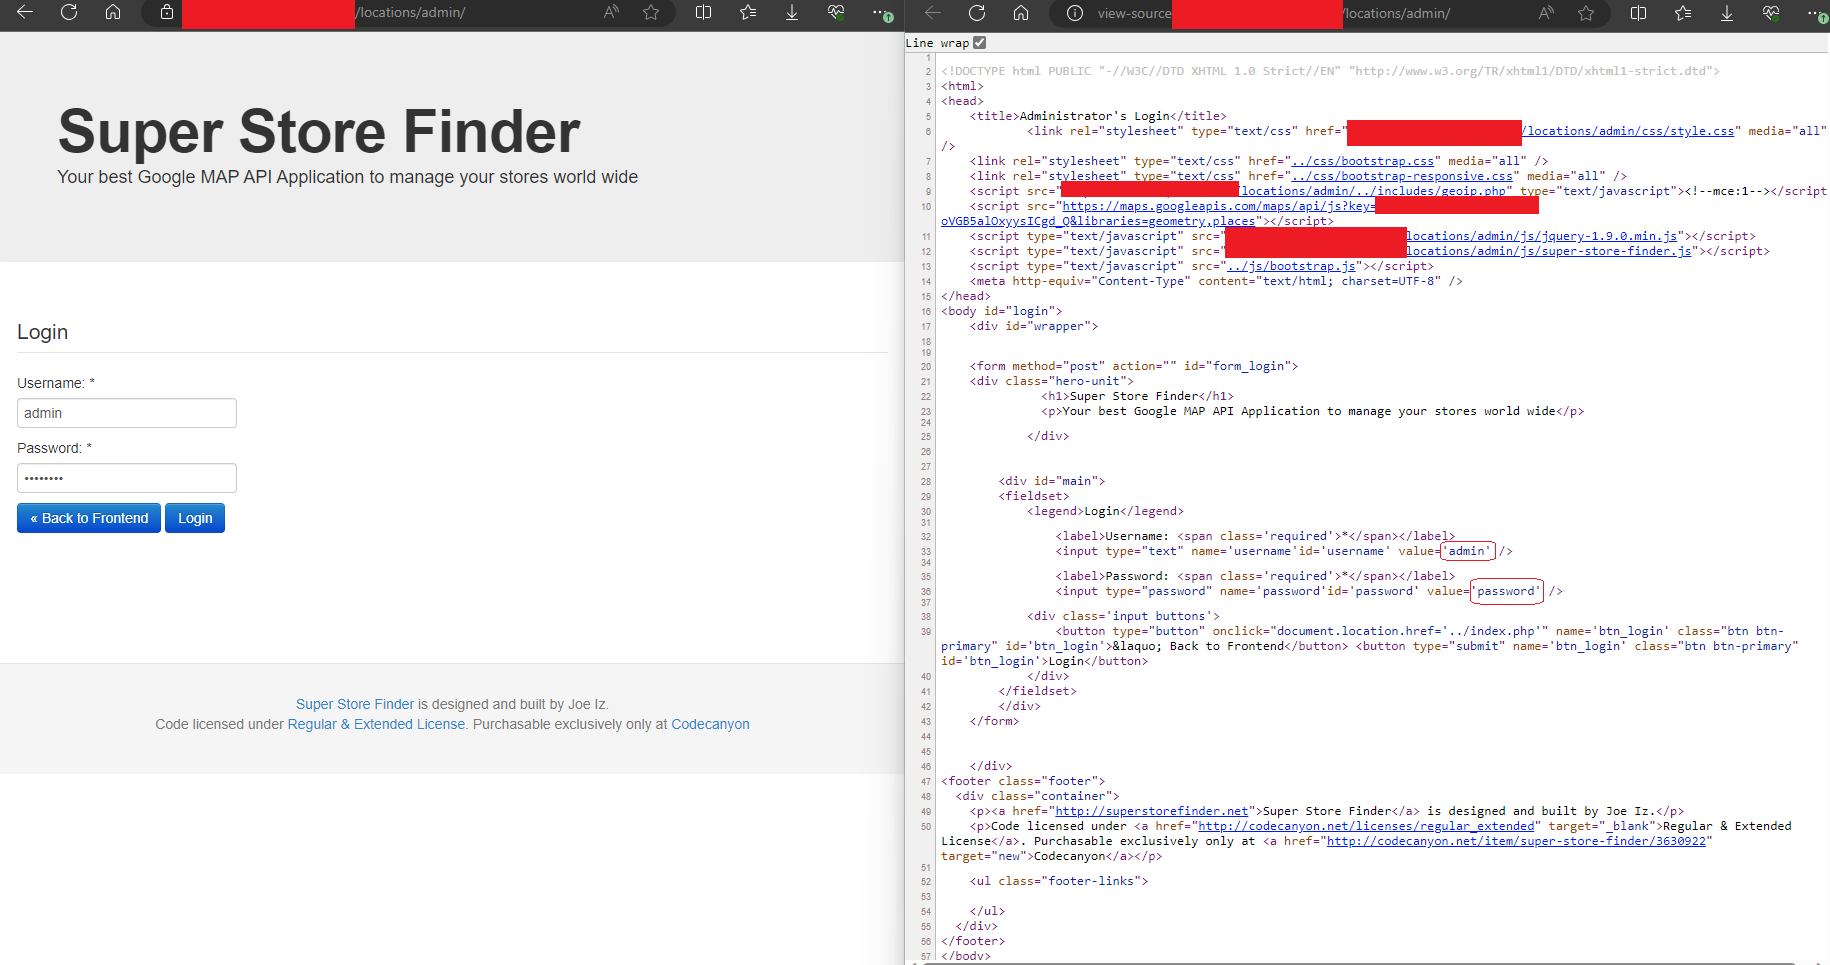 redblueteam/cve-2023-41508
CVE-2023-41508 - A hard-coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 cyb3rmaddy/cve-2023-23397-report
An exploitation demo of Outlook Elevation of Privilege Vulnerability
 horizon3ai/cve-2023-27350
Proof-of-concept exploit for PaperCut CVE-2023-27350, chaining authentication bypass with built-in scripting abuse to achieve remote code execution…
 smokeintheshell/cve-2023-20198
CVE-2023-20198 Exploit PoC
 pulentoski/explotacion-cve-2023-32315-openfire
Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
 graysignal/apache-ofbiz-auth-bypass-and-rce-exploit-cve-2023-49070-cve-2023-51467
This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…
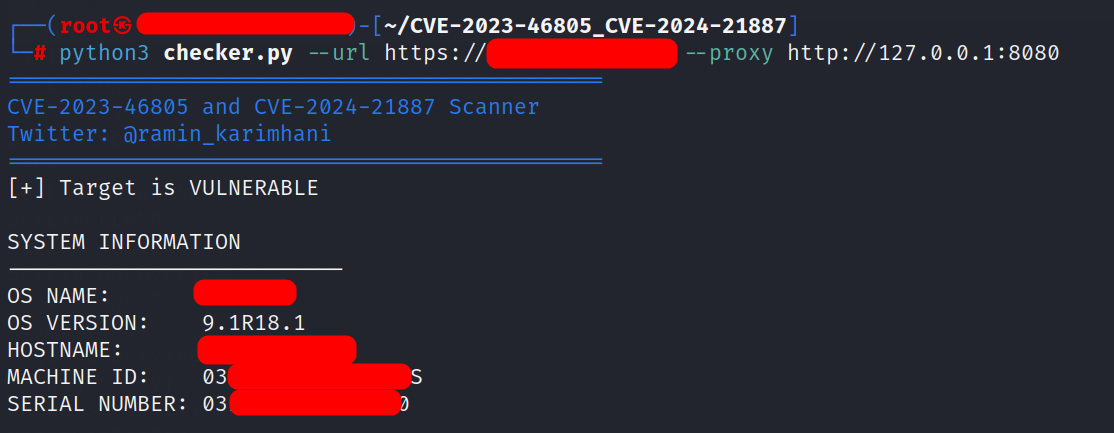 raminkarimkhani1996/cve-2023-46805_cve-2024-21887
The script in this repository only checks whether the vulnerabilities specified in the Ivanti Connect Secure product exist.
 cappricio-securities/cve-2023-5089
Defender Security < 4.1.0 - Protection Bypass (Hidden Login Page)
 pushkarup/cve-2023-23752
Exploit for CVE-2023-23752 (4.0.0 <= Joomla <= 4.2.7).
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
 hackeremmen/gitlab-exploit
Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…
 redteampentesting/cve-2023-33243
PoC for login with password hash in STARFACE