

TATS
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
authenticationidentity-access-managementlog-analysis+2
icemoonhsv/tatsAnalyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 rotarydrone/globalunprotect
Decrypt GlobalProtect configuration and cookie files.
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 bugresearch/cve-2026-6274
Proof-of-concept exploit for CVE-2026-6274, an authentication bypass in Redline WR3200 routers allowing unauthorized password change via static…
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
 u238/grafana-cve-2018-15727
a small utility to generate a cookie in order to exploit a grafana vulnerability (CVE-2018-15727)
 mverschu/cve-2017-7921
HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.
 guy2610/tough-cookie-patch-cve-2023-26136
RFC6265-compliant cookie parsing and CookieJar management library for Node.js, with CVE-2023-26136 security patch. Supports cookie creation,…
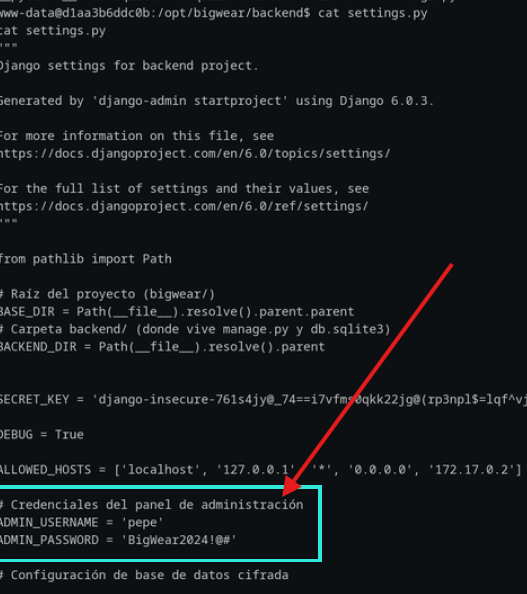 salimelh94/web-penetration-test
Exploiting WordPress vulnerabilities (CVE-2025-34077), authentication bypass via cookie injection, and privilege escalation to root. Part of my…
 jet-pentest/cve-2020-29667
Proof-of-concept exploit for CVE-2020-29667 targeting insufficient session expiration and a hardcoded cookie value in Lan ATMService M3 ATM…
 joelczk/cve-2025-48461
Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…
 ill-deed/crushftp-cve-2024-4040-illdeed
Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…
 wr0x00/cve-2022-23131
Exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Generates a signed session cookie to gain unauthorized admin access.
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 randomrobbiebf/cve-2023-6700
Cookie Information | Free GDPR Consent Solution <= 2.0.22 - Authenticated (Subscriber+) Arbitrary Options Update
 remenis/cve-2025-63666
Tenda AC15 cookie exposure