
exploit-mikrotik-2026
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
authenticationexploitationinformation-gathering+4
14
blackhatexploitation/exploit-mikrotik-2026CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 xqi1337/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 praetorian-inc/adfsrelay
Proof of Concept Utilities Developed to Research NTLM Relaying Attacks Targeting ADFS
 gagaltotal/cve-2026-mikrotik-poc
MikroTik RouterOS PoC Collection - CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 red-darkin/cve-2026-18963-keycloak
Proof-of-concept exploit for CVE-2026-18963, a critical Keycloak reset-credentials bypass enabling unauthenticated account takeover. Includes lab…
 bugch3ck/imposter
Proof of concept for CVE-2015-0006. Fixed in MS15-005 https://docs.microsoft.com/en-us/security-updates/SecurityBulletins/2015/ms15-005 .
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
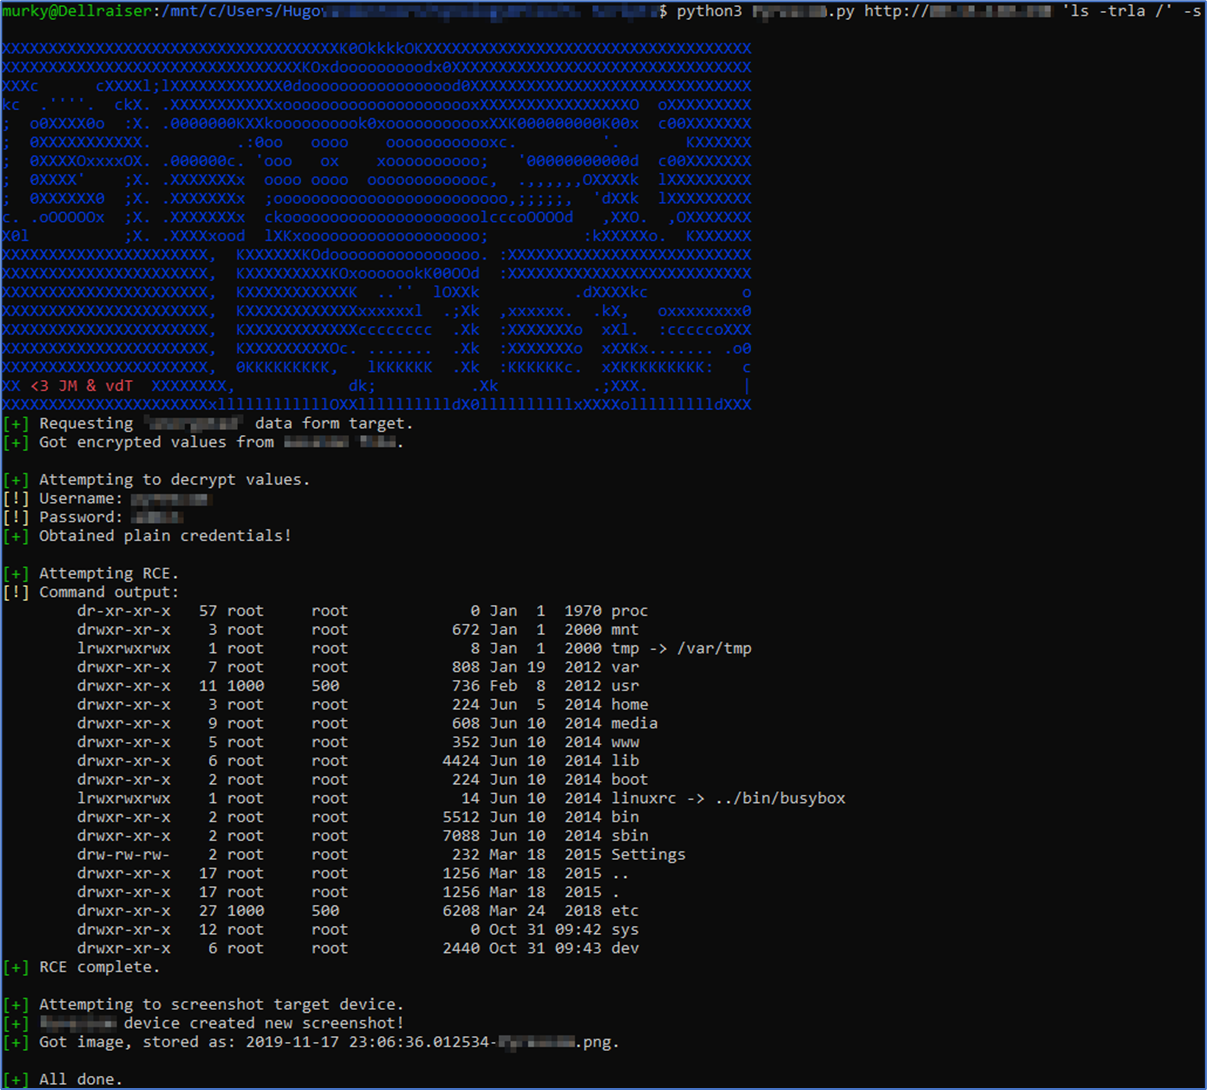 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
 t0w0t/poc-cve-2026-18963
Proof-of-concept exploit for CVE-2026-18963, an authentication bypass in Keycloak's forgot-password flow, allowing password reset without proper…
 ericyoc/stego_provenance_defense
Steganographic prompt-injection defense for agentic AI using decode-time provenance binding, HMAC authentication, and MCP trust enforcement.
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 naheeju/poc-cve-2026-0073
Security research PoC for CVE-2026-0073: ADB authentication bypass verification
 chenjp/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.