

web2py-e94946d-CVE-2016-3957
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
authenticationcode-analysisdatabase-security+3
sj/web2py-e94946d-cve-2016-3957web2py/web2py @ e94946d
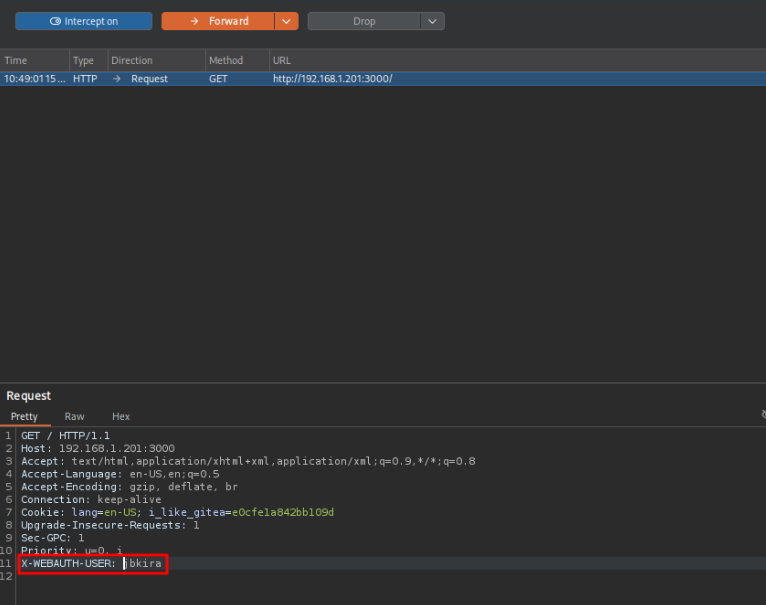 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 eremiel/cve-2018-0114
python2.7 script for JWT generation
 graysignal/apache-ofbiz-auth-bypass-and-rce-exploit-cve-2023-49070-cve-2023-51467
This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…
 0xmrma/cve-2026-34828
listmonk’s Session Persistence After Password Reset and Password Change
 adityathebe/poc-cve-2018-0114
POC for CVE-2018-0114 written in Go