
raider
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
owasp/raiderOWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…
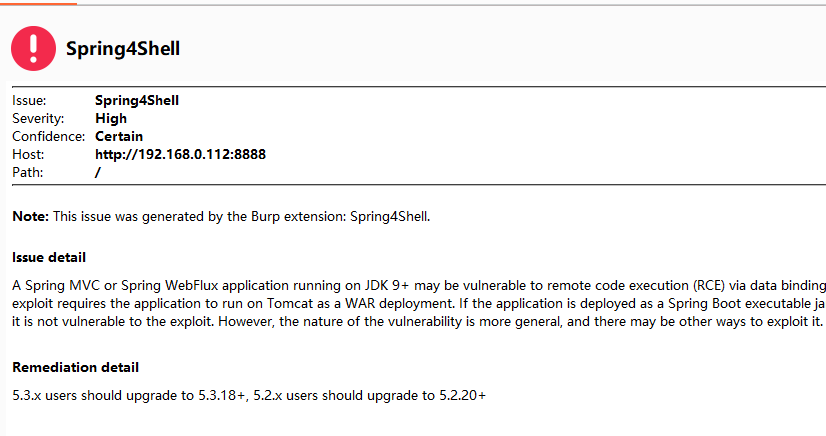 loneyers/spring4shell
Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
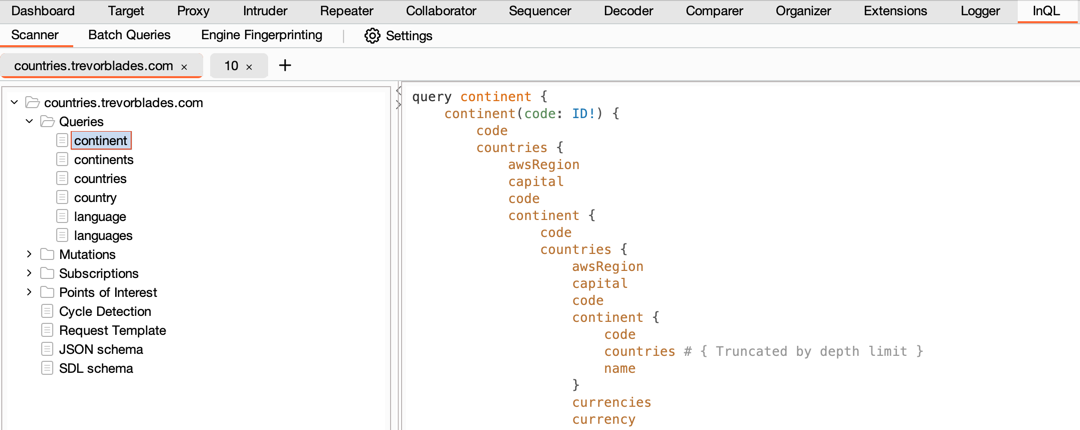 doyensec/inql
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
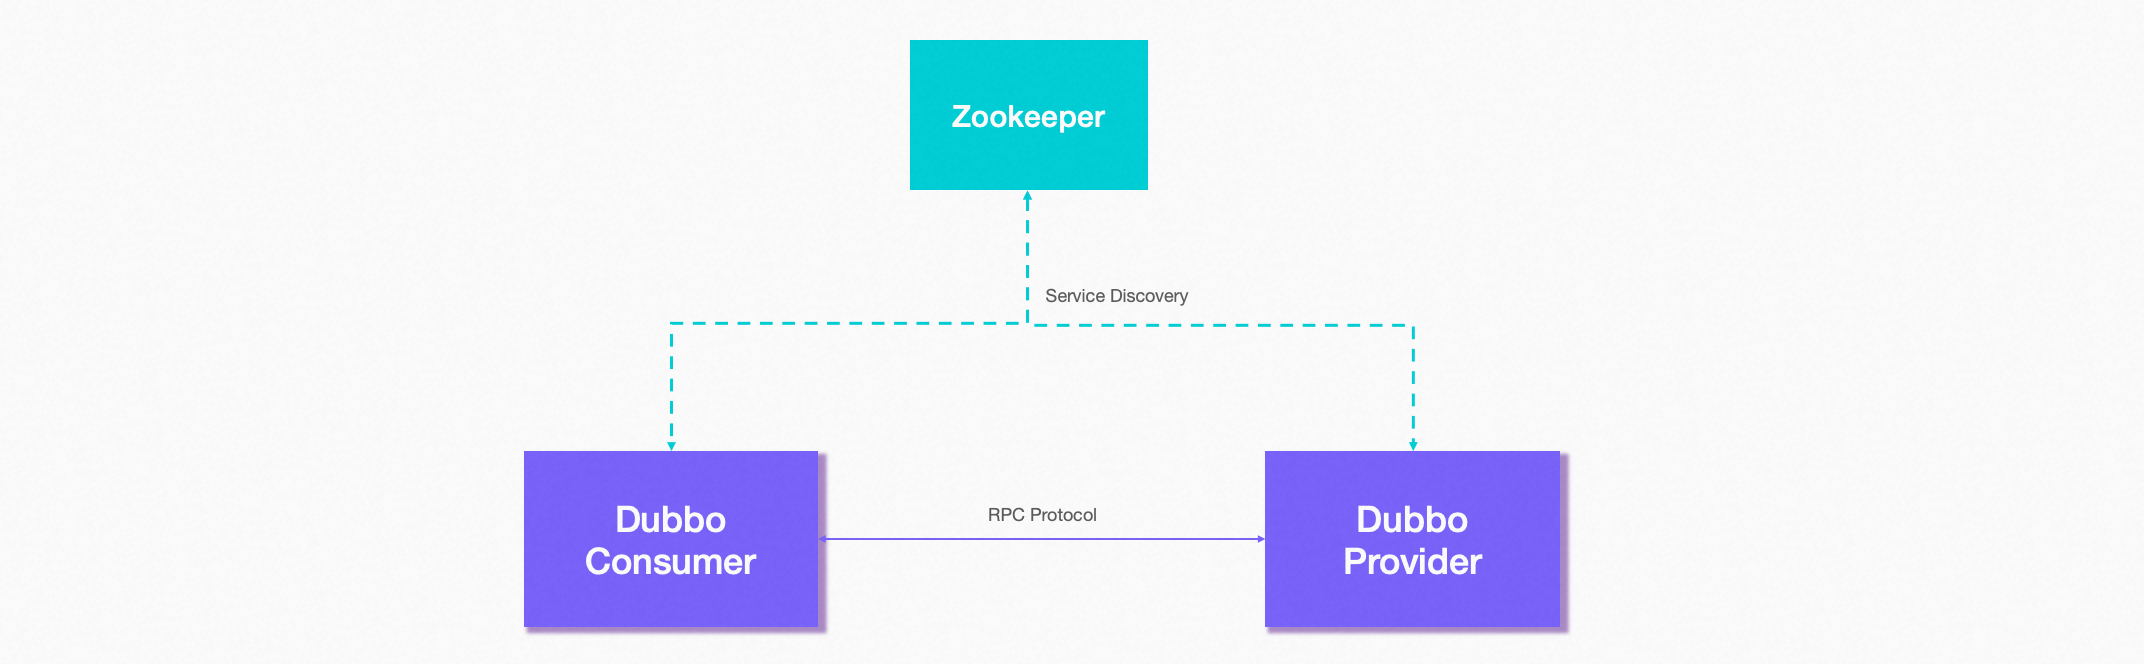 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…