

CVE-2026-34910-PoC
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
api-security-testingauthenticationexploitation+3
boreas37/cve-2026-34910-pocCVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
 hunt-benito/bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork
PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
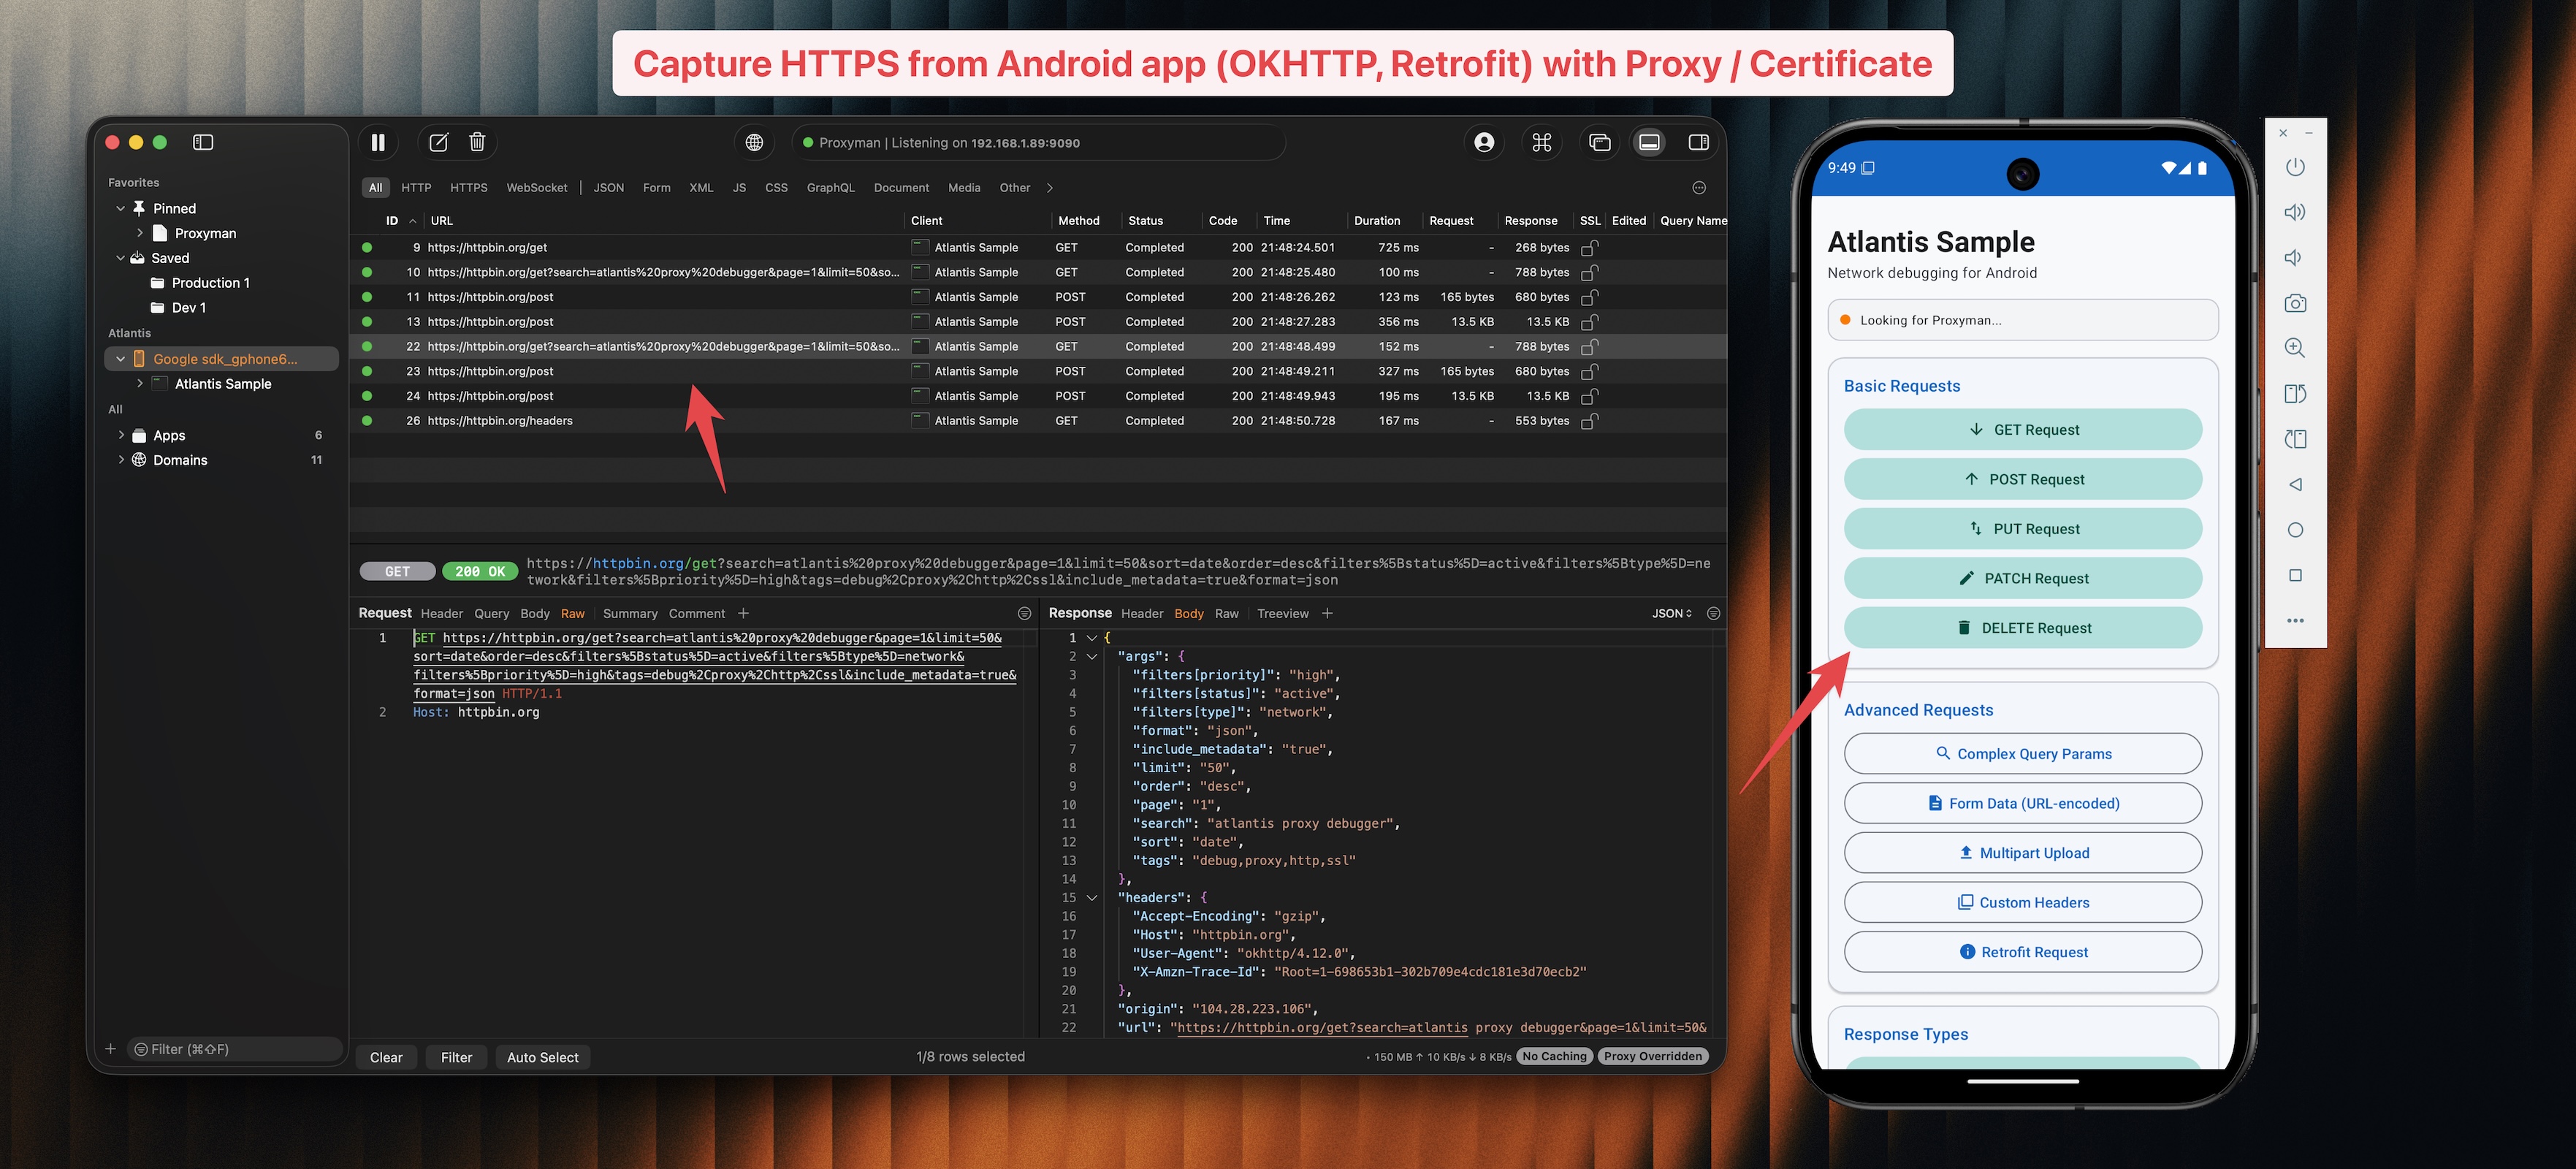 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…