
CVE-2023-6289
 randomrobbiebf/cve-2023-6289
Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
api-security-testingexploitationinformation-gathering+3
randomrobbiebf/cve-2023-6289Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 palmtreeforest/codepath_week_7-8
CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API
 corgizz/springcloud
Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
 google/martian
Martian is a library for building custom HTTP/S proxies
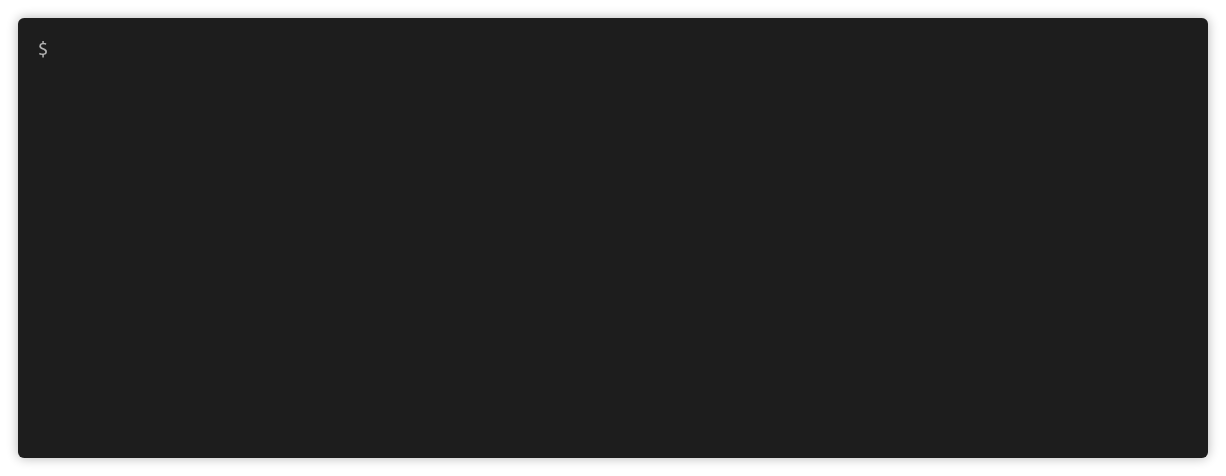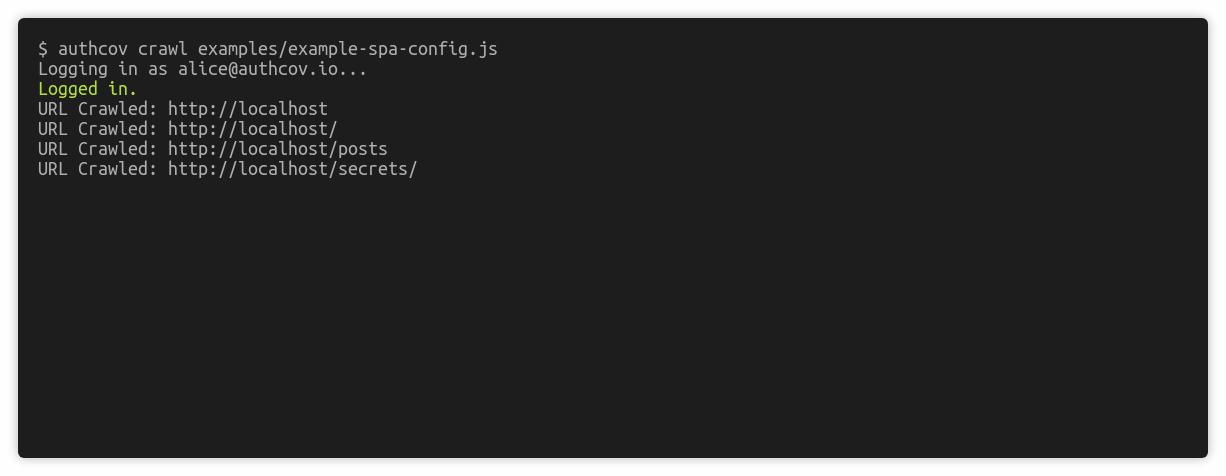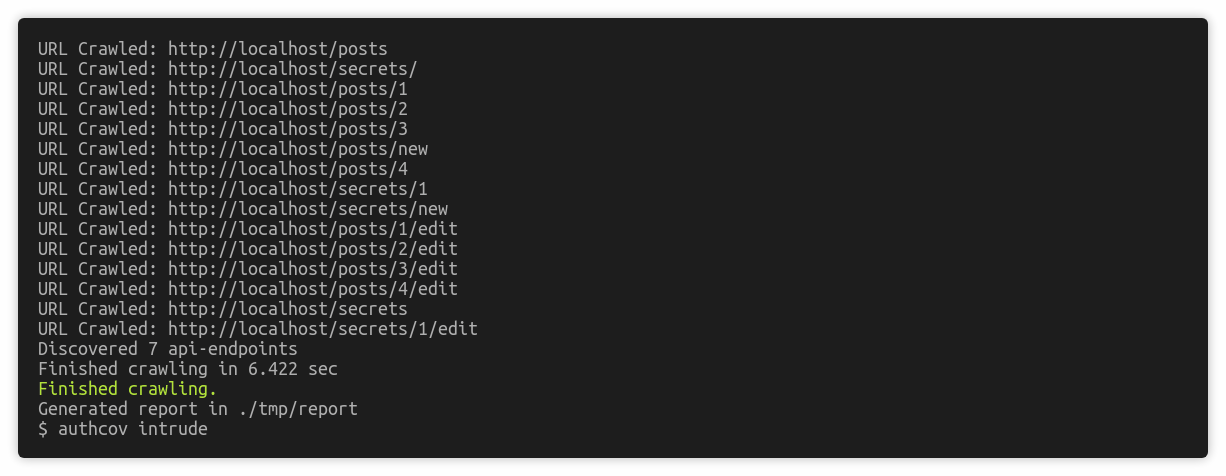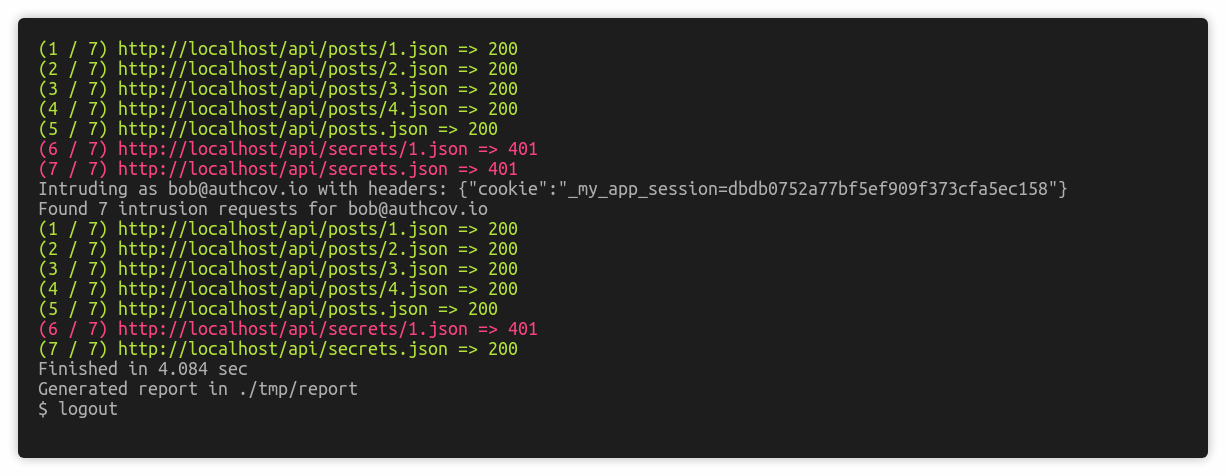 authcov/authcov
Web app authorisation coverage scanning
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
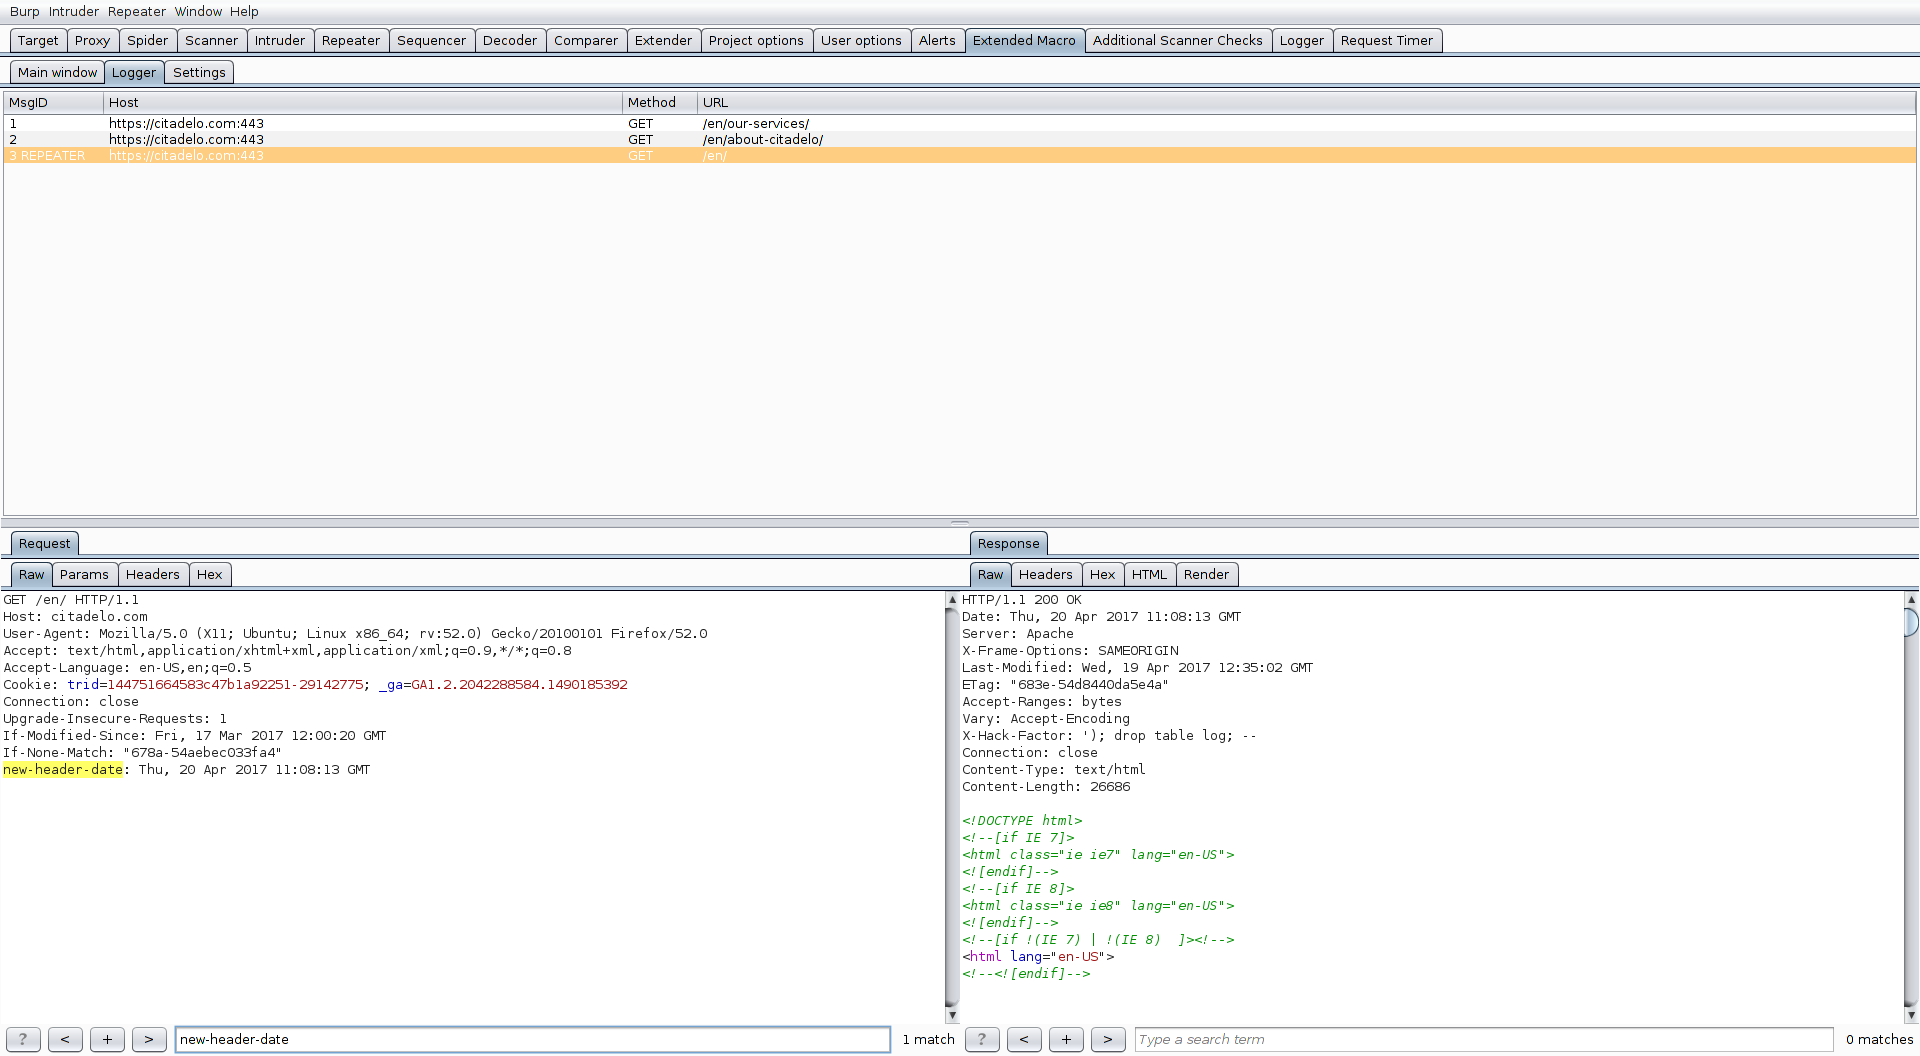 fruh/extendedmacro
ExtendedMacro - BurpSuite plugin providing extended macro functionality
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…
 themalwareguardian/brokeclaudia
CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
 wingleszy/htb-enigma-walkthrough
Write-up машины Enigma (HTB). Корпоративная инфраструктура: NFS exposure → Webmail recon → OpenSTAManager RCE (CVE-2026-38751) → прескалация до root…