

sast-scan-action
 offensive360/sast-scan-action
GitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
api-security-testingcloud-securitycode-analysis+4
offensive360/sast-scan-actionGitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
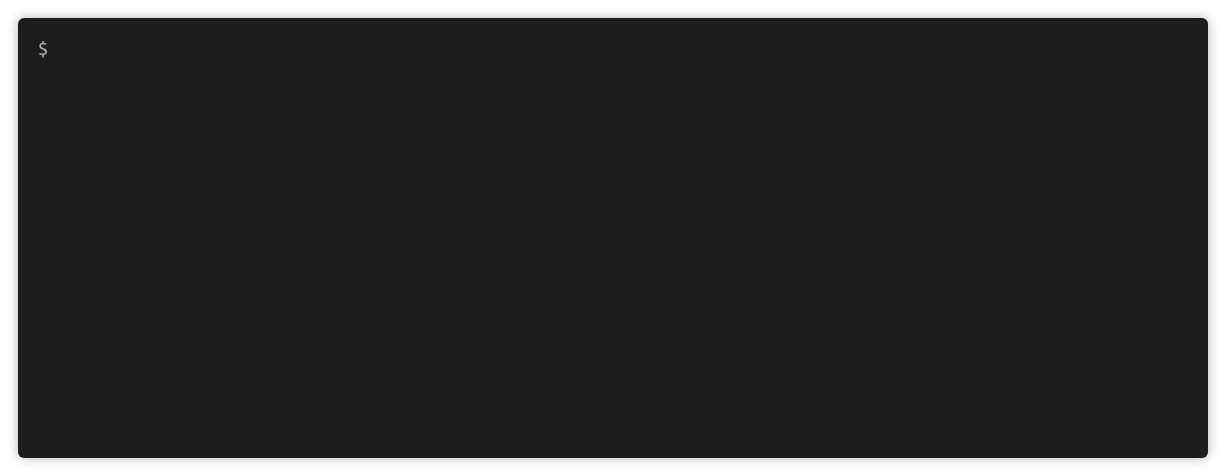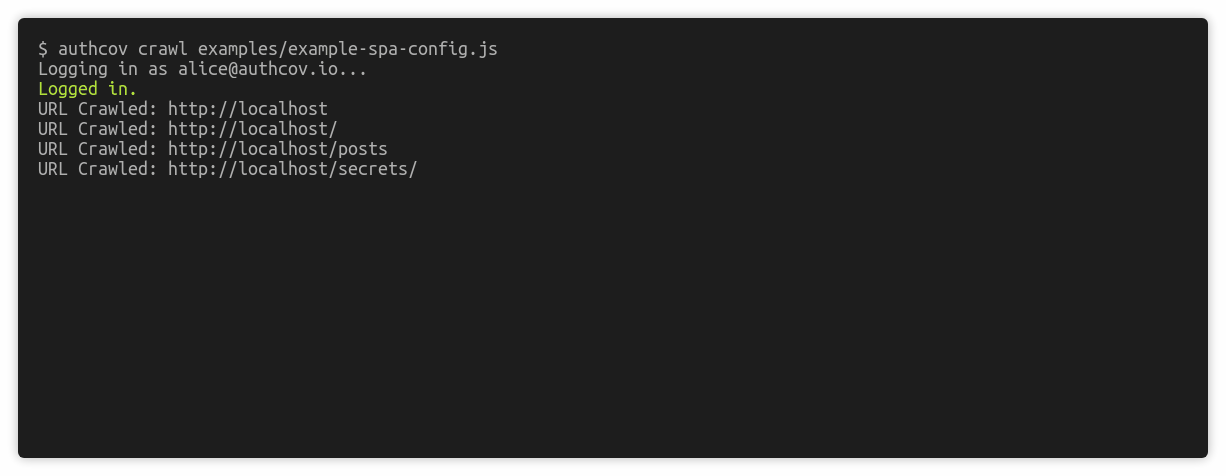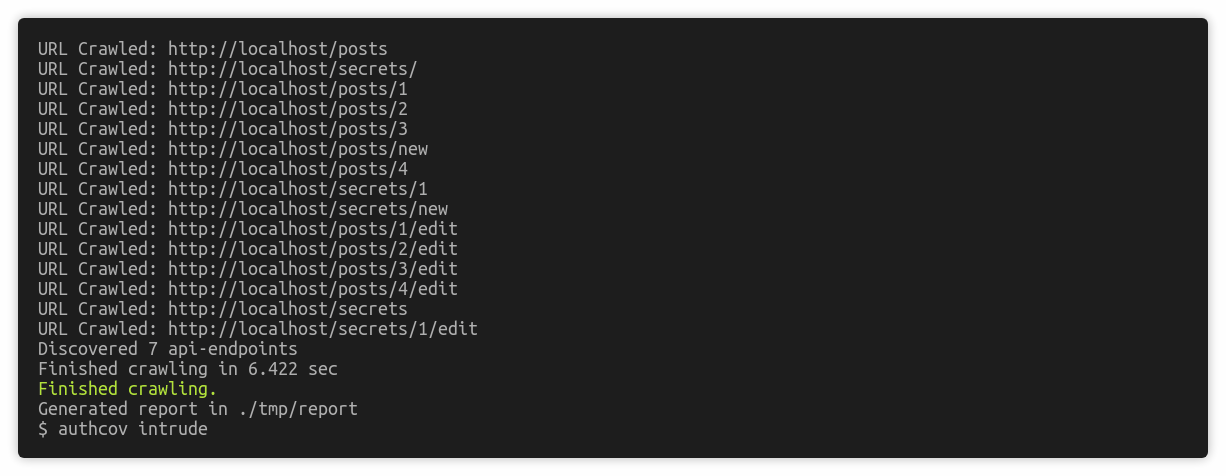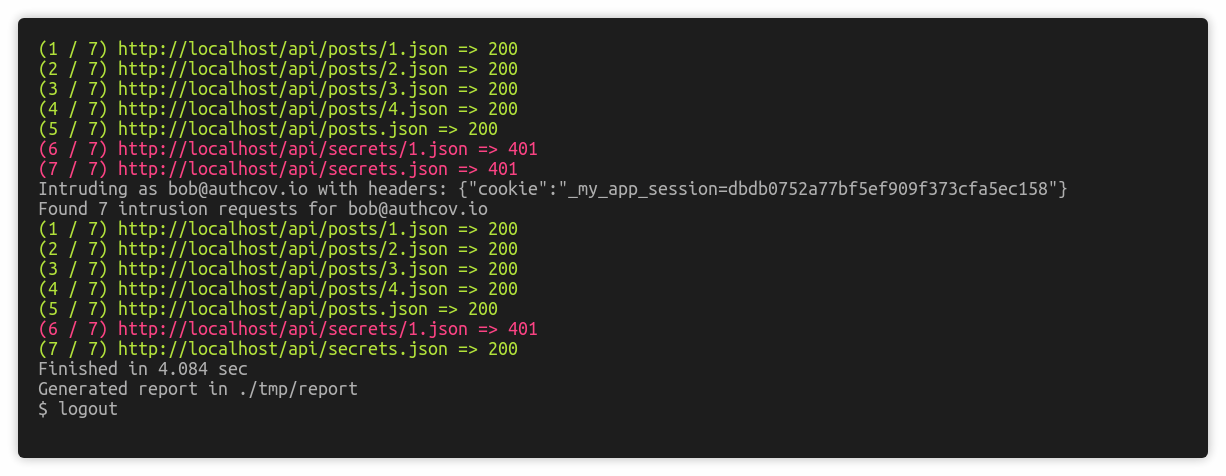 authcov/authcov
Web app authorisation coverage scanning
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through the Remote Debugging…
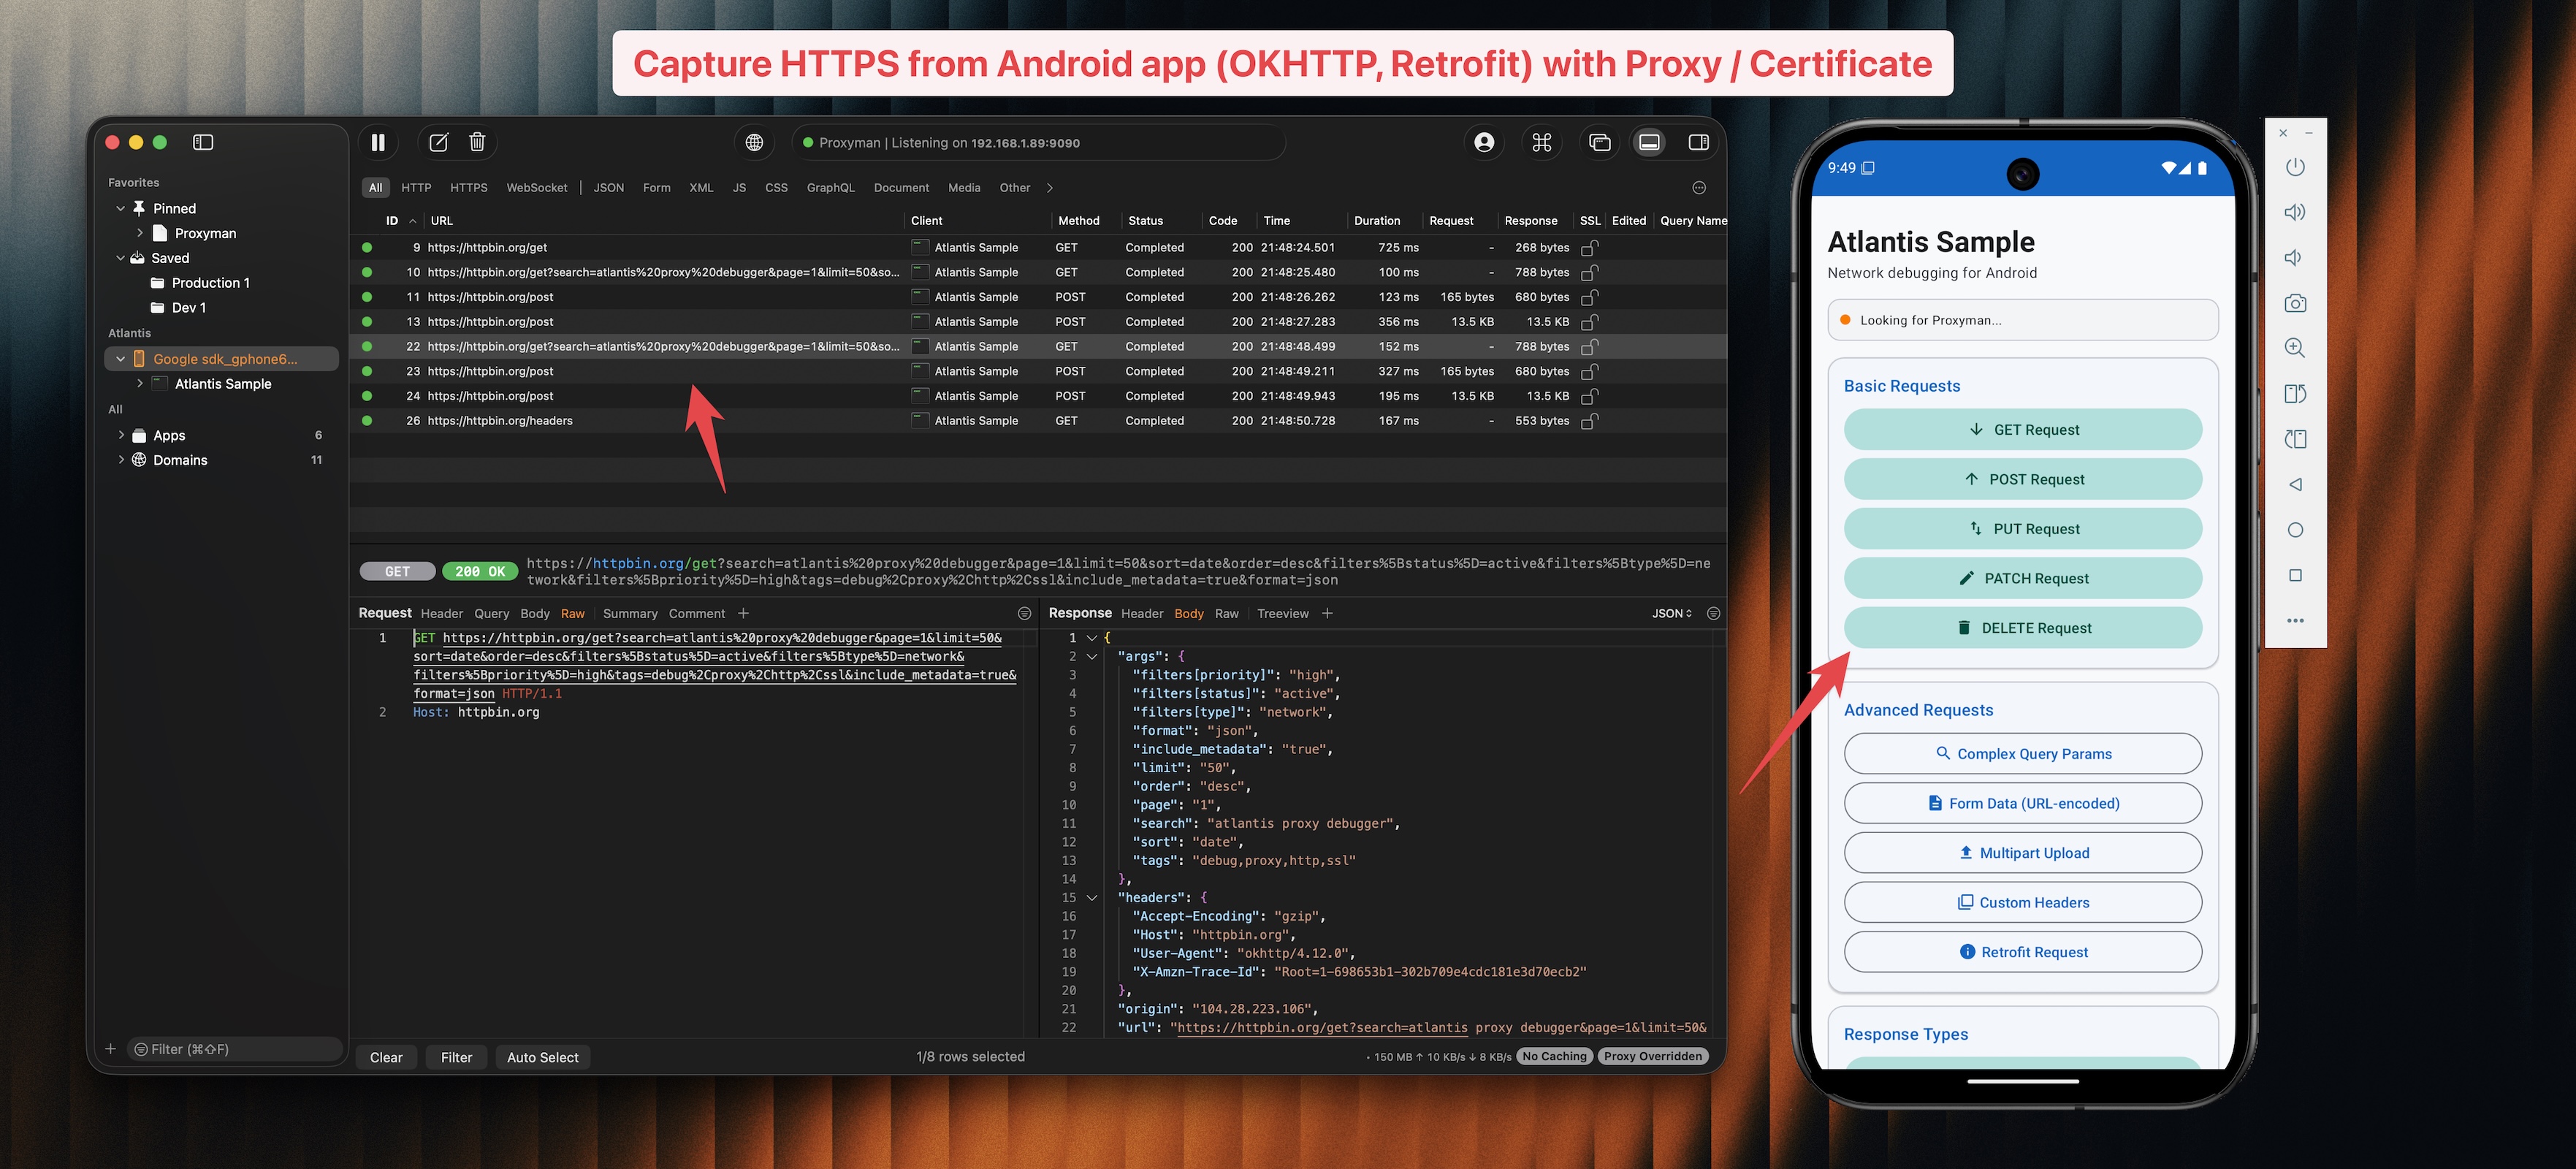 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…