

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
380 results
APIHarvester preview

APIHarvester

GitHubpiratesshield/apiharvester

The one shot API attacker tool - finds the API url from the given root simulate the automated attacks

api-securityapi-security-testingcrawler+9
32
2 months ago
ActiveScanPlusPlus preview

ActiveScanPlusPlus

GitHubalbinowax/activescanplusplus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
api-security-testingdefensive-toolsexploitation+7
66717 days ago
selenium-wire preview
Archived

selenium-wire

GitHubwkeeling/selenium-wire

Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
api-security-testinginformation-gatheringpenetration-testing+2
2.0k2 years ago
martian preview
Archived

martian

GitHubgoogle/martian

Martian is a library for building custom HTTP/S proxies

api-security-testingdynamic-analysis-sandboxingpenetration-testing+3
2.0k1 year ago
GraphCrawler preview
Archived

GraphCrawler

GitHubgsmith257-cyber/graphcrawler

GraphQL automated security testing toolkit

api-security-testinginformation-gatheringreconnaissance+3
3342 years ago
brokeCLAUDIA preview
Archived

brokeCLAUDIA

GitHubthemalwareguardian/brokeclaudia

CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
api-security-testingeducationexploitation+3
311 months ago
burp-rest-api preview
Archived

burp-rest-api

GitHubvmware-archive/burp-rest-api

REST/JSON API to the Burp Suite security tool.
api-security-testingpenetration-testingscripting-automation+4
5661 year ago
raider preview
Archived

raider

GitHubdigeex/raider

DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
api-security-testingauthenticationpenetration-testing+1
1395 years ago
hackazon preview
Archived

hackazon

GitHubrapid7/hackazon

A modern vulnerable web app
api-security-testingeducationpenetration-testing+3
1.0k5 years ago
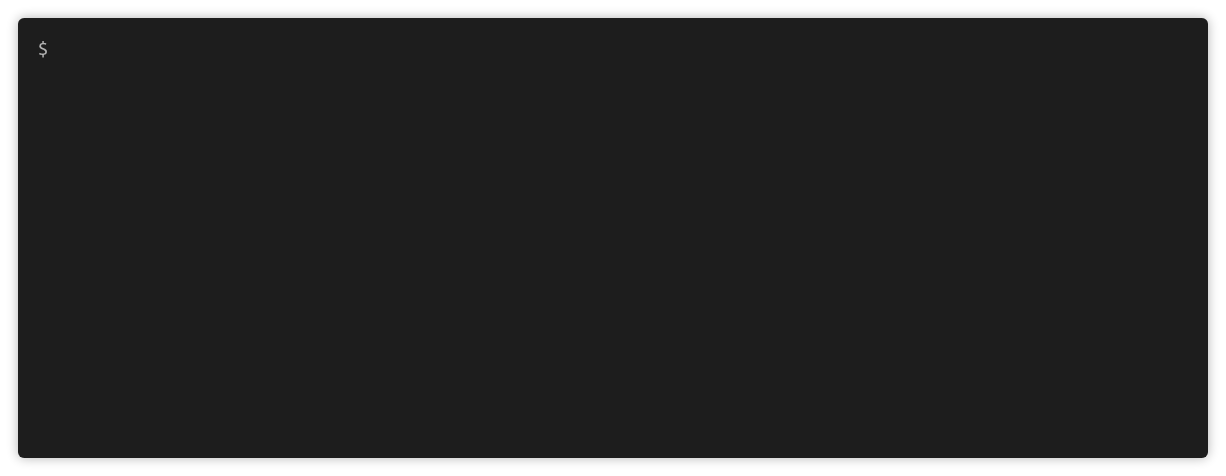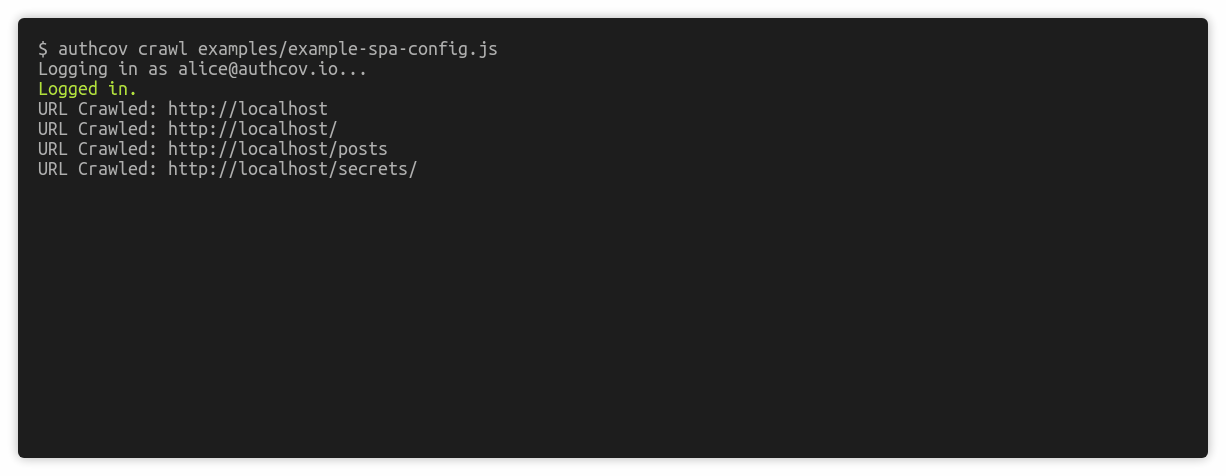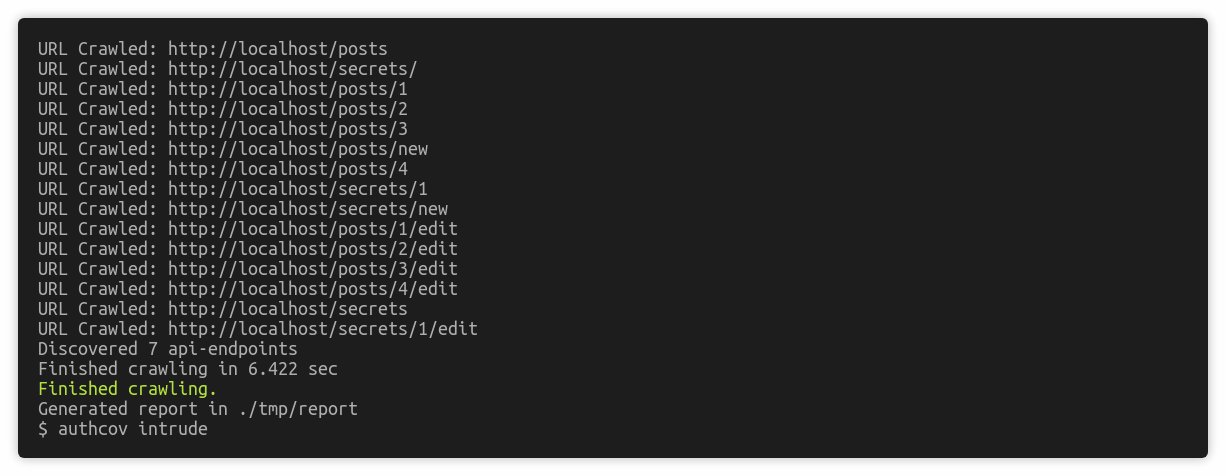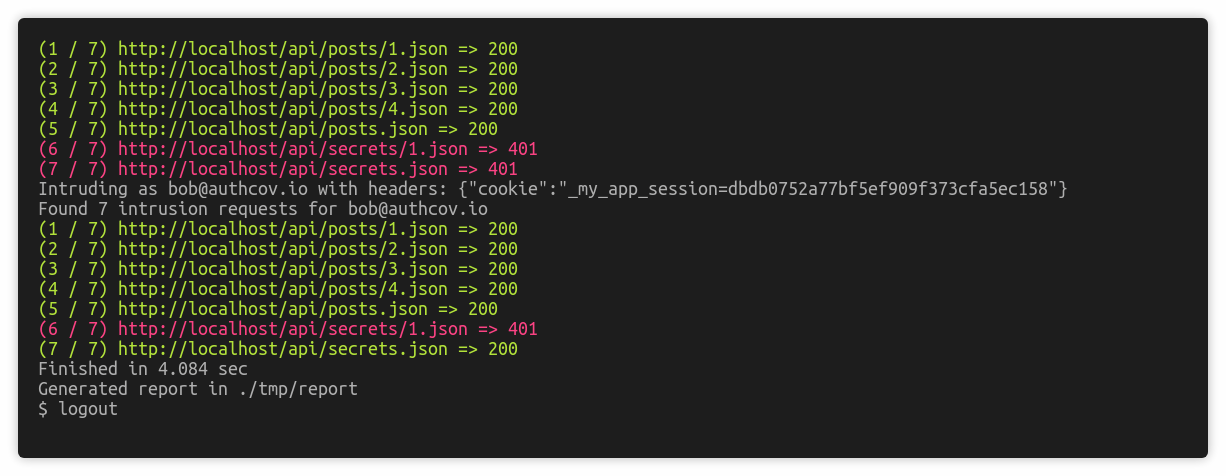
authcov preview
Archived

authcov

GitHubauthcov/authcov

Web app authorisation coverage scanning

api-security-testingauthentication-authorizationcrawler+3
2323 years ago
request_smuggler preview
Archived

request_smuggler

GitHubsh1yo/request_smuggler

Http request smuggling vulnerability scanner
api-security-testingpenetration-testingvulnerability-scanners+3
2284 years ago
syntribos preview
Archived

syntribos

GitHubopenstack-archive/syntribos

Python API security testing tool from OpenStack Security Group

api-security-testingfuzzingpenetration-testing+2
2716 years ago
frida-fuzzer preview
Archived

frida-fuzzer

GitHubandreafioraldi/frida-fuzzer

This experimetal fuzzer is meant to be used for API in-memory fuzzing.
api-security-testingbinary-analysisdynamic-analysis-sandboxing+3
5776 years ago
toxy preview
Archived

toxy

GitHubh2non/toxy

Hackable HTTP proxy for resiliency testing and simulated network conditions

api-security-testingchaos-engineeringnetwork-security+3
2.7k4 years ago
repeat-strike preview

repeat-strike

GitHubhackvertor/repeat-strike

Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
ai-securityapi-security-testinginformation-gathering+6
411 year ago
nogotofail preview
Archived

nogotofail

GitHubgoogle/nogotofail

An on-path blackbox network traffic security testing tool
api-security-testingmobile-securitynetwork-security+3
3.0k4 years ago
burp-extensions-montoya-api-examples preview

burp-extensions-montoya-api-examples

GitHubportswigger/burp-extensions-montoya-api-examples

Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…

api-security-testingeducationpenetration-testing+6
1873 months ago
active-scan-plus-plus preview

active-scan-plus-plus

GitHubportswigger/active-scan-plus-plus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

api-security-testingdefensive-toolspenetration-testing+6
2572 months ago
Previous1…202122Next