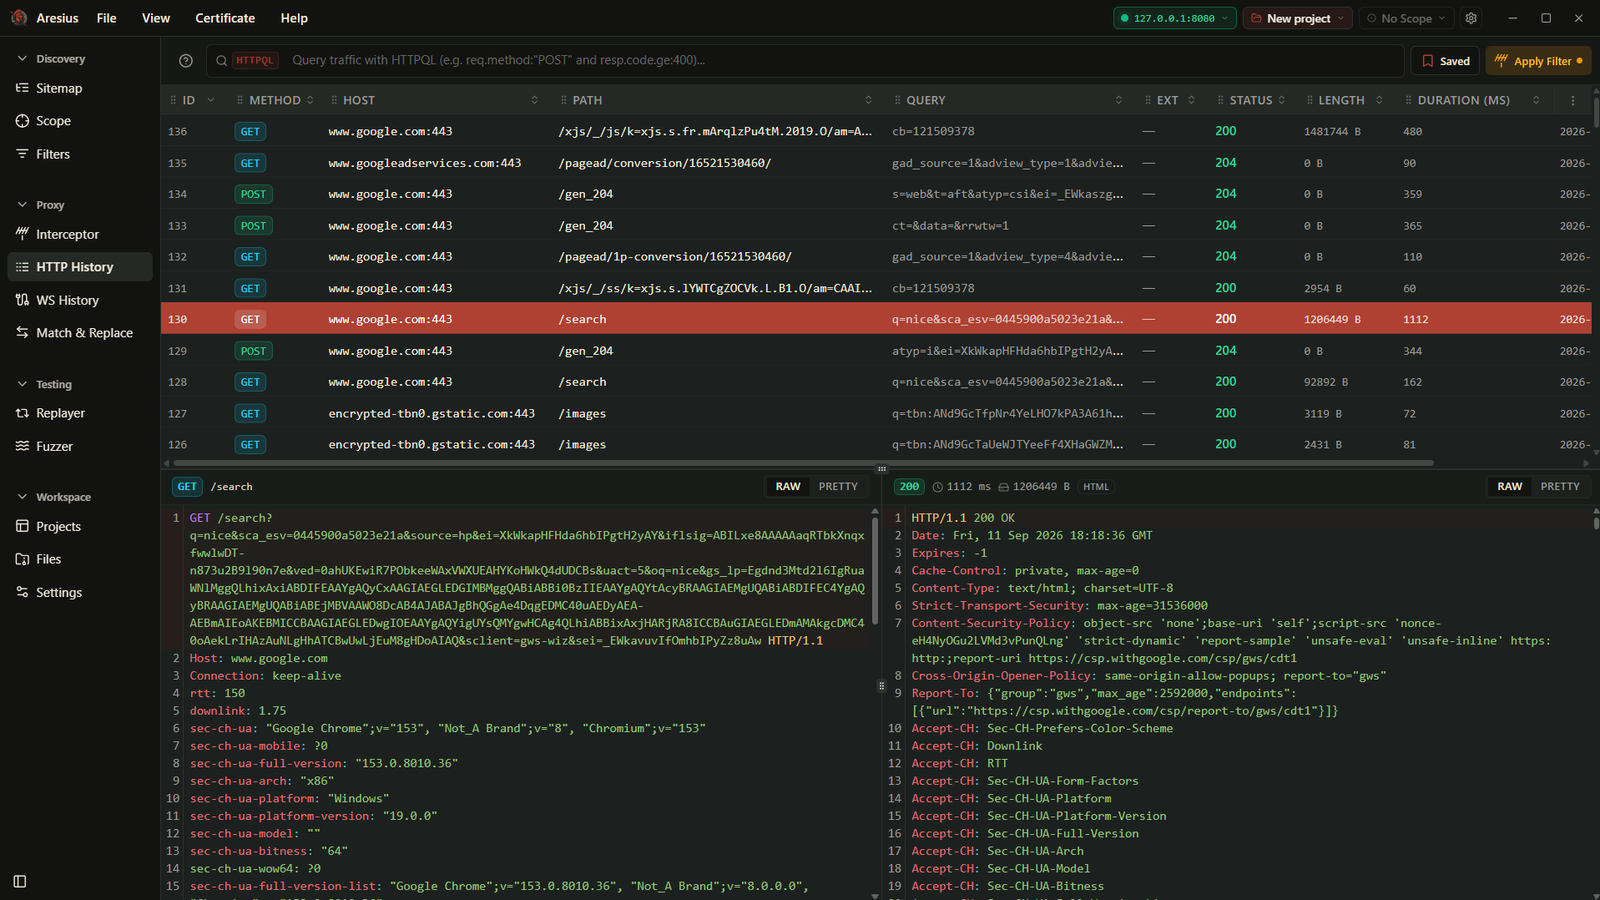
Aresius
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
api-security-testingfuzzinginformation-gathering+6
2
0xmarik/aresiusNative HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 google/martian
Martian is a library for building custom HTTP/S proxies
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…
 themalwareguardian/brokeclaudia
CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 rapid7/hackazon
A modern vulnerable web app
 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
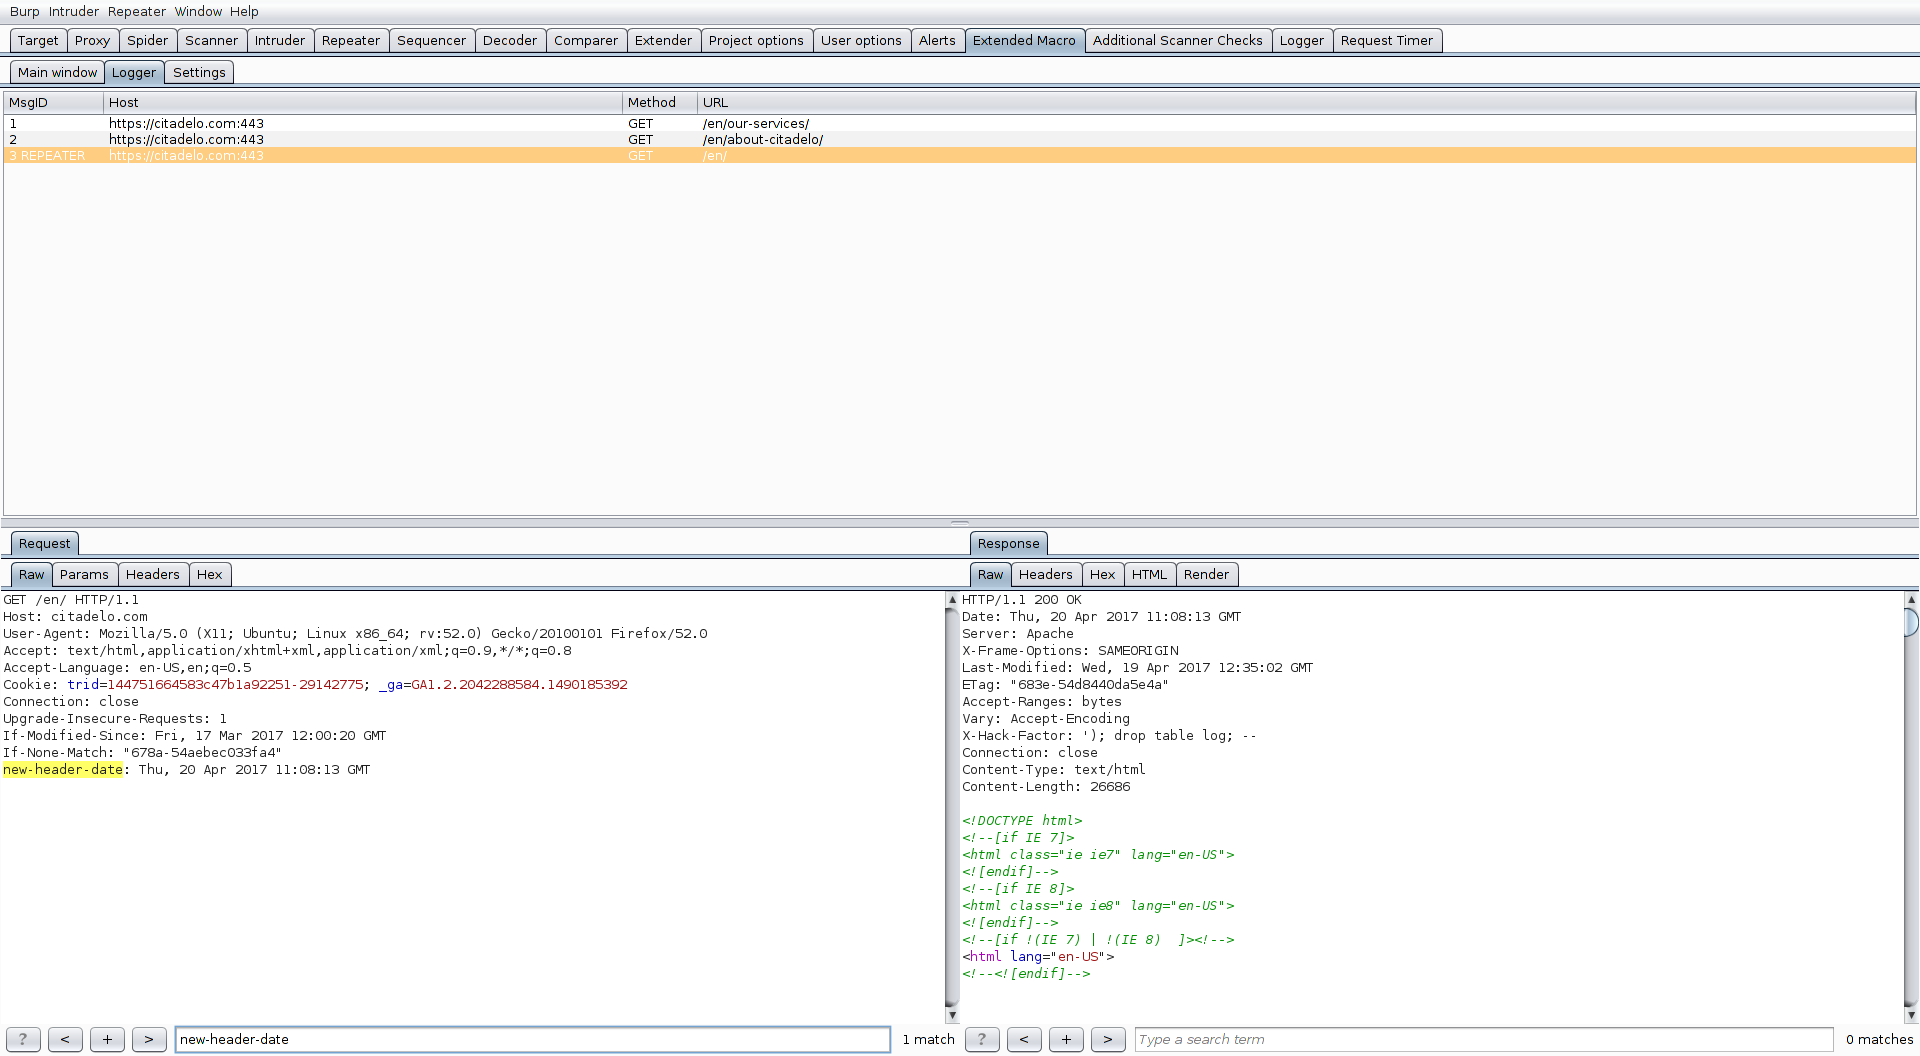 fruh/extendedmacro
ExtendedMacro - BurpSuite plugin providing extended macro functionality
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
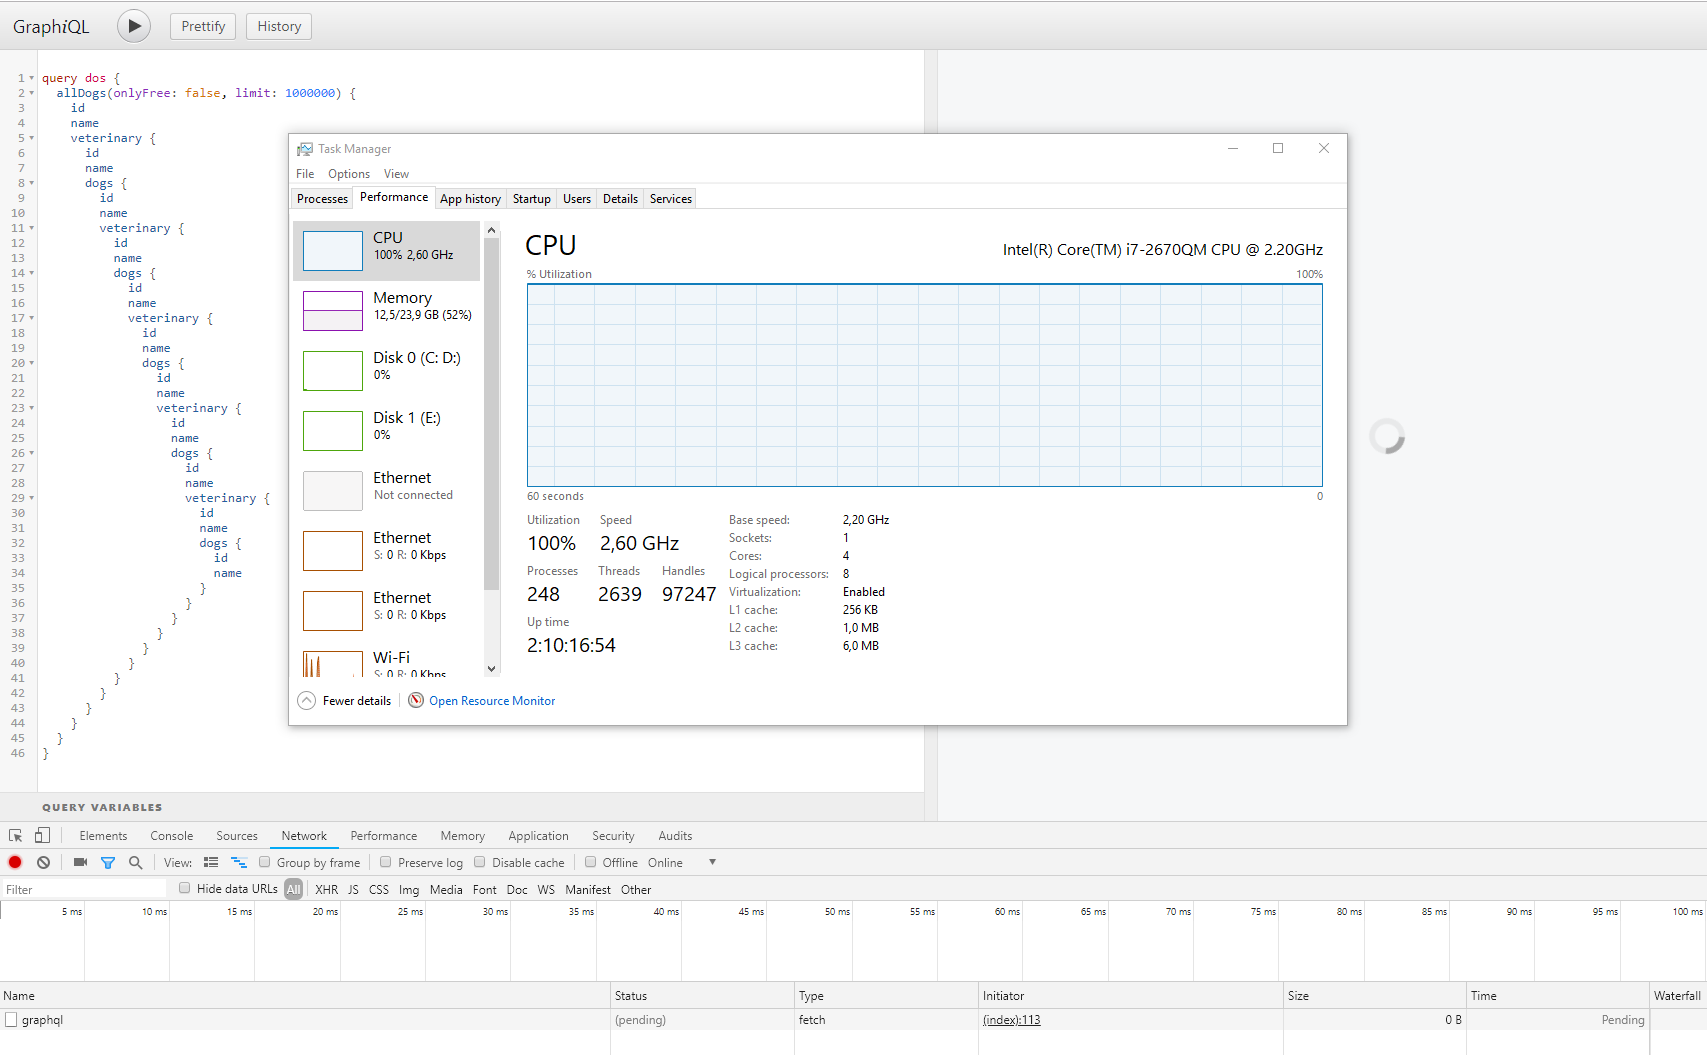 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…
 google/nogotofail
An on-path blackbox network traffic security testing tool