Detect_polyfill_CVE-2024-38537-

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.

Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测

GraphQL automated security testing toolkit

This experimetal fuzzer is meant to be used for API in-memory fuzzing.

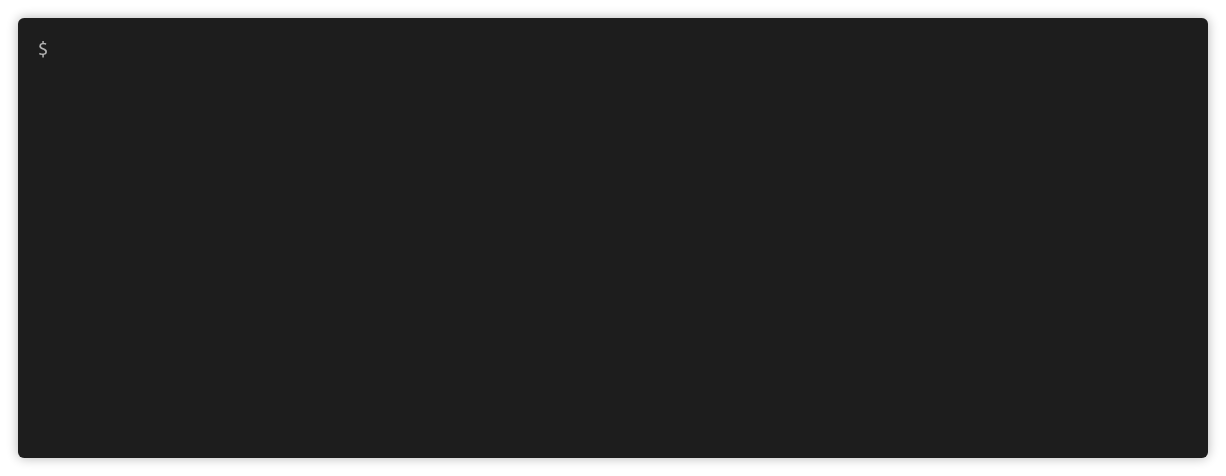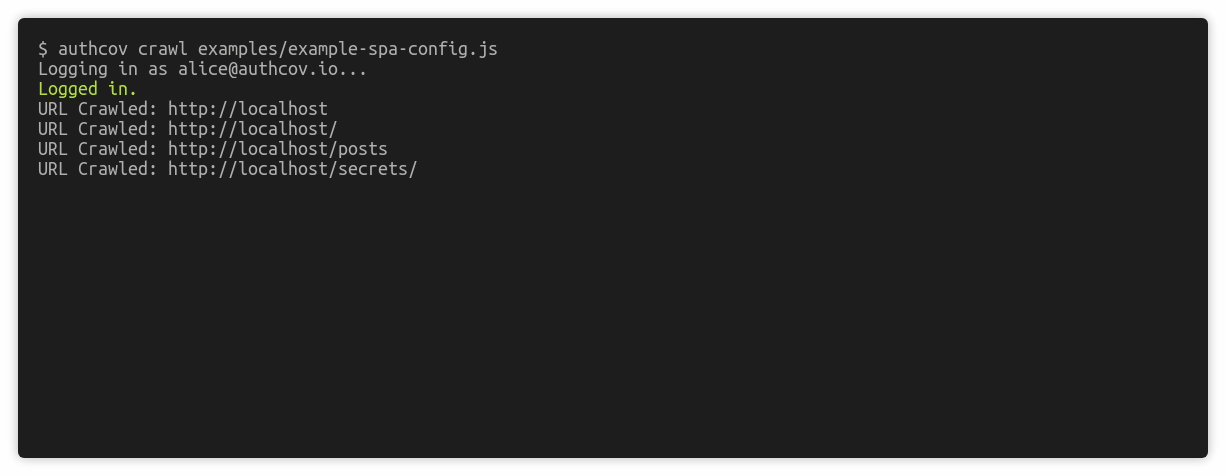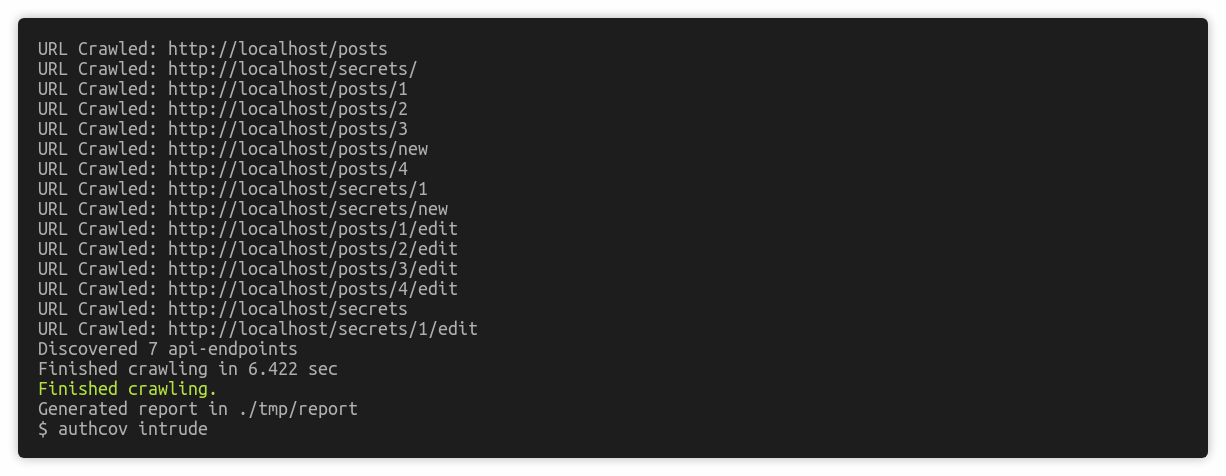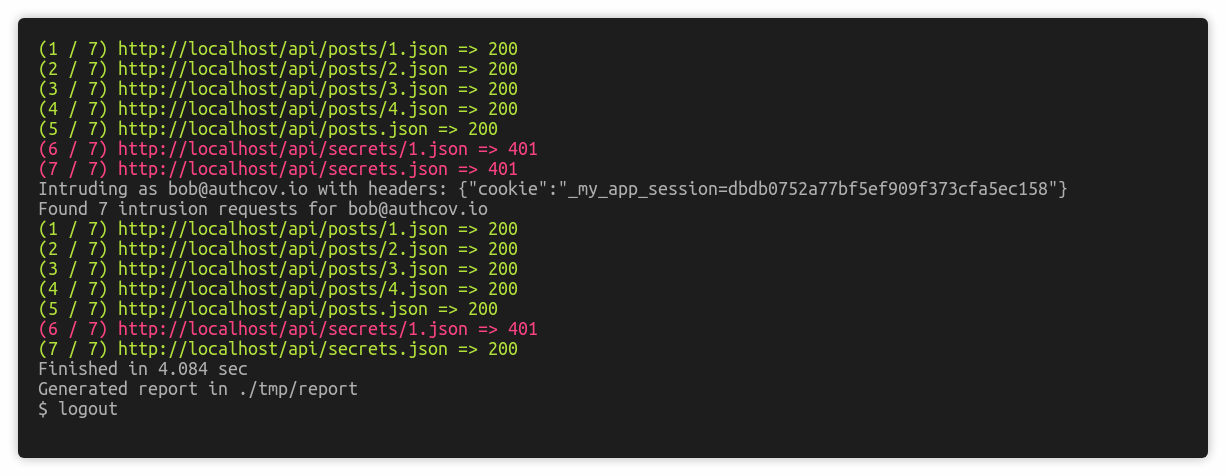
Web app authorisation coverage scanning

Python API security testing tool from OpenStack Security Group

REST/JSON API to the Burp Suite security tool.

An on-path blackbox network traffic security testing tool

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…

Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…

Executable security regression testing for agentic applications and MCP-integrated systems.

DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider

🥧 HTTPie CLI — modern, user-friendly command-line HTTP client for the API era. JSON support, colors, sessions, downloads, plugins & more.

Lightweight service virtualization/ API simulation / API mocking tool for developers and testers

HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…