
cve-2026-19478
 n0xdaemon/cve-2026-19478
Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…
api-security-testingexploitationvulnerability-analysis+2
n0xdaemon/cve-2026-19478Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…
 filipegaudard/cve-2026-35045-poc
Proof-of-concept exploit for CVE-2026-35045, a broken object-level authorization vulnerability in Tandoor Recipes, demonstrating unauthorized recipe…
 y-security/ylog4j
PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 richard-natan/poc-cve-2025-63406
Proof-of-concept for CVE-2025-63406 in GroupOffice, demonstrating API-based object manipulation and authentication flow for vulnerability analysis…
 lstudlo/nextjs-cve-demo
演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。
 dylvie/cve-2026-30824-flowise-nvidia-nim-authentication
A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 learner202649/cve-2025-45809-poc
Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…
 jfriedli/cve-2025-11771
Proof-of-concept exploit for CVE-2025-11771 demonstrating unauthenticated sale record creation via a WordPress REST API endpoint, with browser…
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 jfriedli/cve-2025-6783
Proof-of-concept exploit for CVE-2025-6783 demonstrating SQL injection via crafted HTTP headers and JSON payload against WordPress GoZen Forms REST…
 evtdanya/cve-2026-27886
Strapi CVE-2026-27886. Leaking sensitive data via relational filtering due to lack of query sanitization
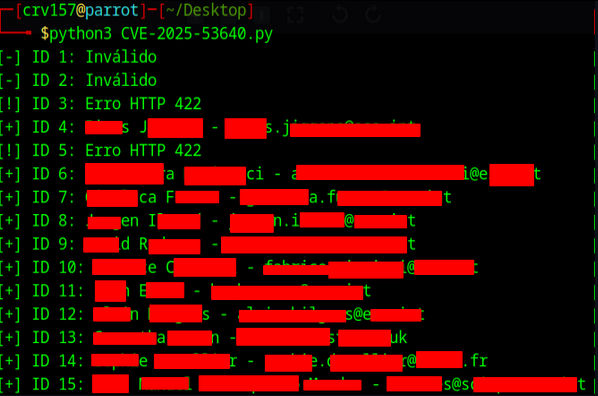 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.
 jfriedli/cve-2025-6792
Proof-of-concept exploit for CVE-2025-6792 demonstrating unauthorized Pusher channel subscription and event eavesdropping in a WordPress plugin via…
 7megaumka7/foskiller
FOSSBilling CVE-2026-53647 & CVE-2026-53646 PoC — Unauthenticated API key disclosure & password reset token reuse
 rootdirective-sec/cve-2026-46645-analysis-lab
Docker-based lab for reproducing CVE-2026-46645, an authorization bypass in SQLAdmin's ajax_lookup endpoint. Includes vulnerable and patched targets,…
 blankbire/cve-2026-24136-lab
CVE-2026-24136 | Lab khai thác lỗ hổng IDOR trên Saleor GraphQL - query order() không kiểm tra xác thực, lộ toàn bộ PII (email, địa chỉ, SĐT) của…