
Archived
toxy
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
vulnerability-analysisweb-proxies-interceptionapi-security-testing+3
2.7k
 google/martian
Martian is a library for building custom HTTP/S proxies
 rapid7/hackazon
A modern vulnerable web app
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
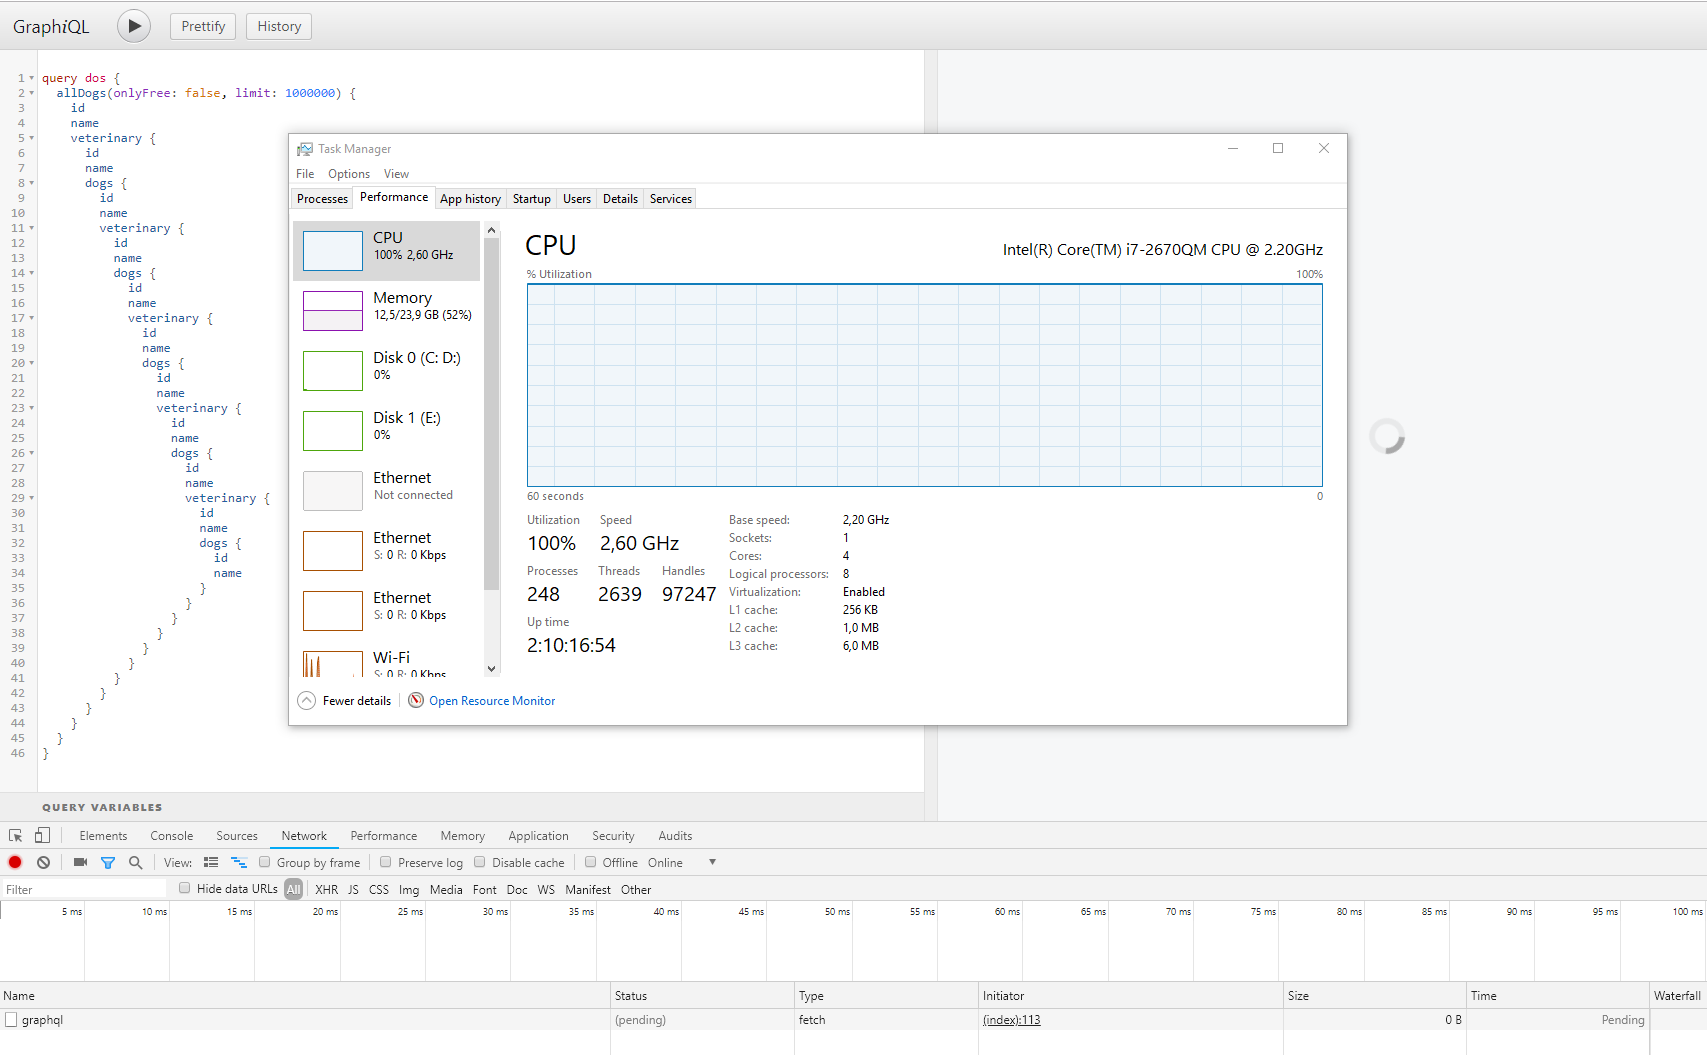 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
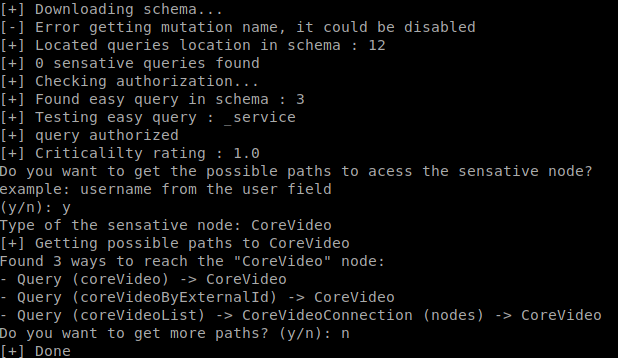 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
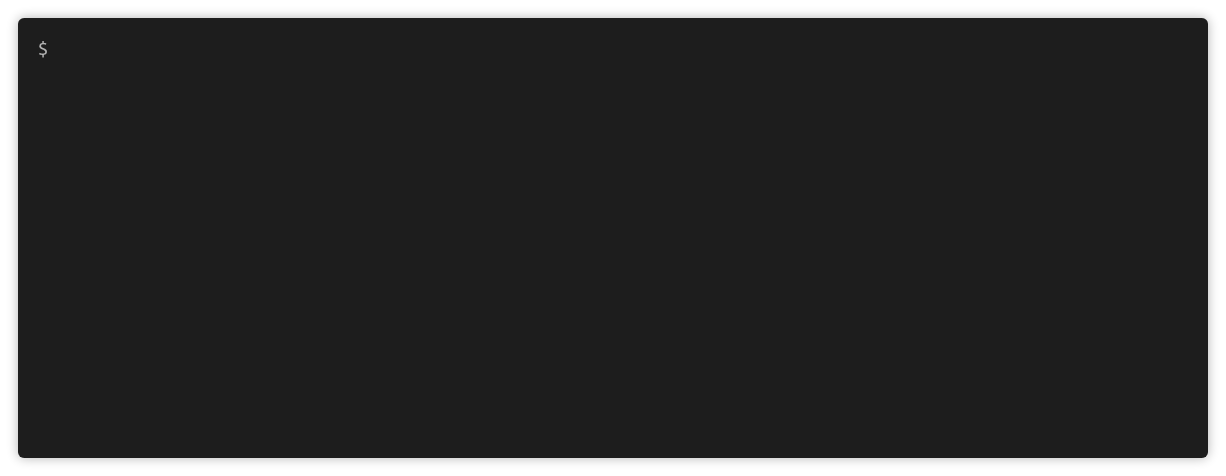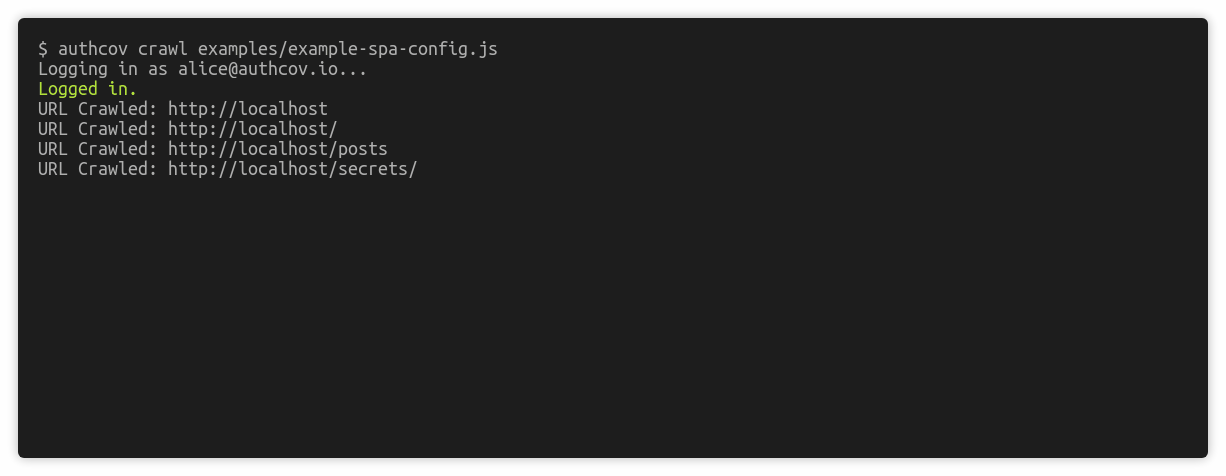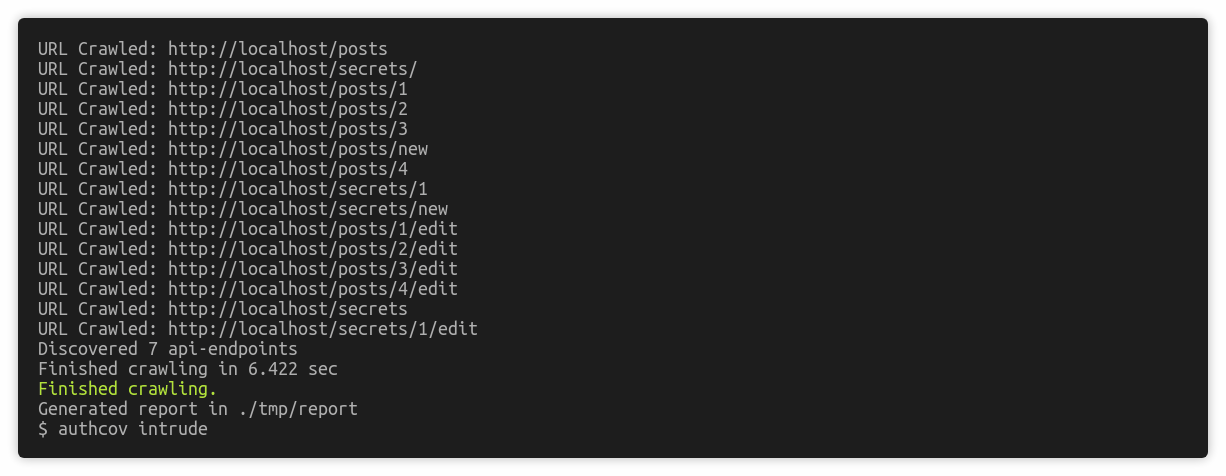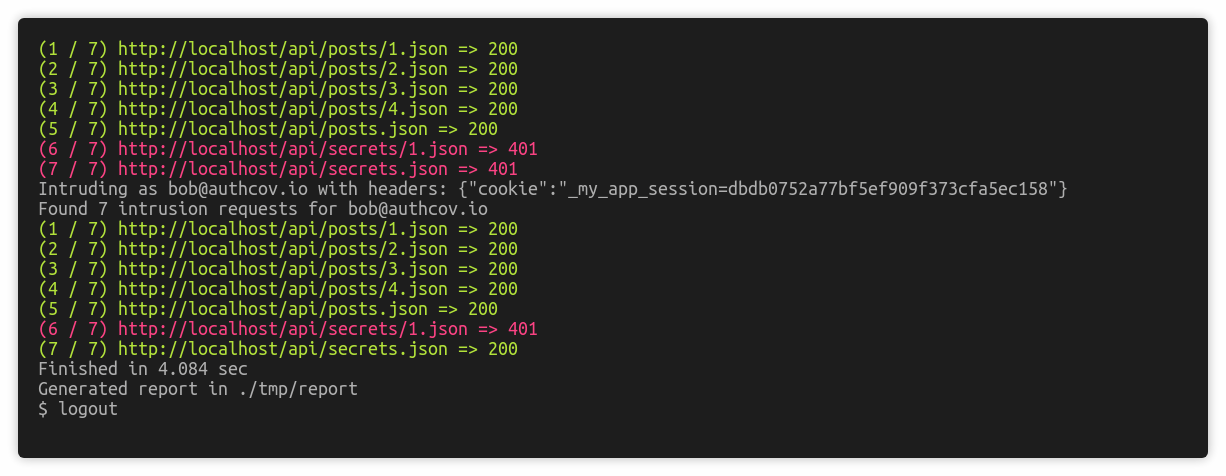 authcov/authcov
Web app authorisation coverage scanning
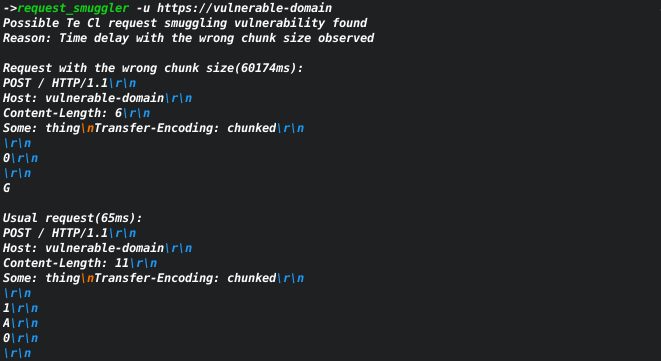 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…
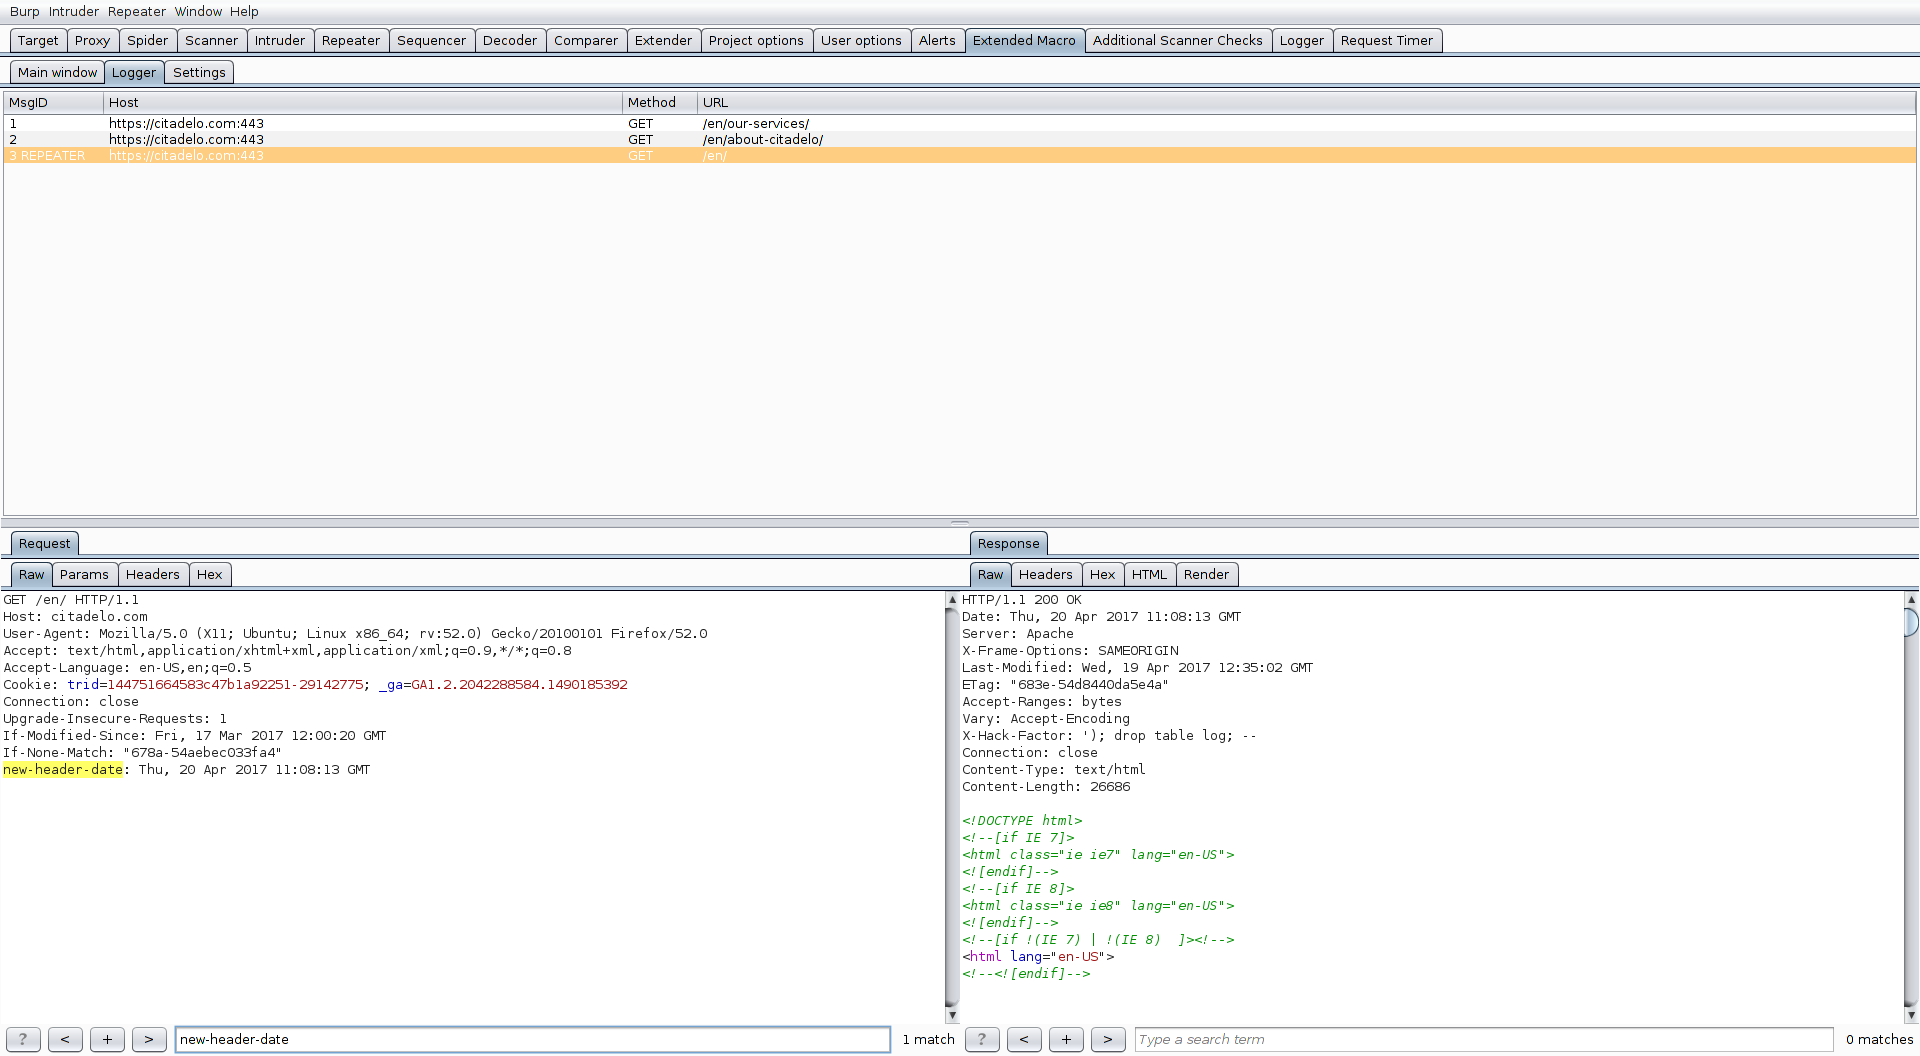 fruh/extendedmacro
ExtendedMacro - BurpSuite plugin providing extended macro functionality
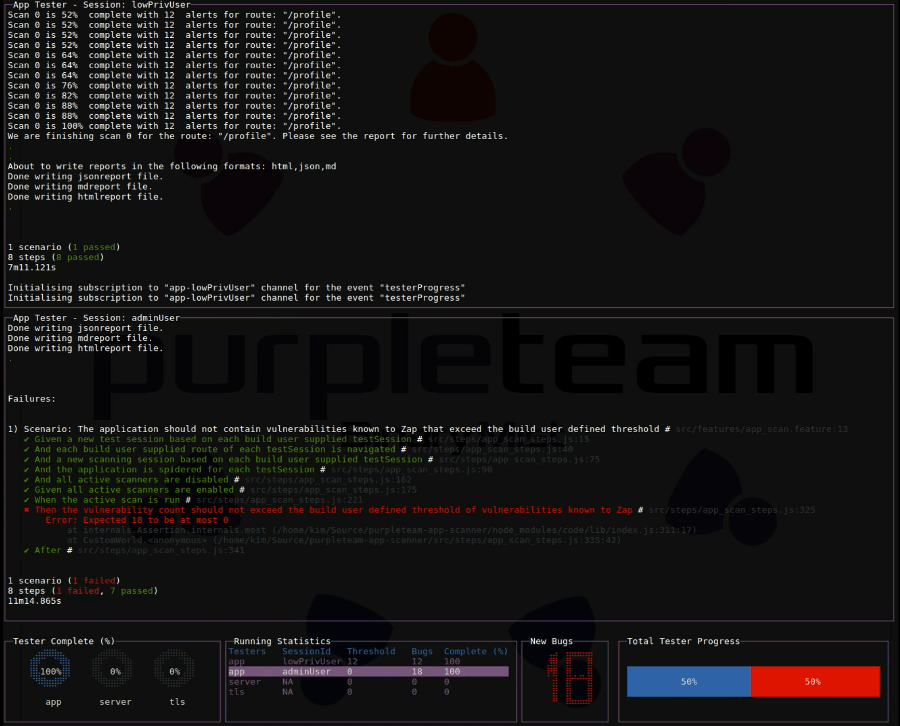
 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam