

Archived
frida-fuzzer
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
dynamic-analysis-sandboxingexploitationapi-security-testing+3
andreafioraldi/frida-fuzzerThis experimetal fuzzer is meant to be used for API in-memory fuzzing.
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
 infobyte/alexafaraday
Alexa skill example for Faraday API
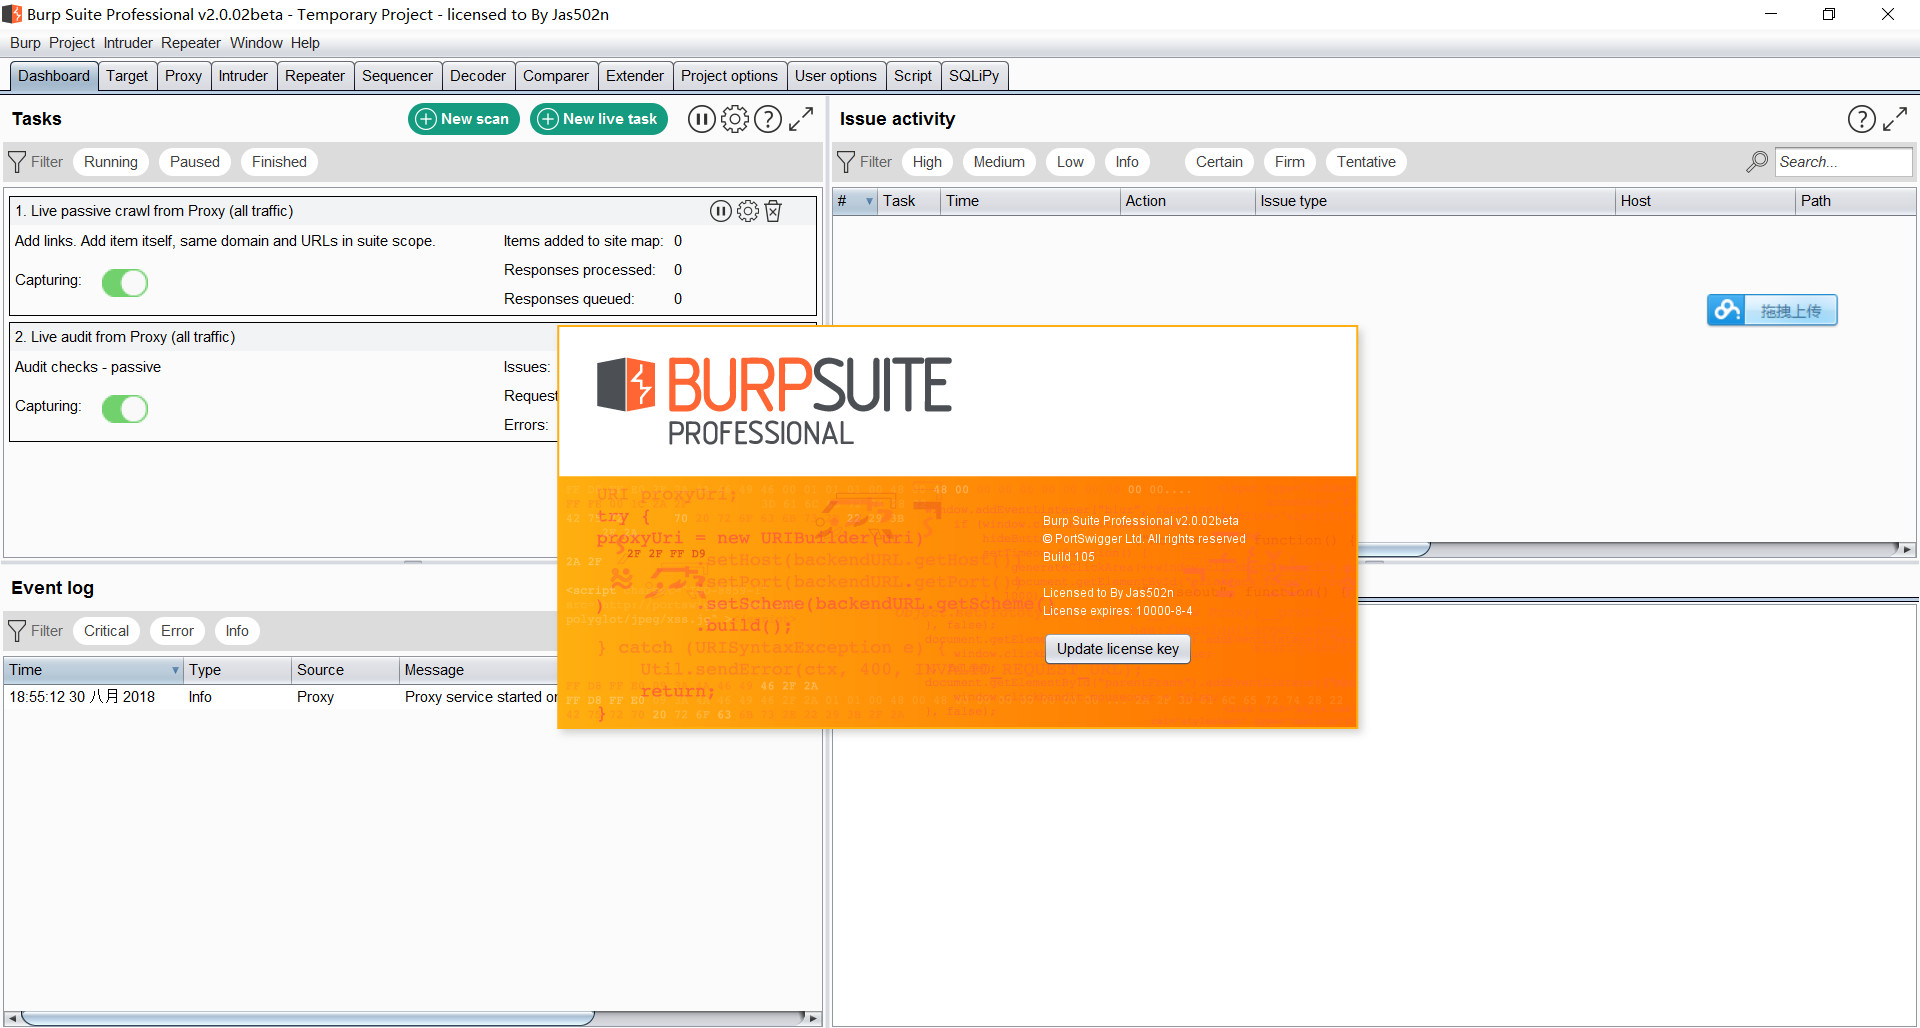 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 joanbono/gurp
Burp Commander written in Go
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 deepseasred/autonessus
This script communicates with the Nessus API in an attempt to help with automating scans. Depending on the flag issued with the script, you can list…
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 subgraph/vega
Subgraph Vega
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library
 ajinabraham/oauth-request-crafter
OAuth Request Crafter
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite