

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
22 results
-LogicSentry-AI preview

-LogicSentry-AI

GitHubvighnesh91/-logicsentry-ai

Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…

ai-securityapi-security-testingcode-analysis+9
1
20 days ago
active-scan-plus-plus preview

active-scan-plus-plus

GitHubportswigger/active-scan-plus-plus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

api-security-testingdefensive-toolspenetration-testing+6
2597 days ago
WebSocketTurboIntruder preview

WebSocketTurboIntruder

GitHubd0ge/websocketturbointruder

Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
api-security-testingfuzzingpenetration-testing+5
121 year ago
CVE-2025-59528-PoC preview

CVE-2025-59528-PoC

GitHubloaxert/cve-2025-59528-poc

PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB

api-security-testingeducationexploitation+3
2 months ago
wp2shell-Exploit-Waf-Bypass preview

wp2shell-Exploit-Waf-Bypass

GitHubm4xsec/wp2shell-exploit-waf-bypass

WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
api-security-testingexploitationpenetration-testing+4
52 months ago
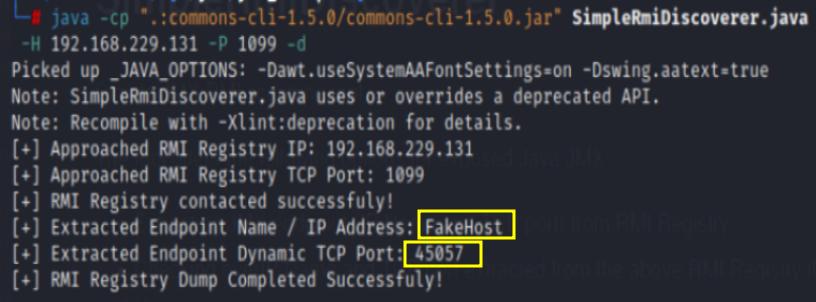
SimpleRmiDiscoverer preview

SimpleRmiDiscoverer

GitHubmarcin-wolak/simplermidiscoverer

Simple JMX RMI scanning tool
api-security-testinginformation-gatheringmisconfiguration+2
42 years ago
Arisu preview

Arisu

GitHubrazureink/arisu

Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
api-security-testingcrawlerinformation-gathering+2
1 month ago
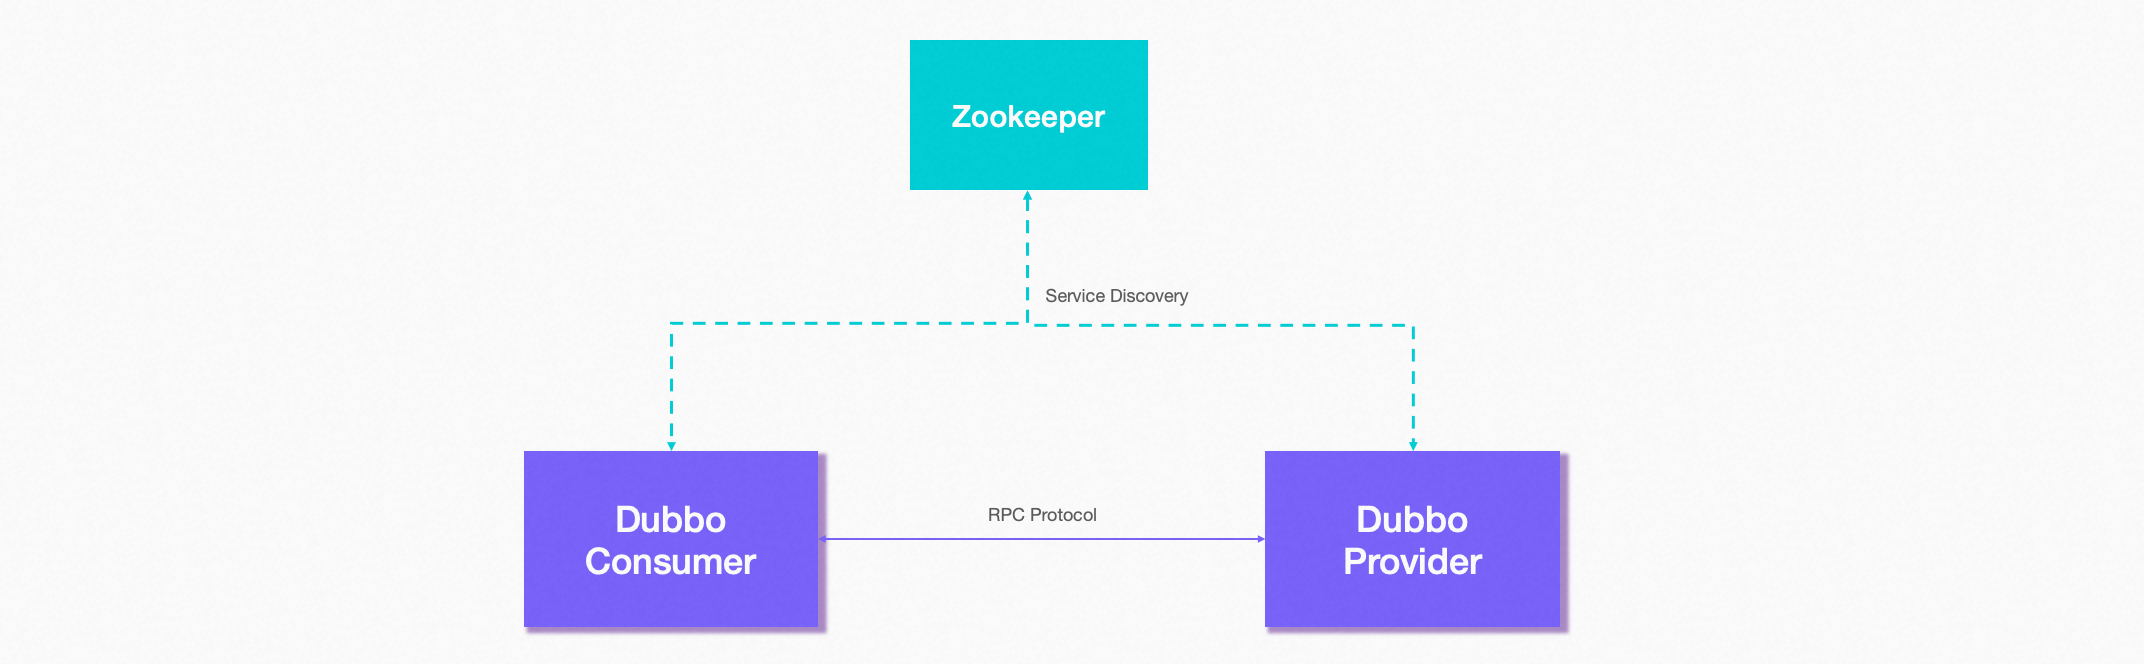
apache__dubbo_CVE-2021-30180_2-7-9 preview

apache__dubbo_CVE-2021-30180_2-7-9

GitHubshoucheng3/apache__dubbo_cve-2021-30180_2-7-9

Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
api-securityapi-security-testingexploitation+3
1 year ago
CVE-2026-47101-PoC preview

CVE-2026-47101-PoC

GitHublearner202649/cve-2026-47101-poc

The code for personally reproducing the corresponding vulnerability
api-security-testingauthentication-authorizationeducation+7
5 months ago
r2s preview

r2s

GitHubmxm0z/r2s

A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
api-security-testingcloud-securityexploitation+3
10 months ago
bug-reaper preview

bug-reaper

GitHubshaniidev/bug-reaper

Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
api-security-testingctfeducation+8
758 months ago
Apache-APISIX-CVE-2022-24112 preview

Apache-APISIX-CVE-2022-24112

GitHubm4xsec/apache-apisix-cve-2022-24112

Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
api-securityapi-security-testingexploitation+3
154 years ago
burp-cc-bridge preview

burp-cc-bridge

GitHublarrypeseckis/burp-cc-bridge

REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
api-security-testingpenetration-testingscripting-automation+3
74 months ago
CVE-2023-31719 preview

CVE-2023-31719

GitHubmateustesser/cve-2023-31719

Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…

api-security-testingdatabase-securityexploitation+3
3 years ago
resterm preview

resterm

GitHubunkn0wn-root/resterm

Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
api-security-testingcloud-securitydevsecops+3
2.0k1 day ago
CVE-2022-24112-POC preview

CVE-2022-24112-POC

GitHubkavishkagihan/cve-2022-24112-poc

Apache APISIX 2.12.1 Remote Code Execution by IP restriction bypass and using default admin AIP token
api-security-testingexploitationmisconfiguration+3
24 years ago
OWASP-WSTG-Rag preview

OWASP-WSTG-Rag

GitHubzilbonn/owasp-wstg-rag

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code

ai-securityapi-security-testingauthentication+8
2310 months ago
android-reverse-engineering-skill preview

android-reverse-engineering-skill

GitHubsimoneavogadro/android-reverse-engineering-skill

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

android-securityapi-security-testingbinary-analysis+8
8.5k18 days ago
Previous12Next