Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…

Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more

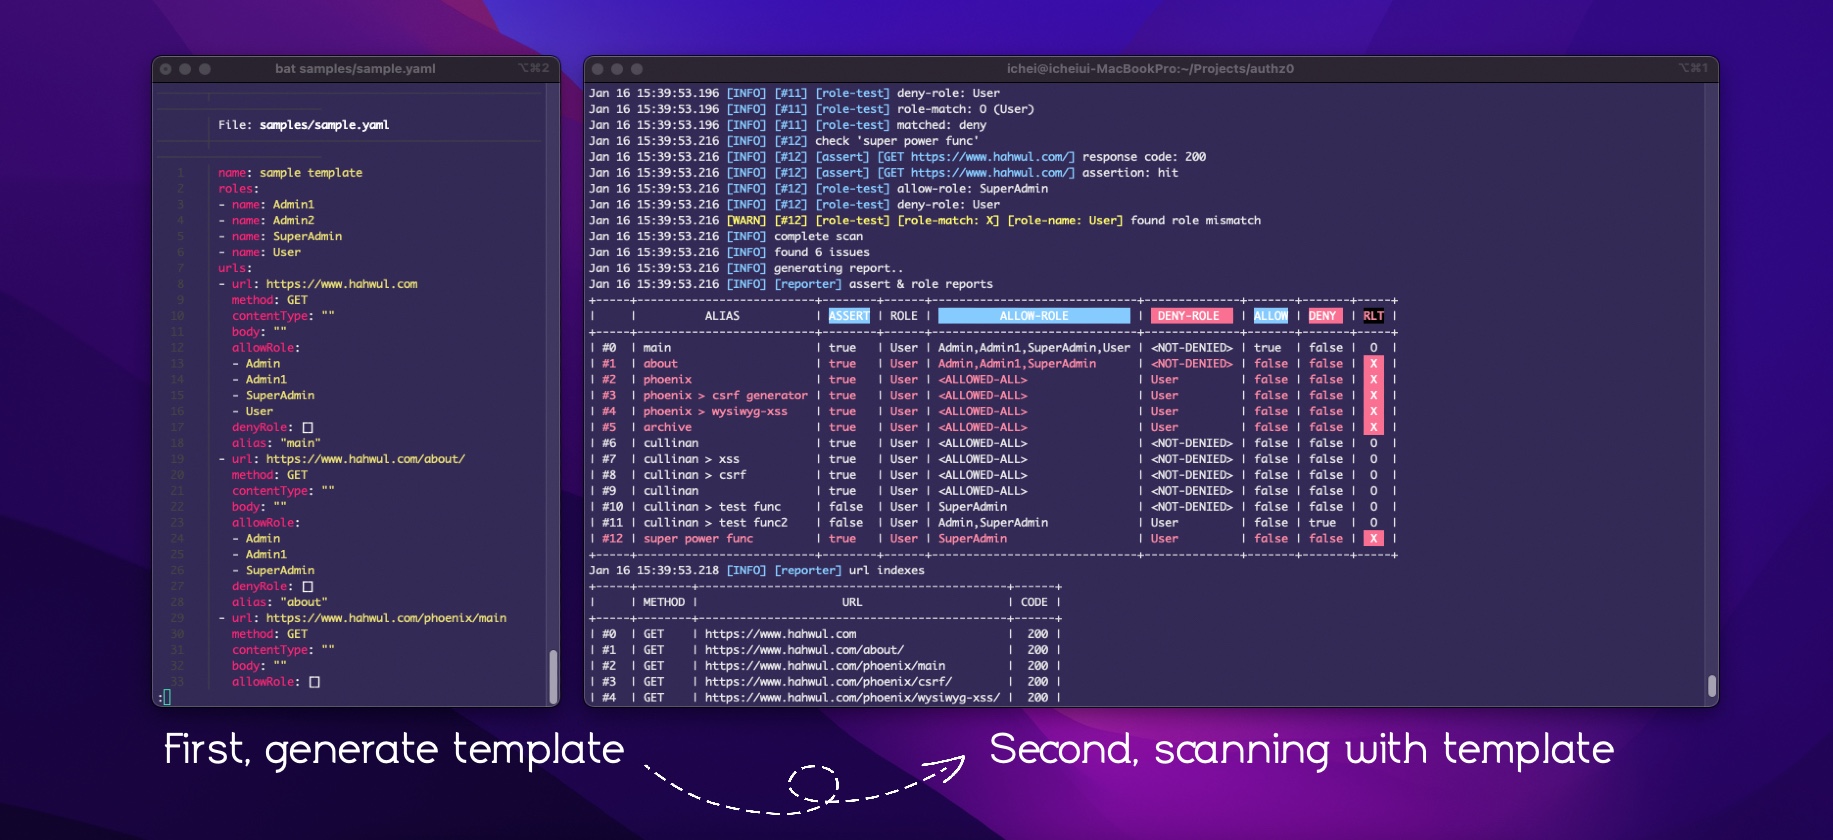
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.

REST/JSON API to the Burp Suite security tool.

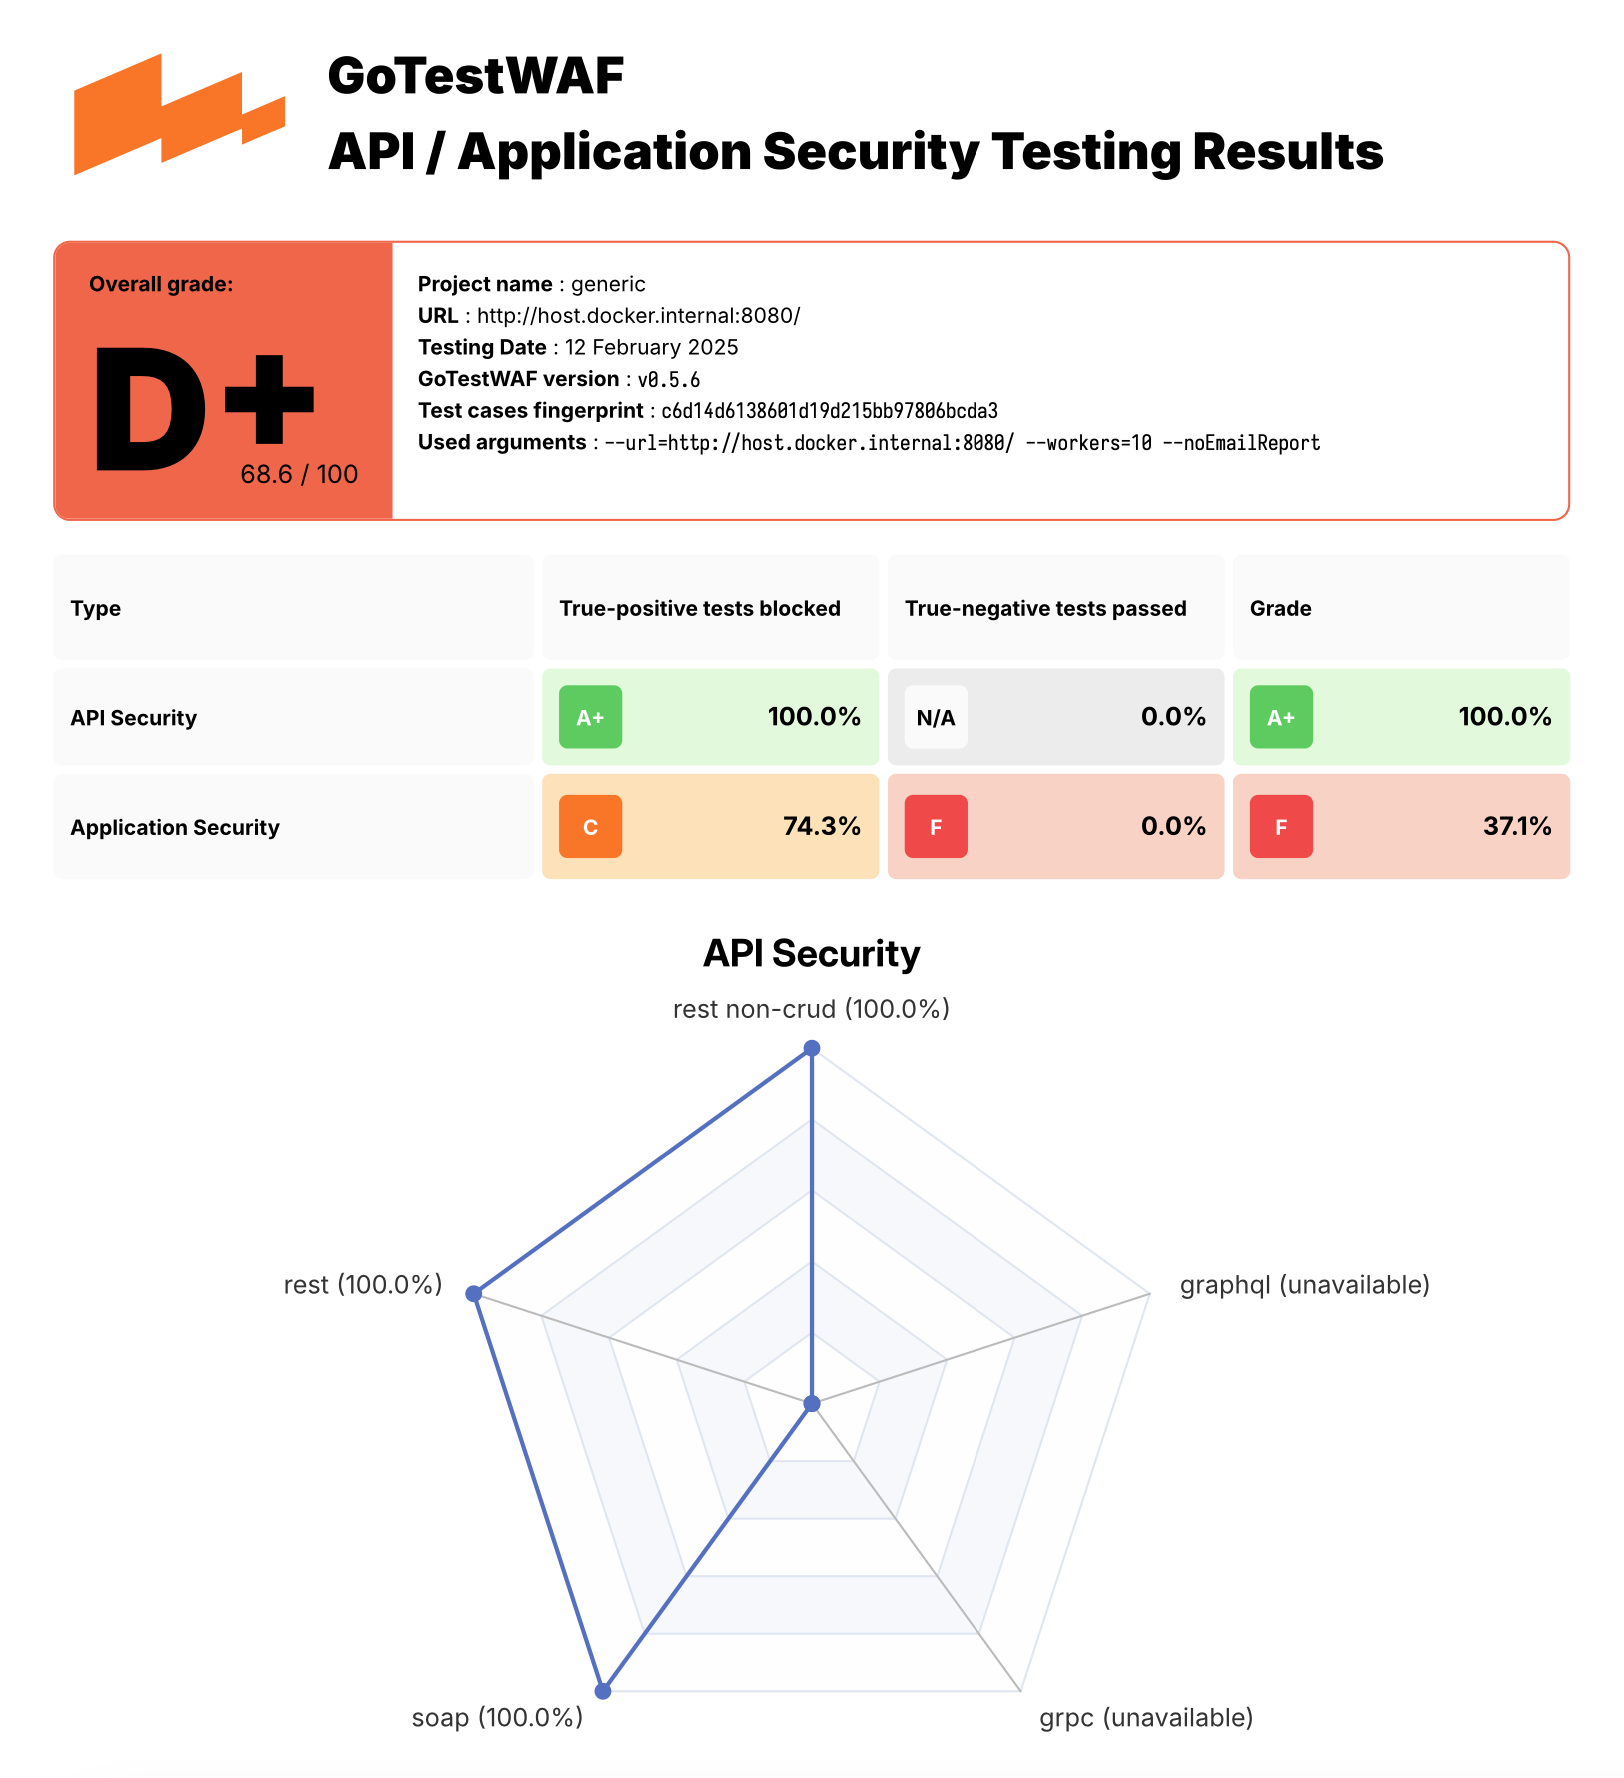
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses

RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…

An strace-like program for the Windows 'native' API

An API hooking framework for intercepting and monitoring Windows applications

A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.

Http request smuggling vulnerability scanner

A Burp Extension designed to identify argument injection vulnerabilities.

MAPS cloud scanner and response parser for Microsoft Defender research.

Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…

CyberArk Security Audit