

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
44.7k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
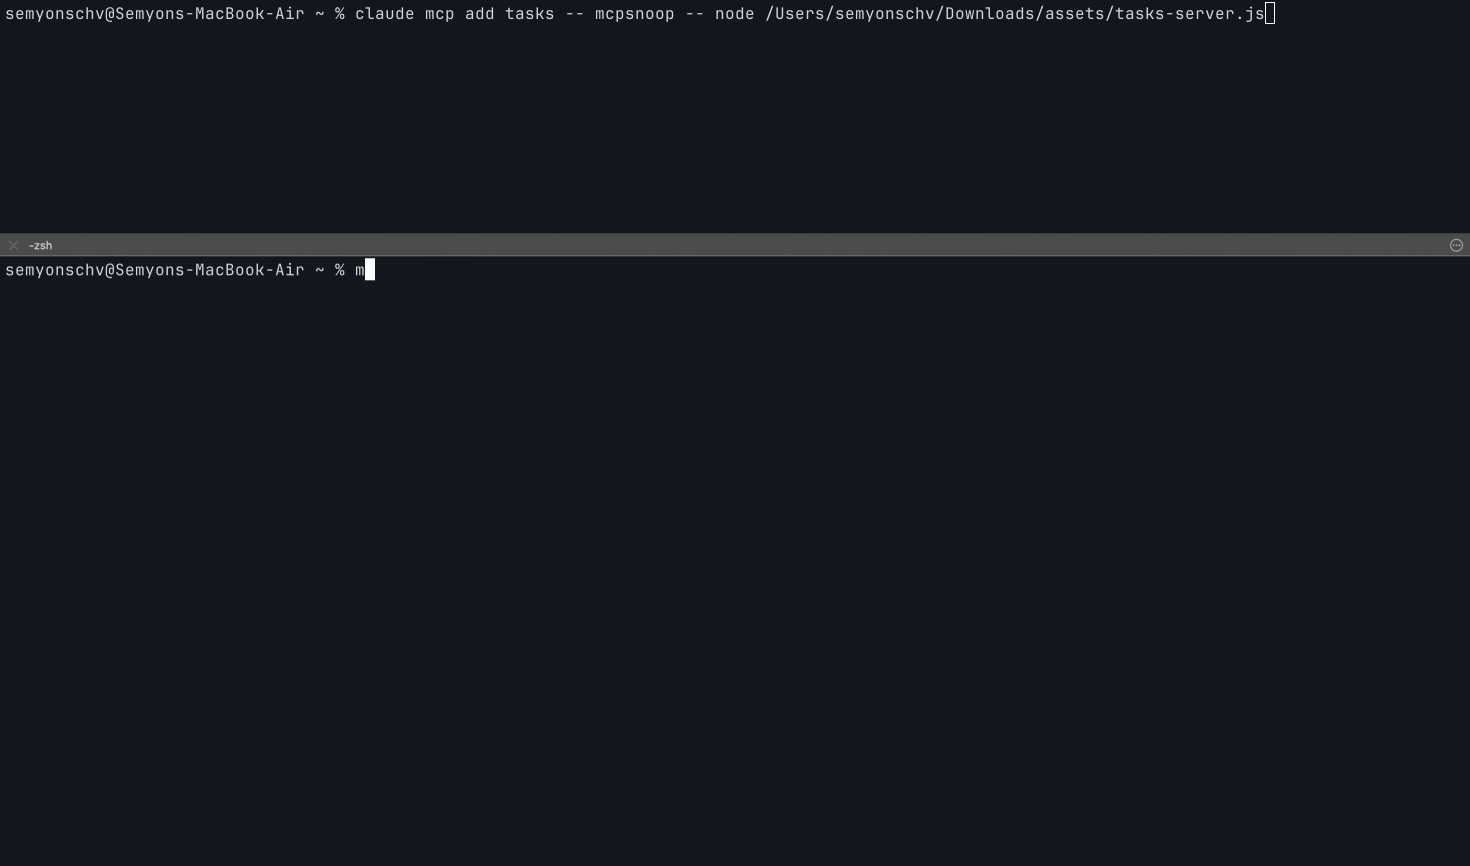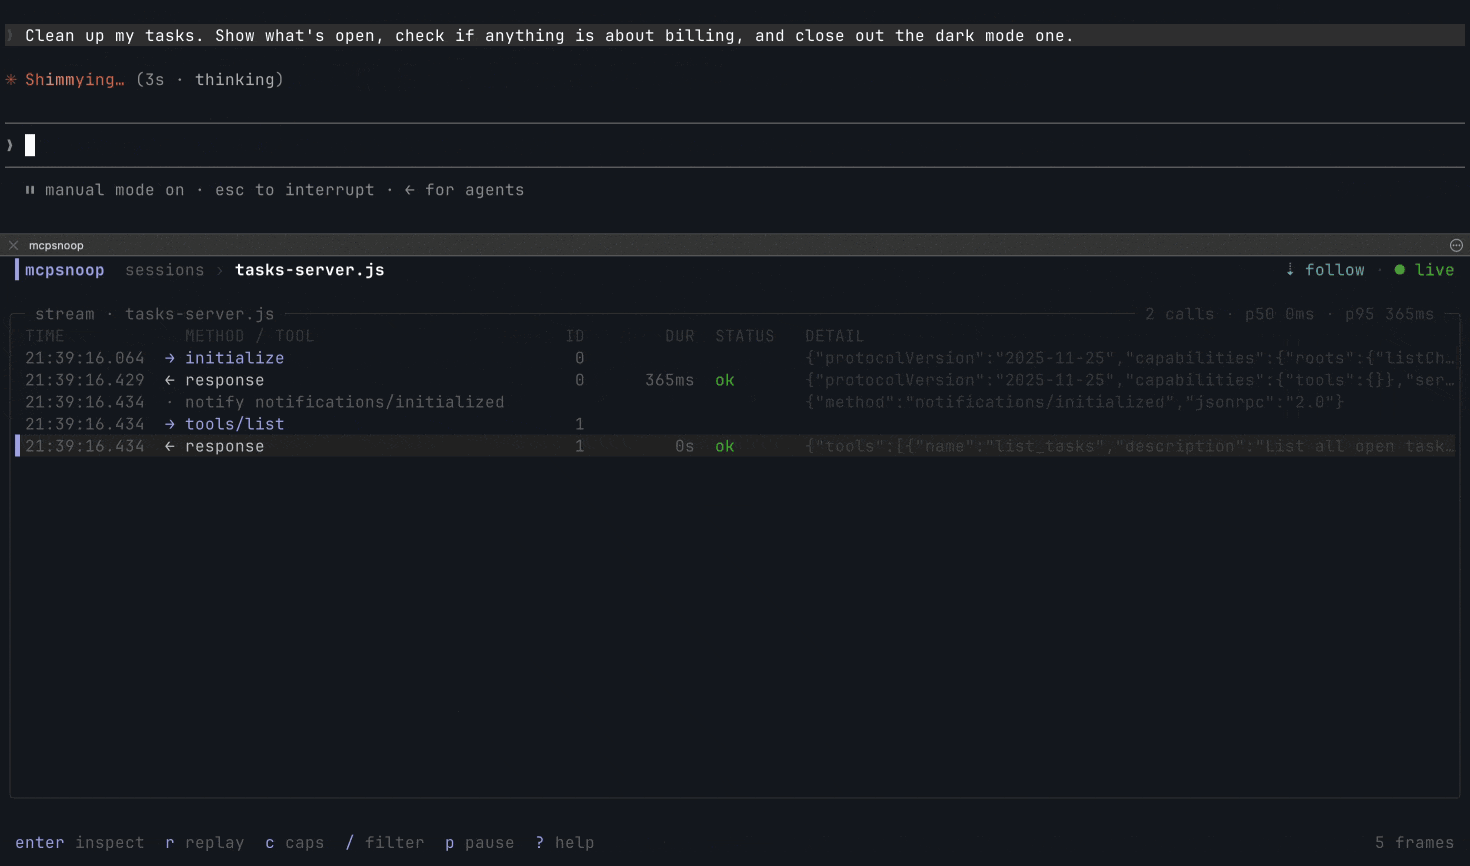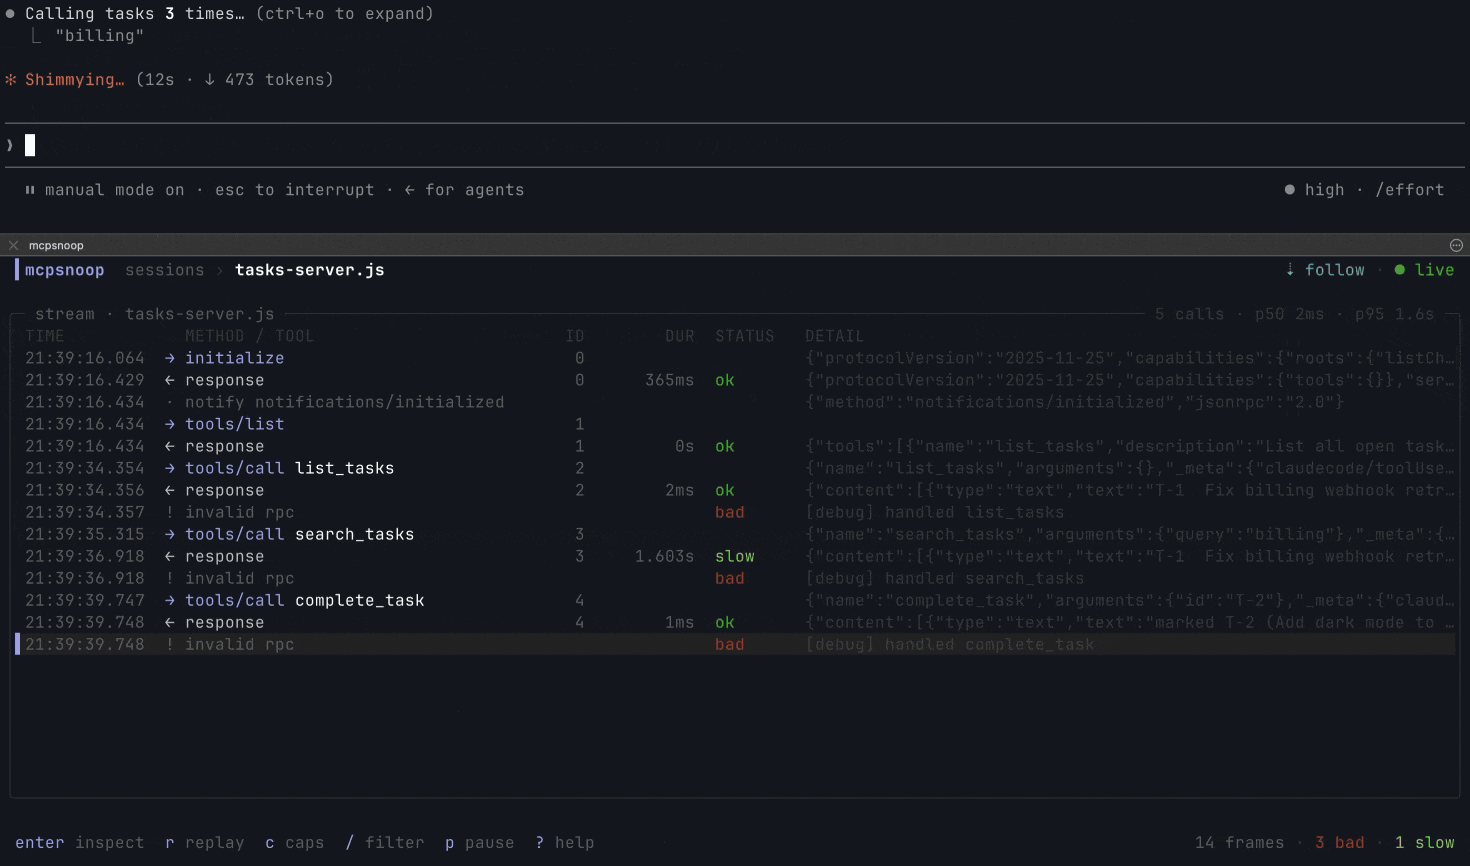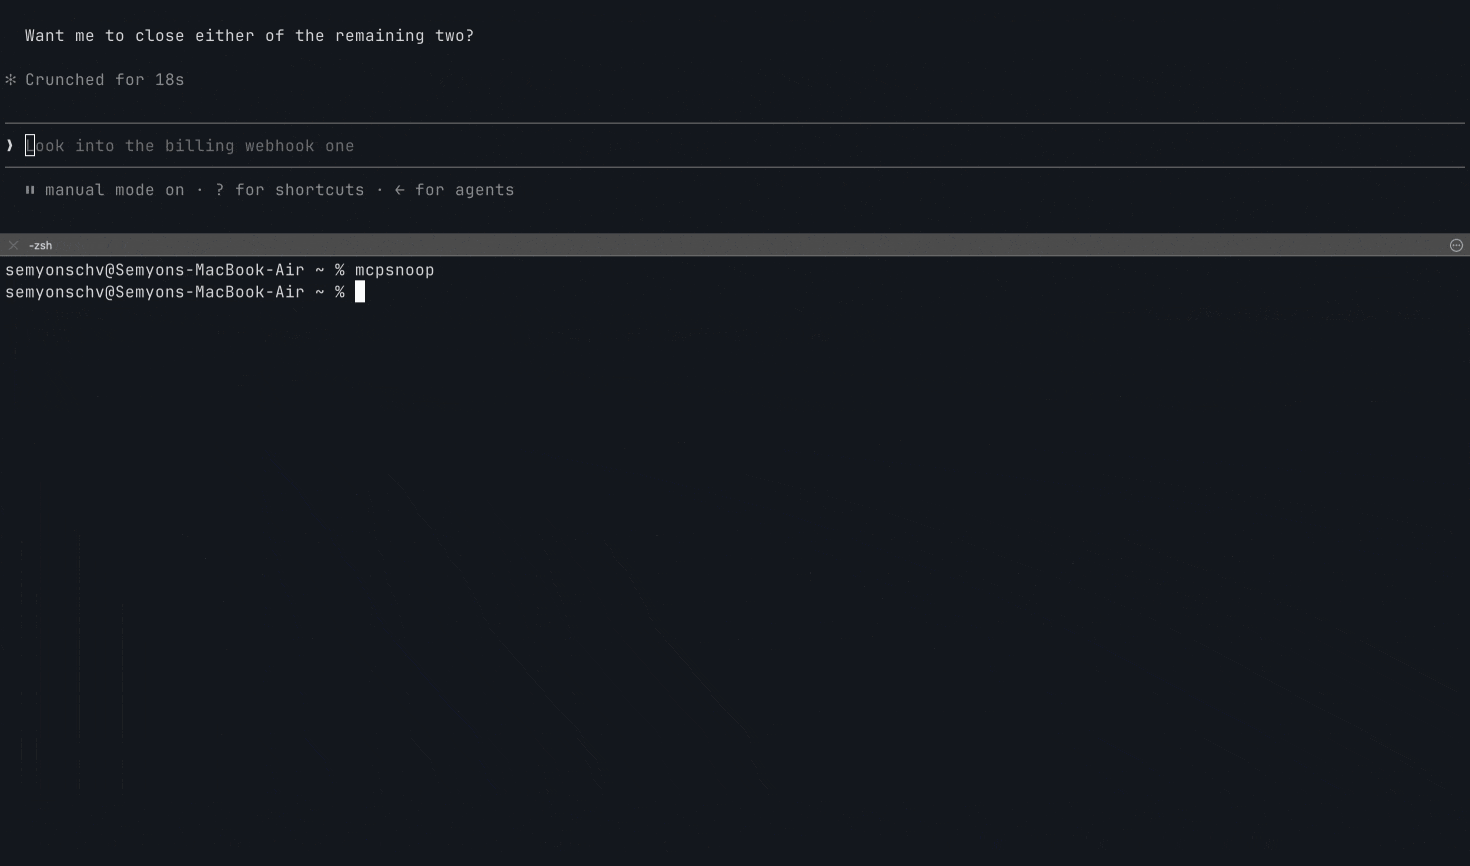 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 ebryx/aes-killer
Burp Plugin to decrypt AES encrypted traffic on the fly
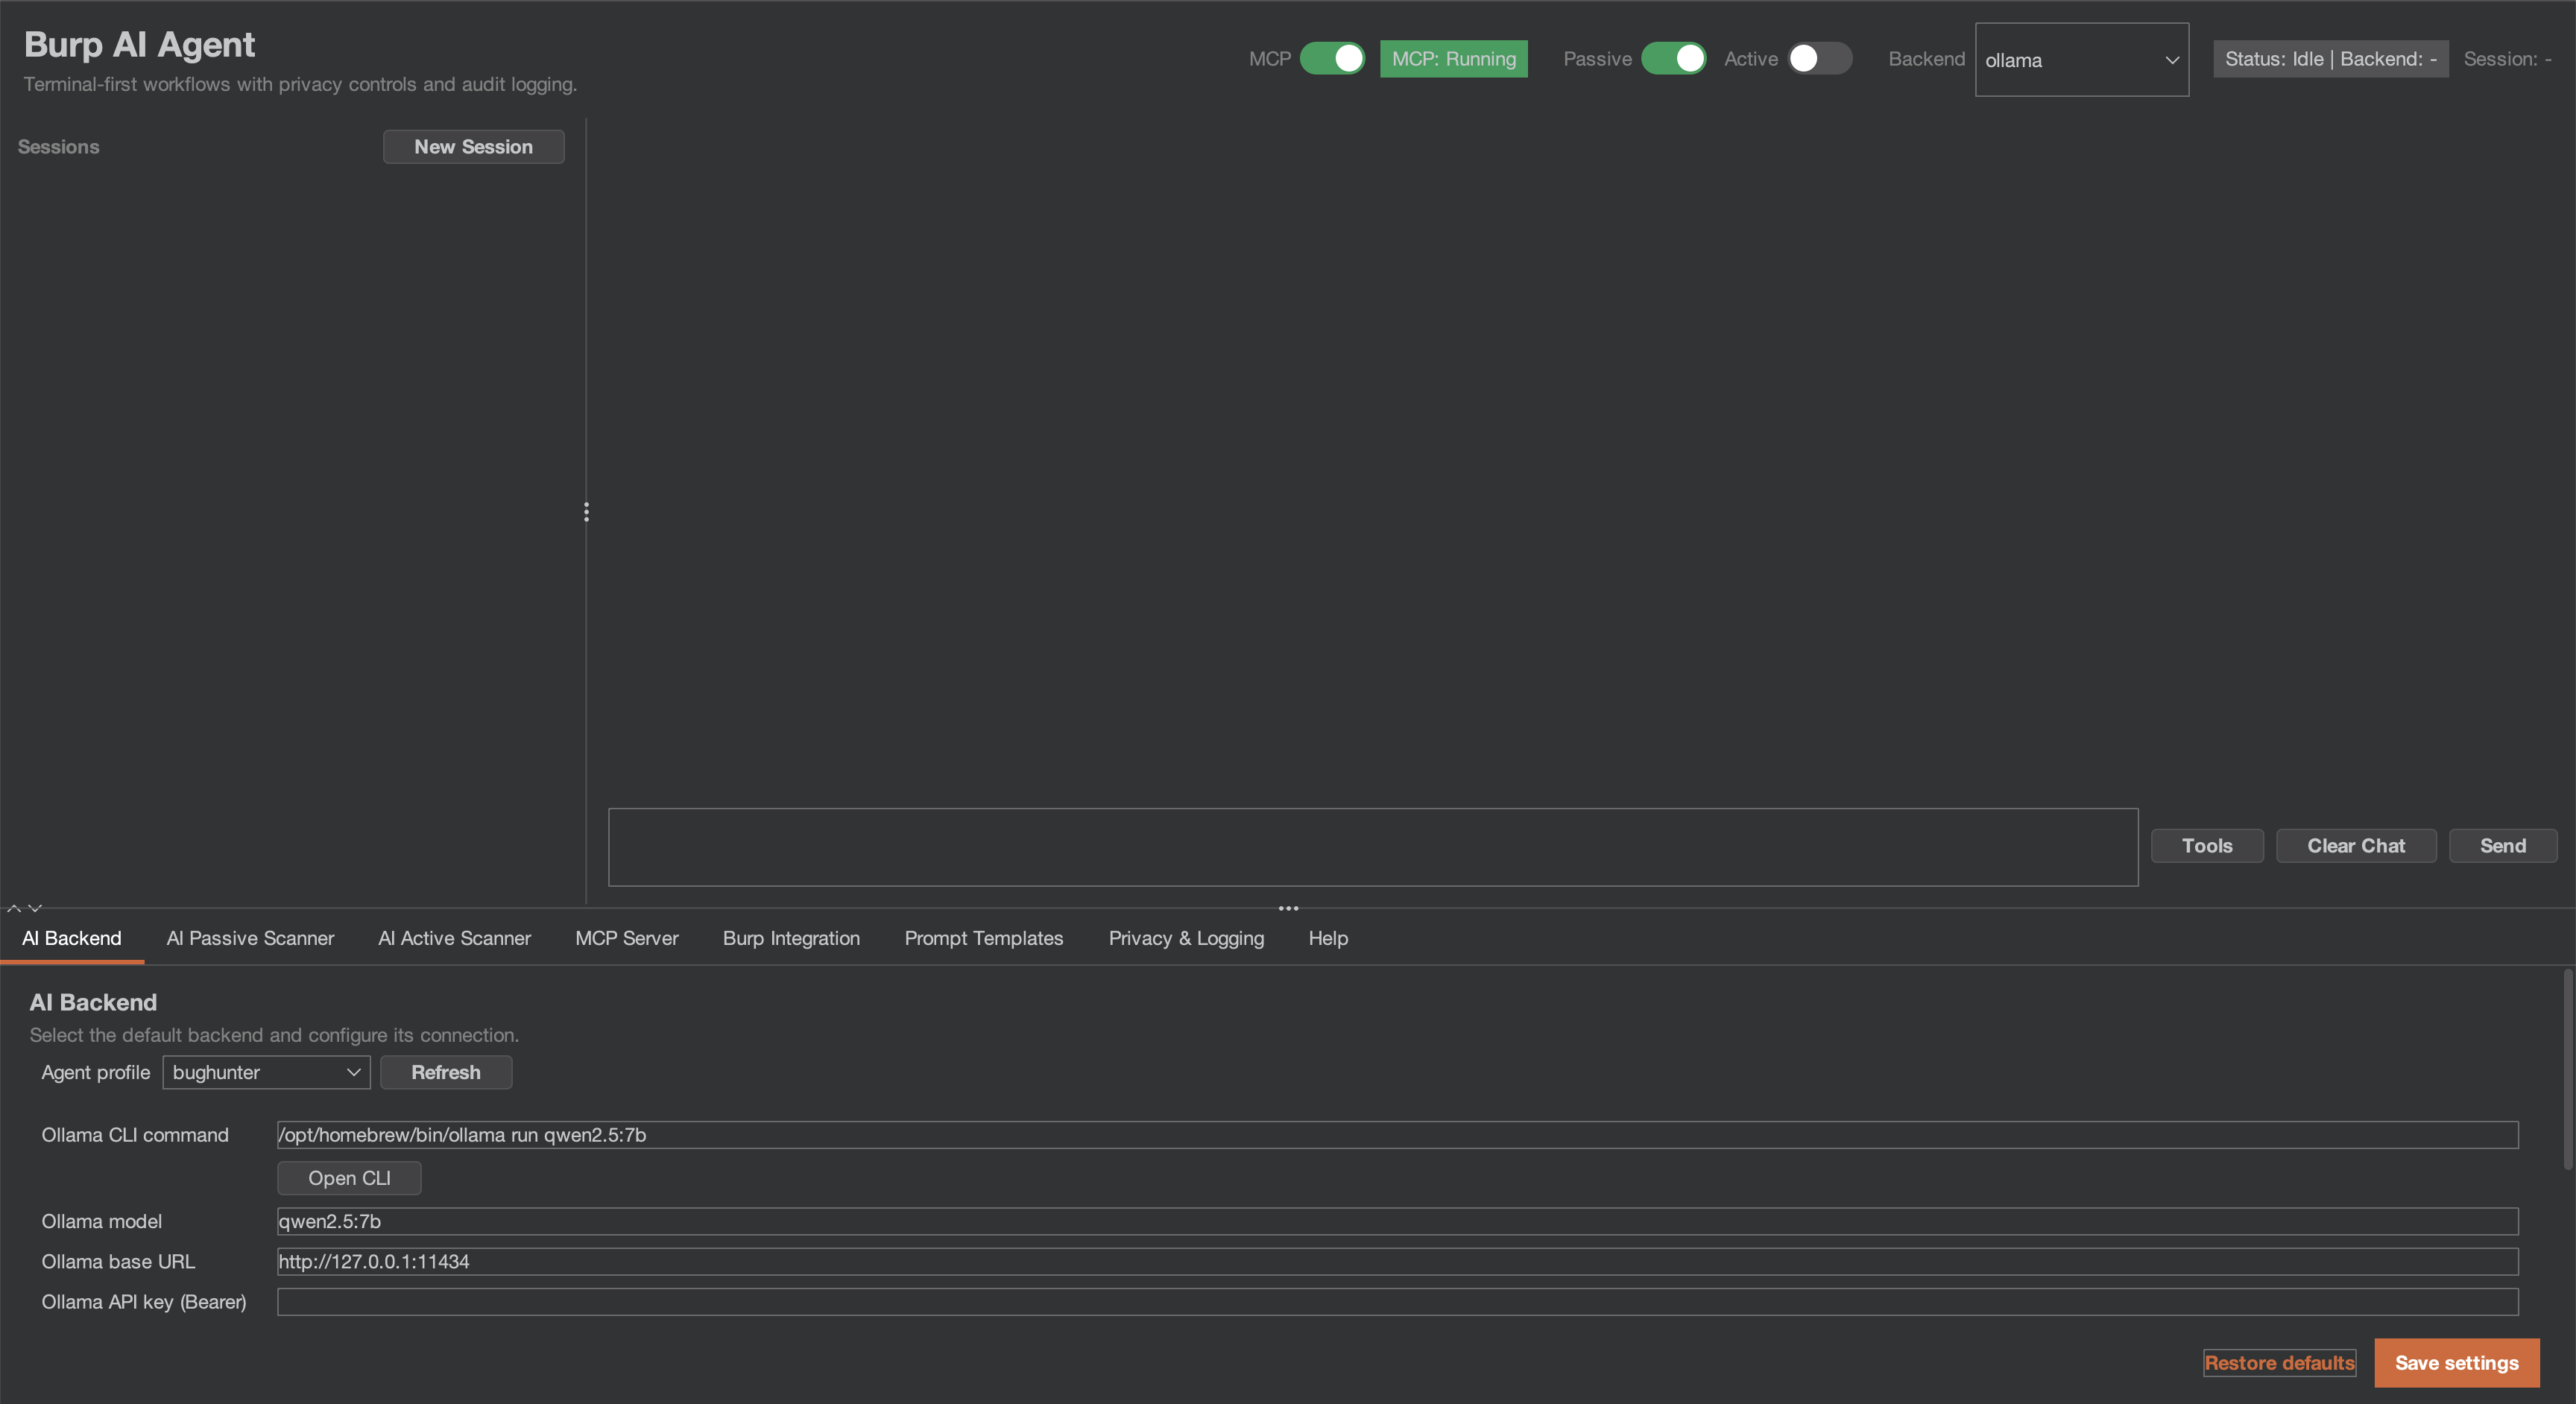 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
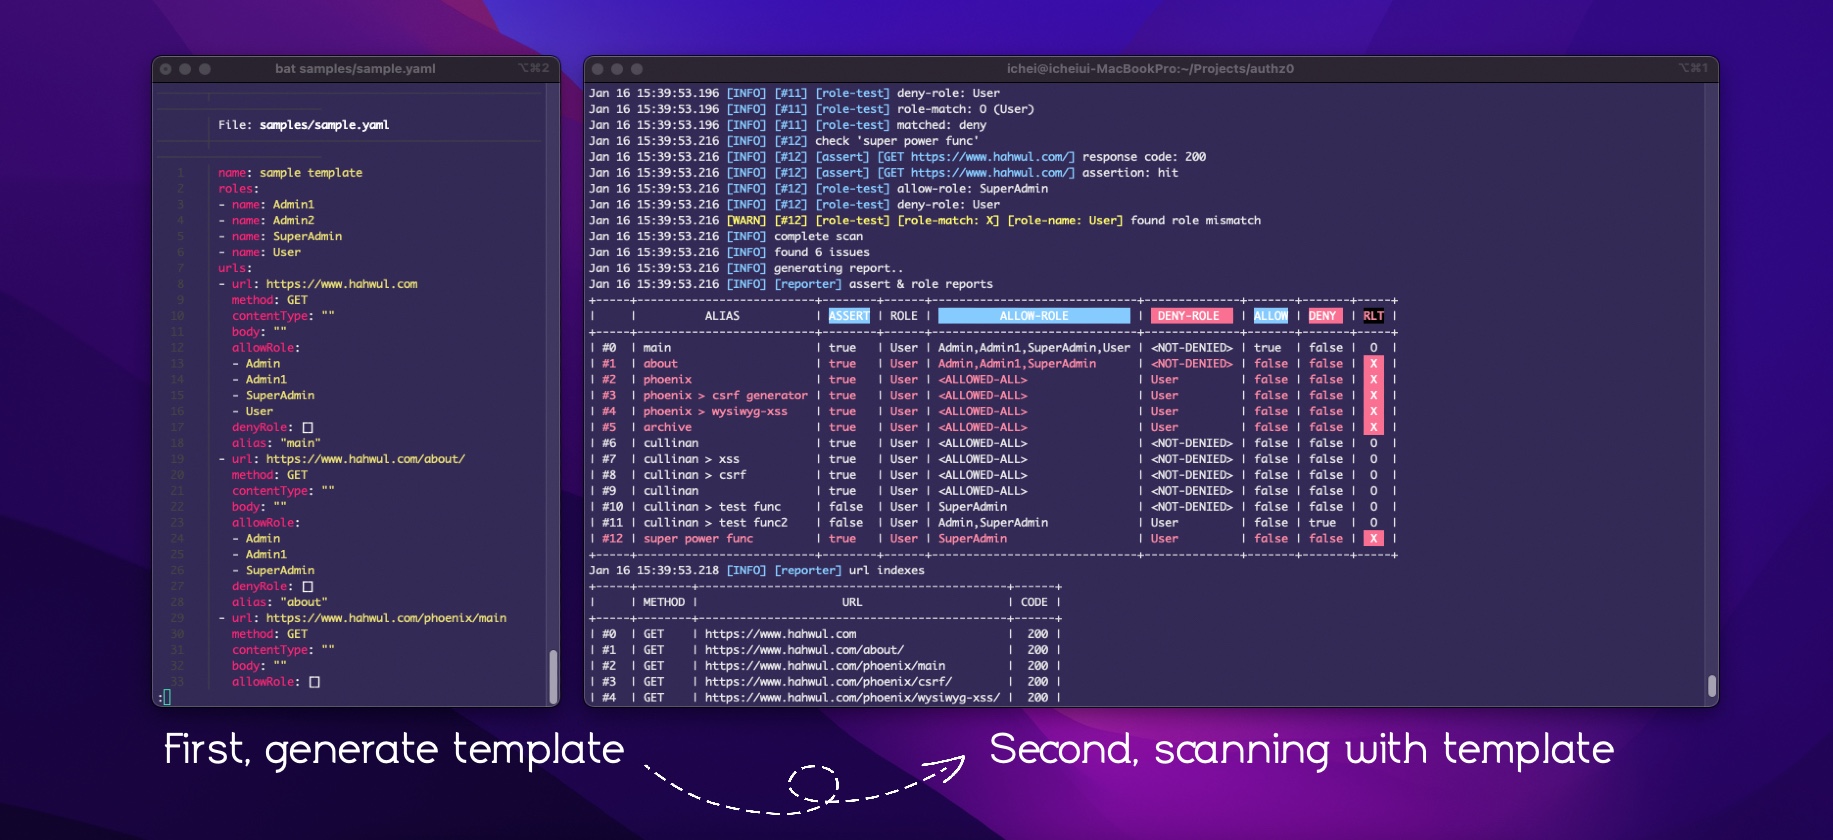 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 assetnote/batchql
GraphQL security auditing script with a focus on performing batch GraphQL queries and mutations
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 george0papasotiriou/cve-2026-11103-graphql-batching-alias-rate-limit-bypass
Proof-of-concept exploit for CVE-2026-11103 demonstrating GraphQL rate-limit bypass through batching and field aliases; includes vulnerable Node.js…