
CVE-2026-35616
 wa6n3r/cve-2026-35616
Exploit script for CVE-2026-35616 that bypasses certificate chain verification in Fortinet API by discovering valid CNs, generating a forged client…
api-securityexploitationpenetration-testing+2
1
wa6n3r/cve-2026-35616Exploit script for CVE-2026-35616 that bypasses certificate chain verification in Fortinet API by discovering valid CNs, generating a forged client…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
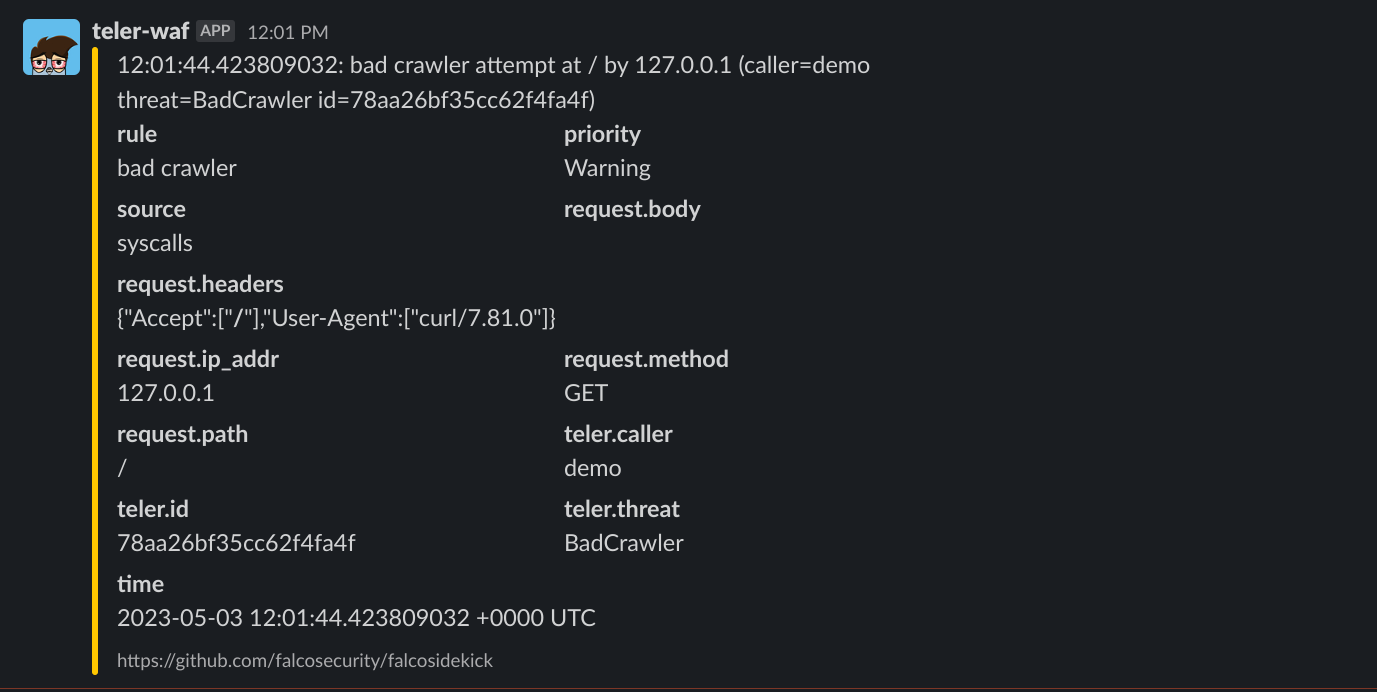 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 symfony/symfony
The Symfony PHP framework
 mbadanoiu/cve-2019-11287
CVE-2019-11287: DoS via Heap Overflow in RabbitMQ Web Management Plugin
 zecure/shadowd
The Shadow Daemon web application firewall server
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 vagnerd/cve-2023-27587-poc
The simple PoC of CVE-2023-27587
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 openidentityplatform/openam
Open-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
 rabbitsafe/cve-2021-37580
Proof-of-concept exploit for Apache ShenYu Admin JWT authentication bypass (CVE-2021-37580). Includes a scanning script to detect vulnerable…