

gotestwaf
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
api-securityapi-security-testingpenetration-testing+4
1.8k
wallarm/gotestwafAn open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 opnsense/core
OPNsense GUI, API and systems backend
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
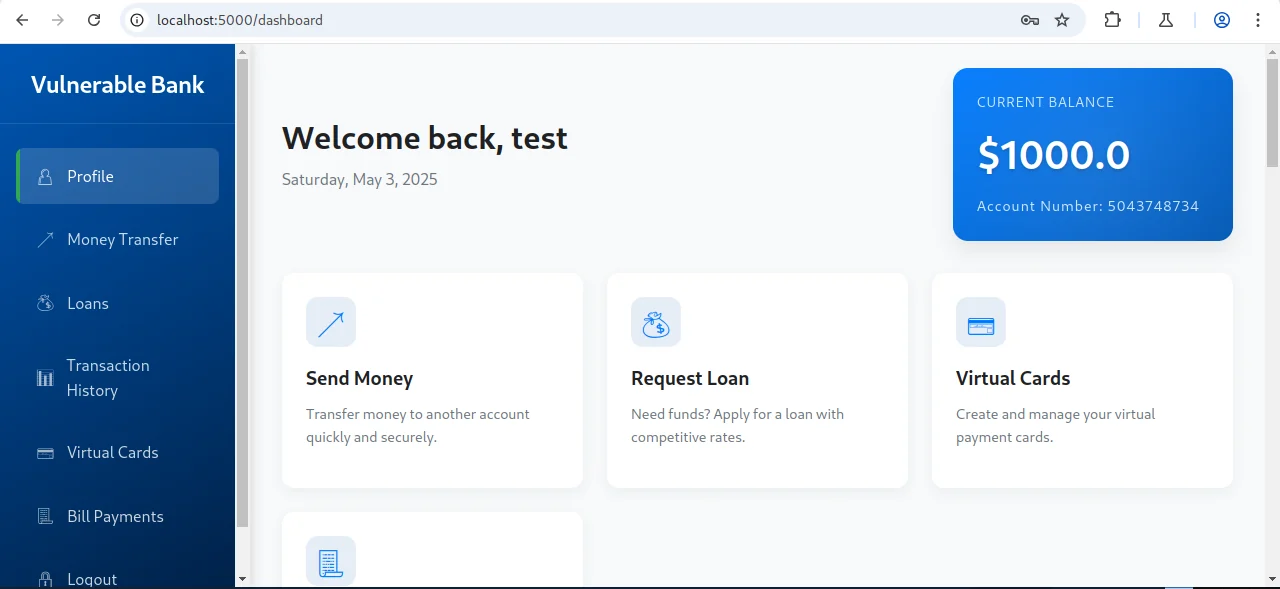 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
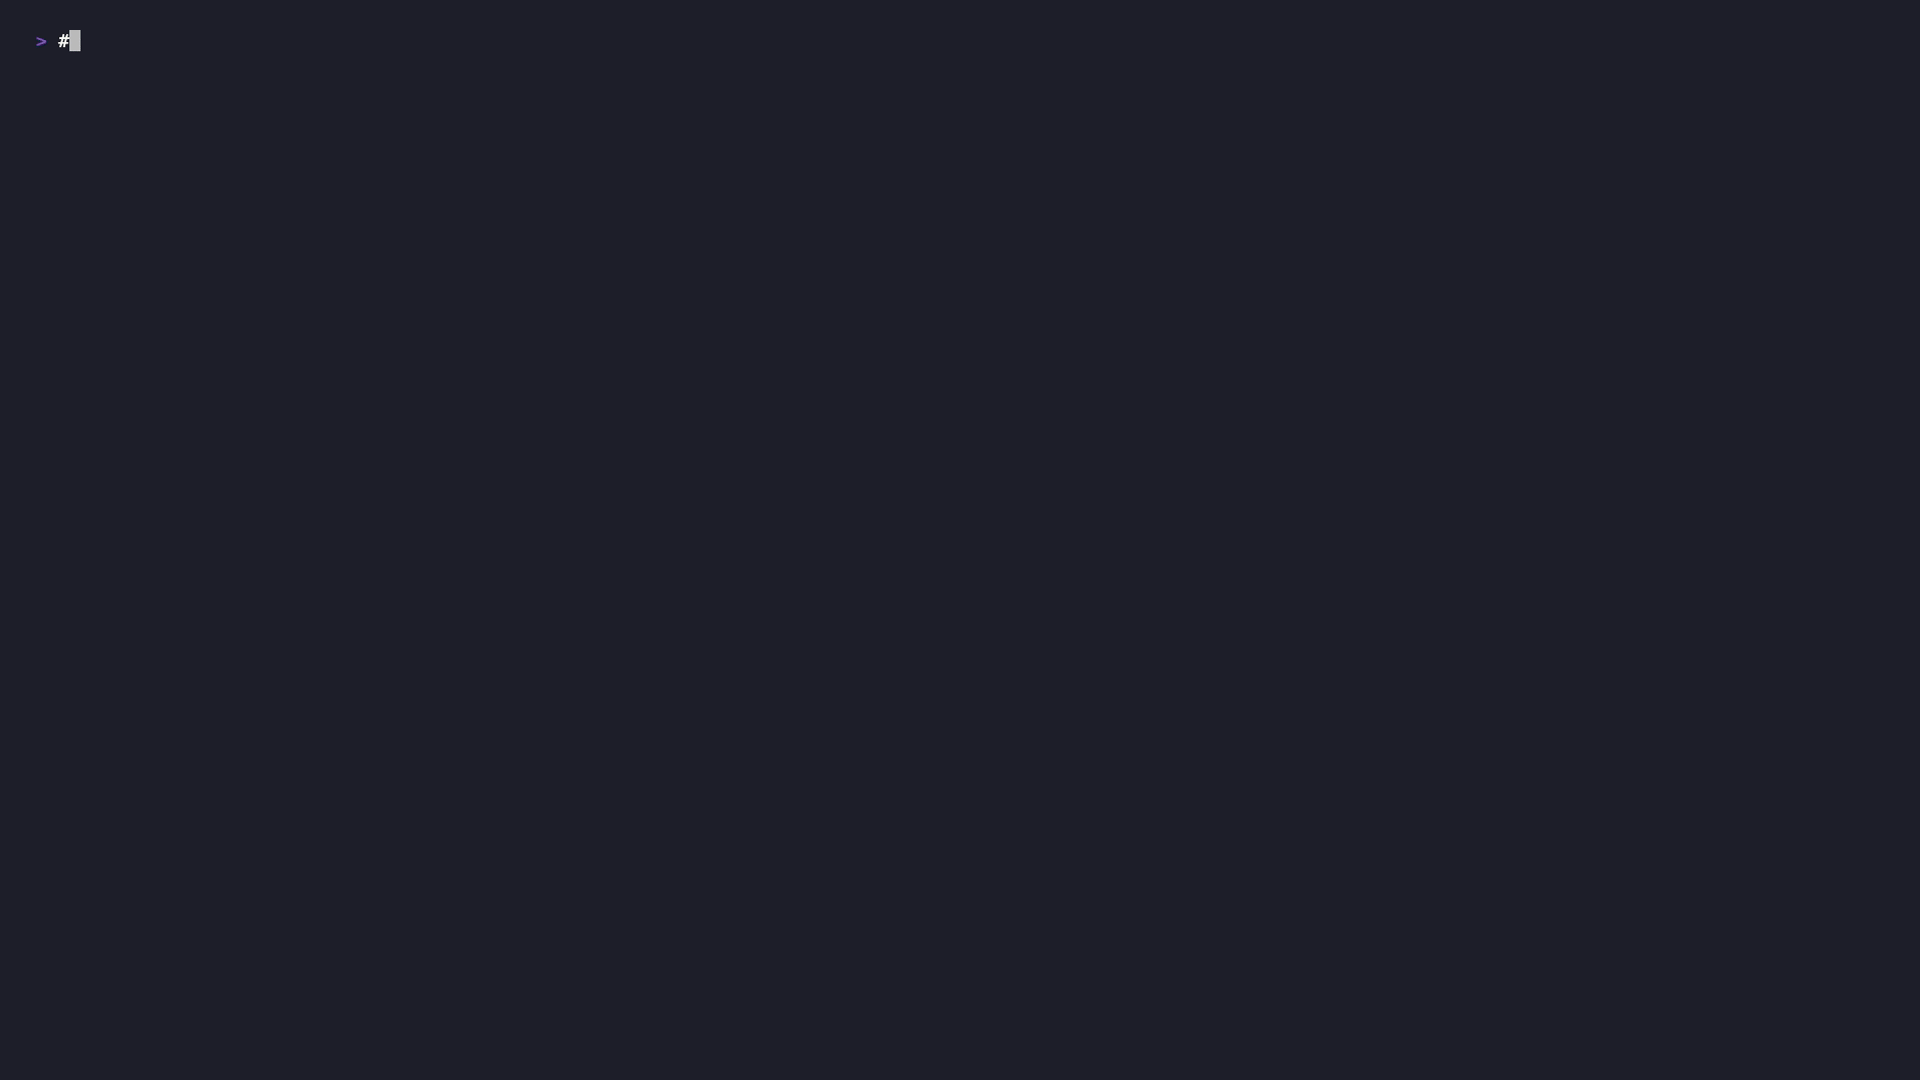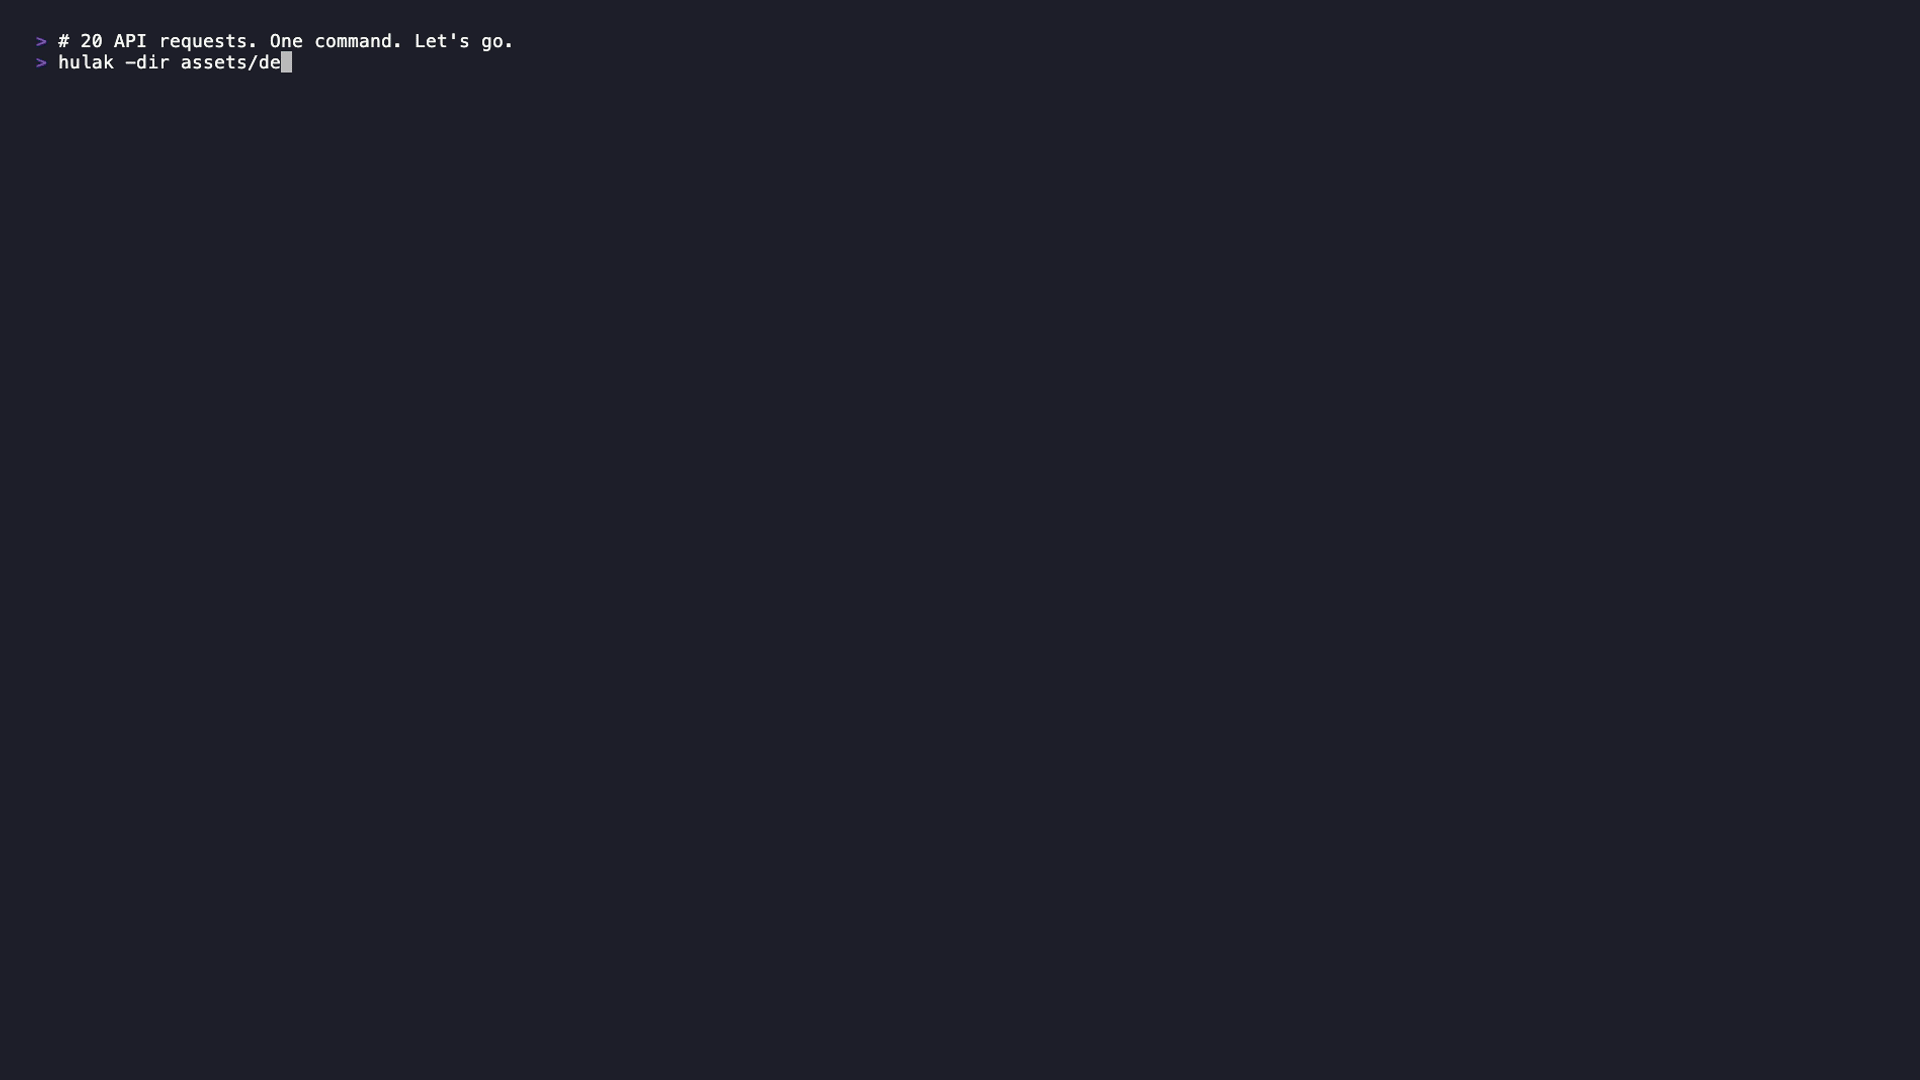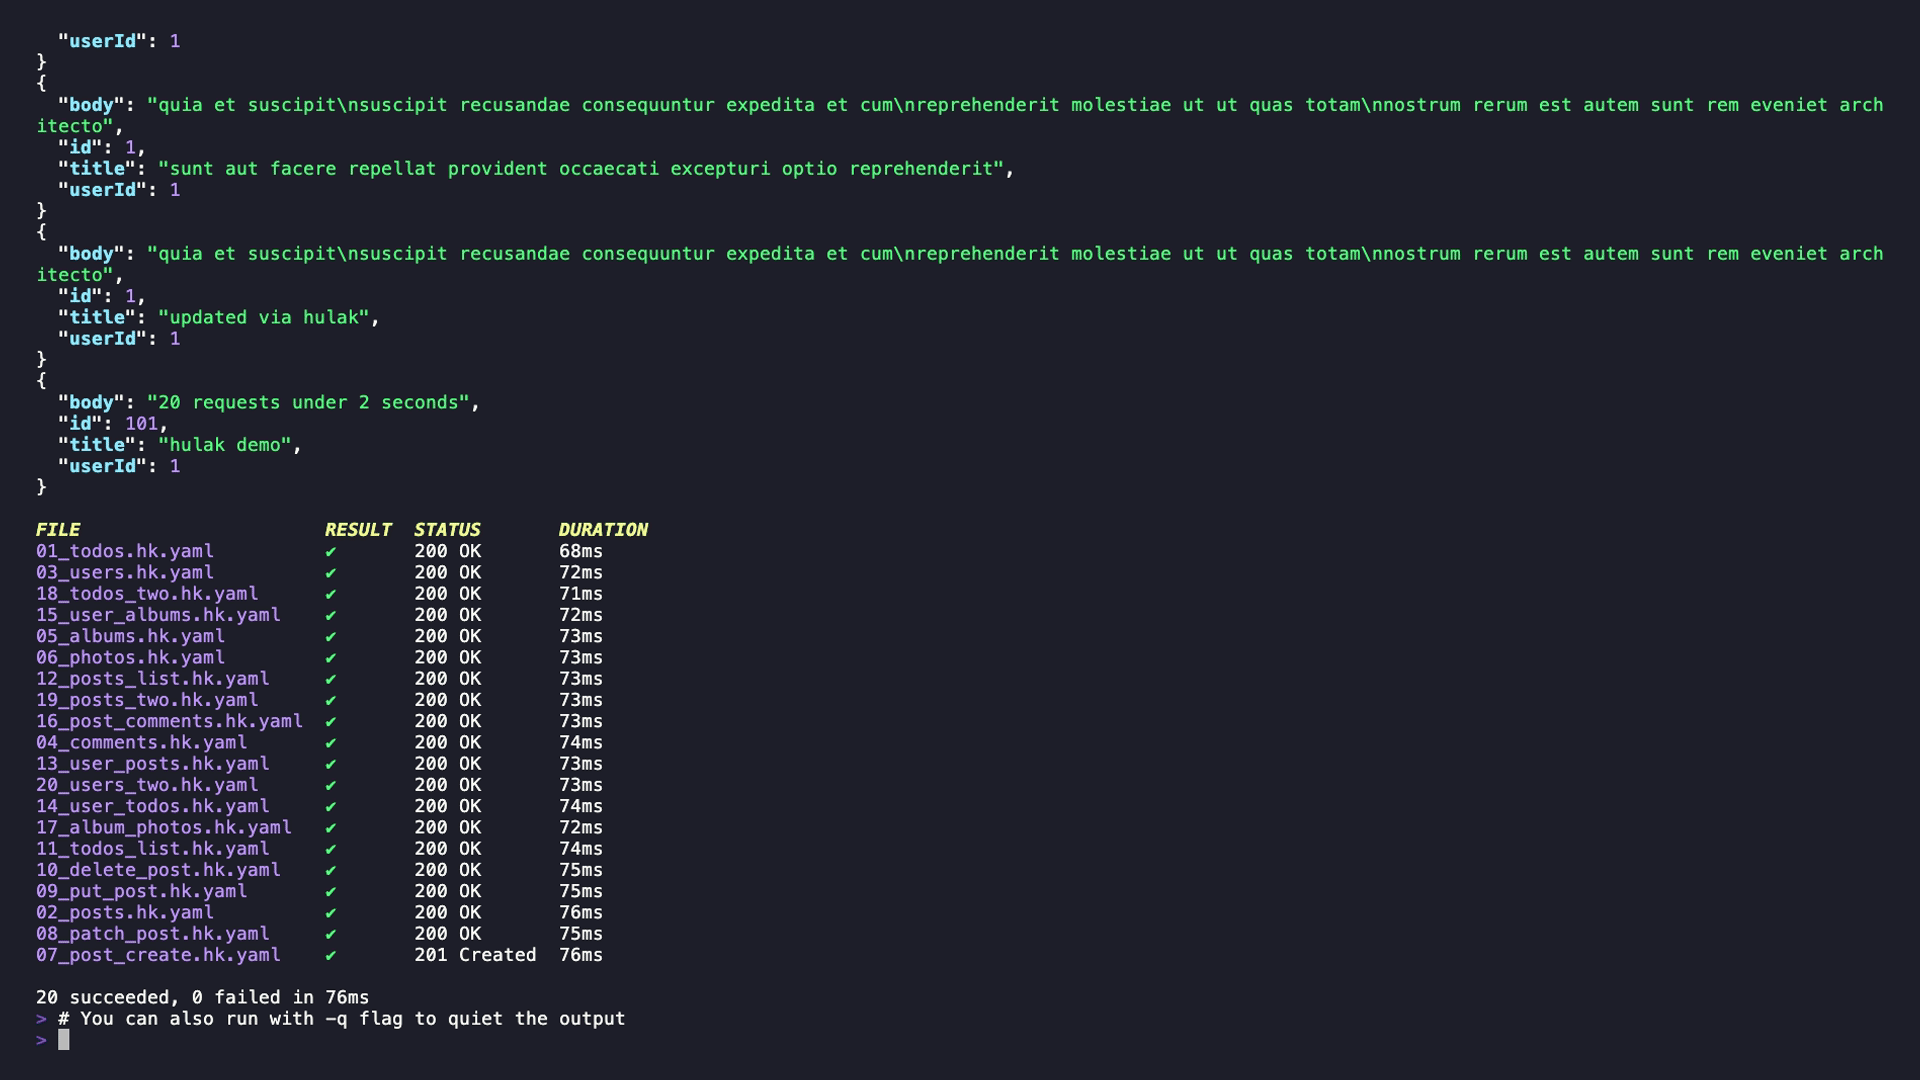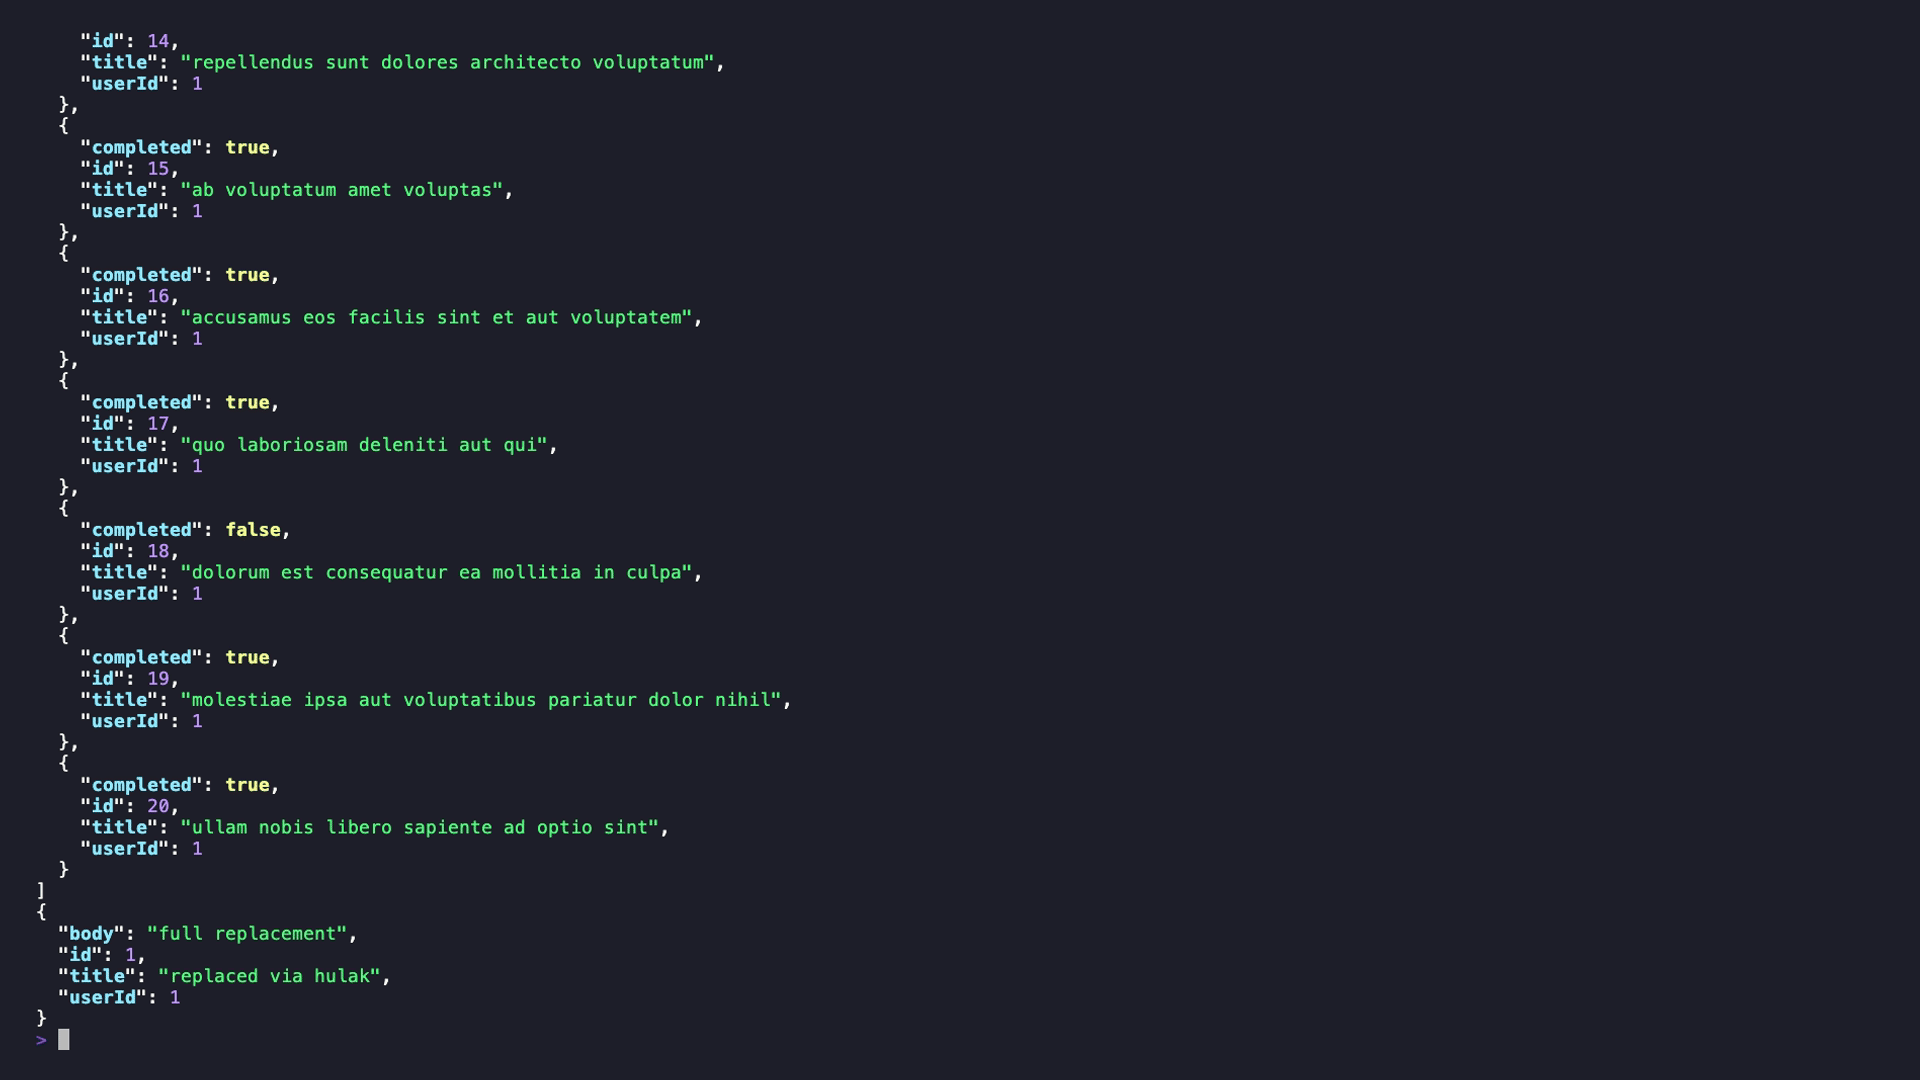 xaaha/hulak
Lightweight file-based CLI API client with age-encrypted secrets, first-class GraphQL support and MCP server for agentic workflow.
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 teycir/apihunter
Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.
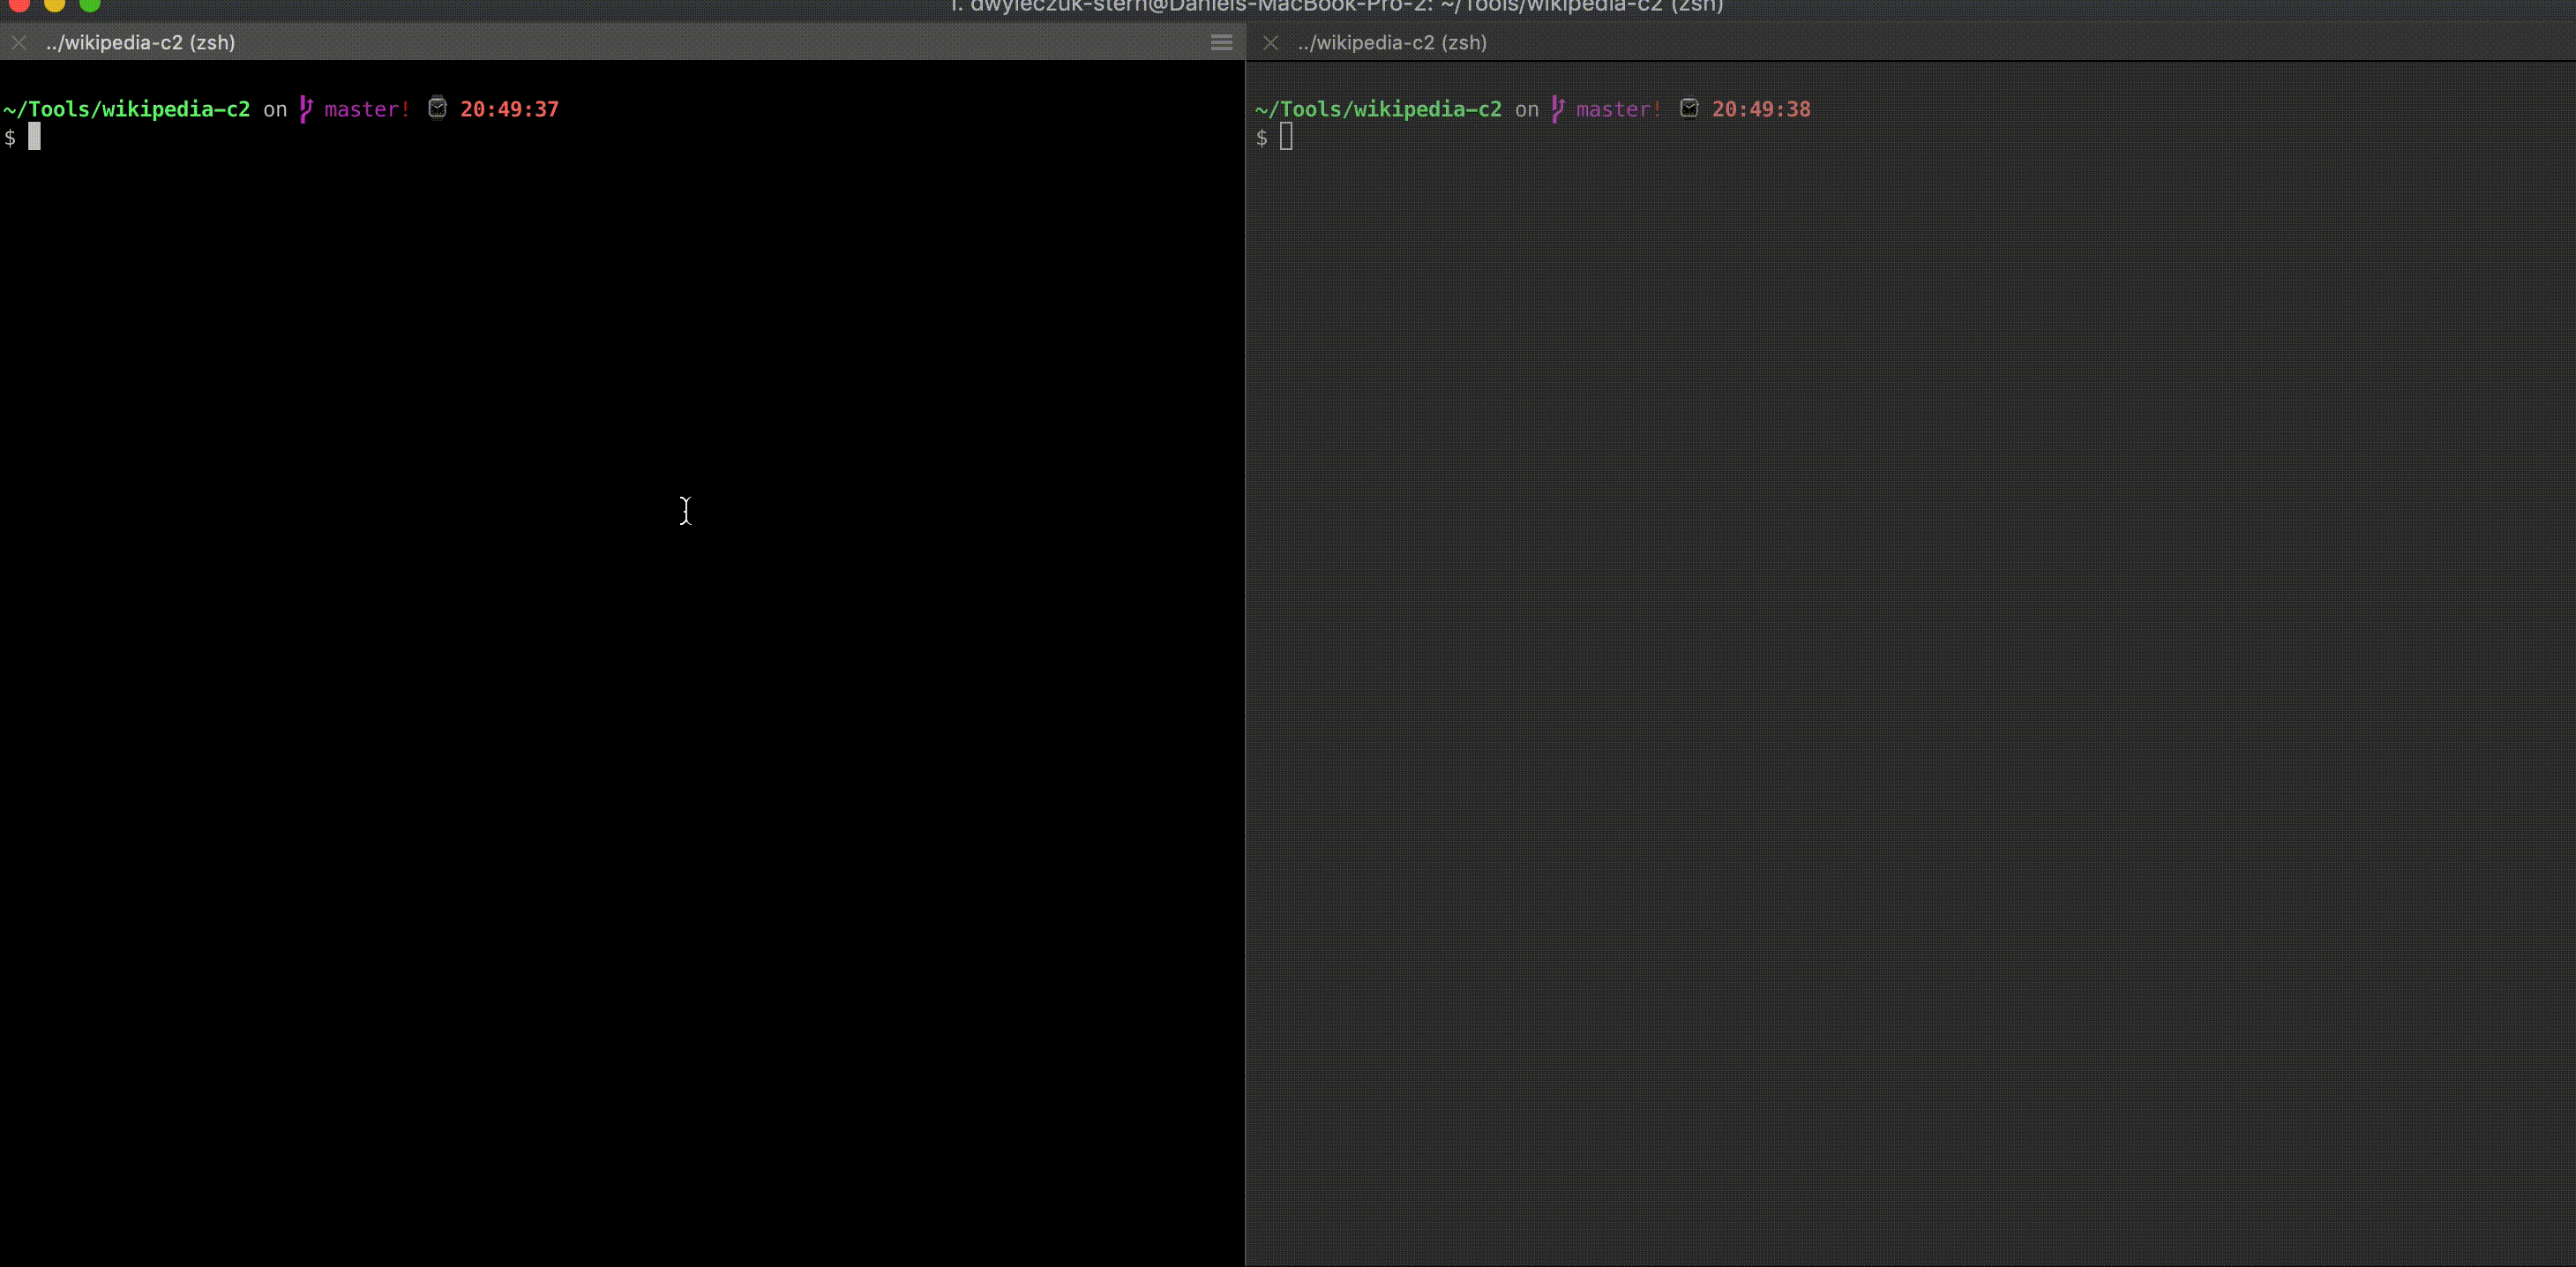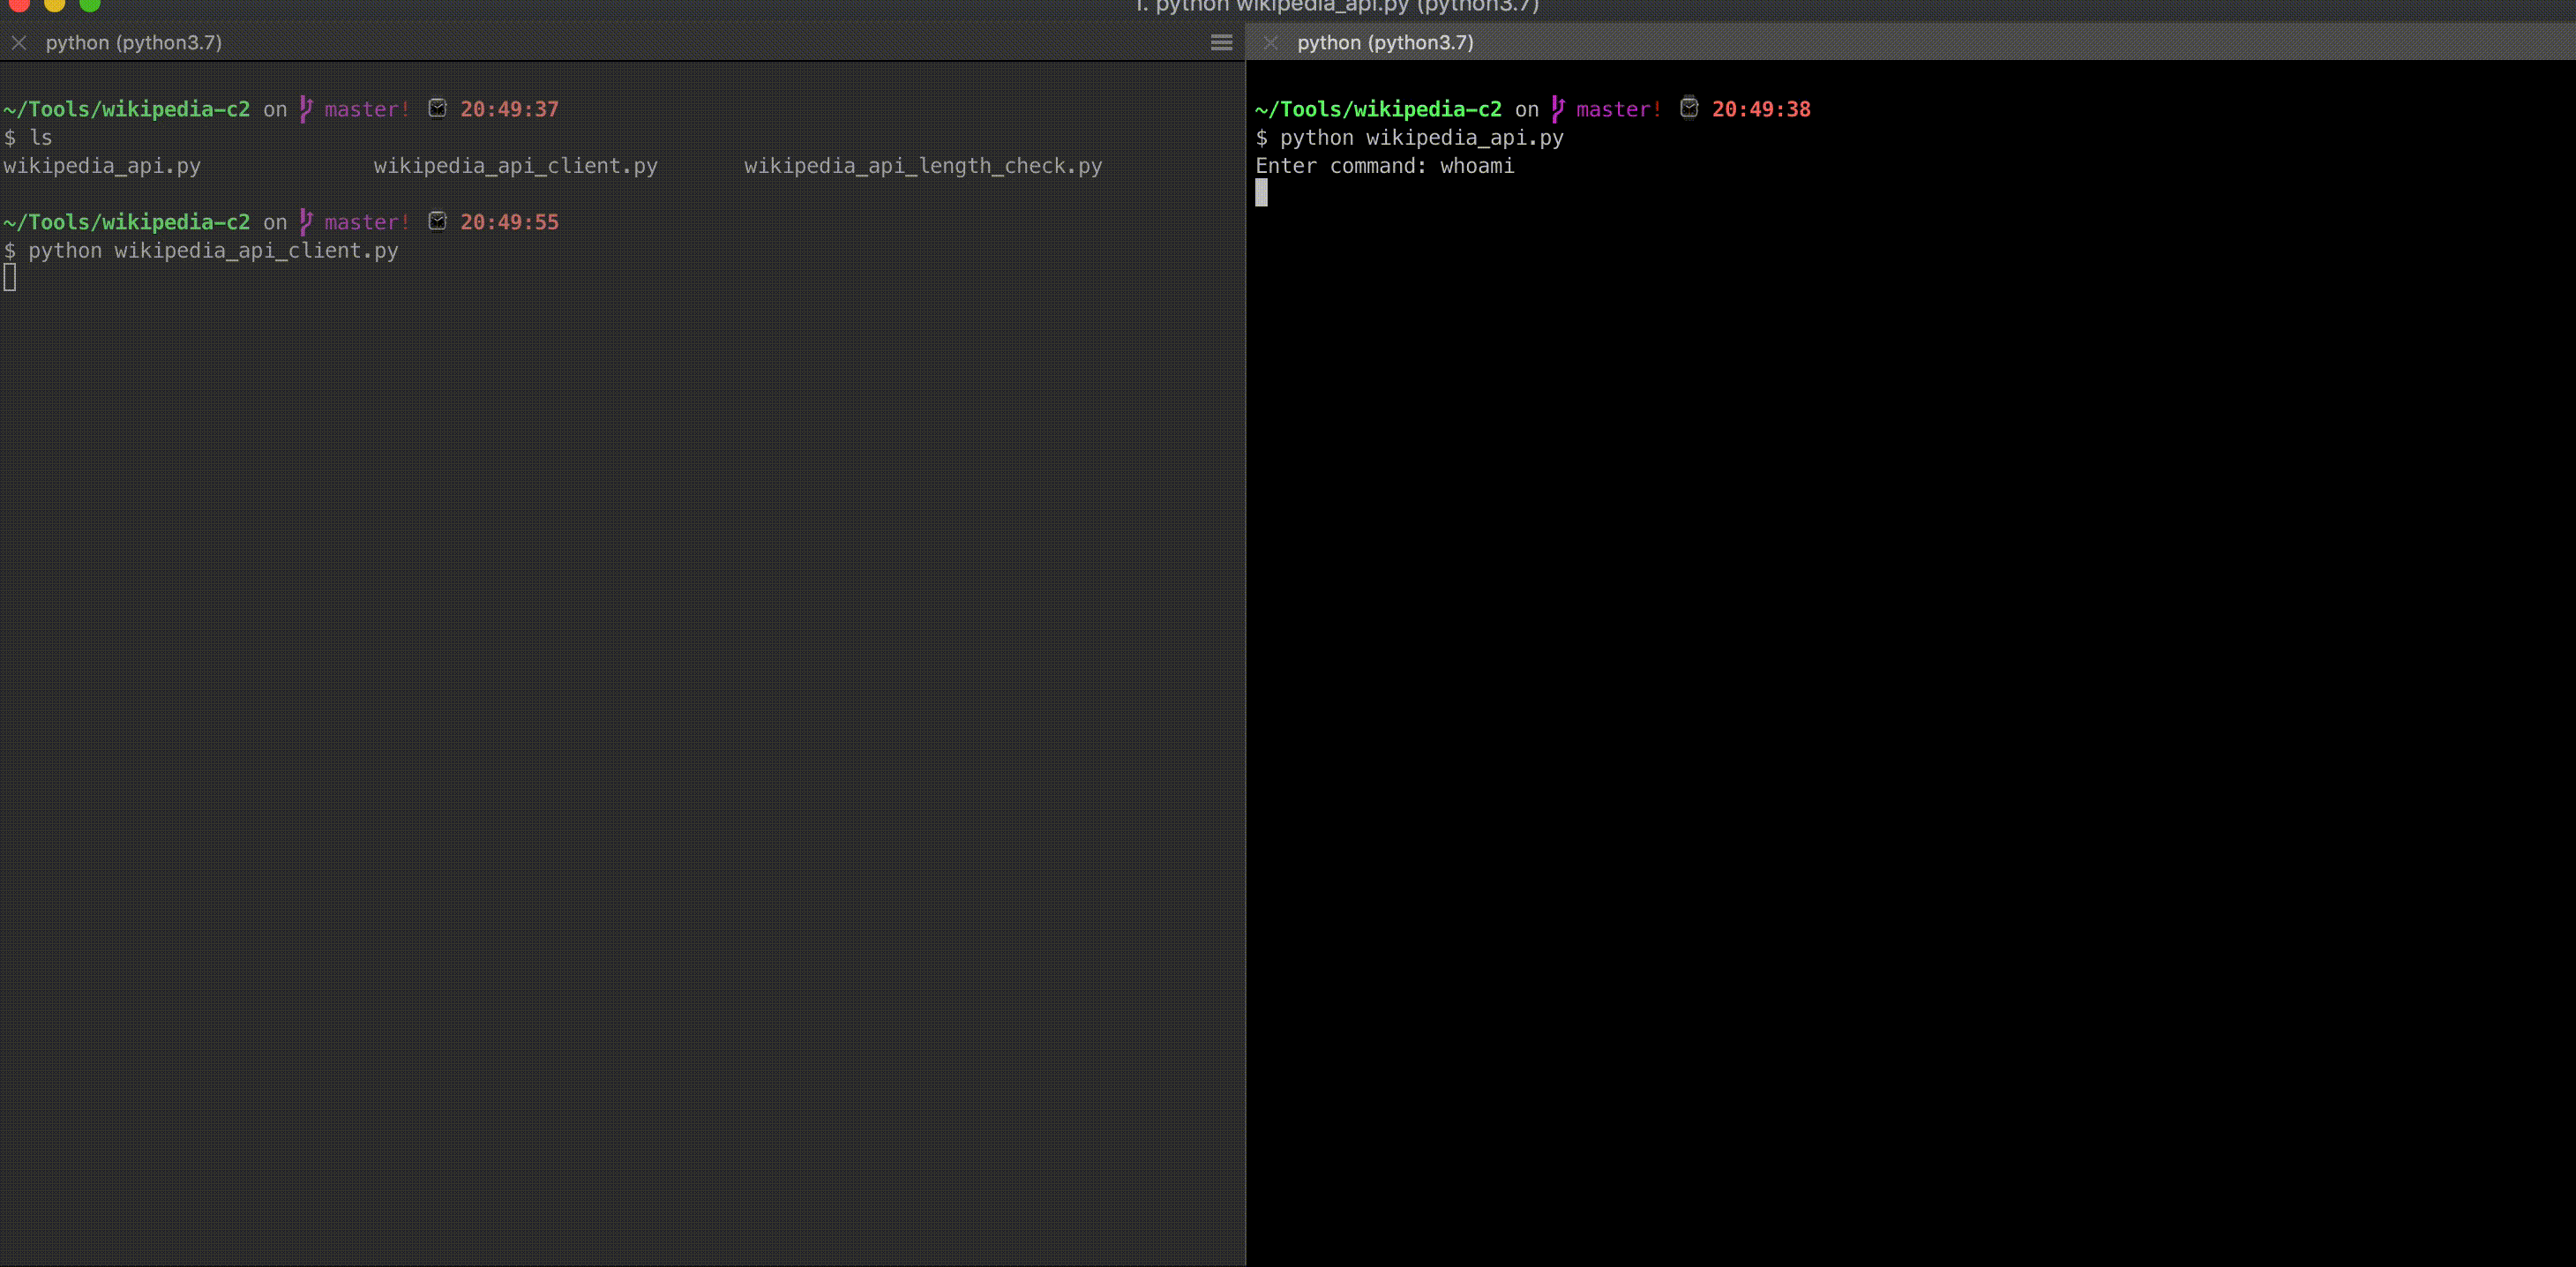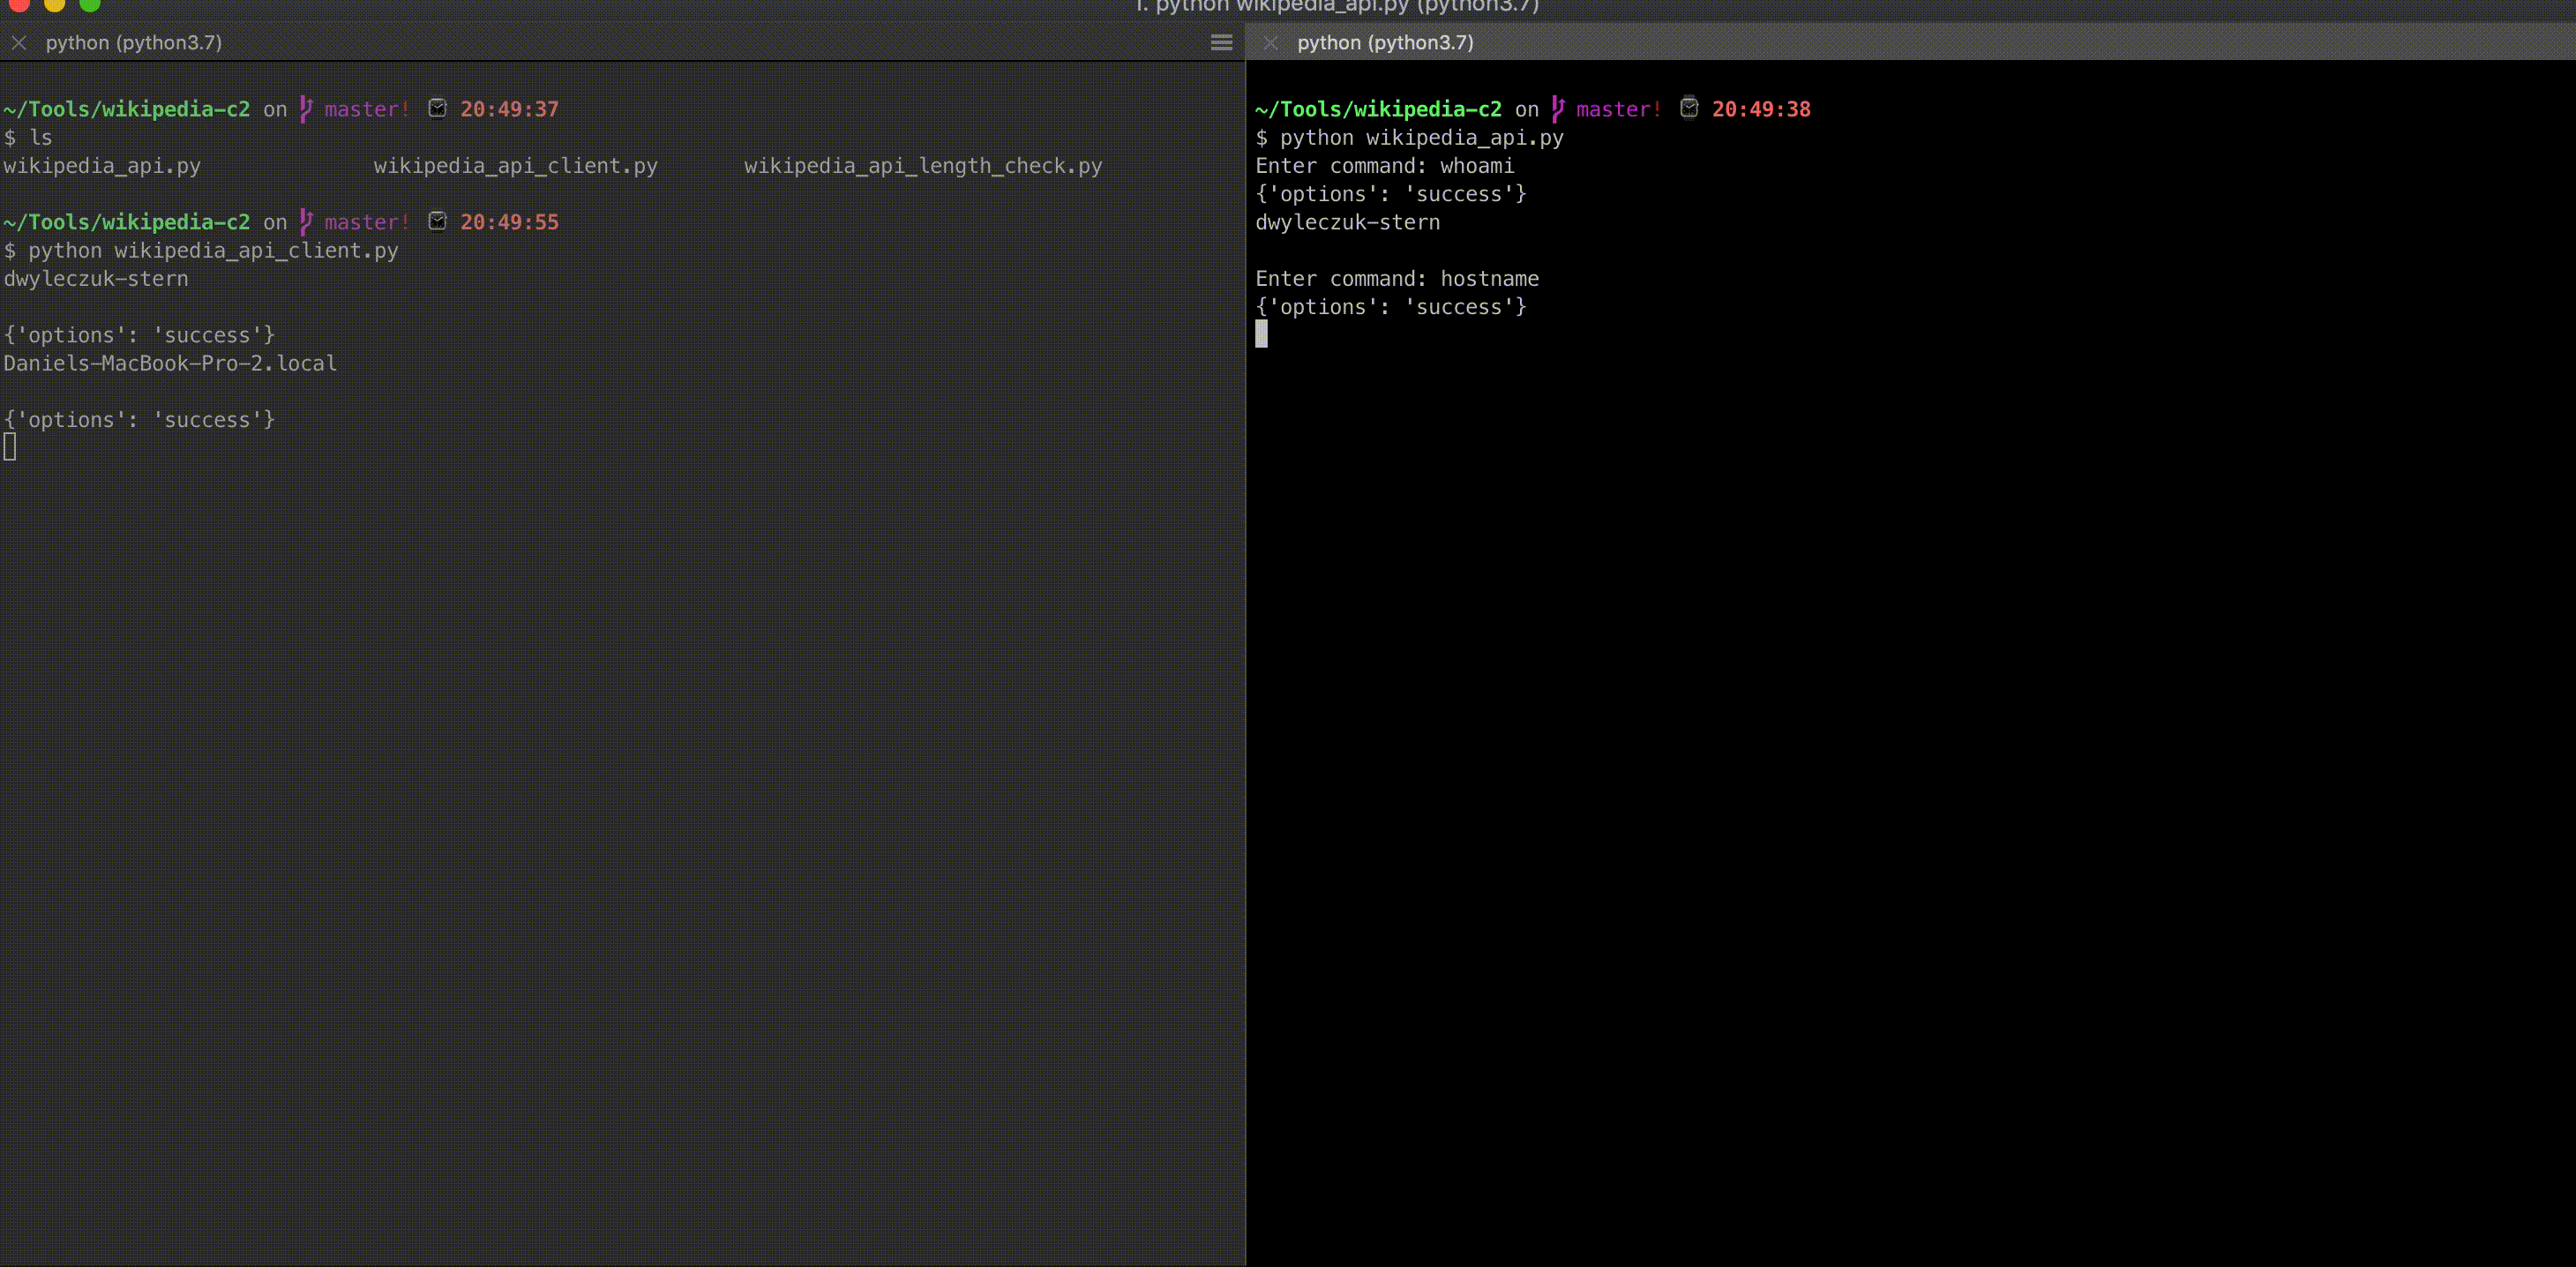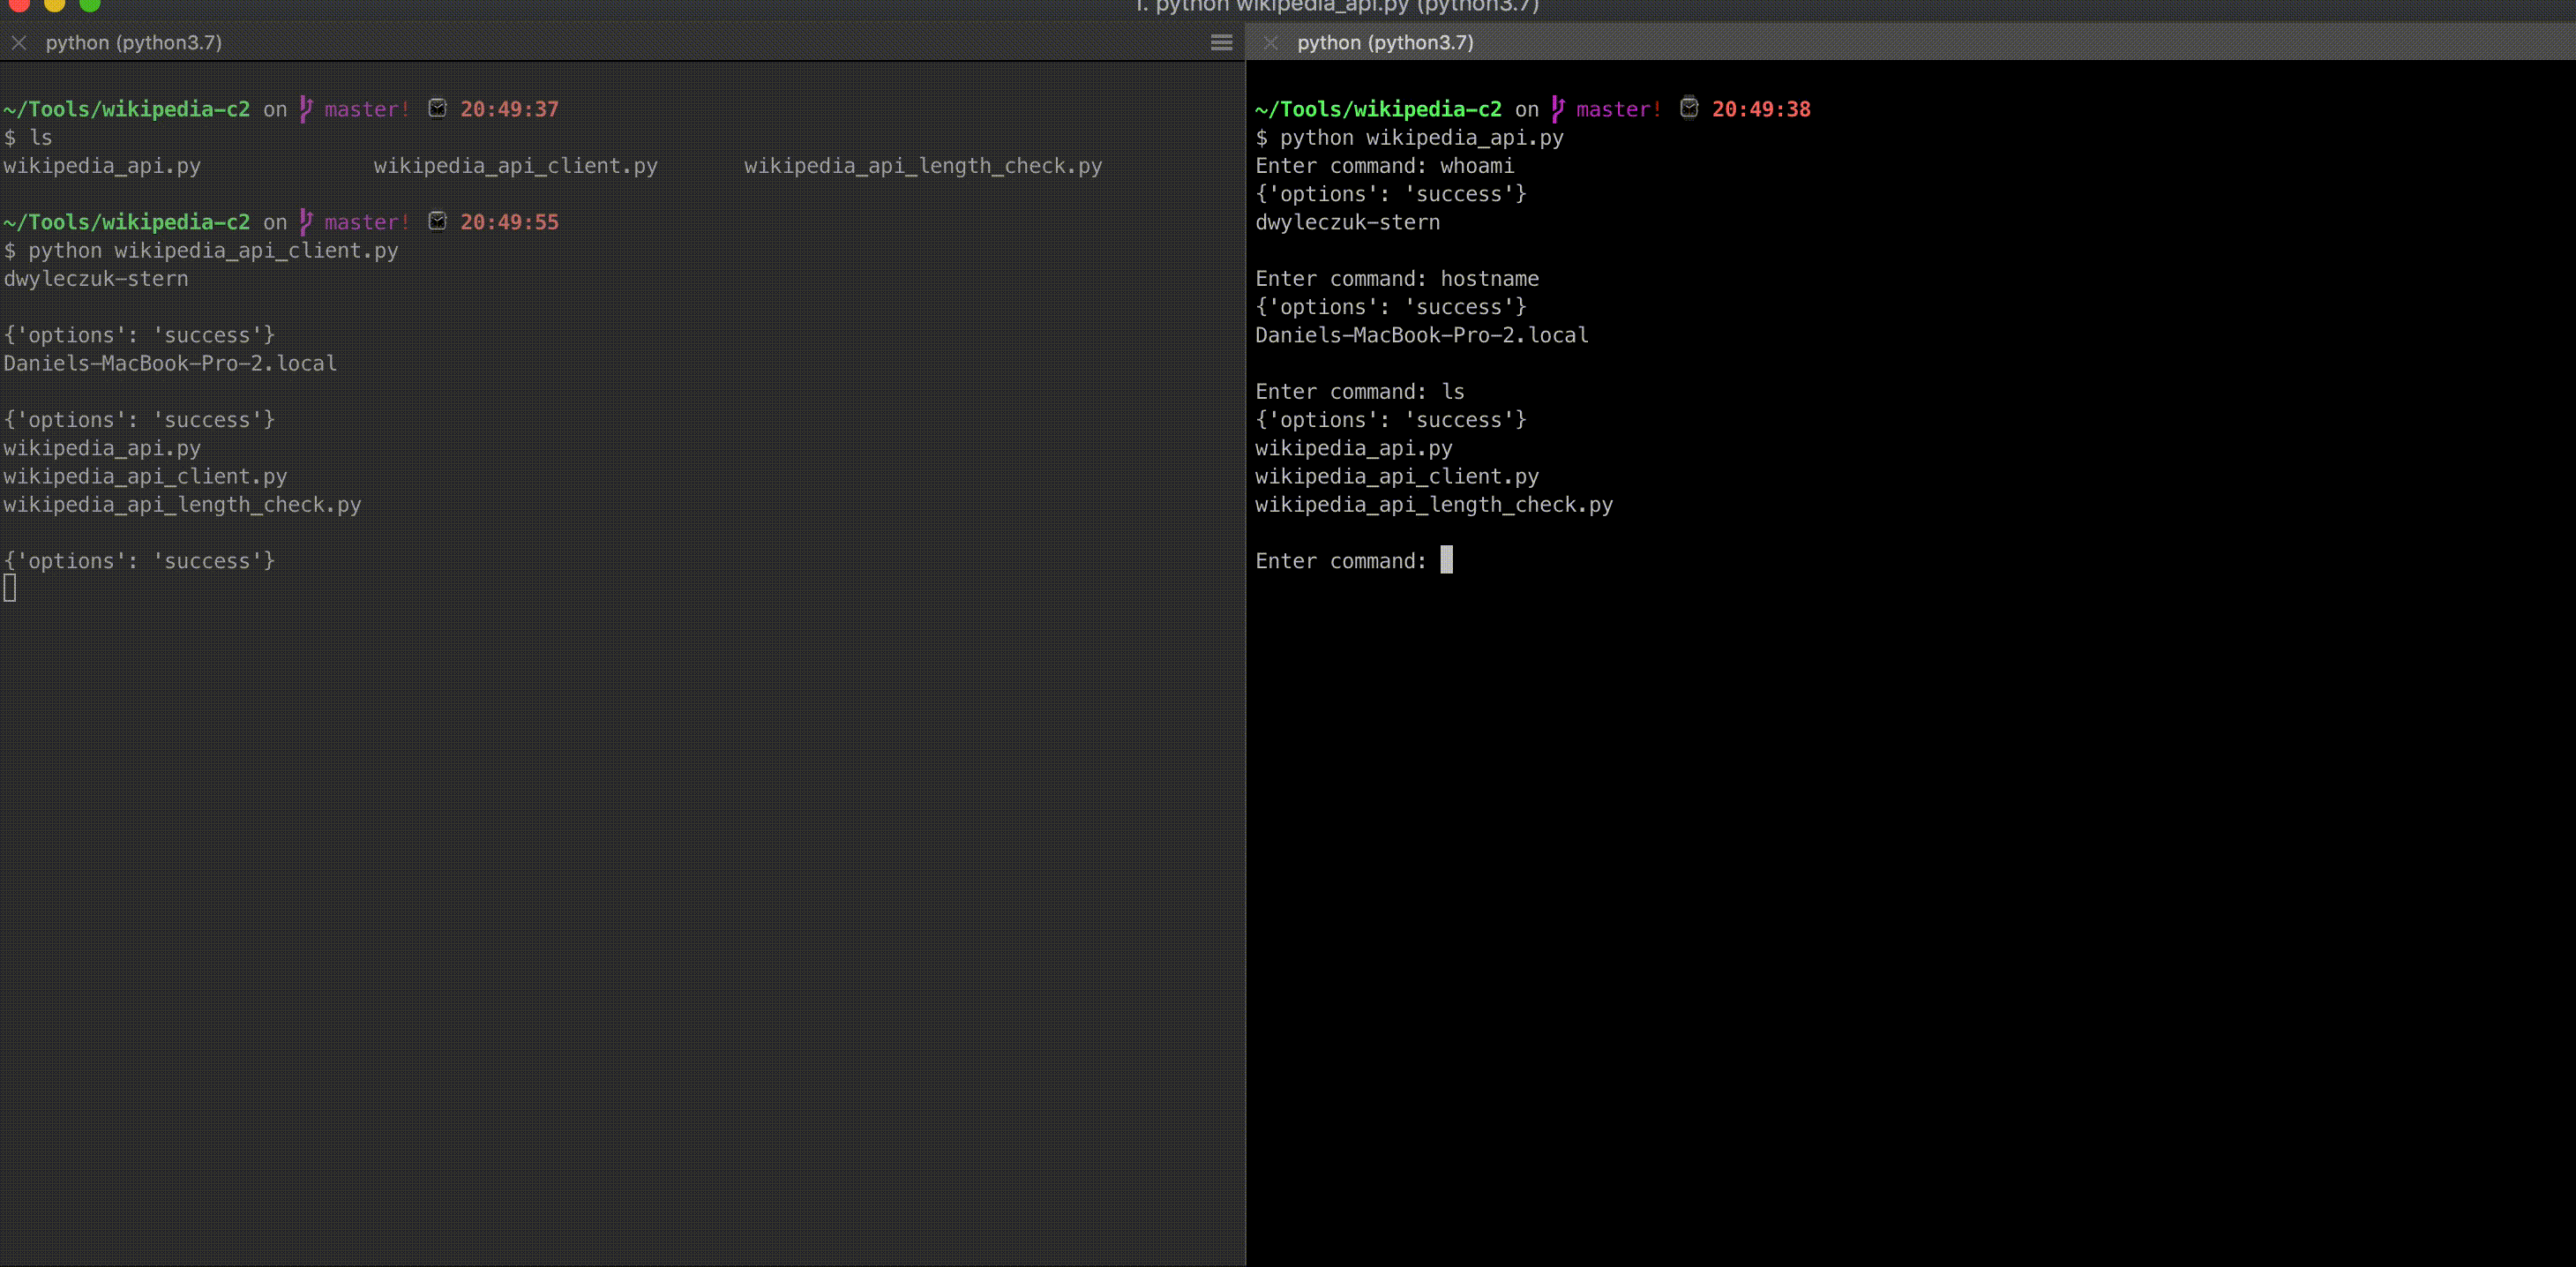 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control