

opentaint
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
ai-securityapi-securitycode-analysis+7
158
seqra/opentaintFormal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
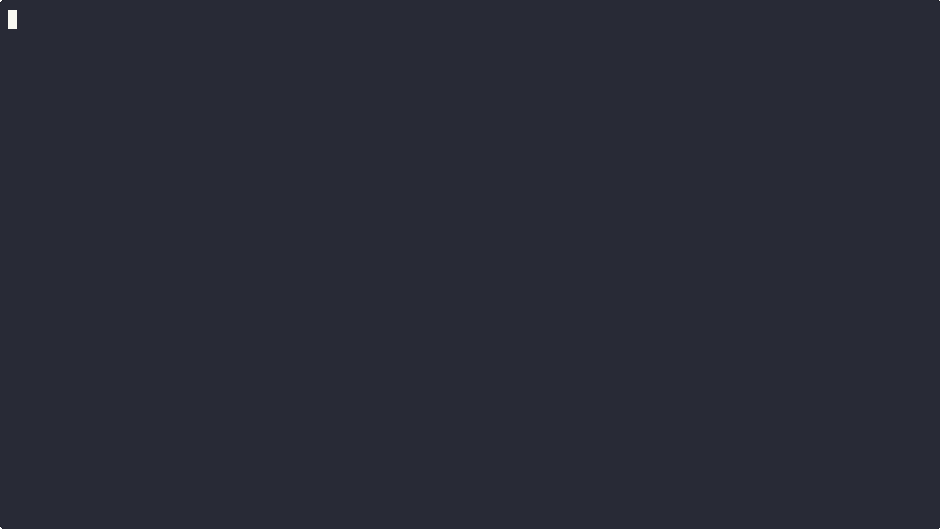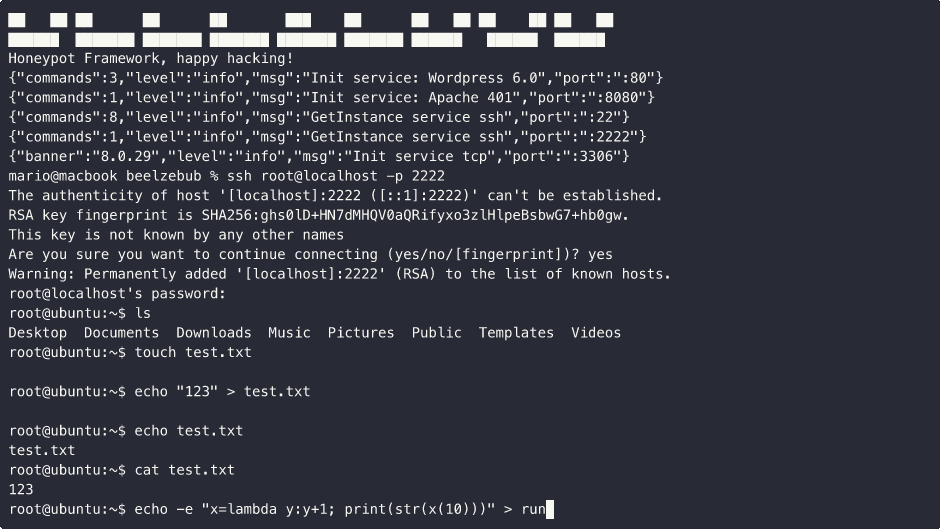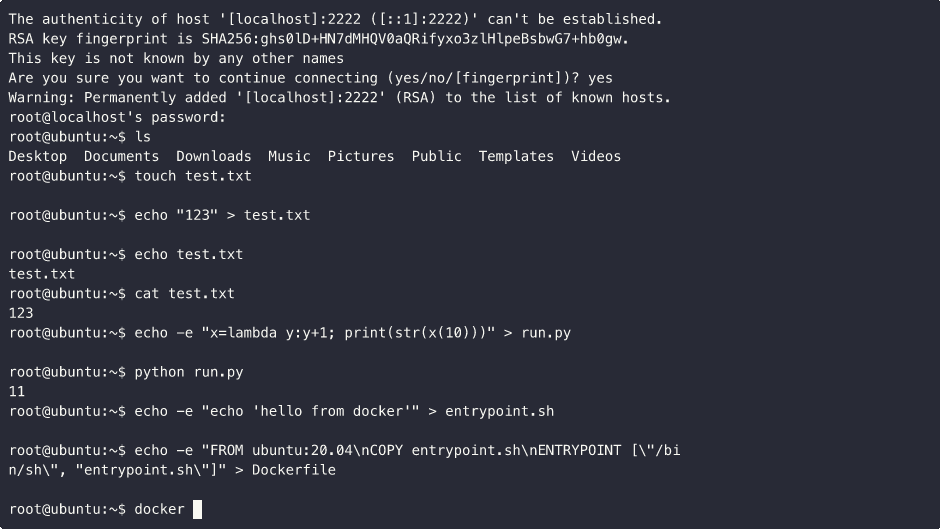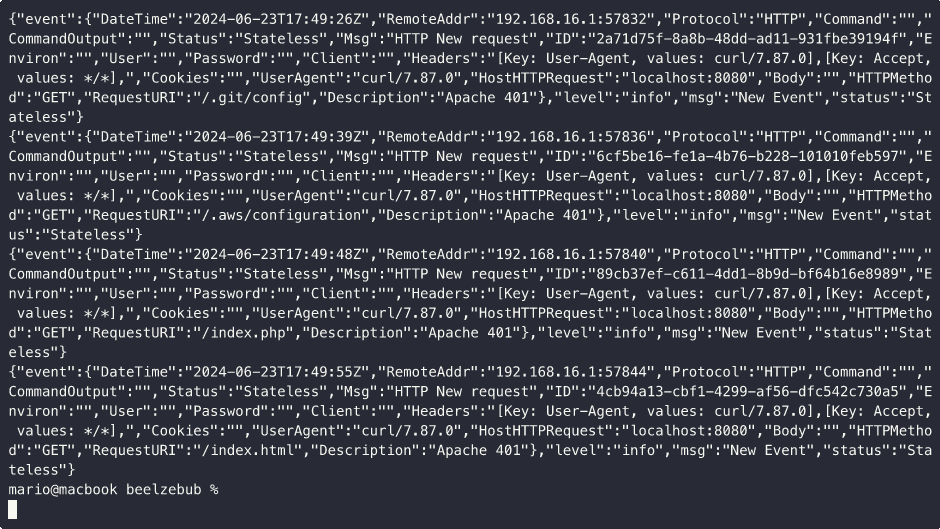 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
 sleuthco/clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF…
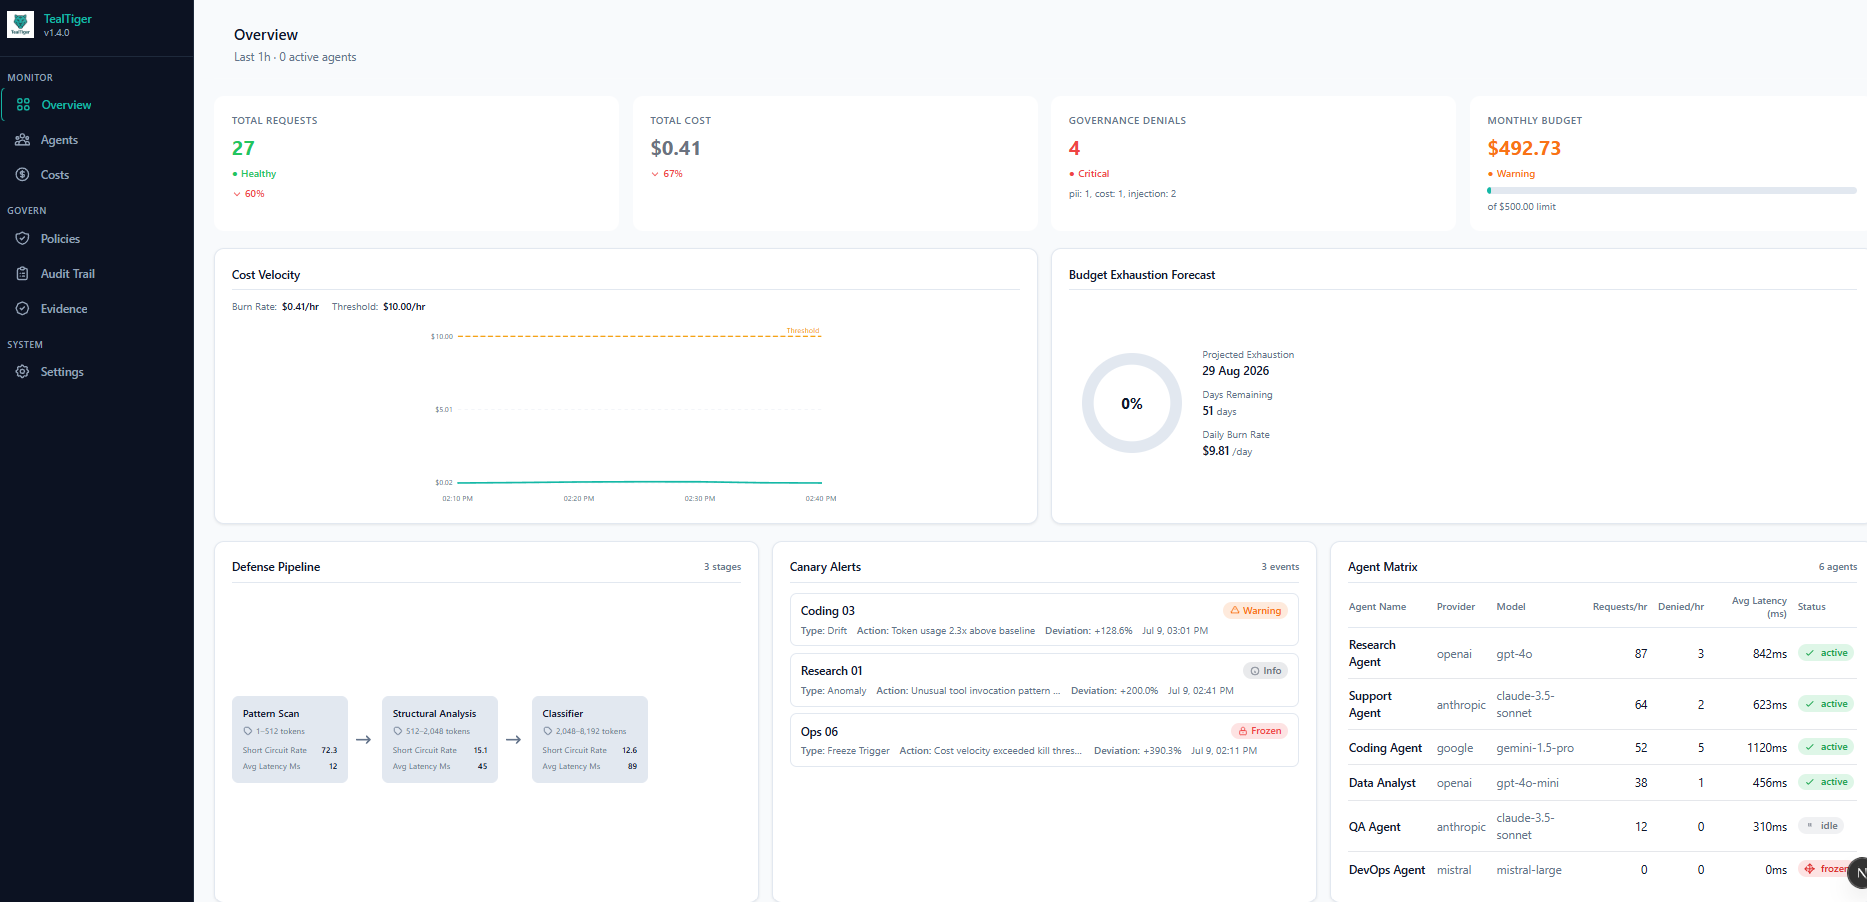 agentguard-ai/tealtiger
Powerful protection for AI agents - Open-source security and cost tracking for AI applications
 juanlunaia/aegis-latent-core
AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 ilhomjonr/cve-2026-67598
CVE-2026-67598 — Emlog Pro: disabled TLS certificate validation in AI assistant (MITM → API-key theft). CWE-295, CVSS 9.1. Reported by @IlhomjonR.
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
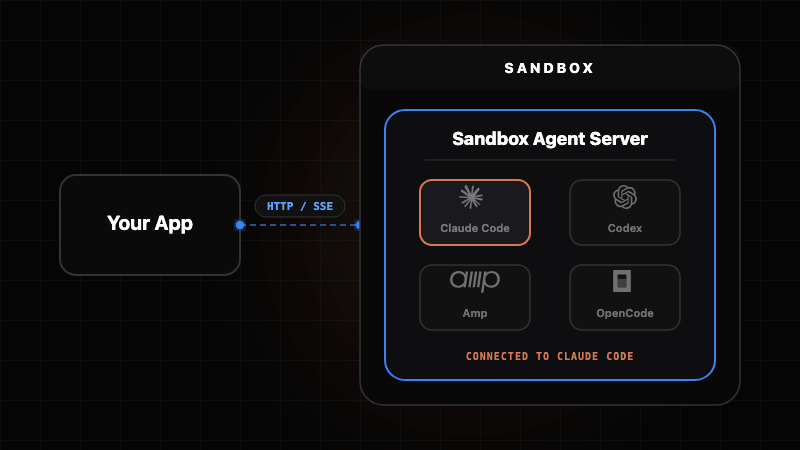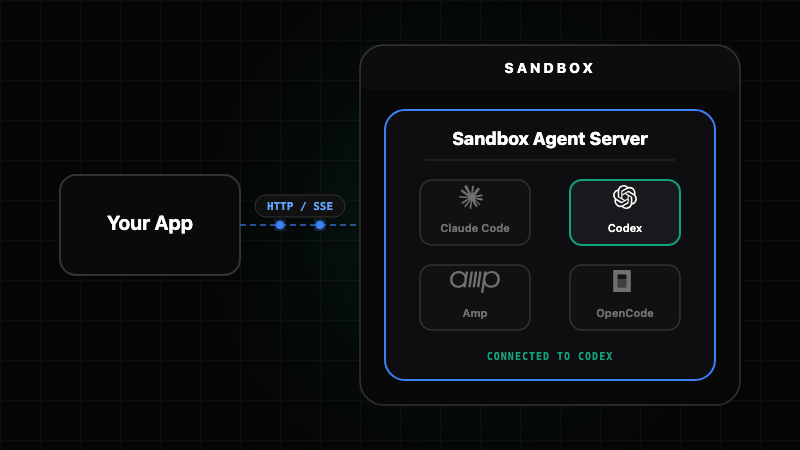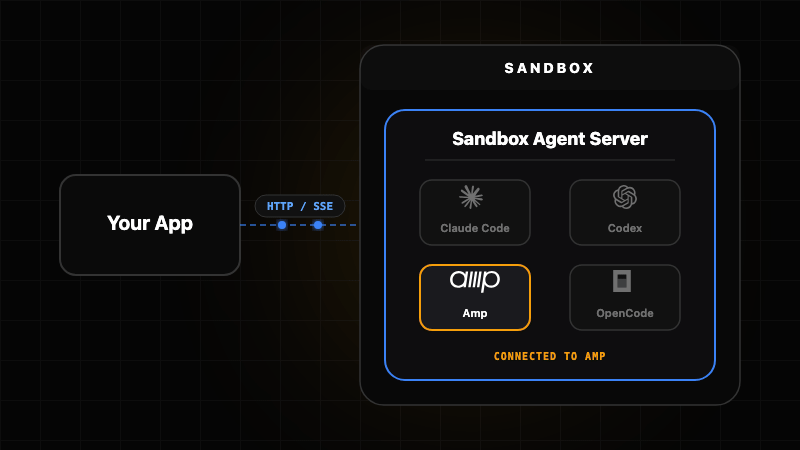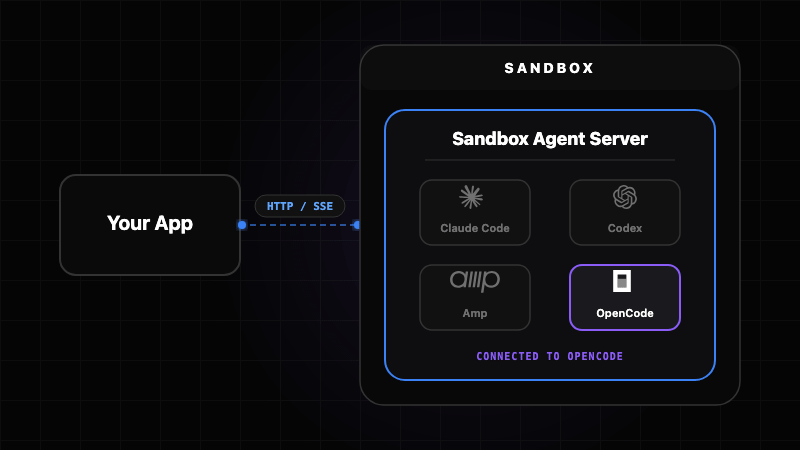 rivet-dev/sandbox-agent
Run Coding Agents in Sandboxes. Control Them Over HTTP. Supports Claude Code, Codex, OpenCode, and Amp.
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.