
Windows-Python-RAT
 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
api-securitycommand-and-controlpayload-development+3
118
the404hacking/windows-python-ratA New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 oh-az/noargs
Windows API hooking tool that dynamically spoofs and conceals process arguments via Detours library and PEB manipulation, enabling stealthy process…
 everywall/ladder
Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
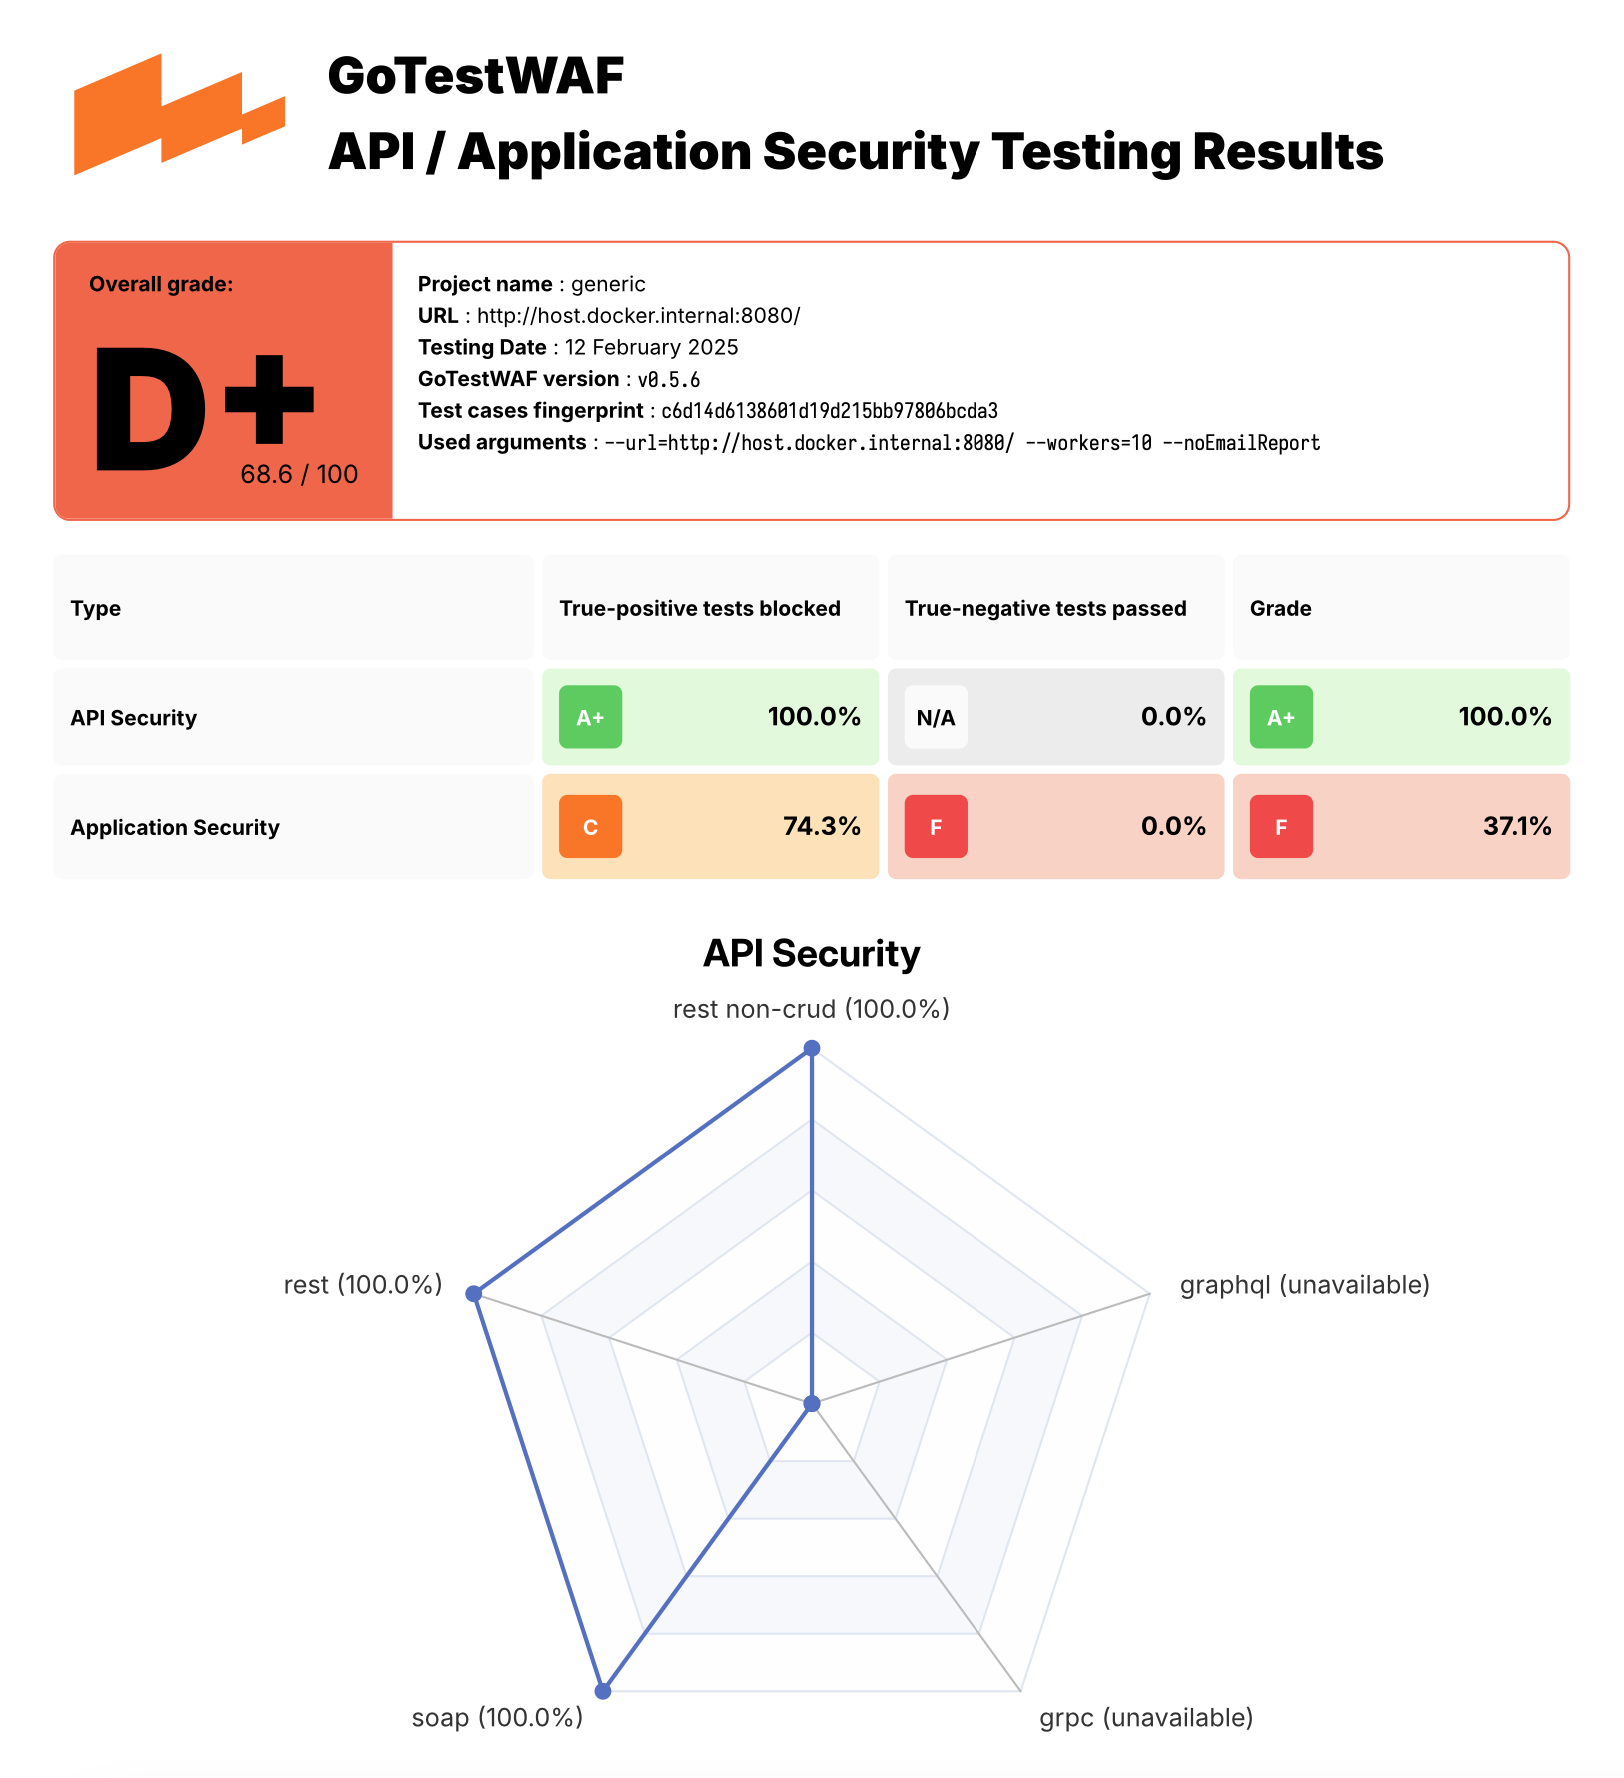 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 shoucheng3/asf__nifi_cve-2023-36542_1-22-0
Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…
 shoucheng3/apache__nifi_cve-2022-33140_1-16-22
Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…
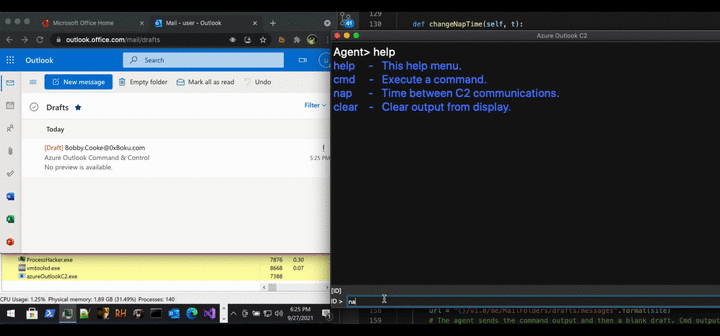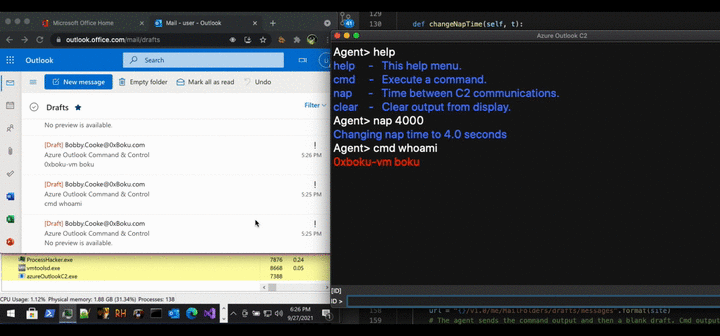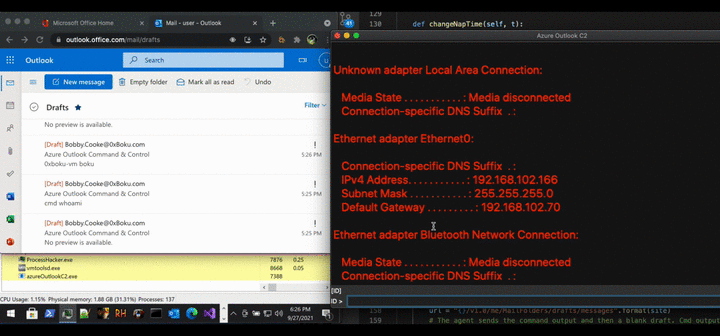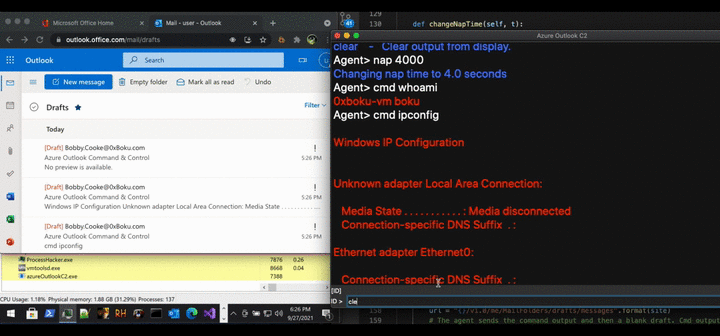 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 sushank05/mcp-doorman
A lightweight mcp to prevent poisoning CVE (CVE-2025-54136), researchers hijacking Claude Code/Copilot/Gemini via prompt injection, and hundreds of…
 nuid/nebulousad
NebulousAD automated credential auditing tool.
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
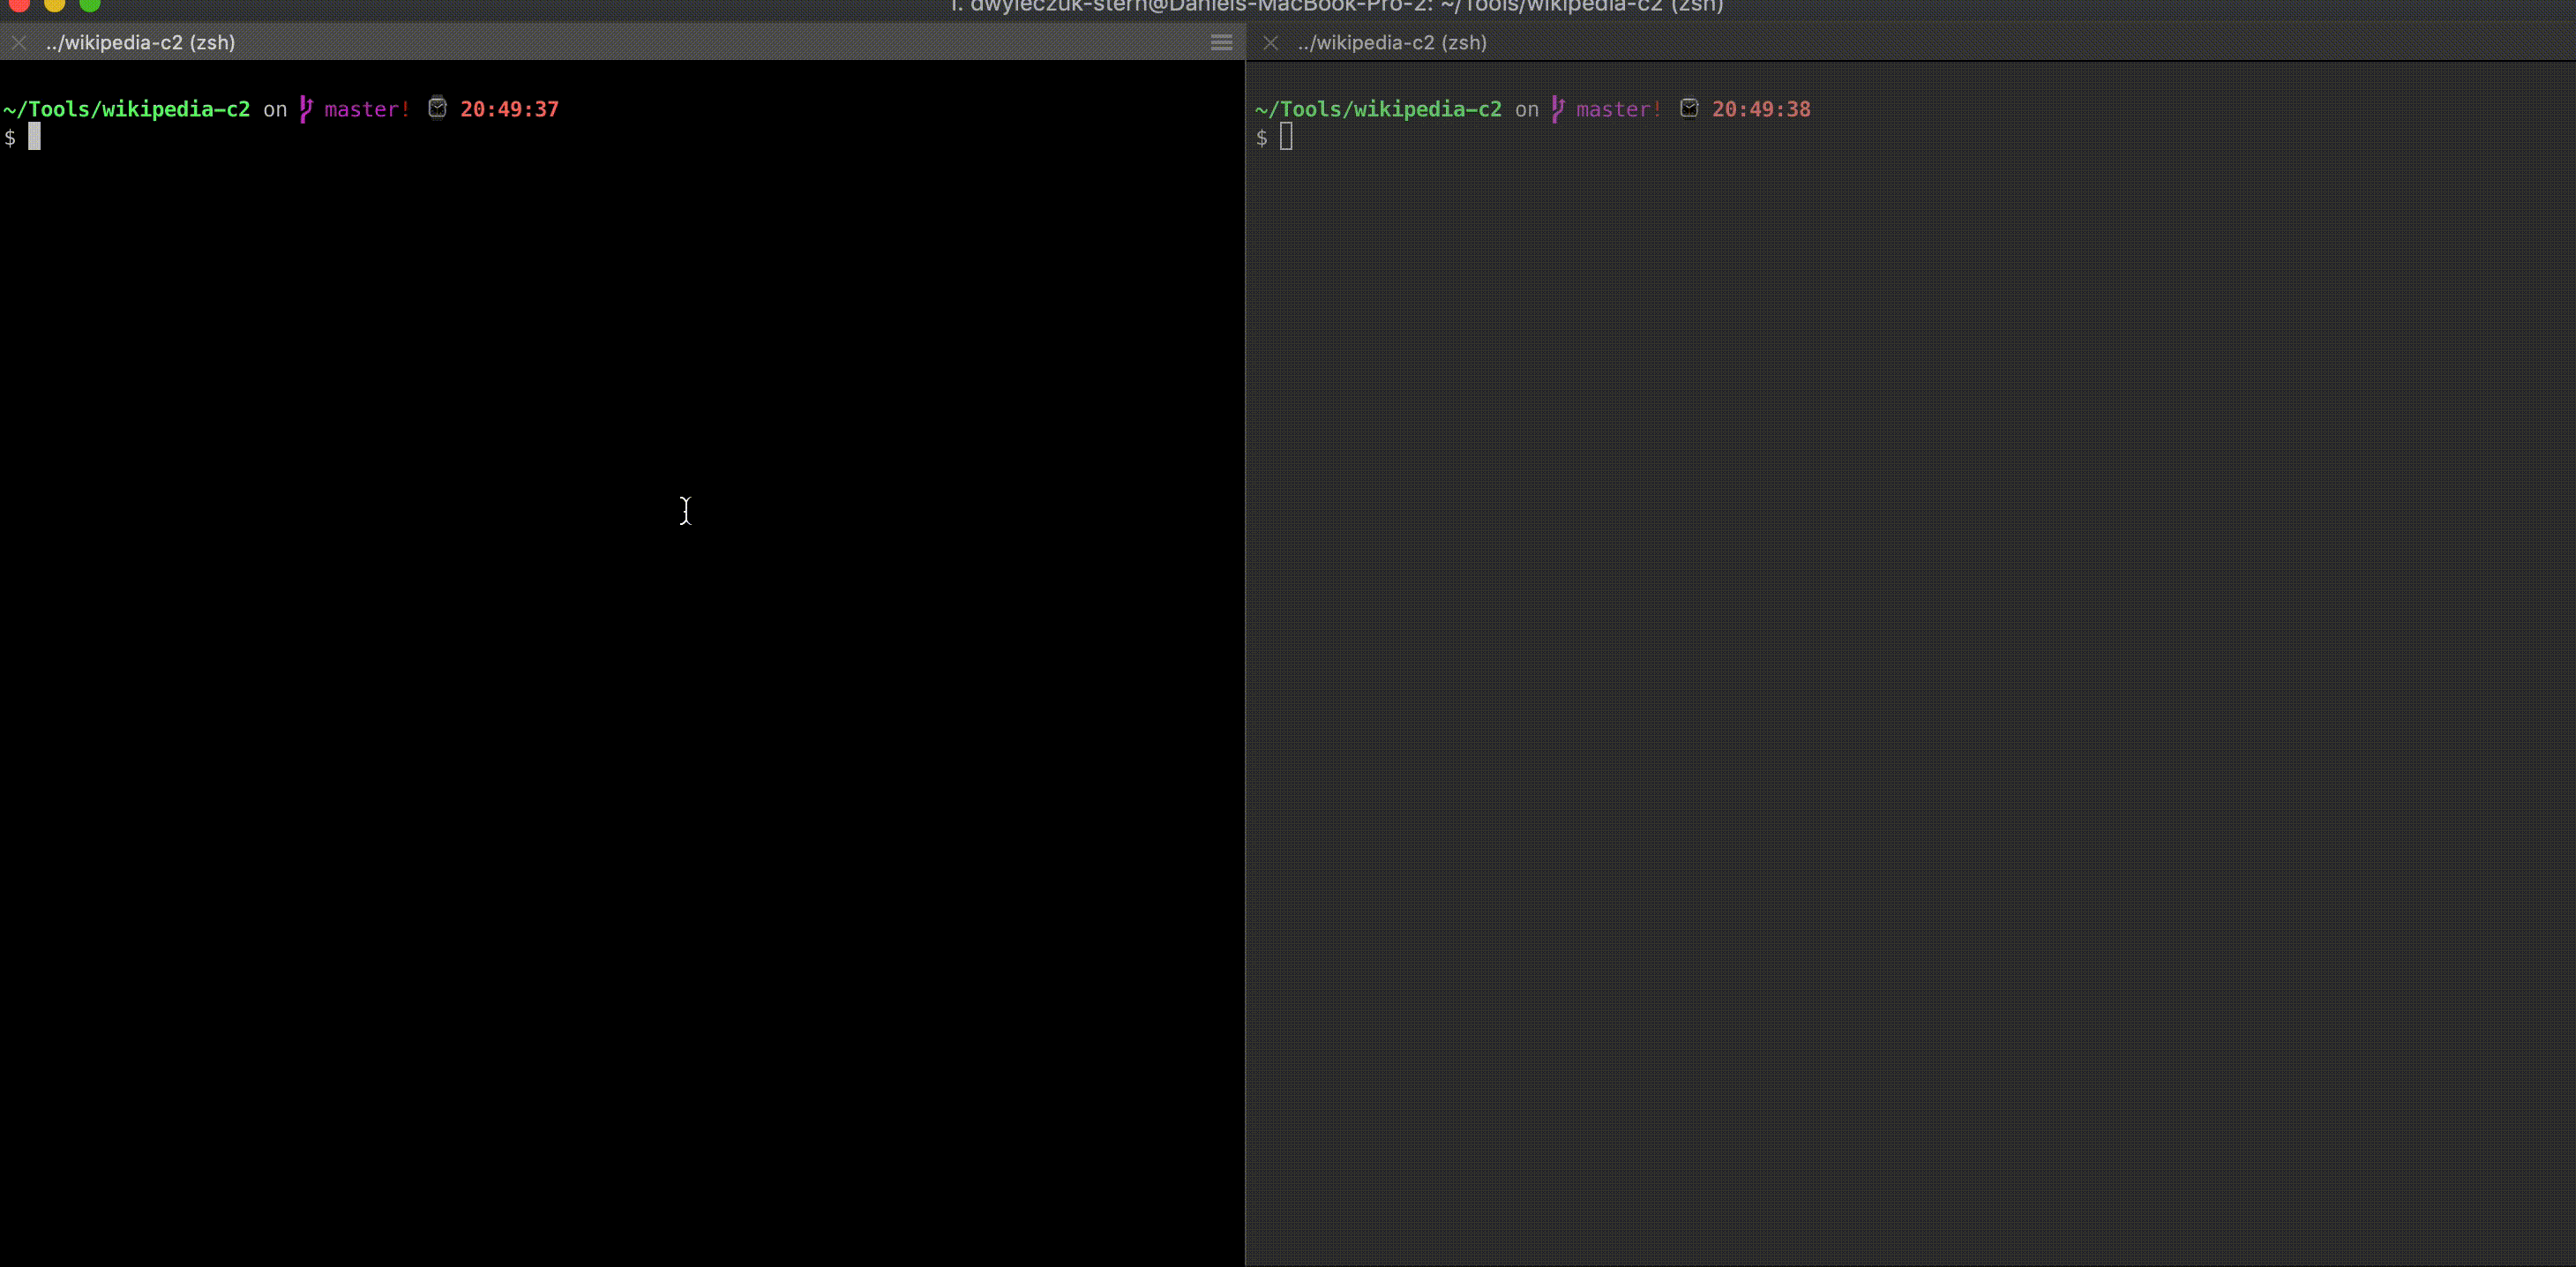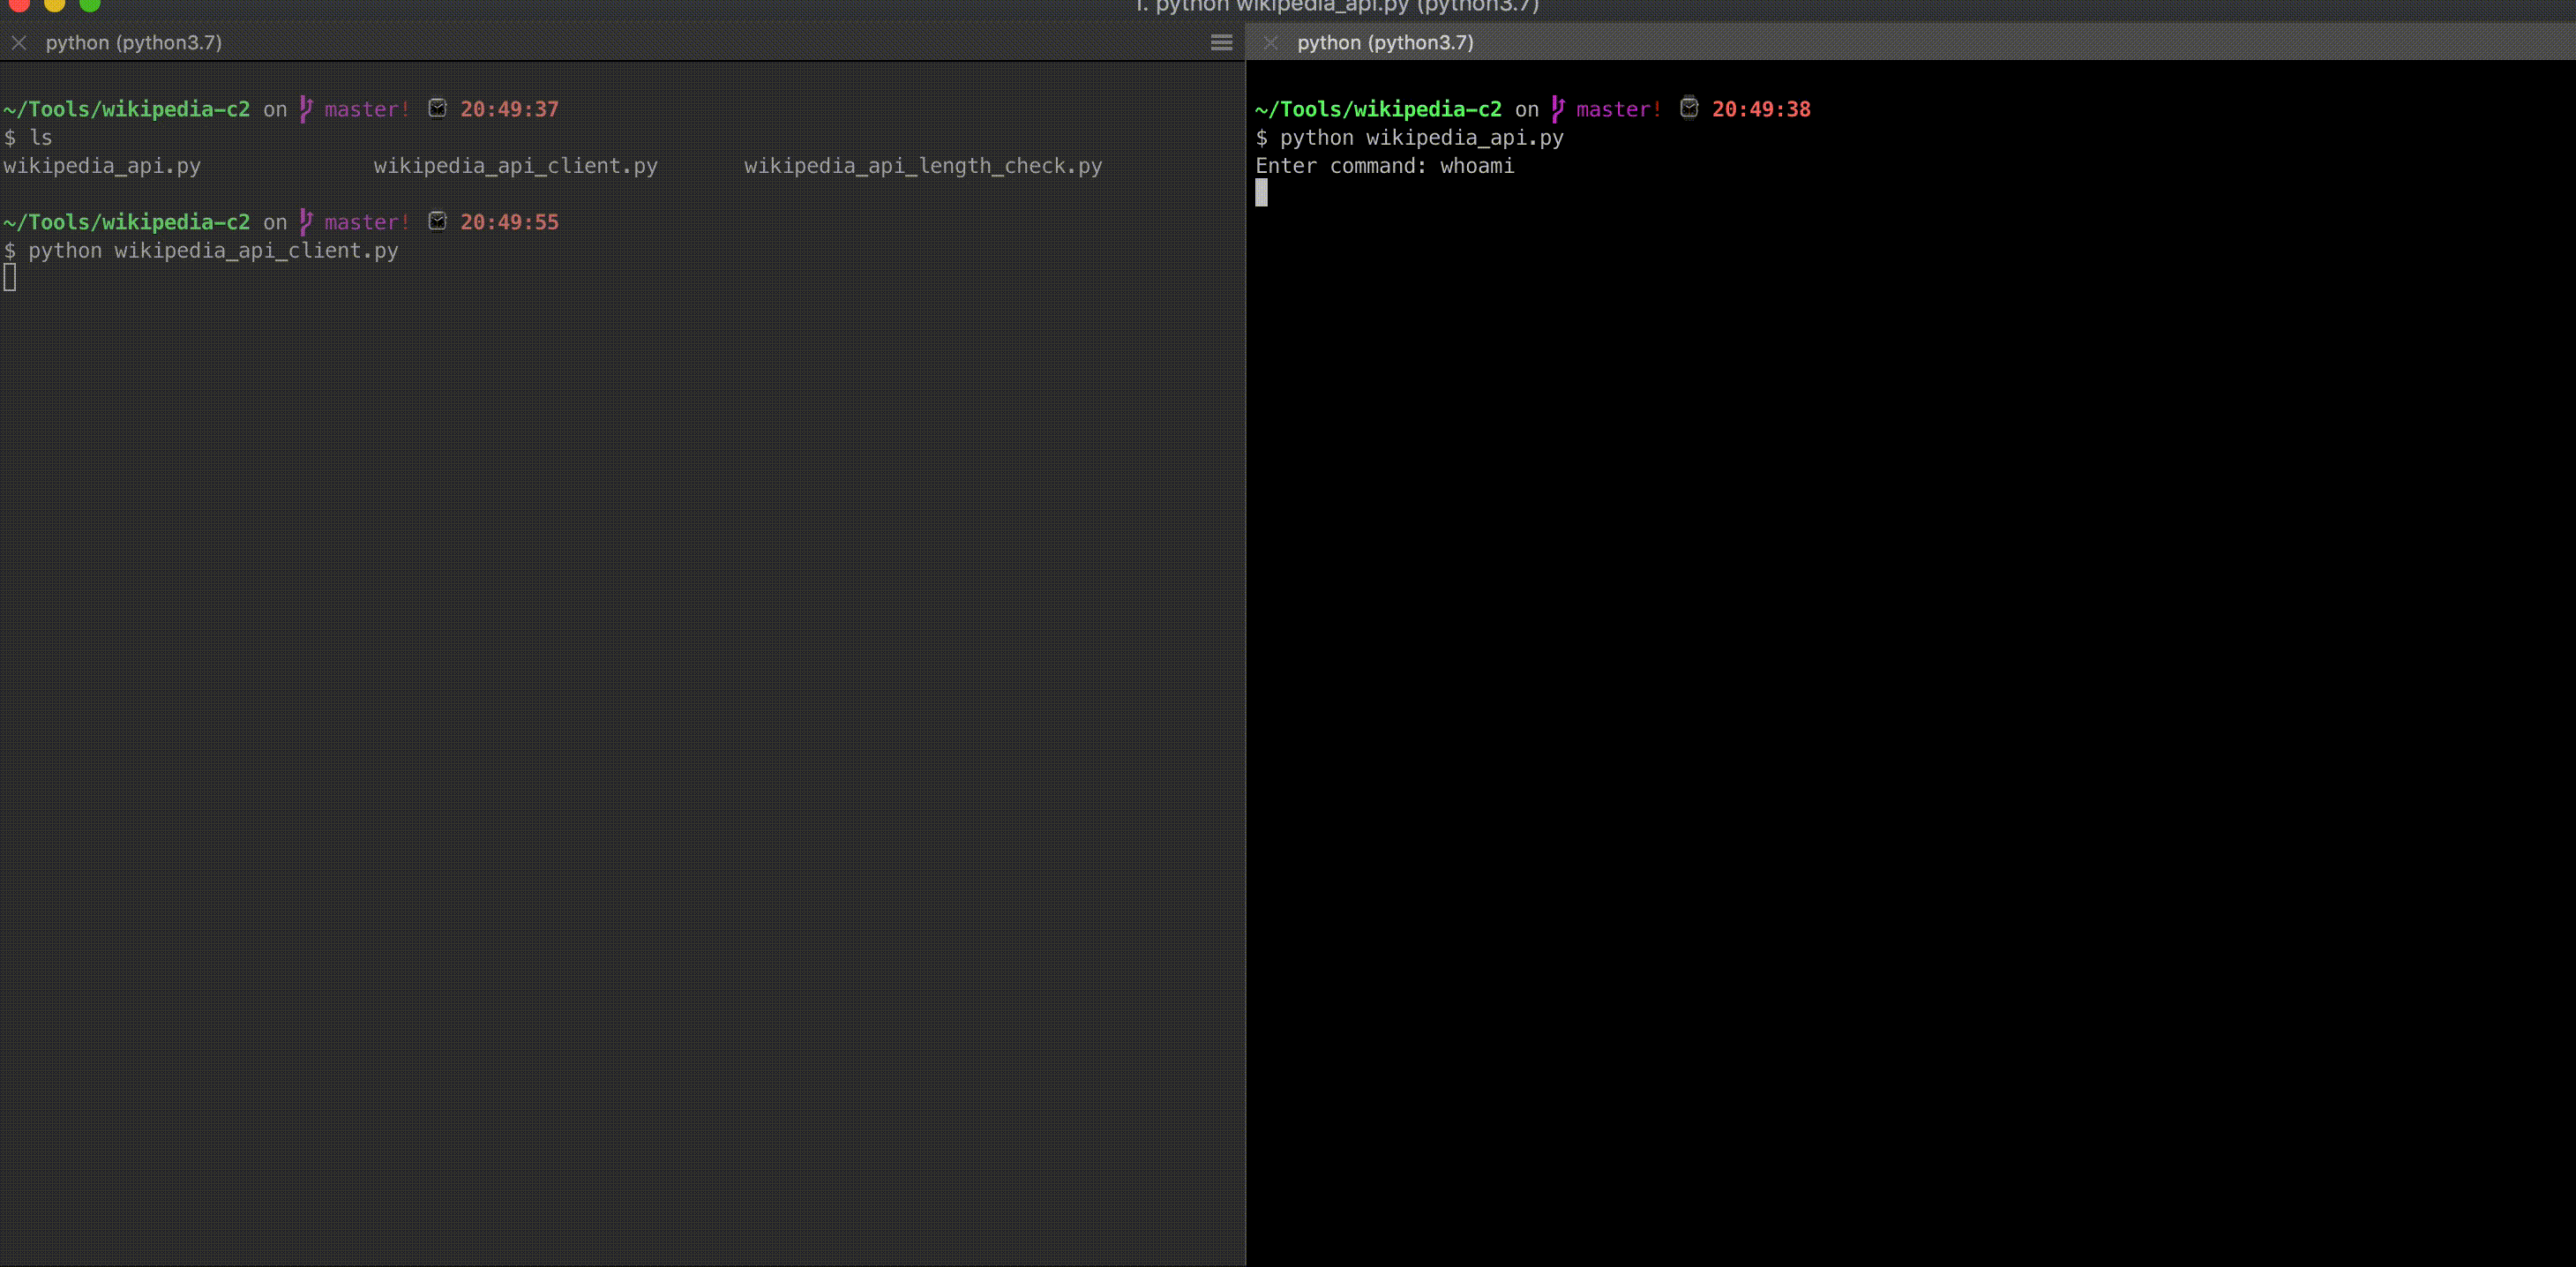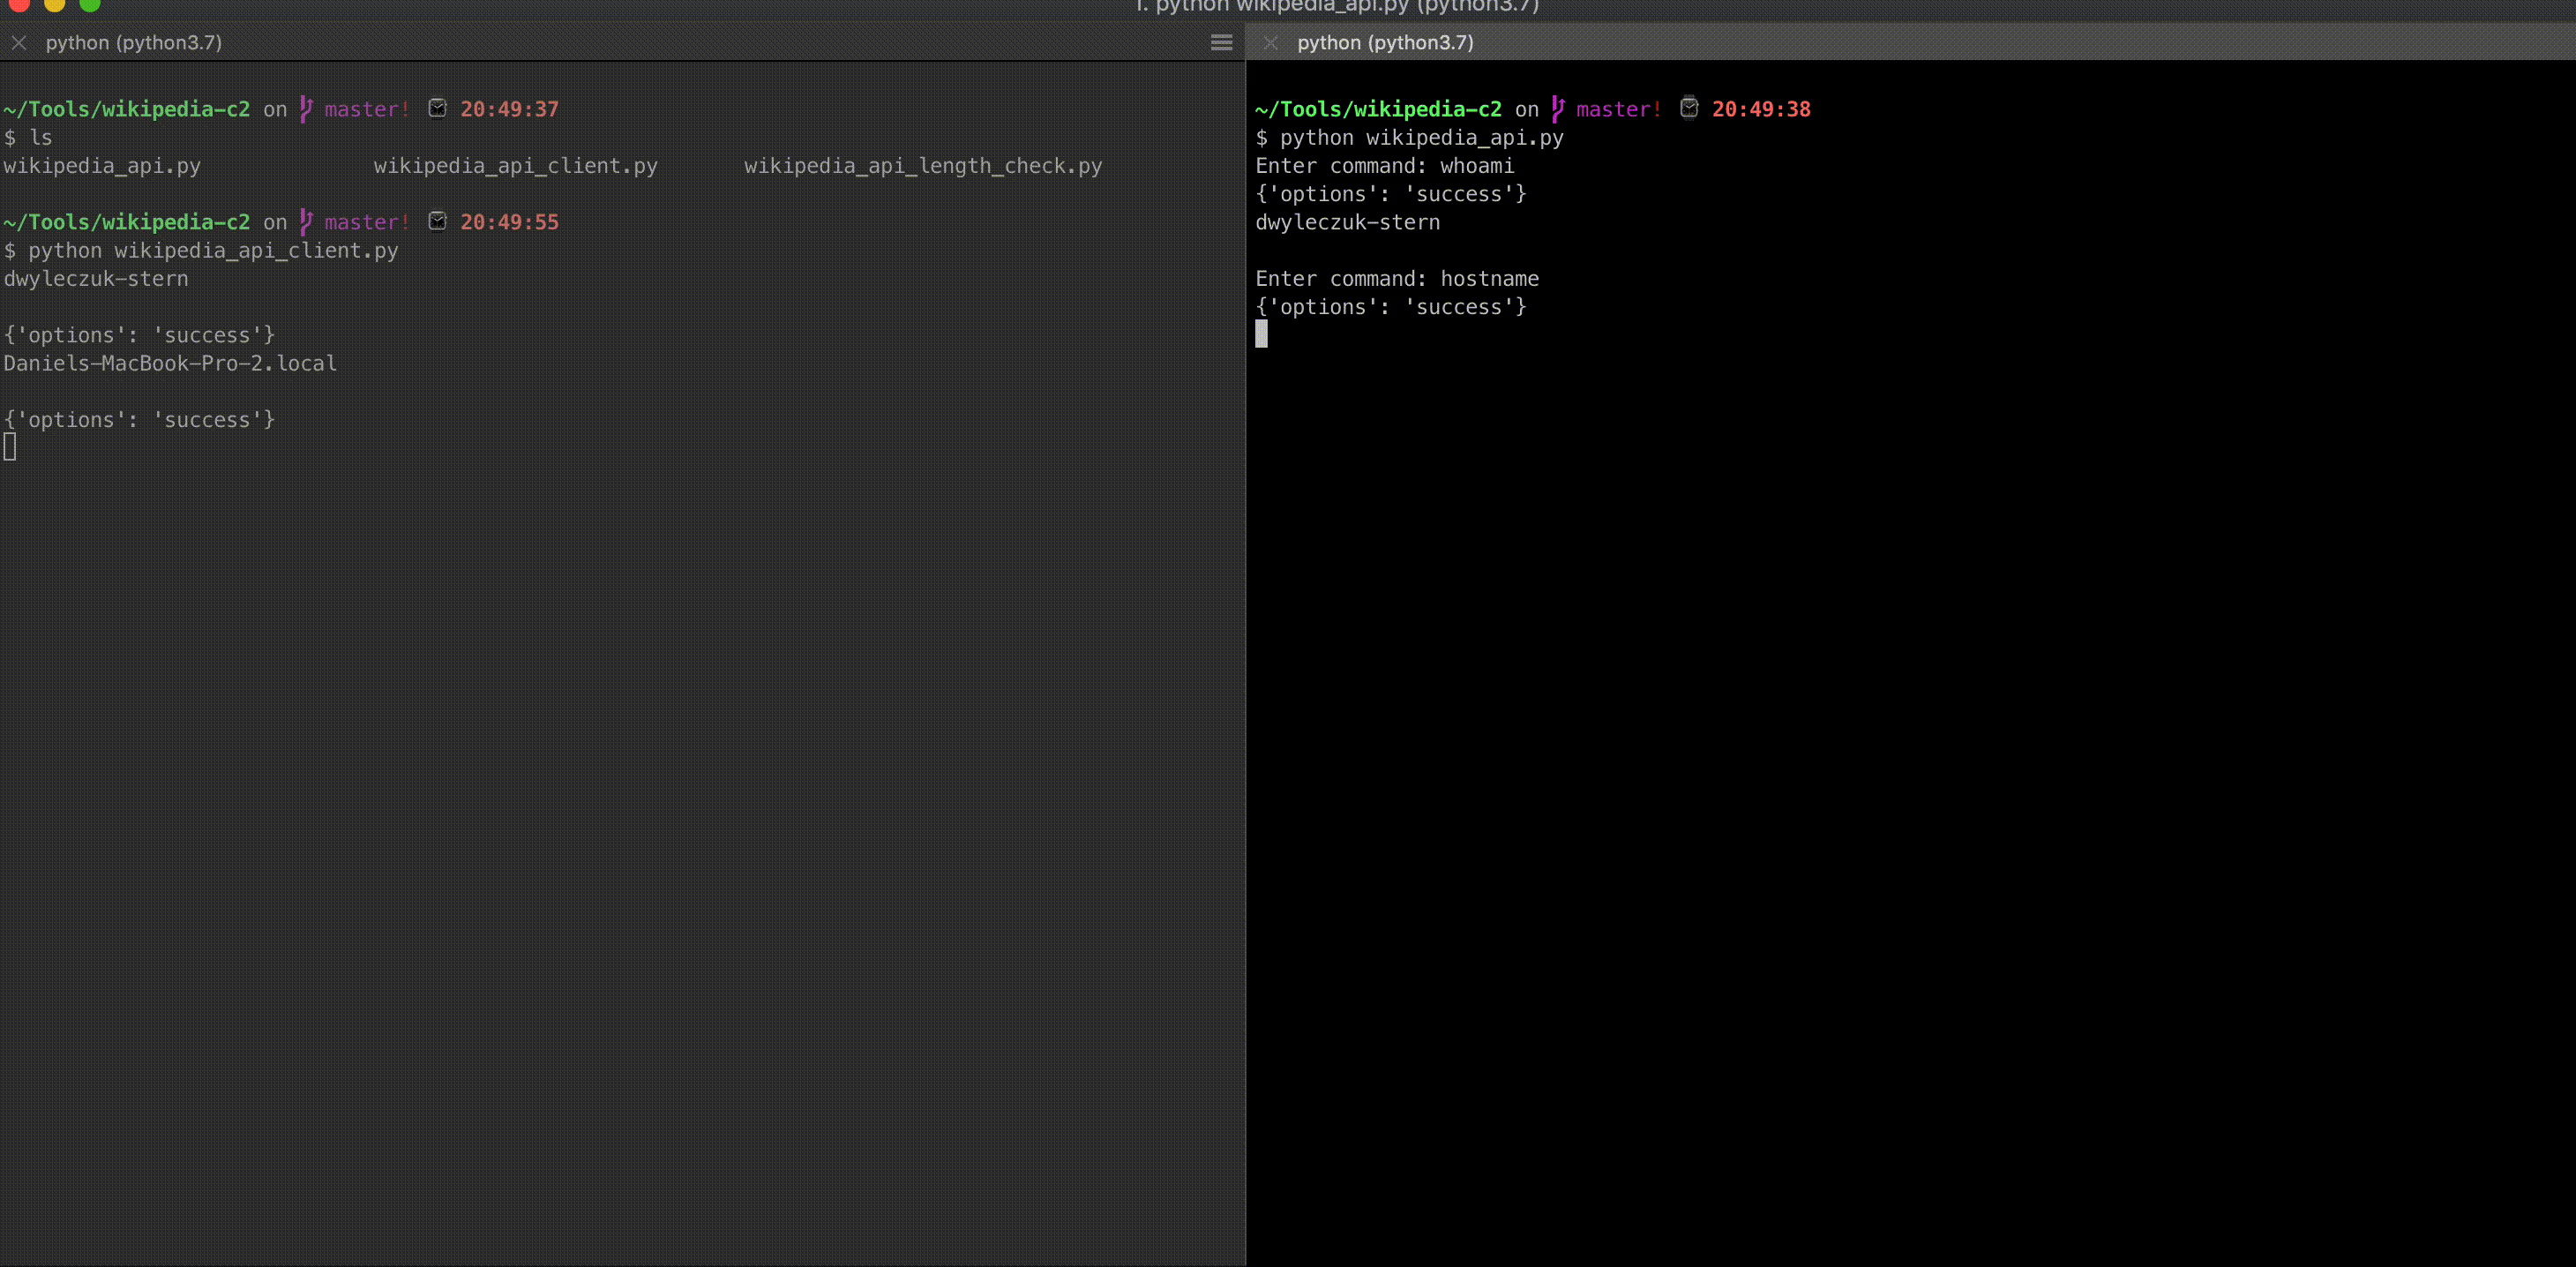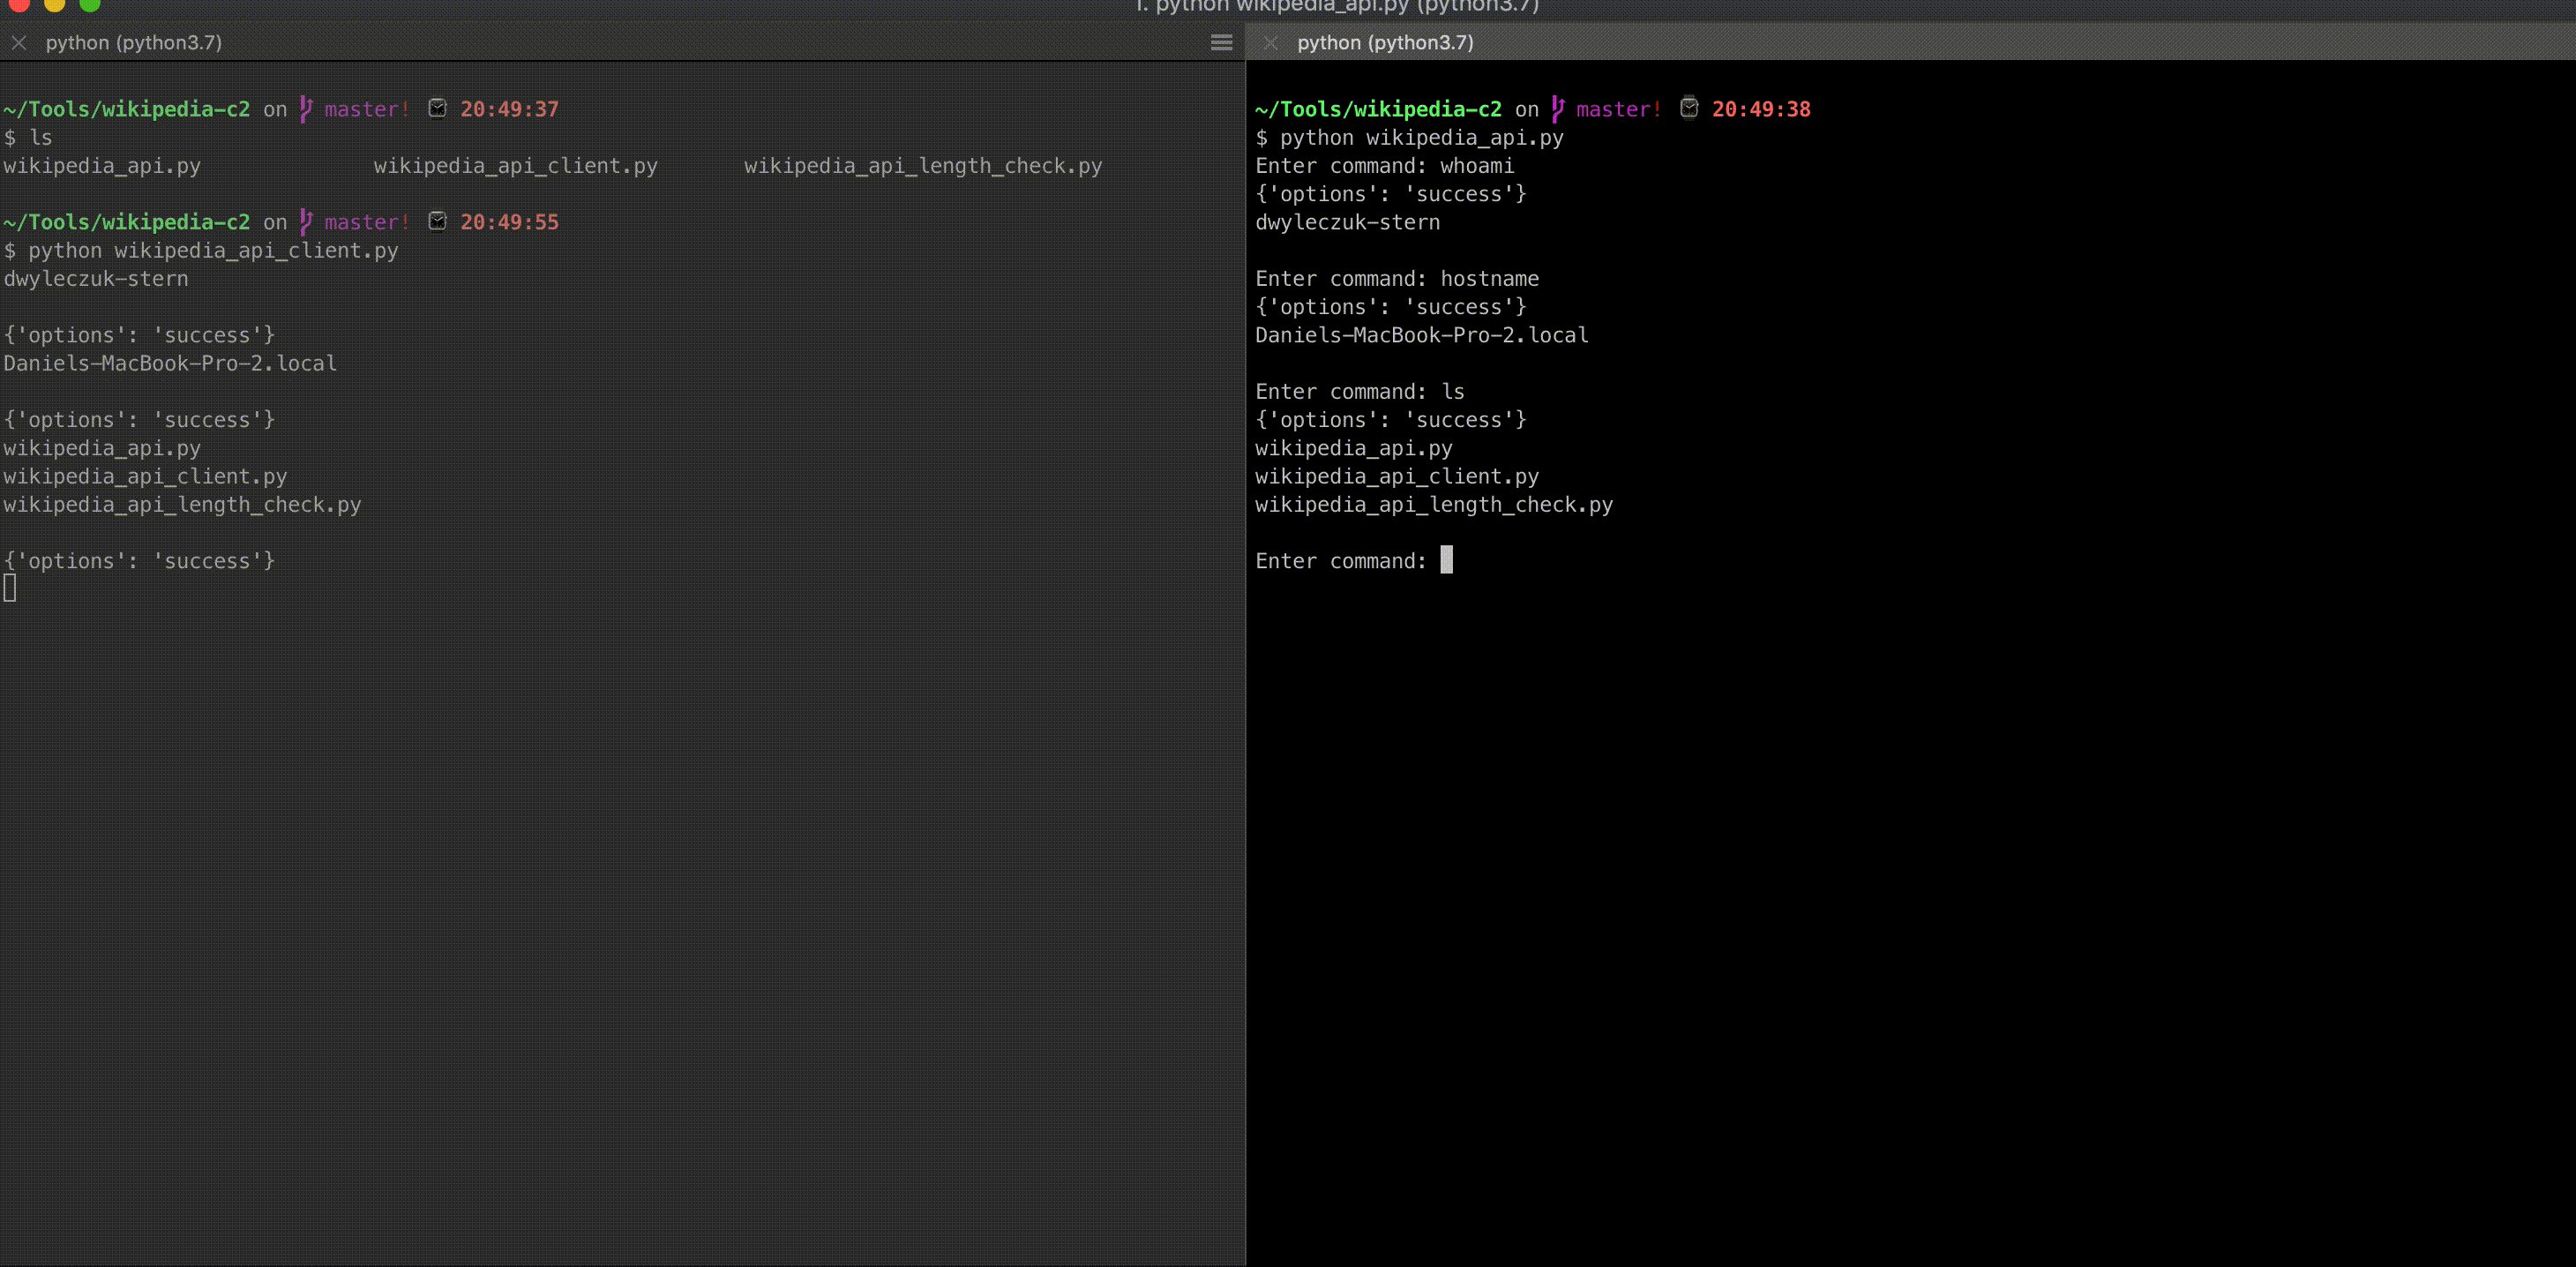 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
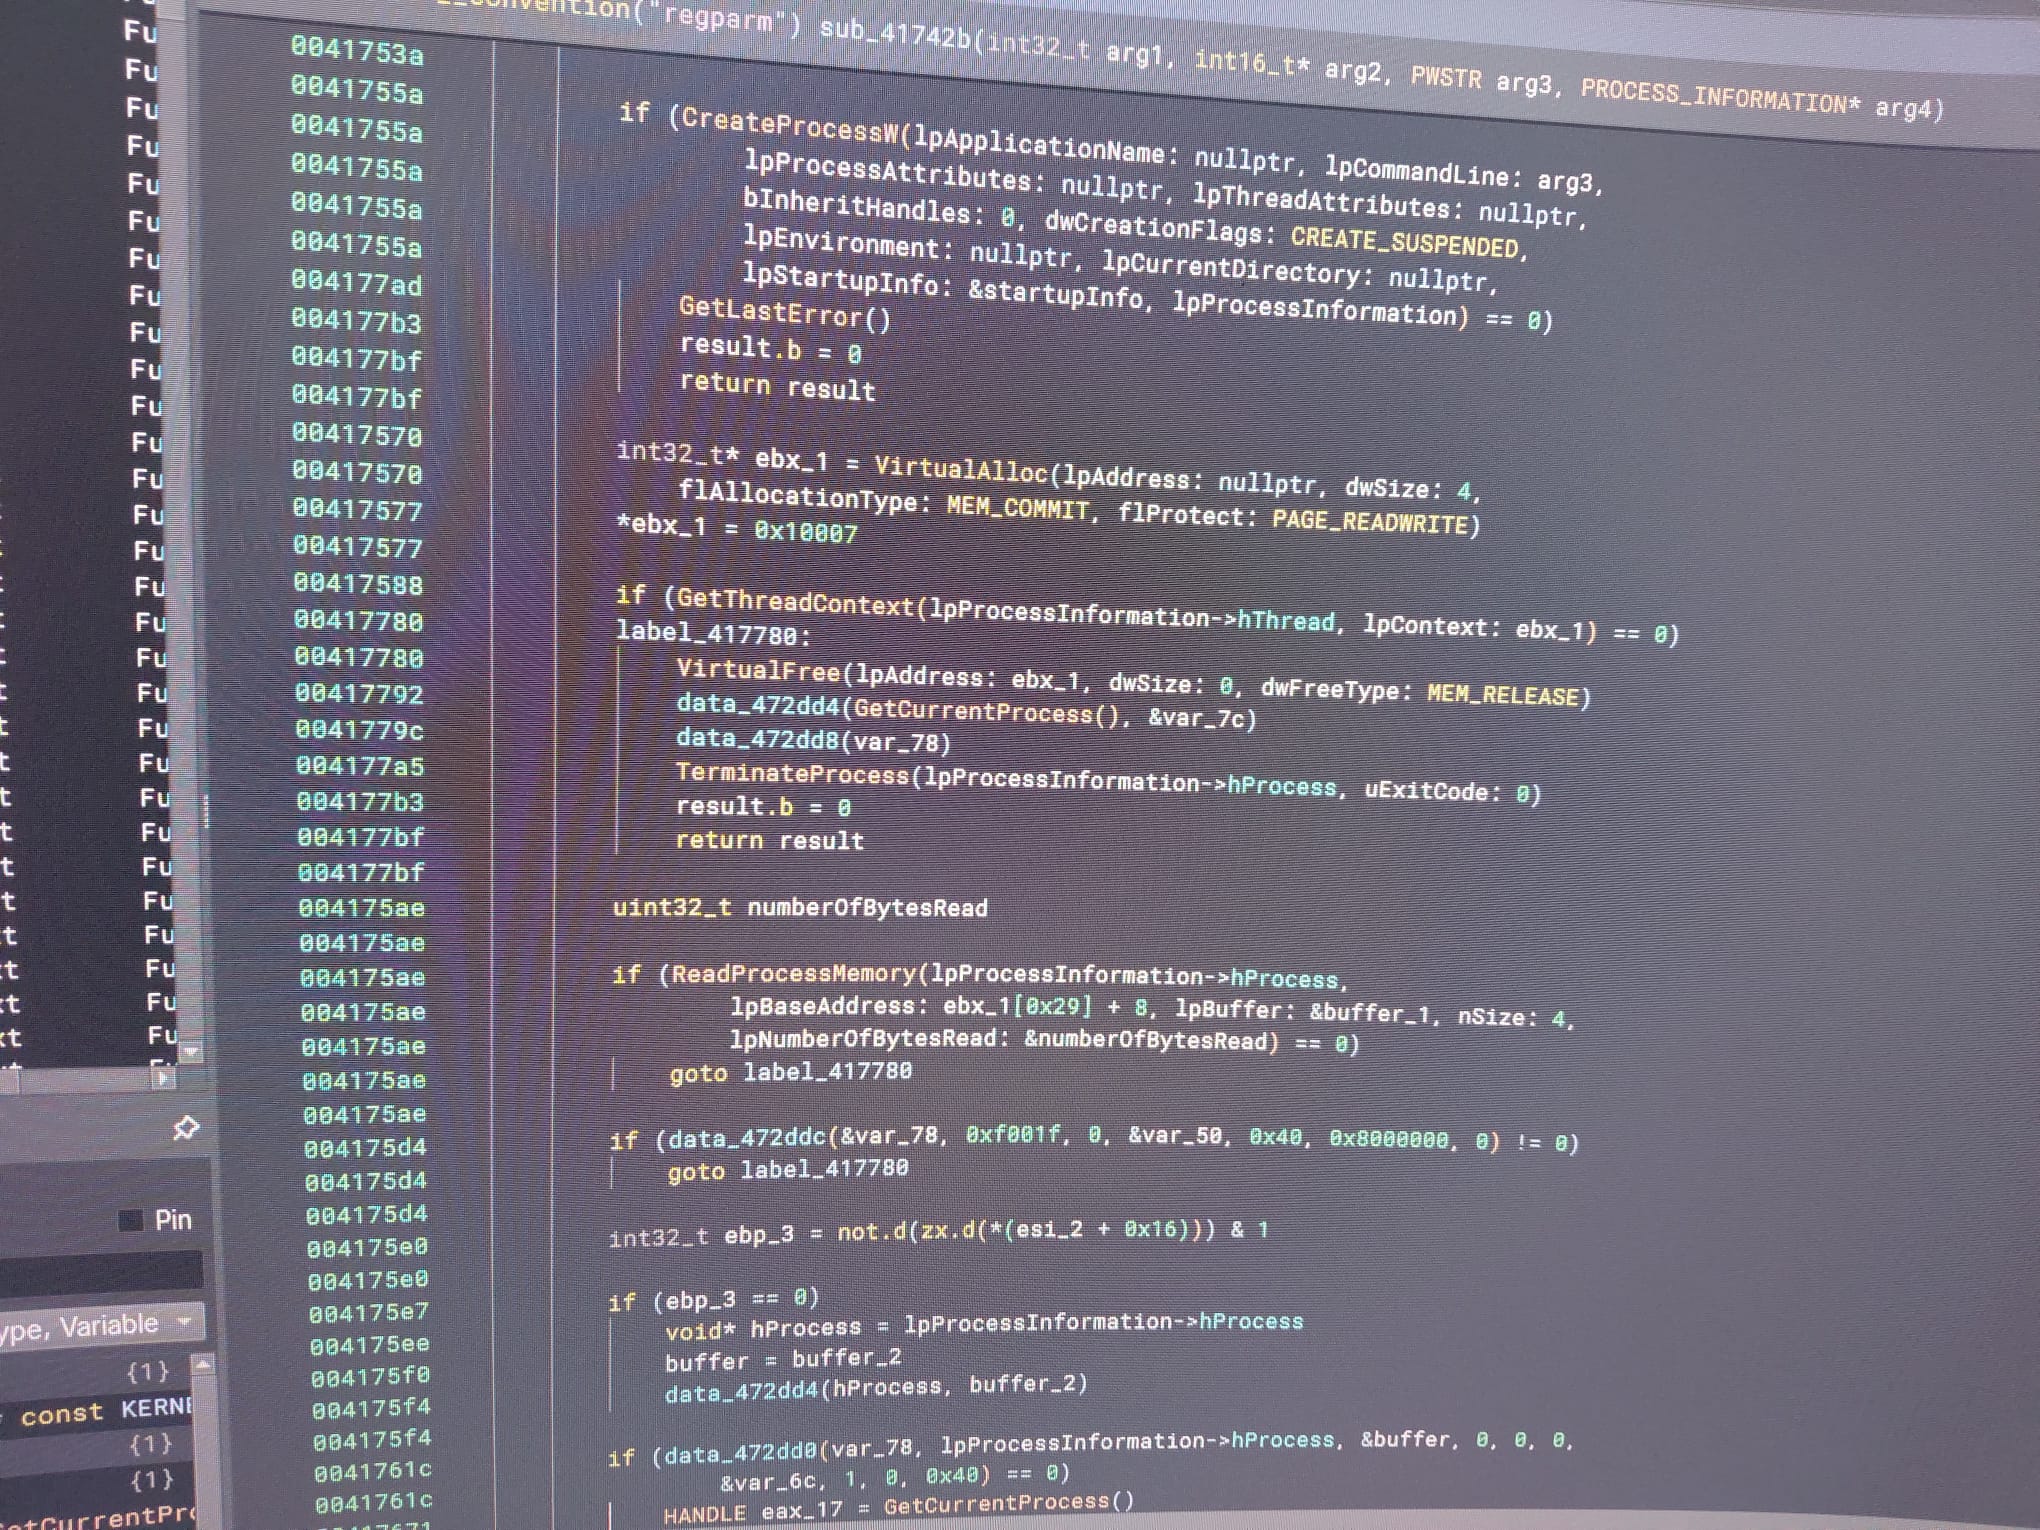 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478