
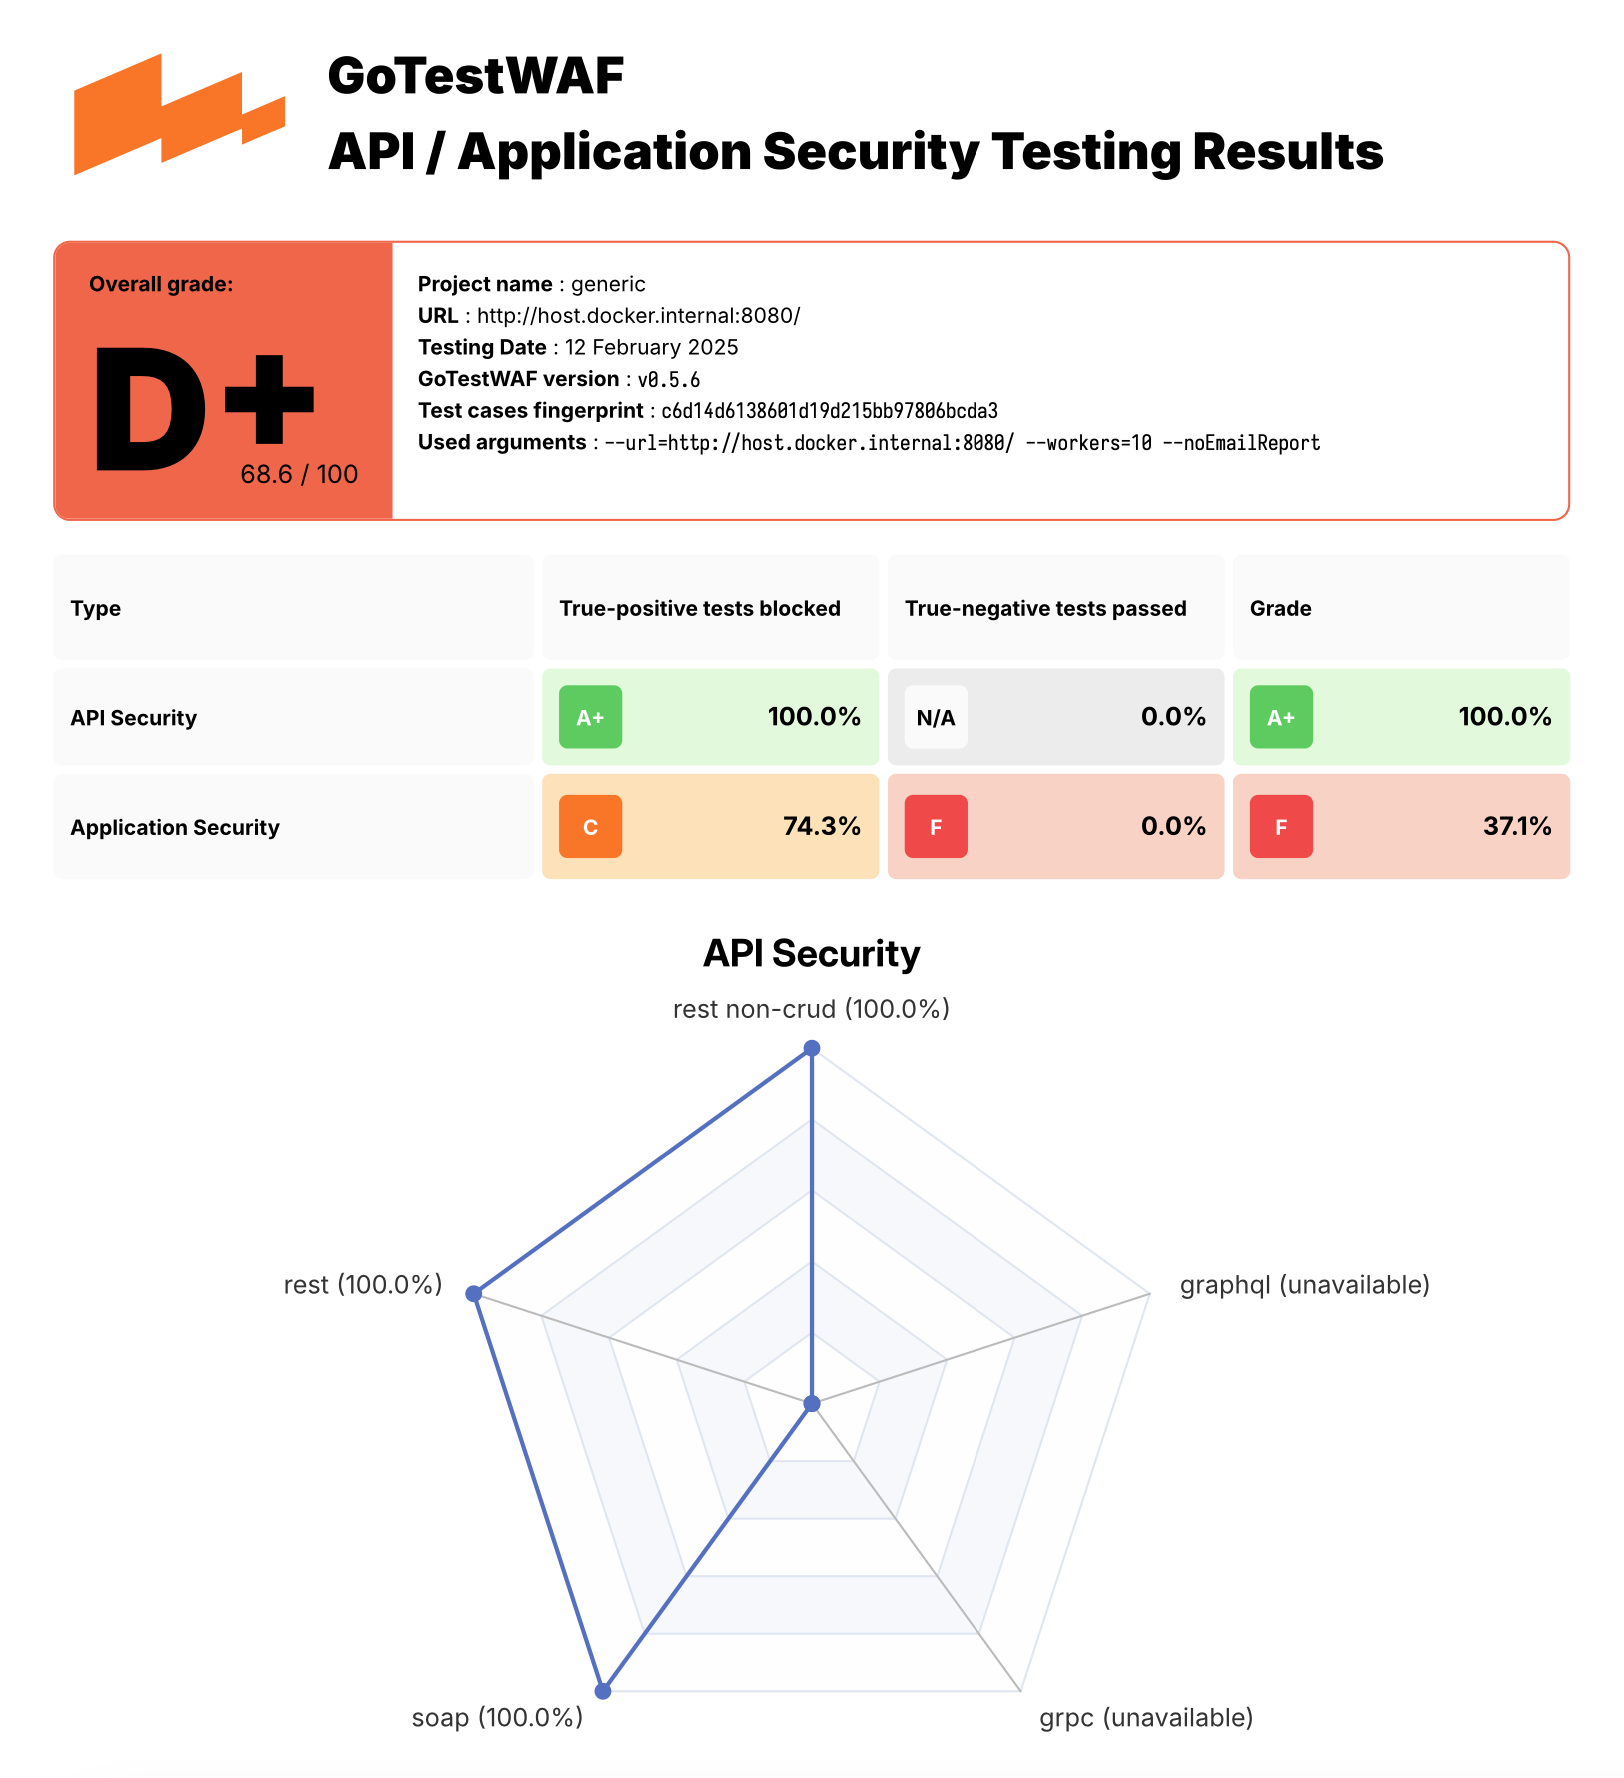
gotestwaf
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
api-securityapi-security-testingpenetration-testing+4
1.8k
wallarm/gotestwafAn open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 shoucheng3/springsource__spring-security-oauth_cve-2018-1260_2-3-2-release
OAuth and OAuth2 support library for Spring Security, enabling secure API authentication and authorization for consumer and provider implementations…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 opnsense/core
OPNsense GUI, API and systems backend
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.