
CVE-2025-6514
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection
api-securityauthenticationcommand-and-control+3
cyberency/cve-2025-6514mcp-remote exposed to OS command injection
 hereticl1nk/eits-portal-exploit-cve-2026-31367-poc
PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
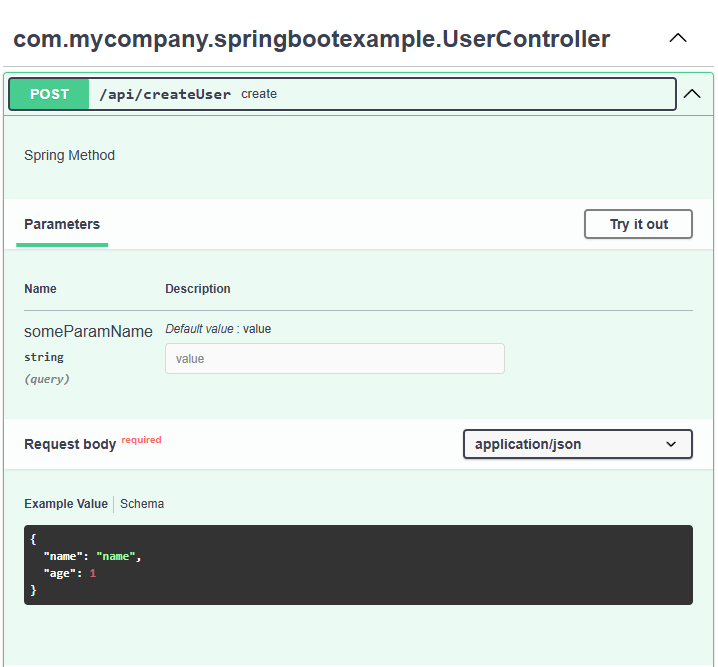 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…