
SentryPeer
 sentrypeer/sentrypeer
Distributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
api-securitynetwork-securitythreat-intelligence
sentrypeer/sentrypeerDistributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 jassics/security-study-plan
Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…
 openpcc/openpcc
An open-source framework for verifiably private AI inference
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 0xrlawrence/pribado
Zero-knowledge privacy platform for confidential API key management, encrypted vault, and secure chat. Built on Oasis Sapphire TEEs
 everywall/ladder
Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
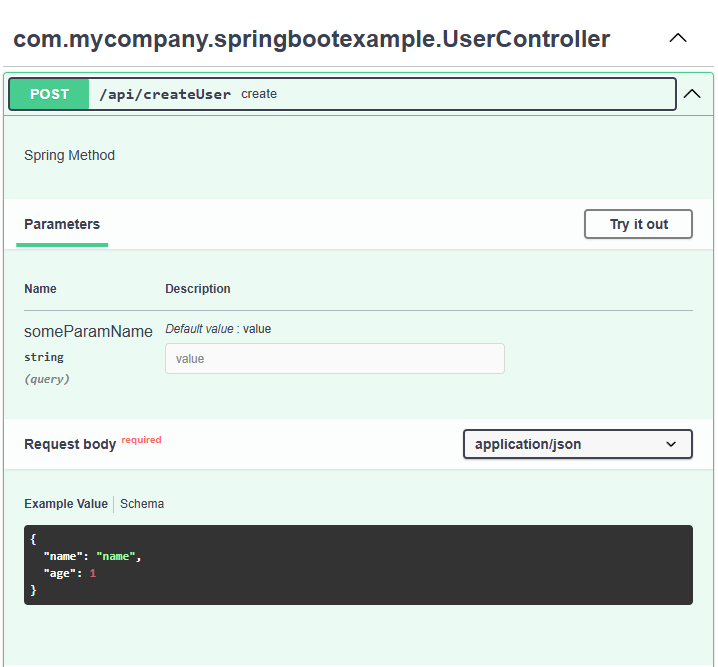 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
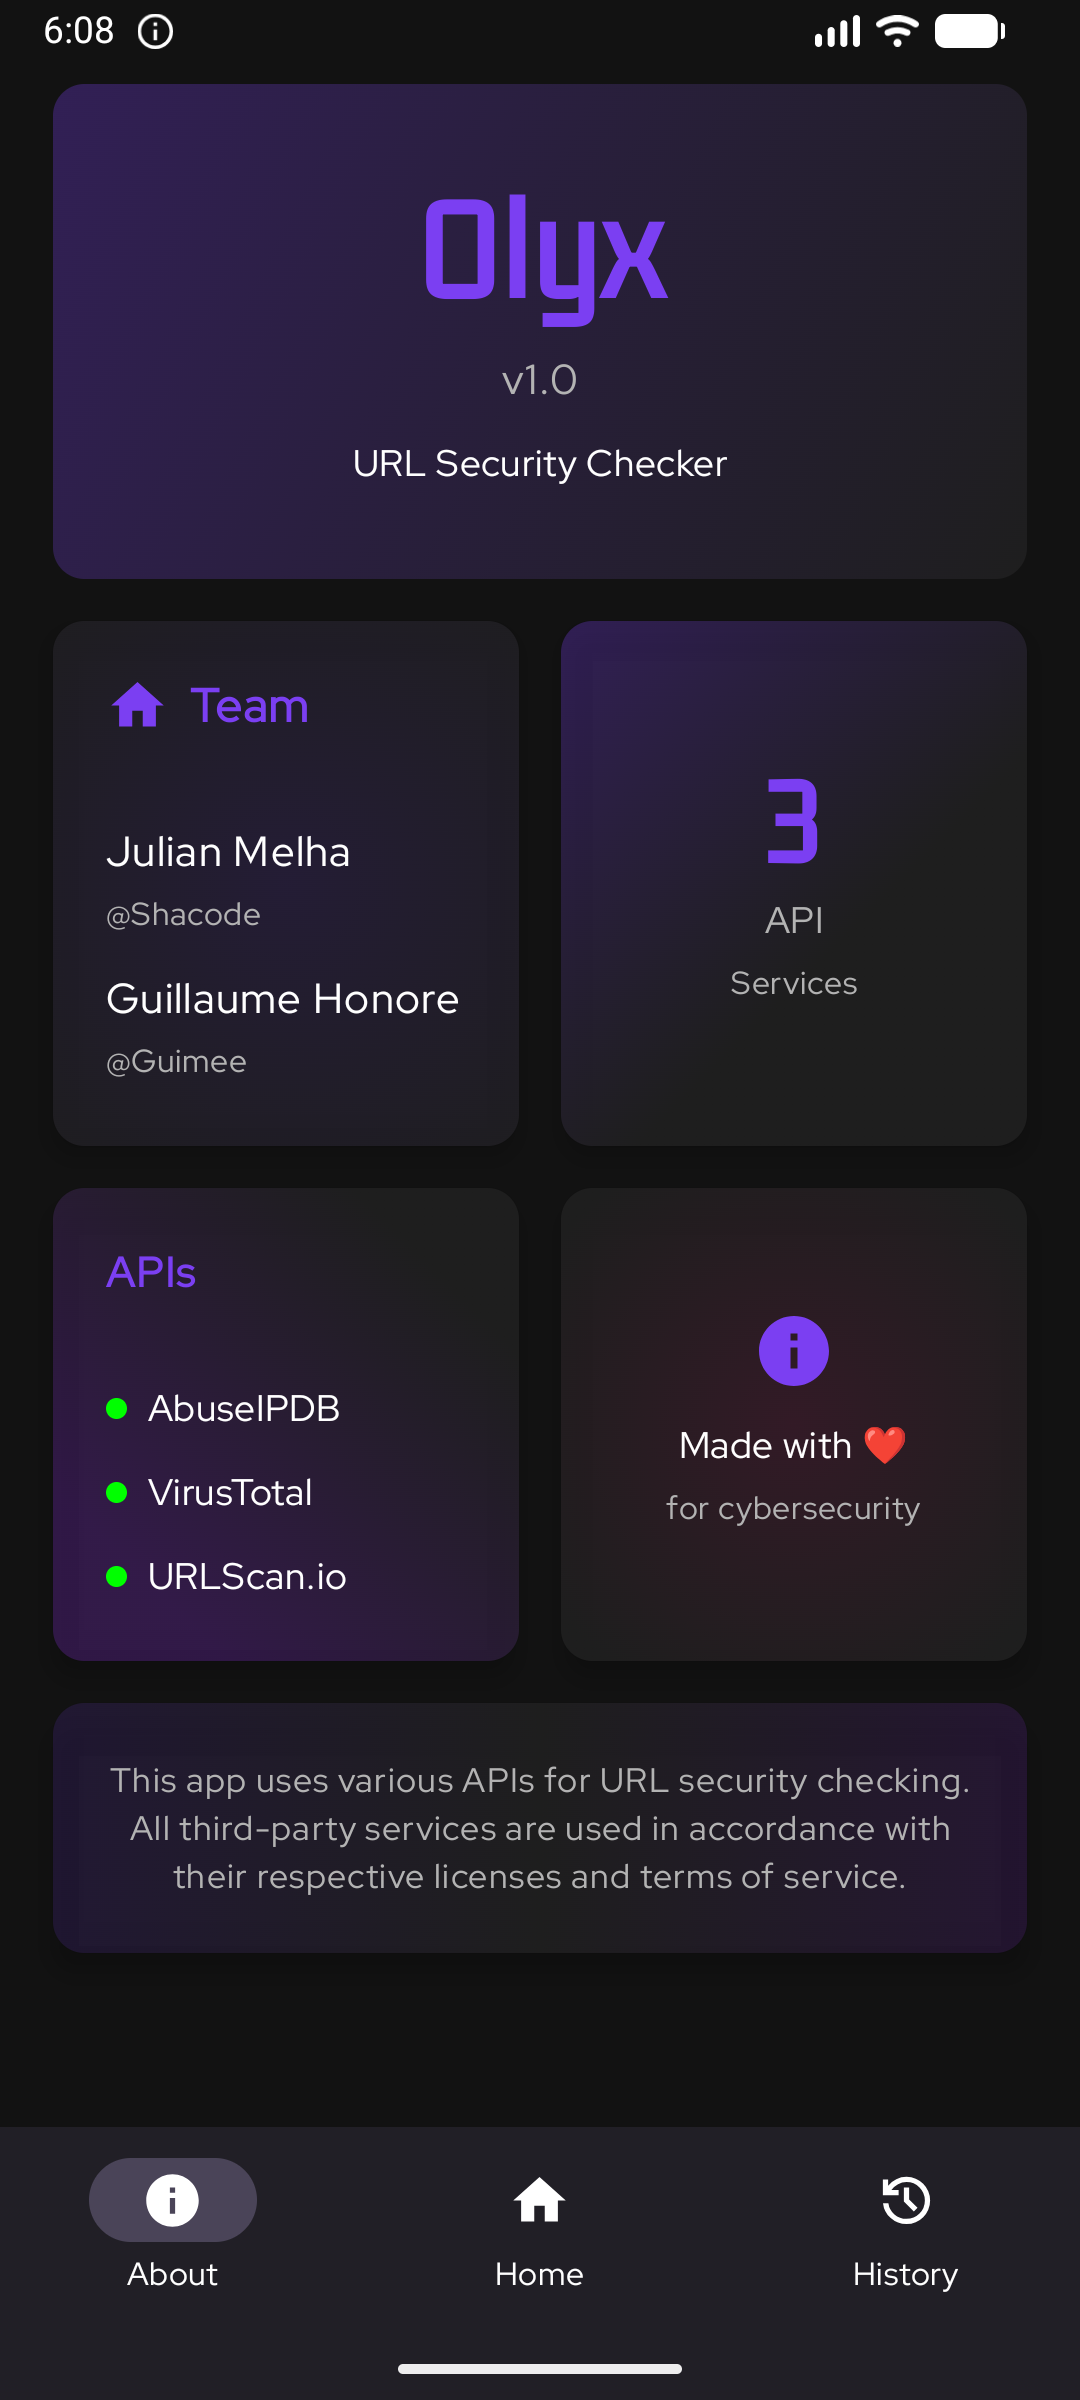
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.