
bluemonday
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
api-securitycode-analysisdefensive-tools+3
3.7k
microcosm-cc/bluemondaybluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 pingidentity/ldapsdk
UnboundID LDAP SDK for Java
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 shoucheng3/apache__sling-org-apache-sling-xss_cve-2016-5394_1-0-8
Java library providing XSS escaping and filtering services (XSSAPI, XSSFilter) to sanitize user-submitted content and prevent cross-site scripting…
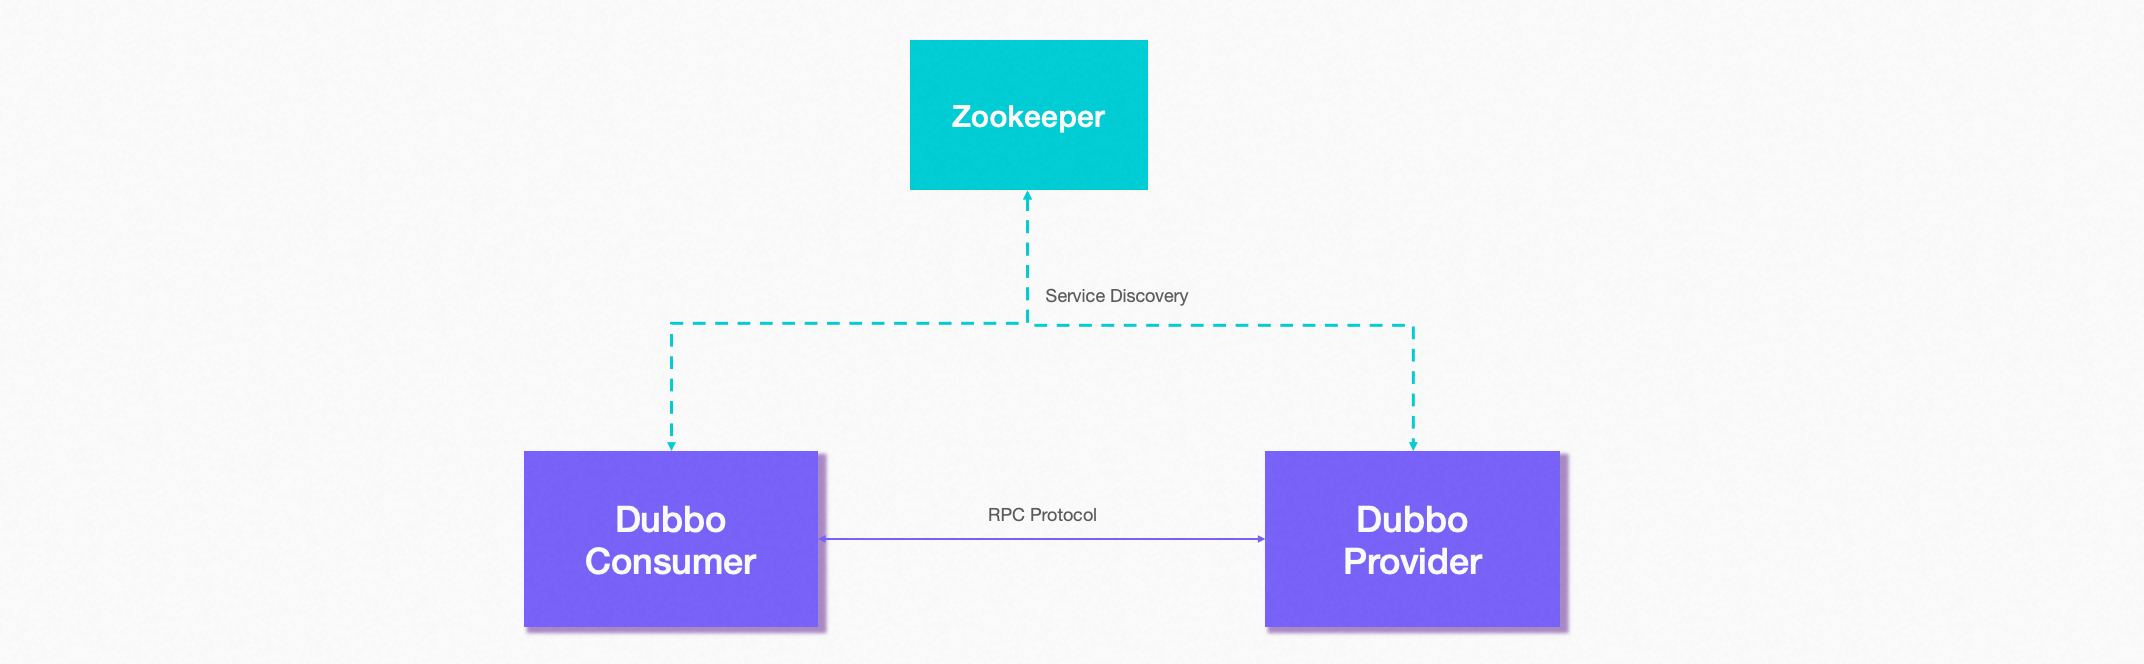 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 shoucheng3/fabric8io__kubernetes-client_cve-2021-4178_5-0-2
Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…
 shoucheng3/hapifhir__org_hl7_fhir_core_cve-2023-28465_5-6-1055
Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 shoucheng3/kubernetes-client__java_cve-2020-8570_client-java-parent-9_0_2_fixed
Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…
 shoucheng3/apache__camel_cve-2018-8041_2-20-3
Open source integration framework for defining routing and mediation rules via DSLs (Java, XML, YAML) to connect various systems consuming or…
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
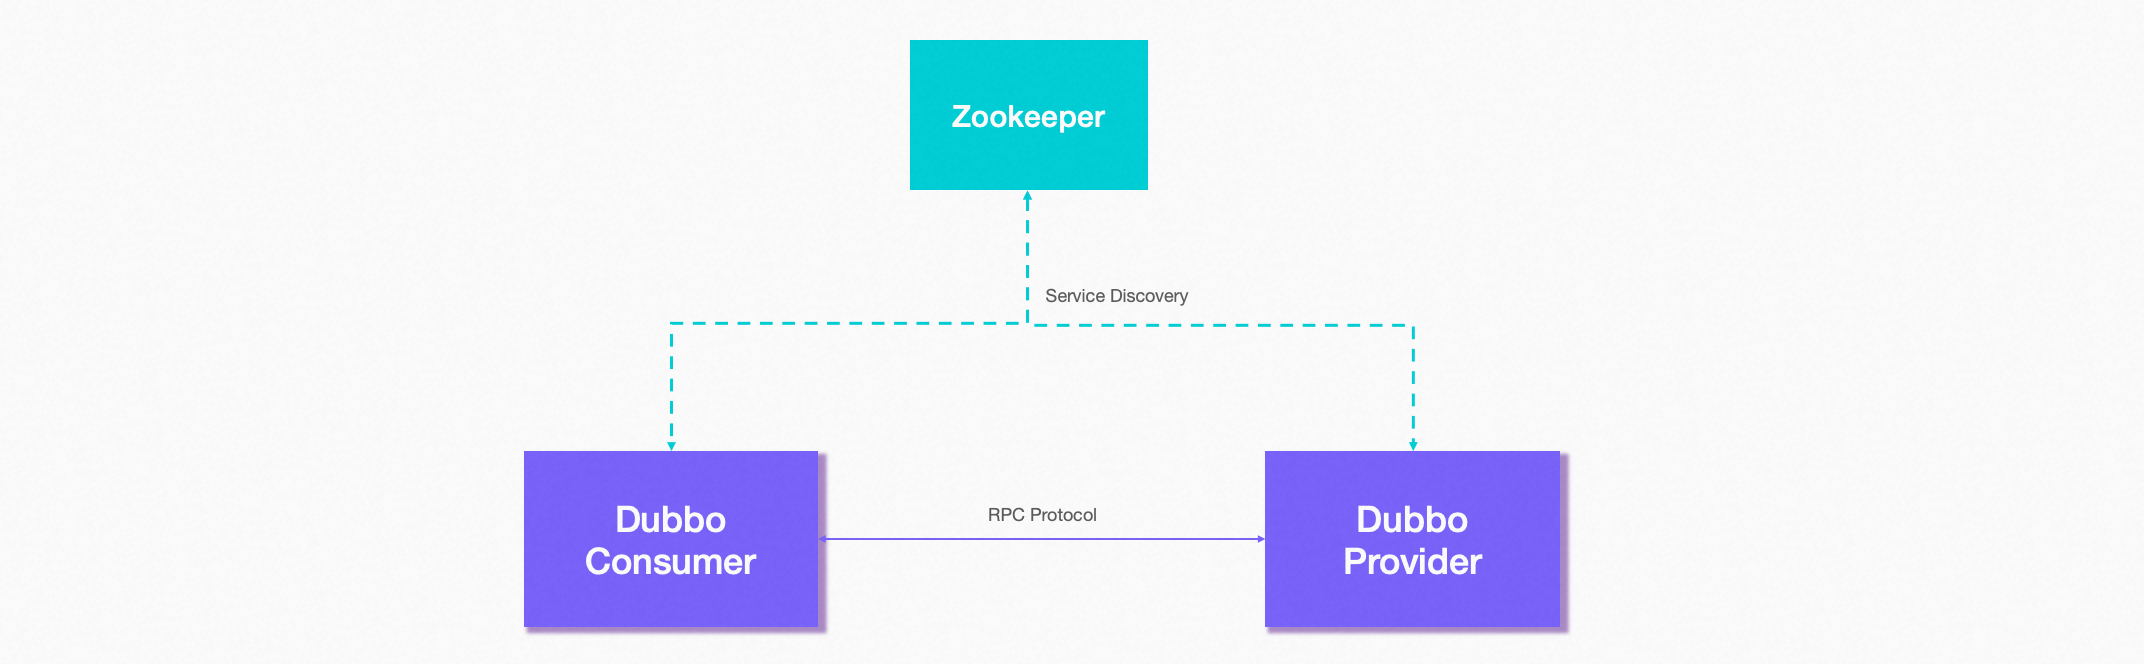 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.