
API-Security-Checklist
 shieldfy/api-security-checklist
Checklist of the most important security countermeasures when designing, testing, and releasing your API
api-securityauthentication-authorizationcurated-resources+4
23.3k
shieldfy/api-security-checklistChecklist of the most important security countermeasures when designing, testing, and releasing your API
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
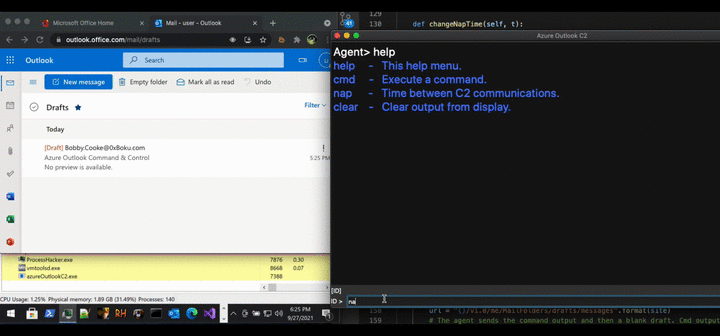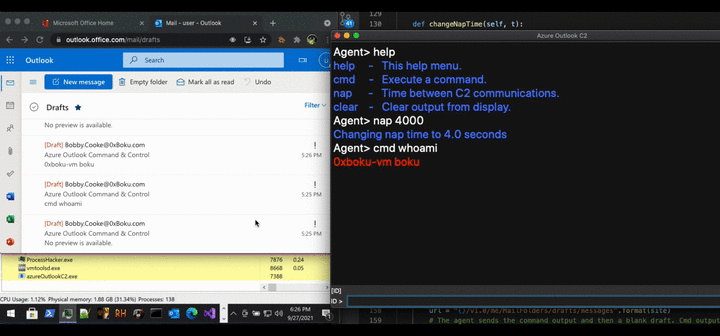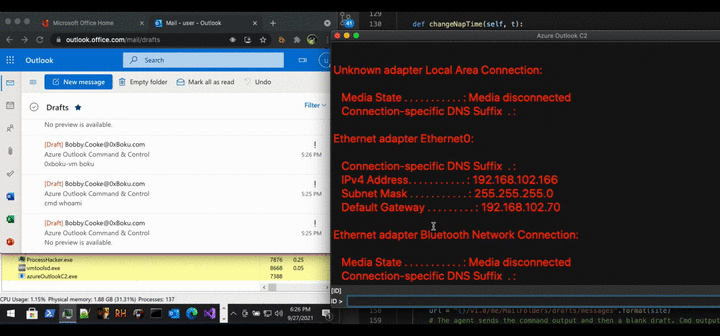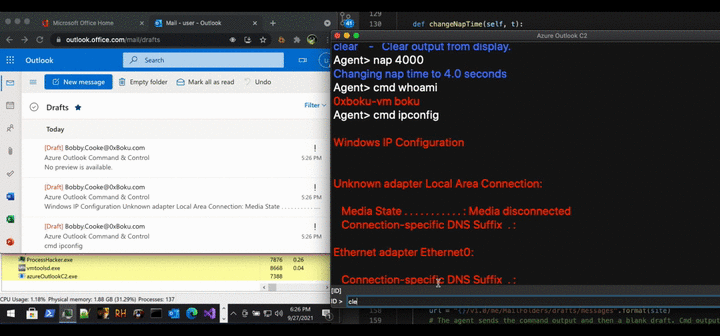 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 davidcarliez/cover
Keep private data, internal infrastructure and secrets out of cloud coding agents without breaking your workflow.
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 qruiqai/leakish
Browser privacy-leak detector — eight detection modules, risk scoring, and per-account history, all in your browser.
 cyberdudebivash/cyberdudebivash-servicenow-ai-agent-audit-script
This script audits ServiceNow AI Agents for vulnerabilities like CVE-2025-12420, governance gaps, and compliance risks. Powered by CYBERDUDEBIVASH –…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…