
CVE-2026-42154
 shadowbyte1/cve-2026-42154
Proof-of-concept exploit for CVE-2026-42154, a denial-of-service vulnerability in Prometheus Remote Read endpoint via crafted Snappy-compressed…
api-securitycloud-securityexploitation+1
shadowbyte1/cve-2026-42154Proof-of-concept exploit for CVE-2026-42154, a denial-of-service vulnerability in Prometheus Remote Read endpoint via crafted Snappy-compressed…
 ltidi2000/cve-2021-45232
Proof-of-concept exploit for CVE-2021-45232, an unauthorized access vulnerability in Apache APISIX Dashboard allowing export/import of admin…
 faccimatteo/cve-2022-4361
Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…
 novem13th/cve-2026-23745-via-graphql-demo
Proof-of-concept exploit for CVE-2026-23745 targeting GraphQL endpoints, demonstrating the vulnerability and potential impact for security testing…
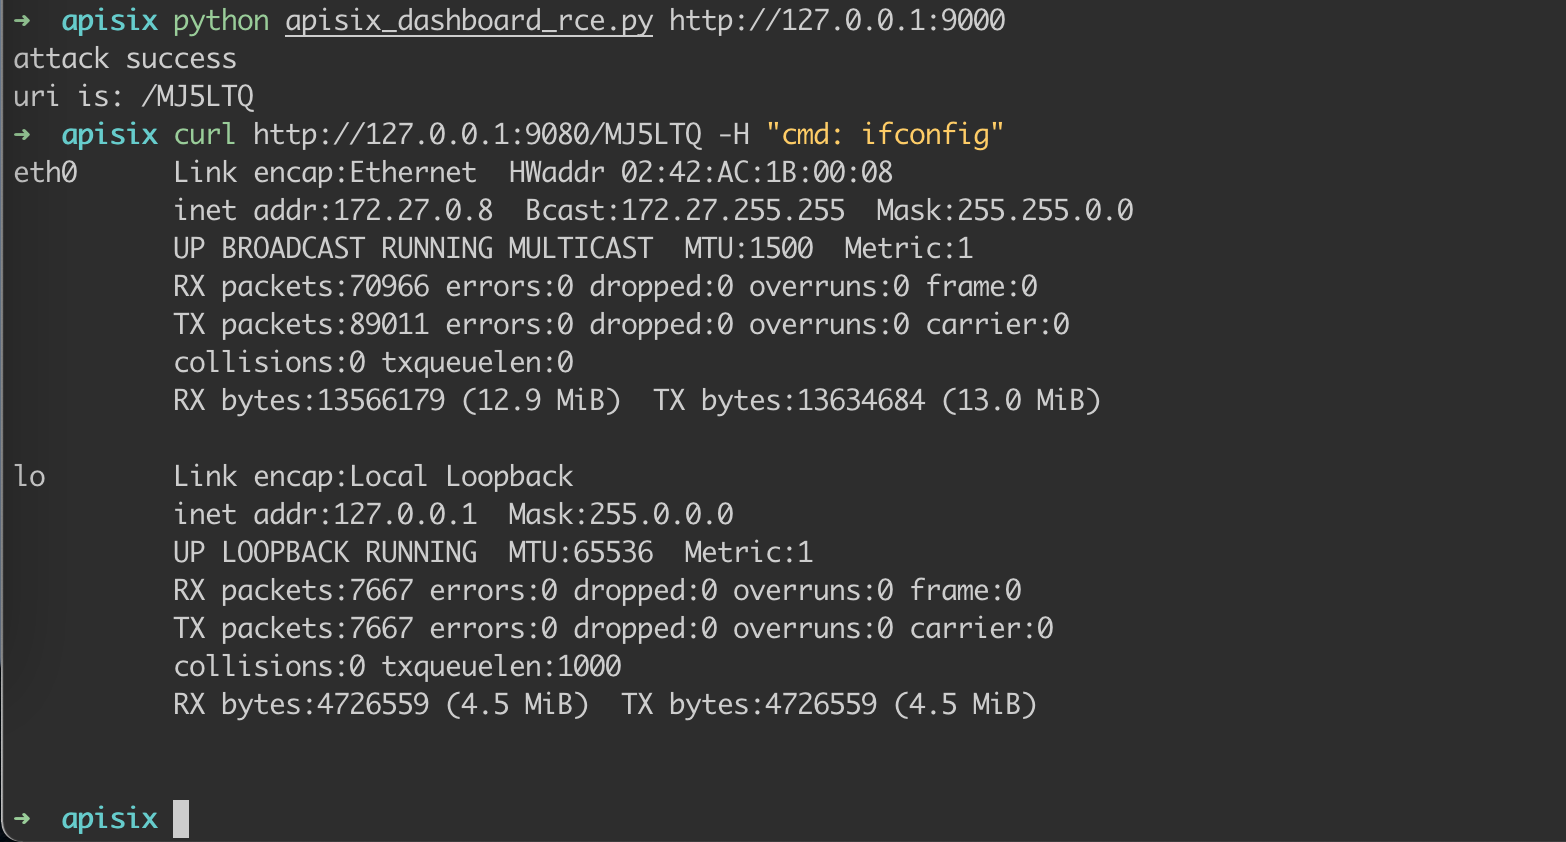 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
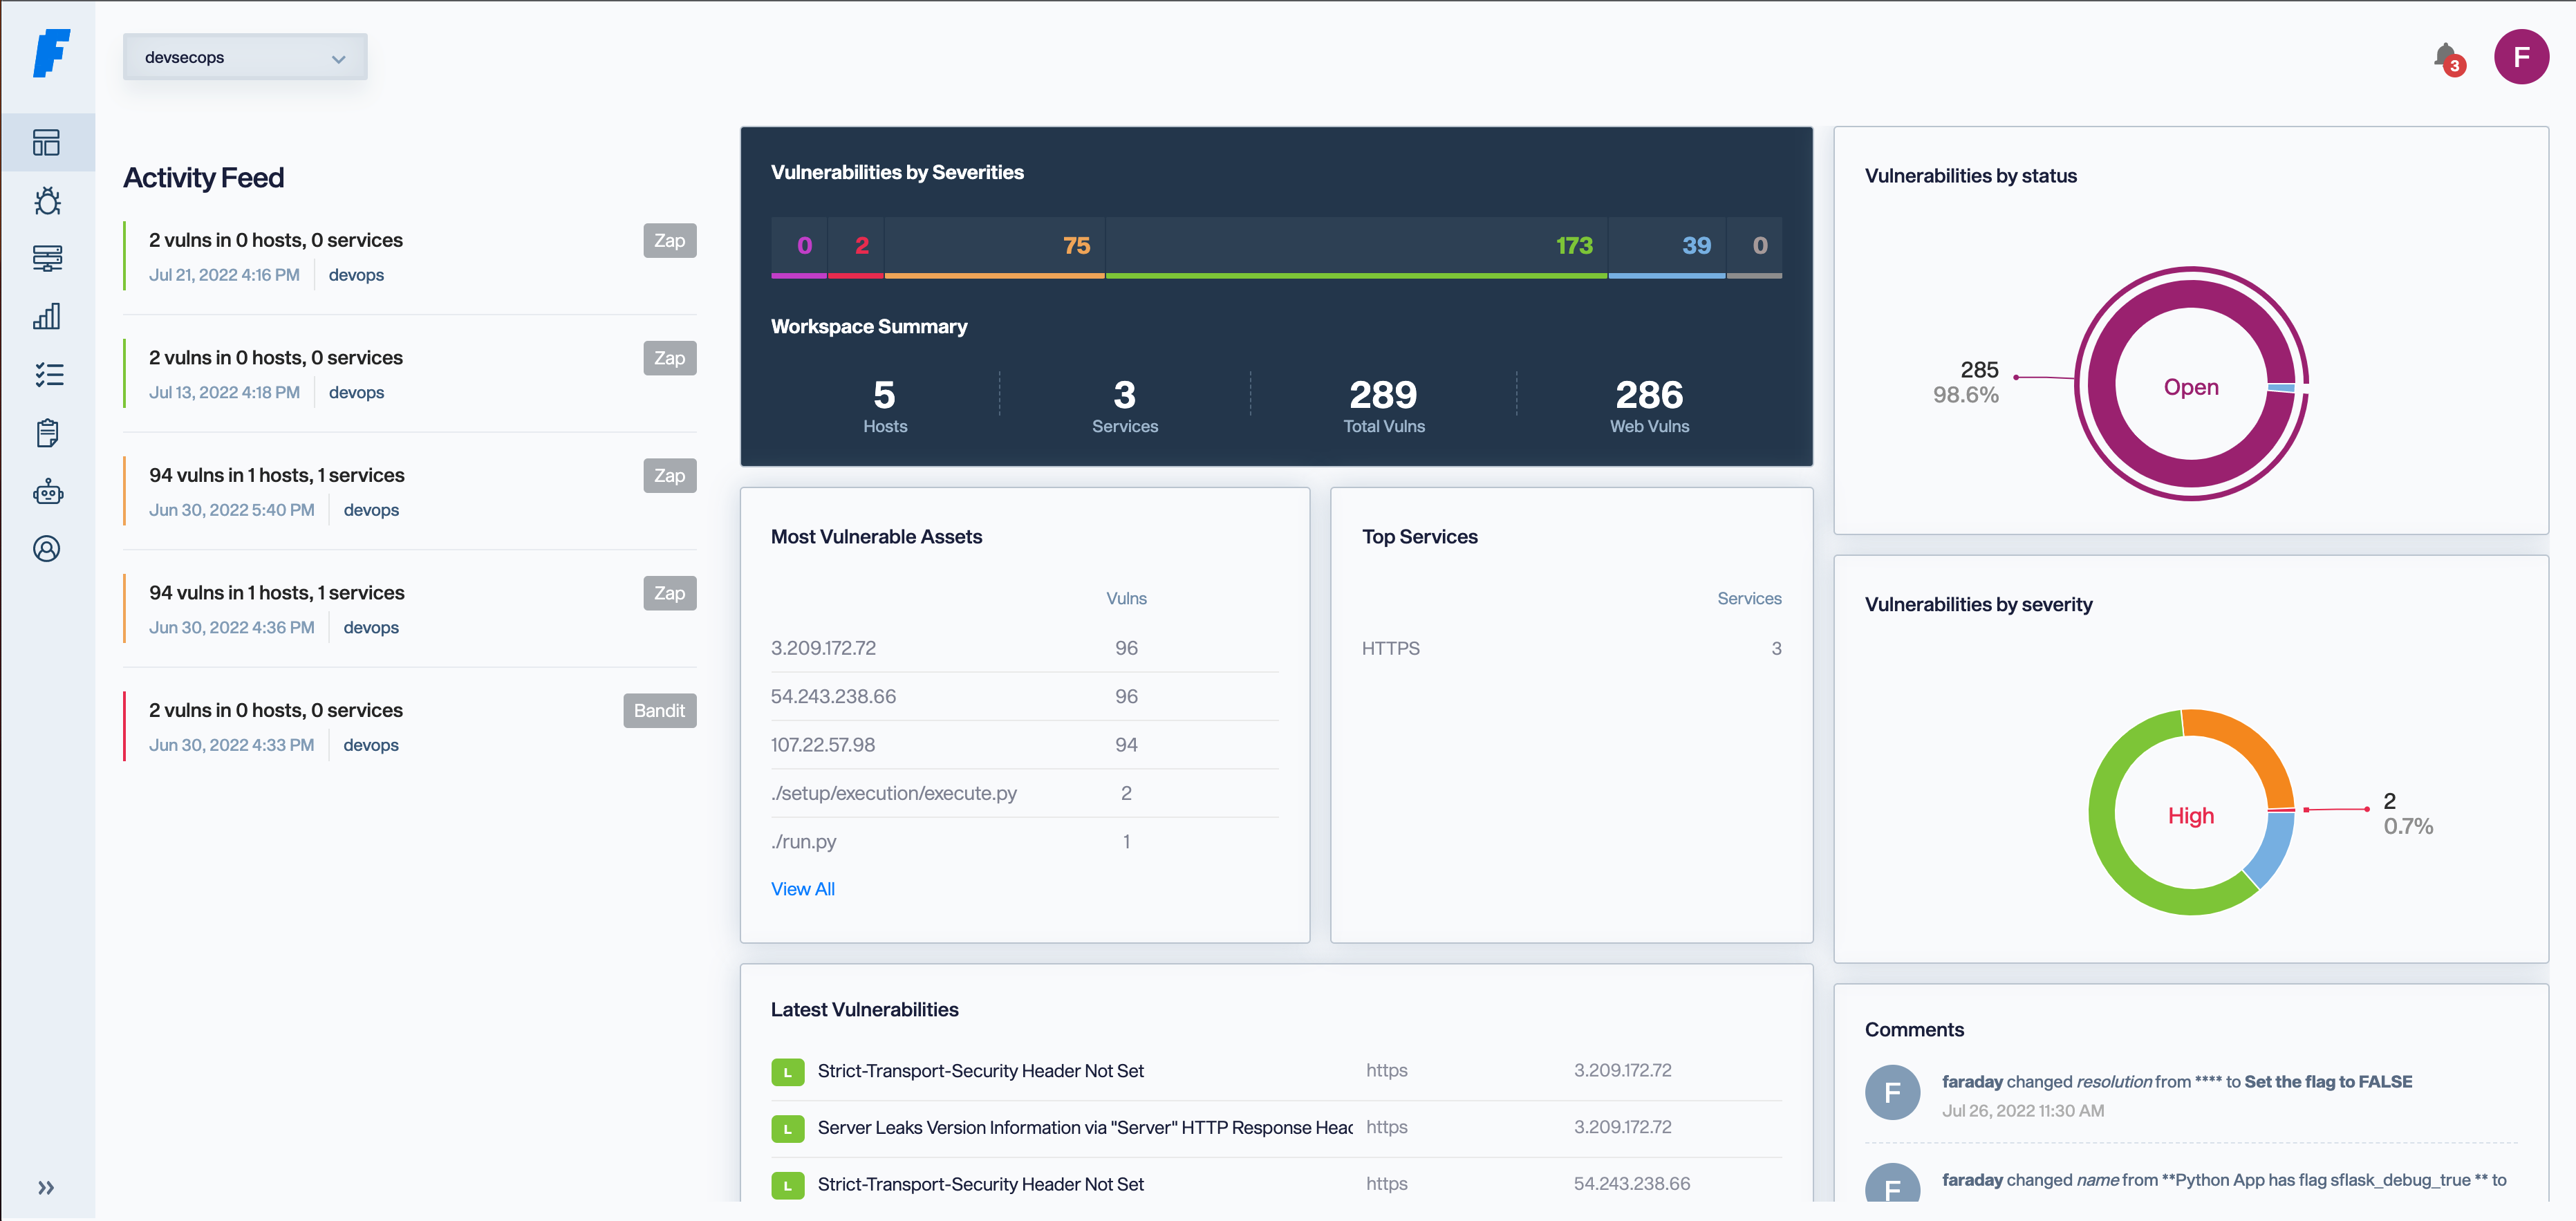 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 twinson333/cve-2026-33032-scanner
Non-destructive vulnerability scanner for Nginx-UI MCP Endpoint Authentication Bypass (CVE-2026-33032)
 envincion1991-cmyk/cve-2026-51954
Vulnerability Research
 sam00/poc-cve-2026-32621-apollo-federation-xss-vulnerability
PoC exploit for CVE-2026-32621 demonstrating Apollo Federation deepMerge prototype pollution via crafted GraphQL aliases, with patched-version tests.
 hunt-benito/the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass
Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…
 oscerd/cve-2026-46726
Reproducer for CVE-2026-46726: Apache Camel camel-vertx-websocket unfiltered inbound header injection enabling SSRF and secret disclosure via…
 hereticl1nk/eits-portal-exploit-cve-2026-31367-poc
PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…
 wa6n3r/cve-2026-35616
Exploit script for CVE-2026-35616 that bypasses certificate chain verification in Fortinet API by discovering valid CNs, generating a forged client…
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…