Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
215 results
CVE-2026-0915-json-Patch.-V2.0 preview

CVE-2026-0915-json-Patch.-V2.0

GitHubterra-nova83/cve-2026-0915-json-patch.-v2.0

Provides a security patch for CVE-2026-0915, adding strict JSON schema validation, input sanitization, and rate limiting to prevent injection and DoS…

api-securitydevsecopsvulnerability-analysis+1
8 months ago
CVE-2026-67598 preview

CVE-2026-67598

GitHubilhomjonr/cve-2026-67598

CVE-2026-67598 — Emlog Pro: disabled TLS certificate validation in AI assistant (MITM → API-key theft). CWE-295, CVSS 9.1. Reported by @IlhomjonR.

ai-securityapi-securitycode-analysis+3
2 months ago
CVE-2019-11287 preview

CVE-2019-11287

GitHubmbadanoiu/cve-2019-11287

CVE-2019-11287: DoS via Heap Overflow in RabbitMQ Web Management Plugin

api-securityexploitationvulnerability-analysis+1
1 year ago
matchlock preview

matchlock

GitHubjingkaihe/matchlock

Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…

ai-securityapi-securitycloud-security+5
6493 months ago
CVE-2024-57972 preview

CVE-2024-57972

GitHubtania-silva/cve-2024-57972

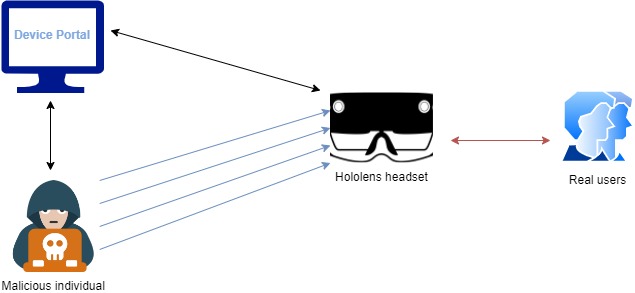
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.

api-securityexploitationhardware-iot-security+2
1 year ago
quarantyne preview
Archived

quarantyne

GitHubquarantyne/quarantyne

Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails

anti-botapi-securityauthentication+3
1234 years ago
CVE-2026-19478-PoC preview

CVE-2026-19478-PoC

GitHubdavkharrr/cve-2026-19478-poc

Proof-of-concept exploit for unauthenticated remote code injection in GitLab's GraphQL API, using crafted queries to modify or delete public projects…

api-securityexploitationinformation-gathering+3
112 months ago
leakish preview

leakish

GitHubqruiqai/leakish

Browser privacy-leak detector — eight detection modules, risk scoring, and per-account history, all in your browser.

anomaly-detectionapi-securitydns-analysis+7
84 months ago
gitea-user-keys-idor preview

gitea-user-keys-idor

GitHubabraxas/gitea-user-keys-idor

Proof-of-concept and lab for a Gitea IDOR (CWE-639) in GET /api/v1/user/keys/{id}, letting an authenticated read:user token enumerate other users'…

api-securityexploitationinformation-gathering+4
21 days ago
CVE-2026-13736 preview

CVE-2026-13736

GitHubminhhk68/cve-2026-13736

Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…

api-securityexploitationinformation-gathering+3
2 months ago
CVE-2026-15583 preview

CVE-2026-15583

GitHubabraxas/cve-2026-15583

Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…

api-securitydata-exfiltrationexploitation+6
21 days ago
CVE-2024-46635 preview

CVE-2024-46635

GitHubh1thub/cve-2024-46635

Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…

api-securityinformation-gatheringmisconfiguration+3
12 years ago
CVE-2026-27739-POC preview

CVE-2026-27739-POC

GitHubmr-redoo7/cve-2026-27739-poc

Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…

api-securityexploitationinformation-gathering+4
6 months ago
CVE-2025-51869 preview

CVE-2025-51869

GitHubsecsys-fdu/cve-2025-51869

Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Liner's chat component, allowing attackers to tamper with other users'…

api-securityinformation-gatheringpenetration-testing+3
11 year ago
CVE-2025-54554 preview

CVE-2025-54554

GitHubaman-parmar/cve-2025-54554

CVE-2025-54554 – Unauthenticated Access in tiaudit REST API leading to Sensitive Information Disclosure

api-securityinformation-gatheringmisconfiguration+2
1 year ago
CVE-2026-89012 preview

CVE-2026-89012

GitHubfaceless0x7/cve-2026-89012

Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

api-securitydata-exfiltrationexploitation+6
61 month ago
CVE-2026-105030-poc preview

CVE-2026-105030-poc

GitHubasvorg/cve-2026-105030-poc

A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API

api-securityexploitationinformation-gathering+4
25 days ago
CVE-2026-58231 preview

CVE-2026-58231

GitHubwildandeveloper/cve-2026-58231

Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…

api-securityauthenticationinformation-gathering+4
1 month ago
Previous12…12Next