

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 oscerd/cve-2026-64640
Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 horkimhab/cve-wazuh
Enrolled agent can smuggle arbitrary OpenSearch _bulk operations via DataValue.index. GHSA-ff9g-85jq-r3g3. Draft

 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
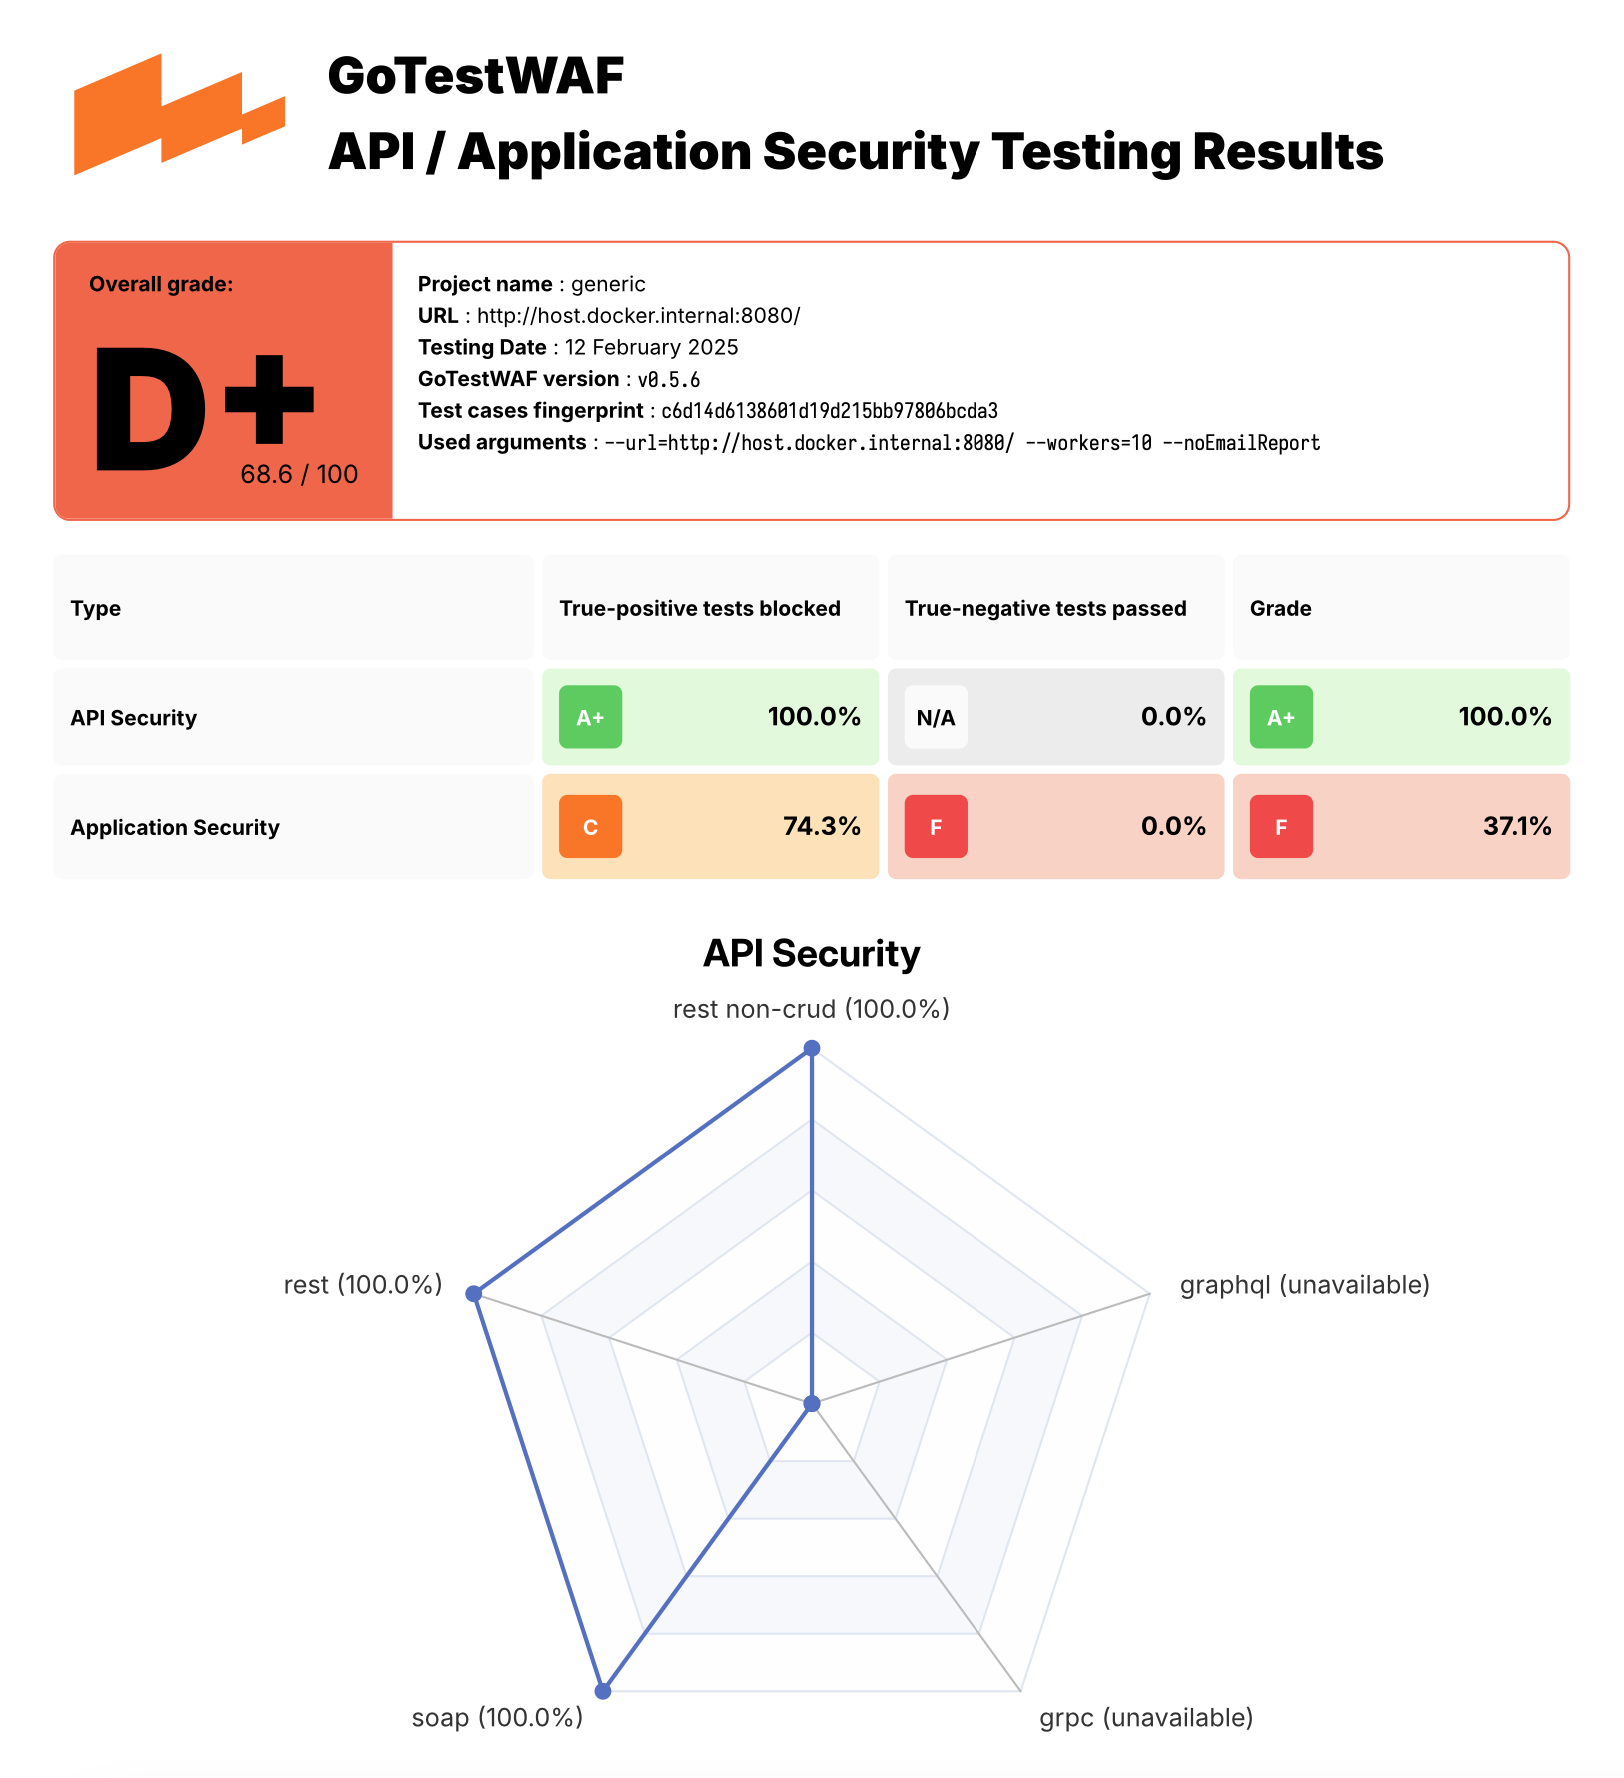 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 armourbird/csf
ArmourBird CSF - Container Security Framework
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 qruiqai/leakish
Browser privacy-leak detector — eight detection modules, risk scoring, and per-account history, all in your browser.
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…

 kavryxdev-group/sandboxed-untrusted-code-execution-runner
Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.
 hunt-benito/the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass
Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…