
zte-smartlife-app-pwned
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
android-securityapi-securitycryptography+7
minanagehsalalma/zte-smartlife-app-pwnedZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…
 twinson333/cve-2026-33032-scanner
Non-destructive vulnerability scanner for Nginx-UI MCP Endpoint Authentication Bypass (CVE-2026-33032)
 sam00/poc-cve-2026-32621-apollo-federation-xss-vulnerability
PoC exploit for CVE-2026-32621 demonstrating Apollo Federation deepMerge prototype pollution via crafted GraphQL aliases, with patched-version tests.
 bsdrip/cve-2026-40179-poc
Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
 ilhomjonr/cve-2026-67598
CVE-2026-67598 — Emlog Pro: disabled TLS certificate validation in AI assistant (MITM → API-key theft). CWE-295, CVSS 9.1. Reported by @IlhomjonR.
 squeeze440/inference-gateway-poc
PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
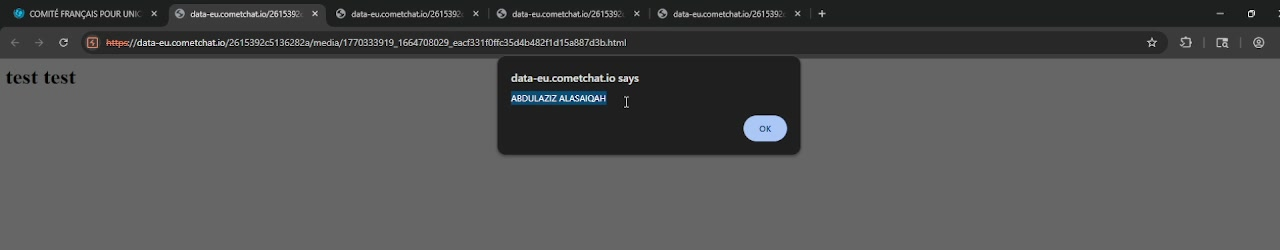 defineid/wildfire
CVE-2026-39154, Stored XSS in CometChat JS SDK
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…