
CVE-2025-51869
 secsys-fdu/cve-2025-51869
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Liner's chat component, allowing attackers to tamper with other users'…
api-securityinformation-gatheringpenetration-testing+3
1
secsys-fdu/cve-2025-51869Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Liner's chat component, allowing attackers to tamper with other users'…
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.
 0xrlawrence/pribado
Zero-knowledge privacy platform for confidential API key management, encrypted vault, and secure chat. Built on Oasis Sapphire TEEs
 ory/hydra
OpenID Certified OAuth 2.0 and OpenID Connect provider for token issuance, client management, JWKS, and login/consent flow orchestration via headless…
 ory/kratos
API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 ory/talos
Scalable API key server for issuing, verifying, and revoking credentials with token derivation for fine-grained capability tokens. Supports…
 securelayer7/promptpurify
Prompt-injection guardrail for LLM applications. Compact model that outperforms larger open-source guards. No regex, no signatures. Demo:…
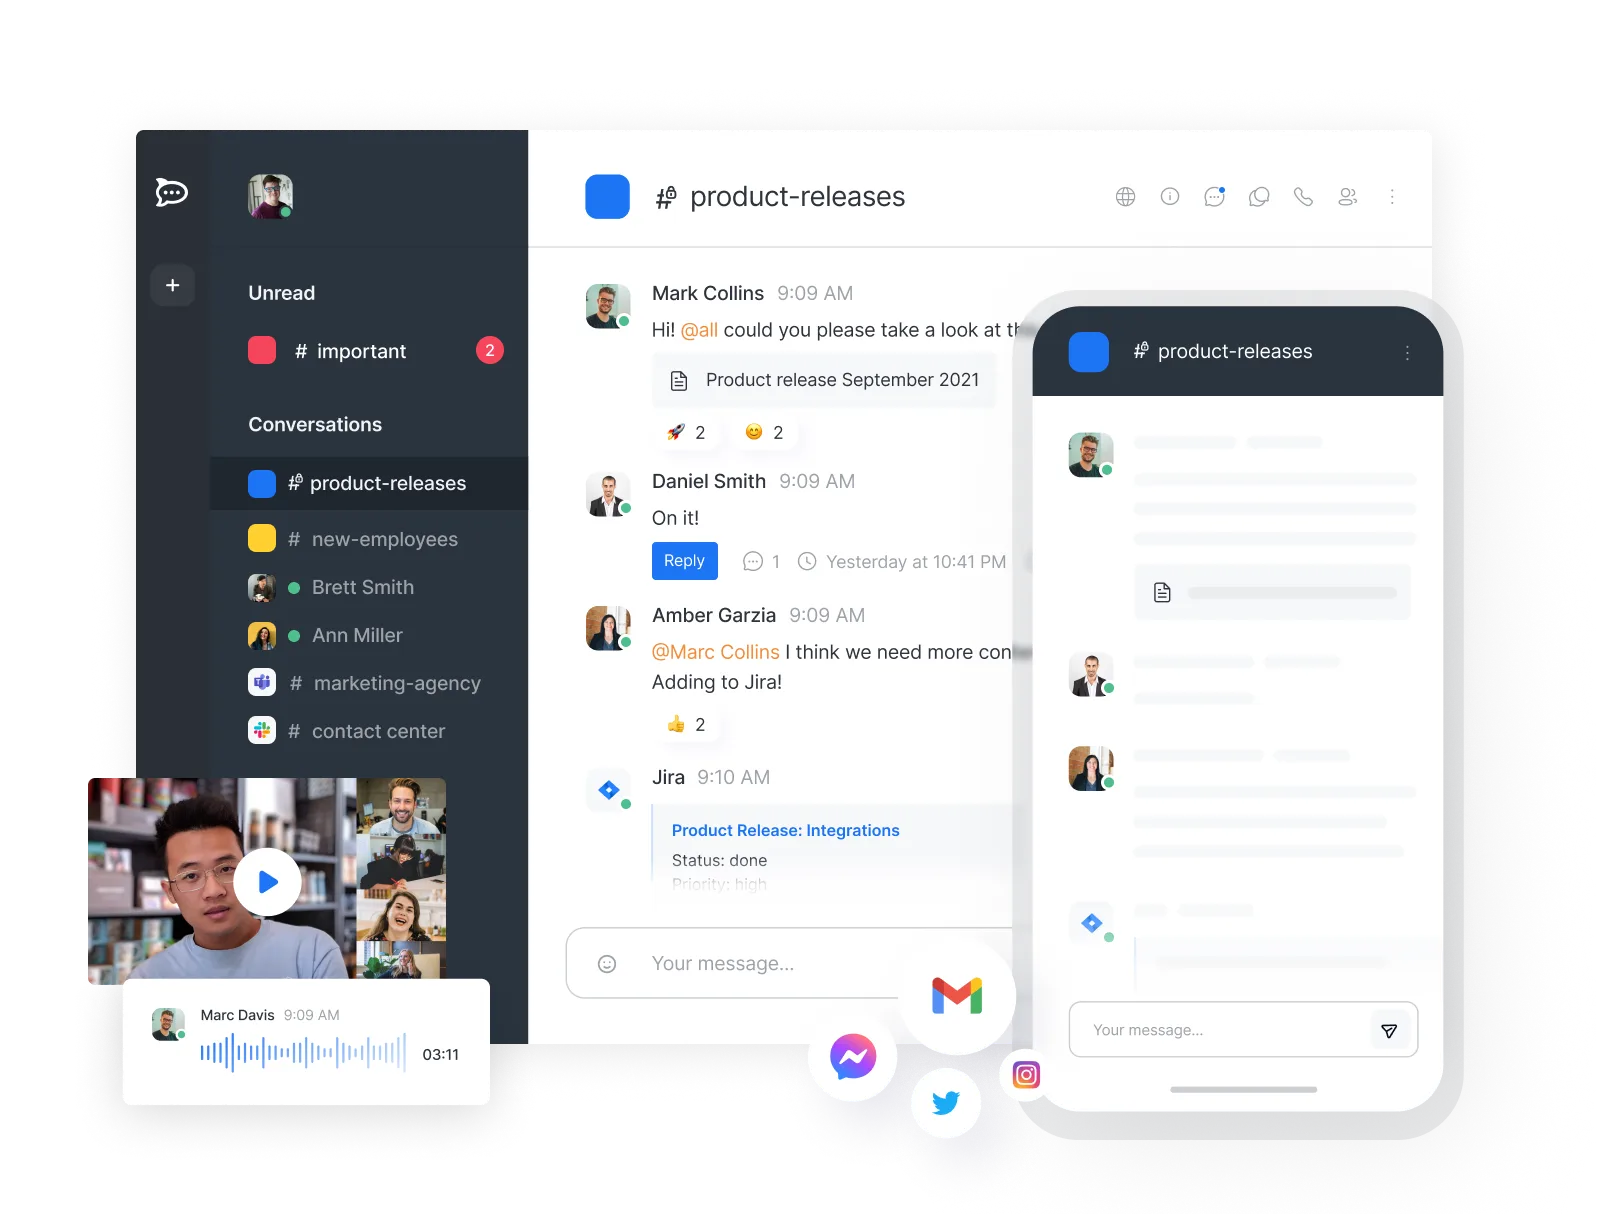 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations