
CVE-2025-56219
 saykino/cve-2025-56219
Detailed advisory for CVE-2025-56219, a rate-limiting flaw in Ascertia SigningHub's Add User API, enabling automated user creation and denial of…
api-securitycurated-resourceseducation+2
saykino/cve-2025-56219Detailed advisory for CVE-2025-56219, a rate-limiting flaw in Ascertia SigningHub's Add User API, enabling automated user creation and denial of…
 owasp/devsecopsguideline
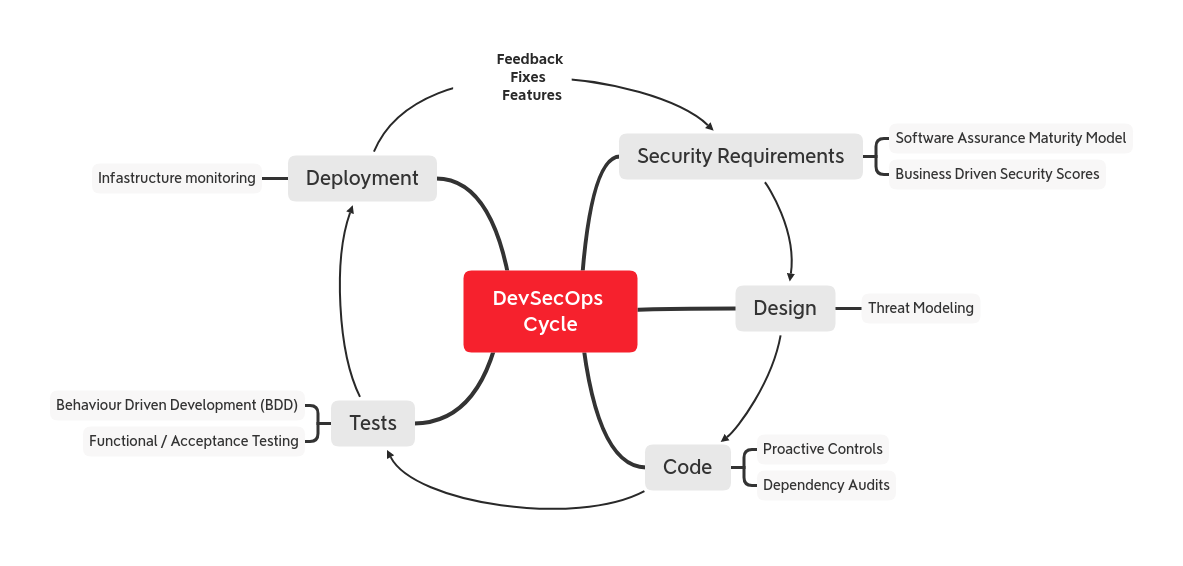
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 ustayready/fireprox
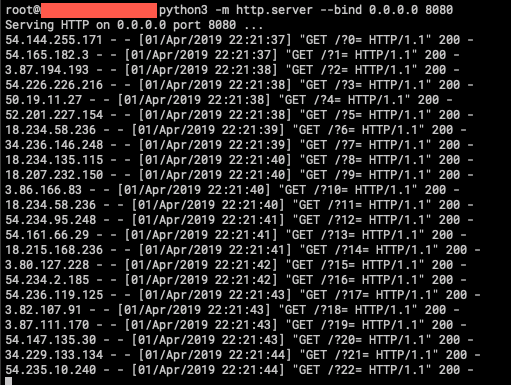
AWS API Gateway management tool for creating on the fly HTTP pass-through proxies for unique IP rotation
 ch4n3-yoon/cve-2025-62727-demo
Proof of concept of CVE-2025-62727 that can cause denial-of-service in FastAPI (based Starlette <= 0.48.0)
 m4xsec/apache-apisix-cve-2022-24112
Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
 saykino/cve-2025-56223
Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
 karlemilnikka/cve-2024-1208-and-cve-2024-1210
Detailed disclosure of CVE-2024-1208 and CVE-2024-1210: sensitive information exposure via REST API in LearnDash WordPress plugin, allowing…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
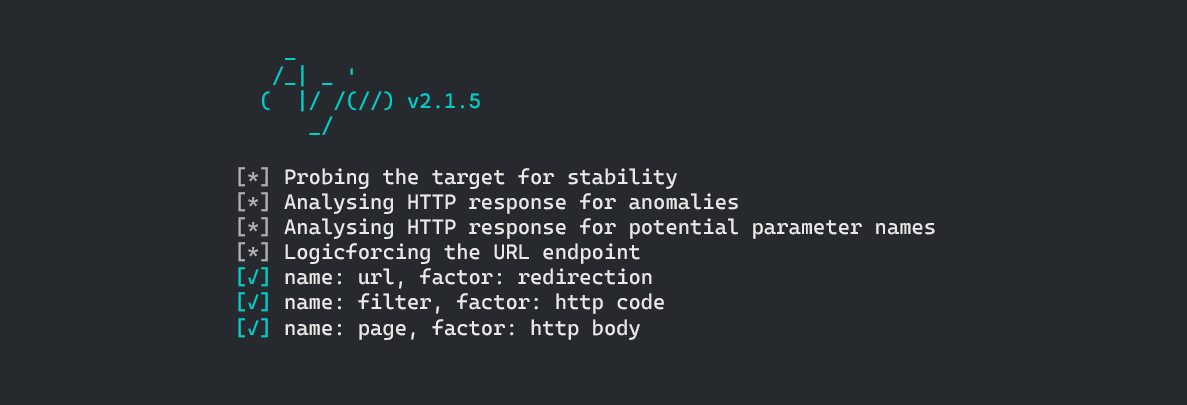 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
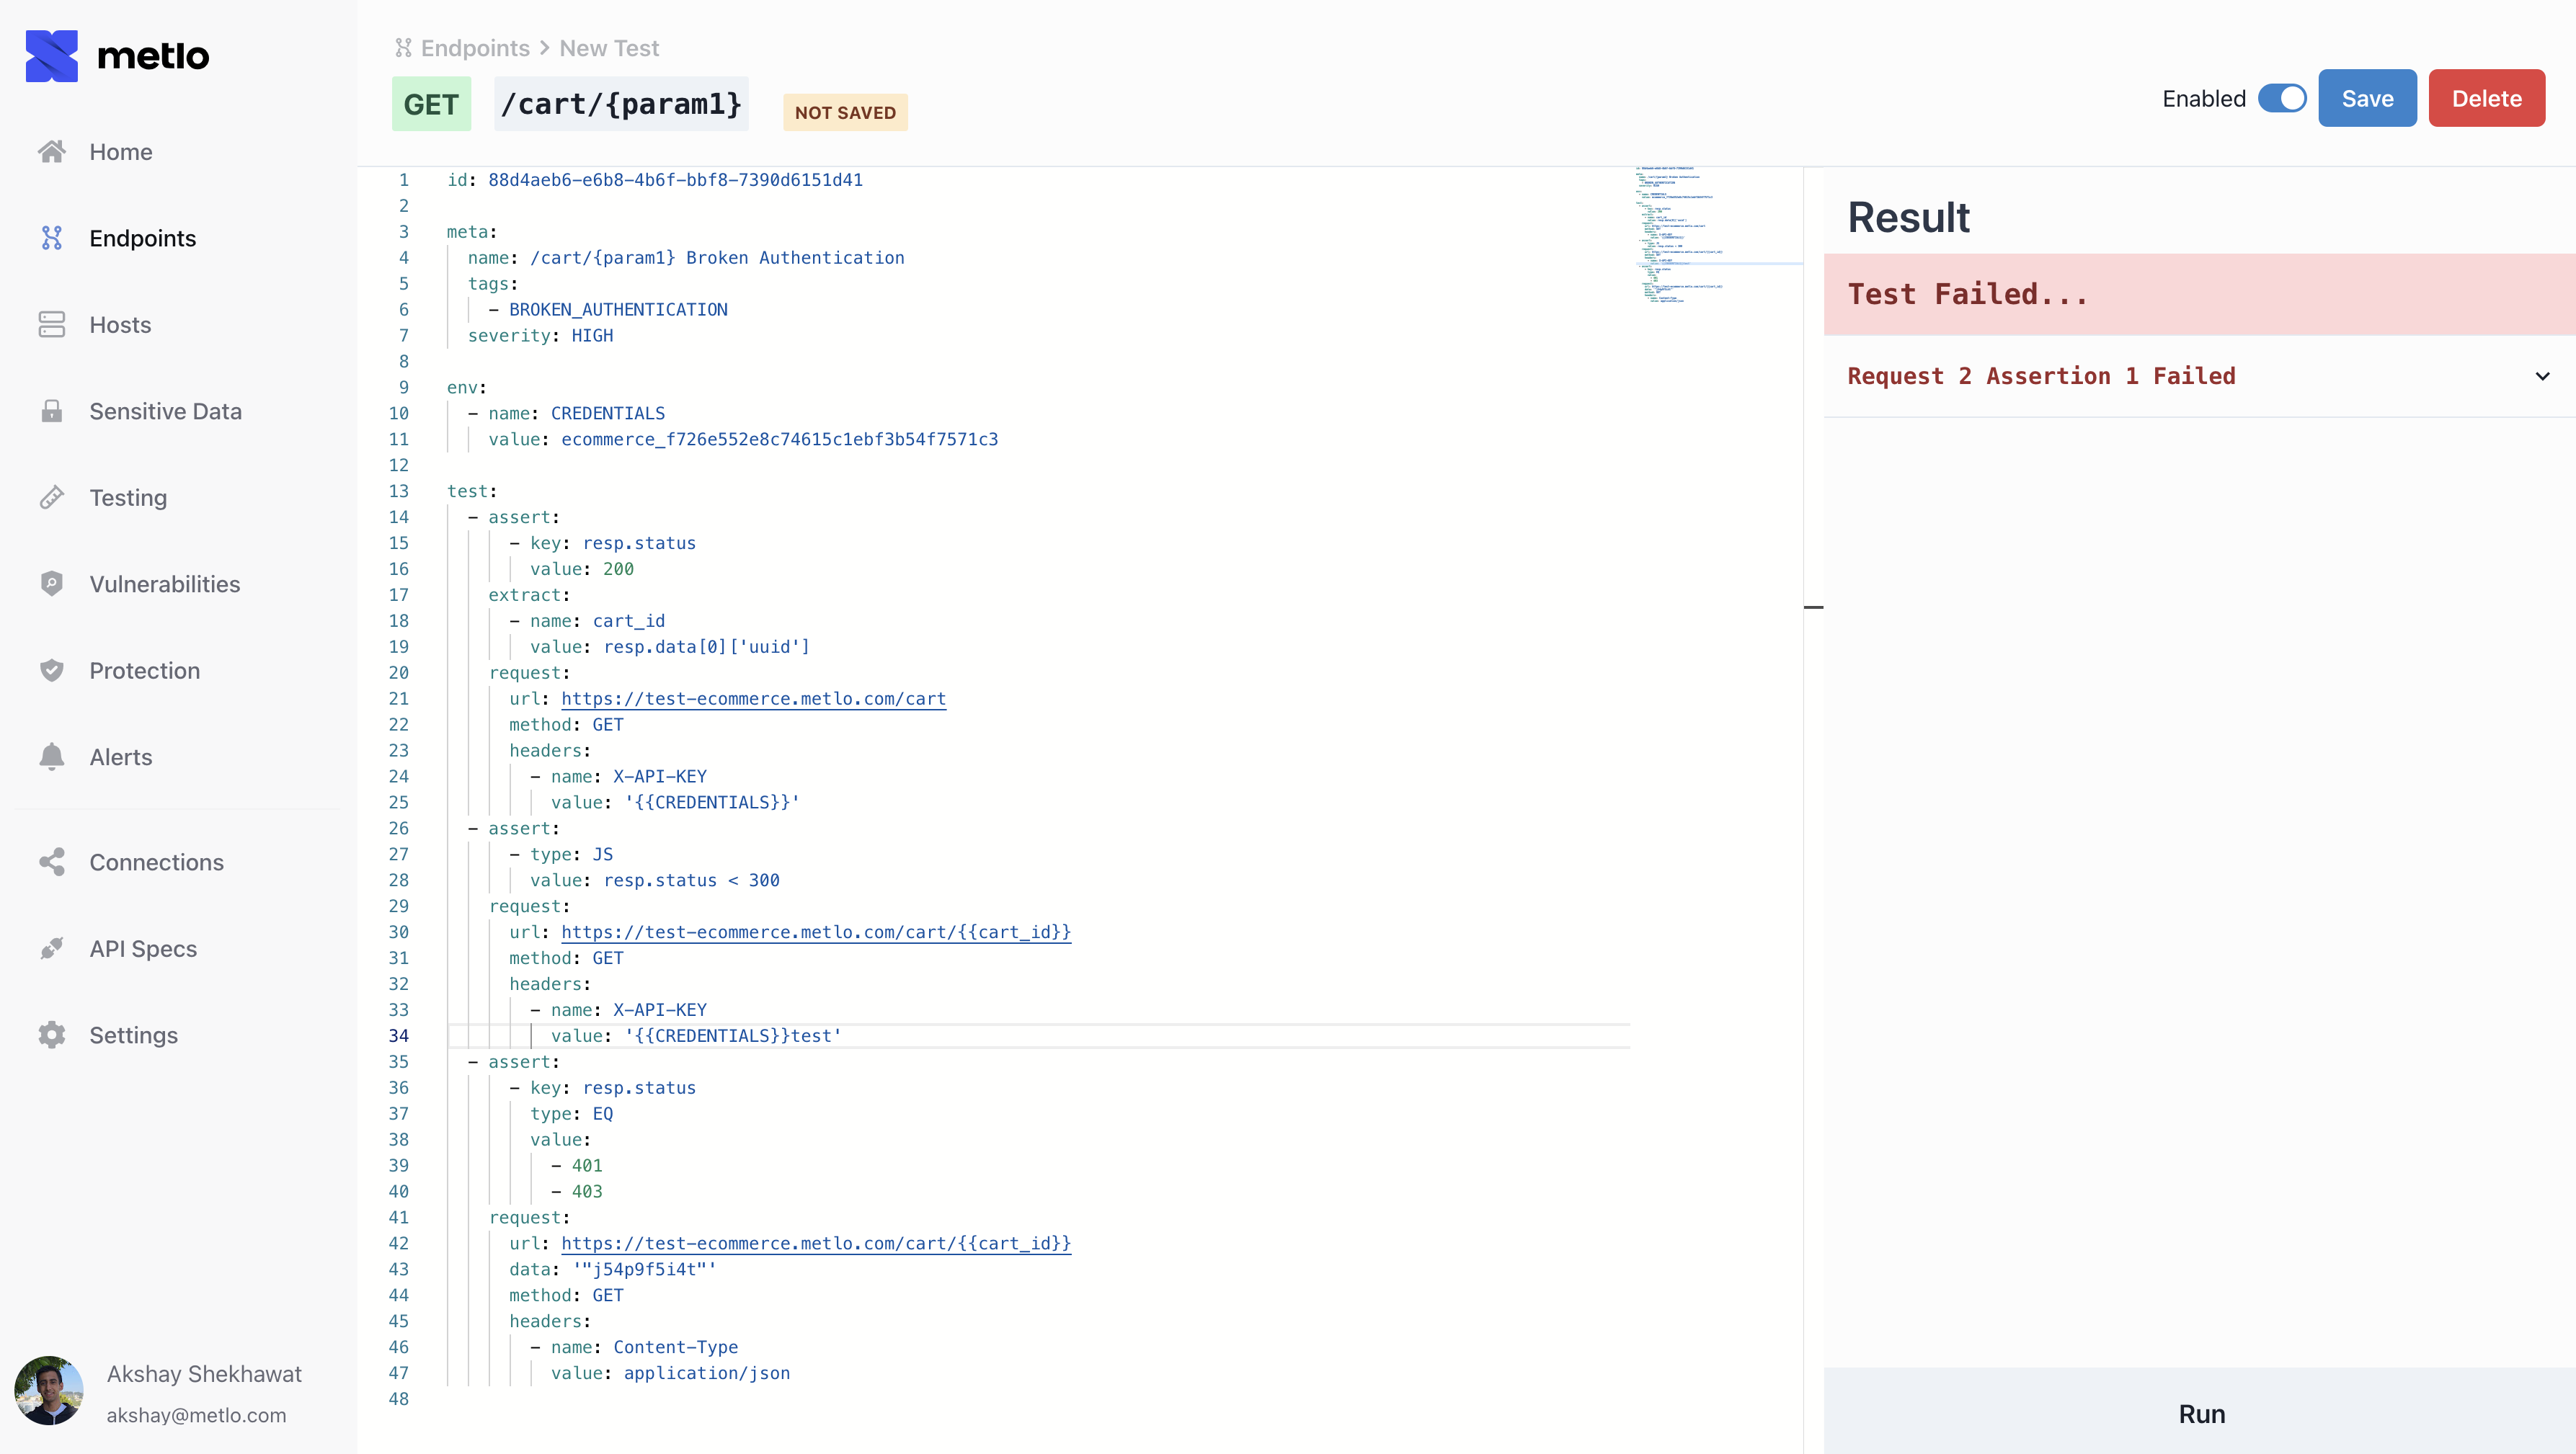 metlo-labs/metlo
Metlo is an open-source API security platform.
 sentrypeer/sentrypeer
Distributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
 commonguy25/authproof-sdk
Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.
 george0papasotiriou/cve-2026-21020-protobuf-message-parsing-polymorphic-deserialization-vulnerability
PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…