
CVE-2018-25031
 afine-com/cve-2018-25031
.json and .yaml files used to exploit CVE-2018-25031
api-securityexploitationphishing-tools+3
afine-com/cve-2018-25031.json and .yaml files used to exploit CVE-2018-25031
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 nicholasaleks/graphql-threat-matrix
GraphQL threat framework used by security professionals to research security gaps in GraphQL implementations
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
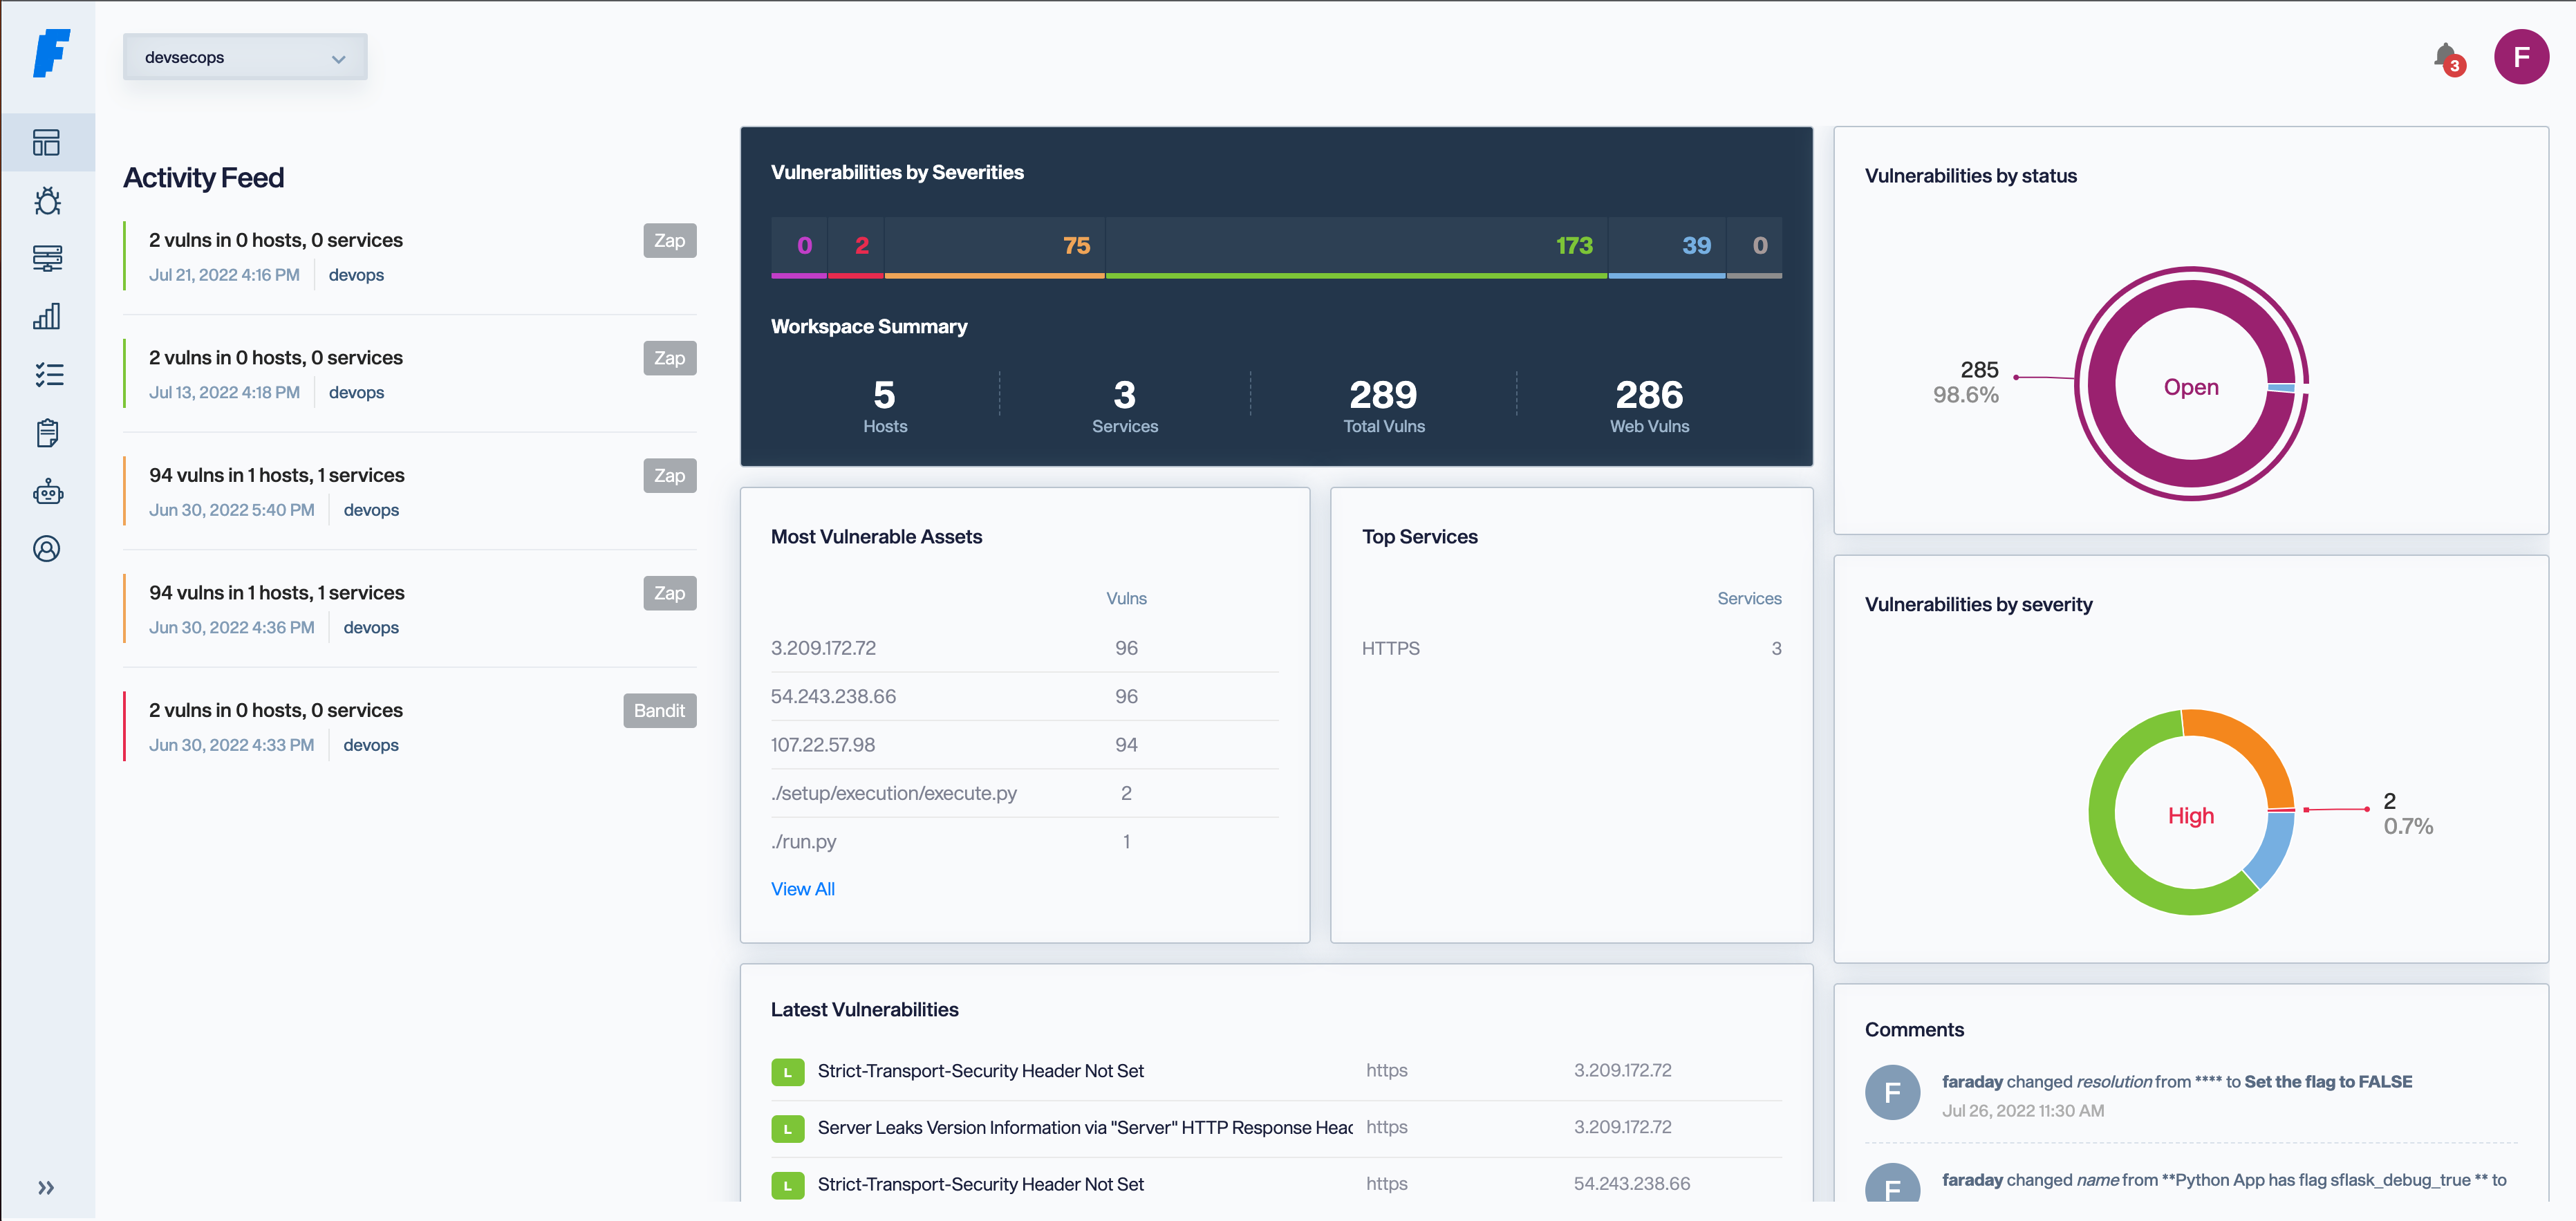 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 shoucheng3/hapifhir__org_hl7_fhir_core_cve-2023-28465_5-6-1055
Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 alt3kx/cve-2022-1388_poc
F5 BIG-IP RCE exploitation (CVE-2022-1388)