

tiny_tracer
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
api-securitybinary-analysisdynamic-analysis-sandboxing+2
1.7k
hasherezade/tiny_tracerIntel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 gdatasoftwareag/vaas
Verdict-as-a-Service SDKs: Analyze files for malicious content
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
 kaysec/hybrid-submit
A script that automatically submits files to Hybrid Analysis (API)
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
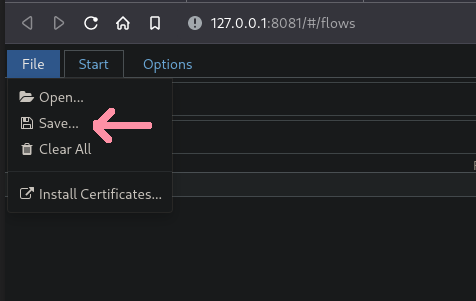 alufers/mitmproxy2swagger
Automagically reverse-engineer REST APIs via capturing traffic
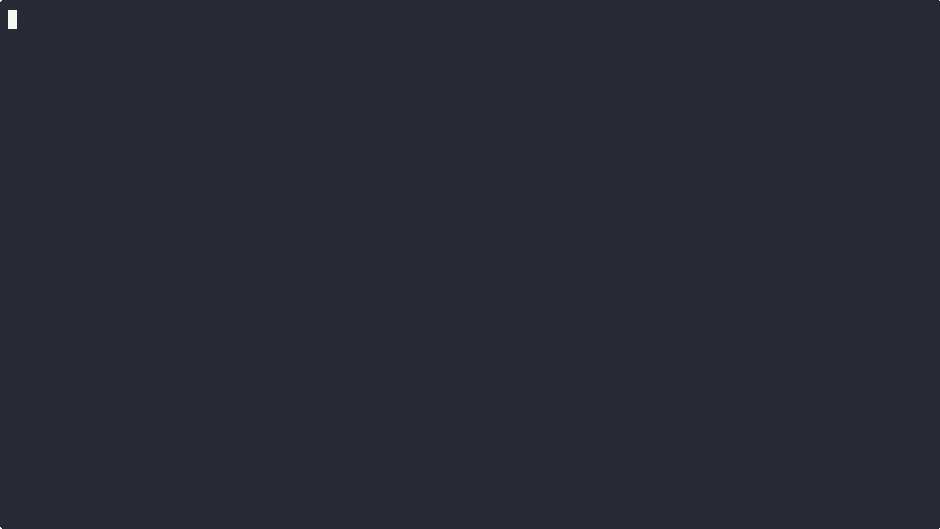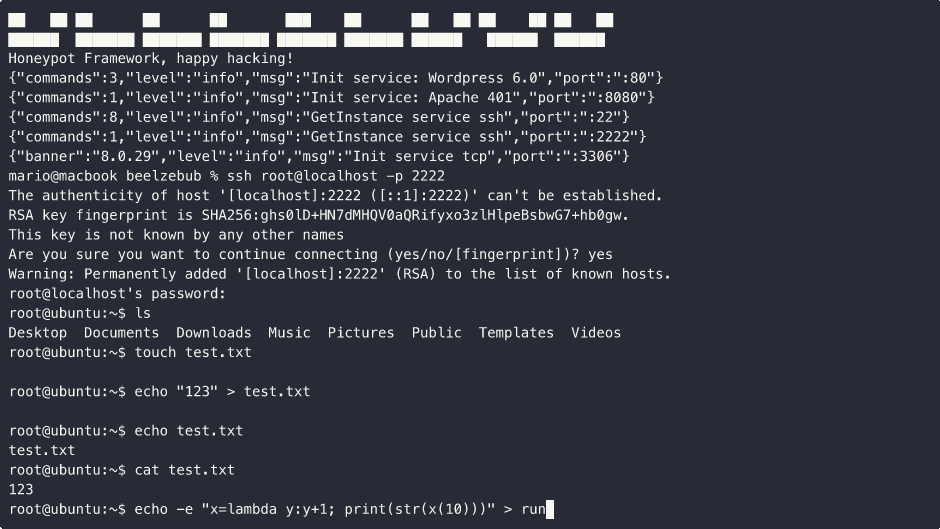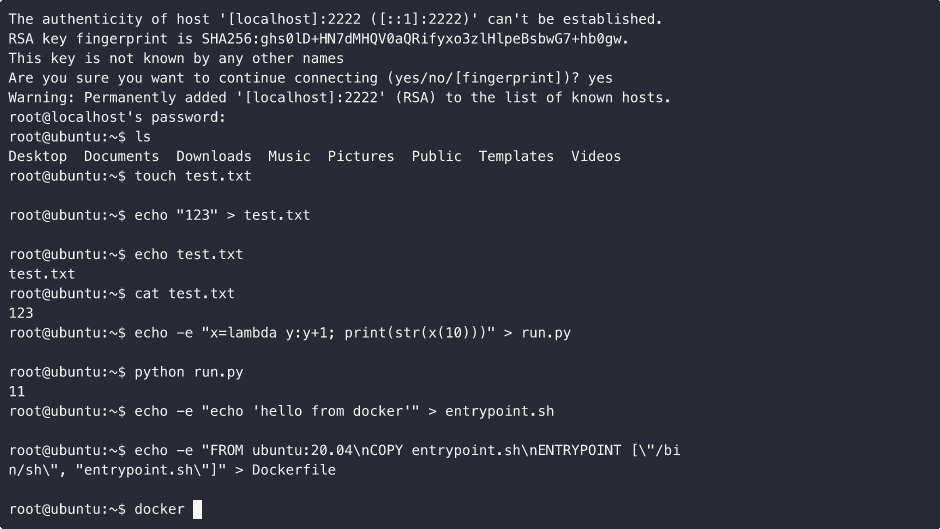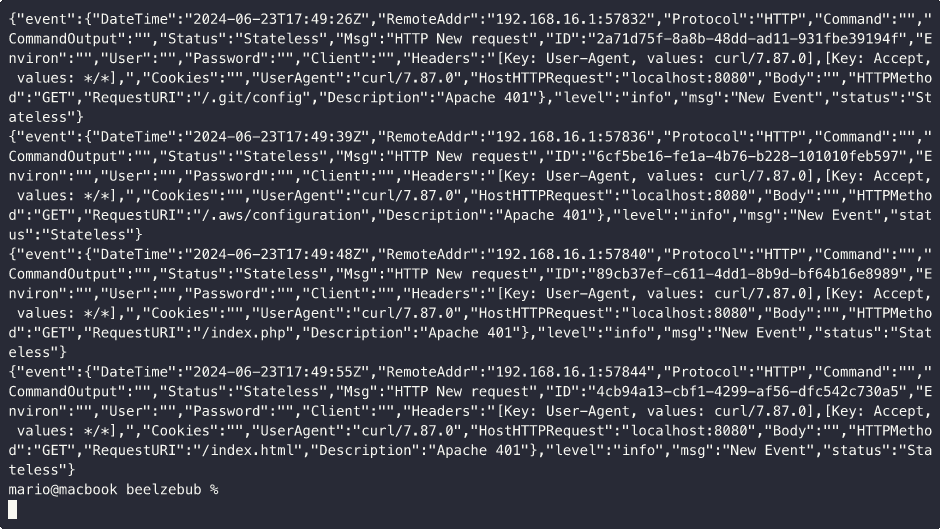 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
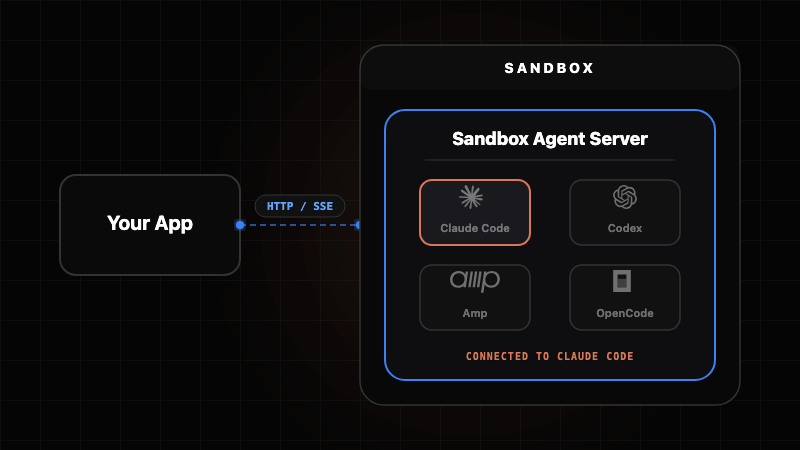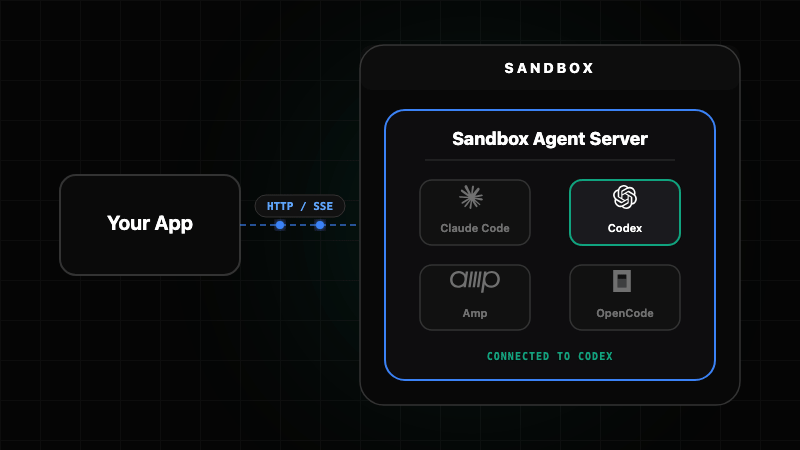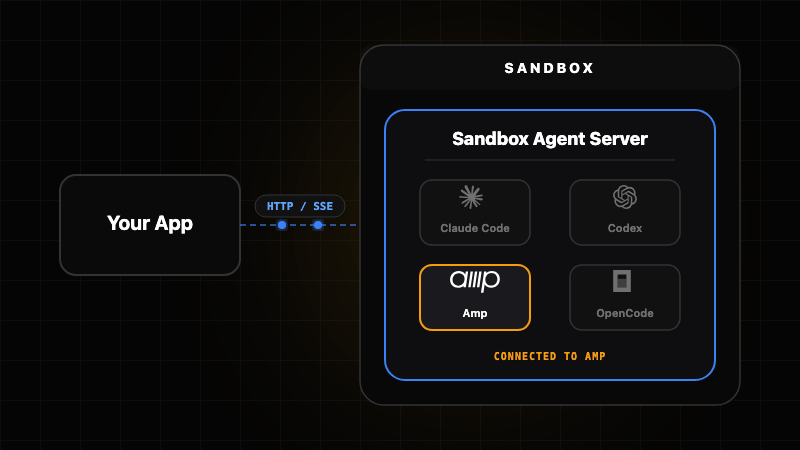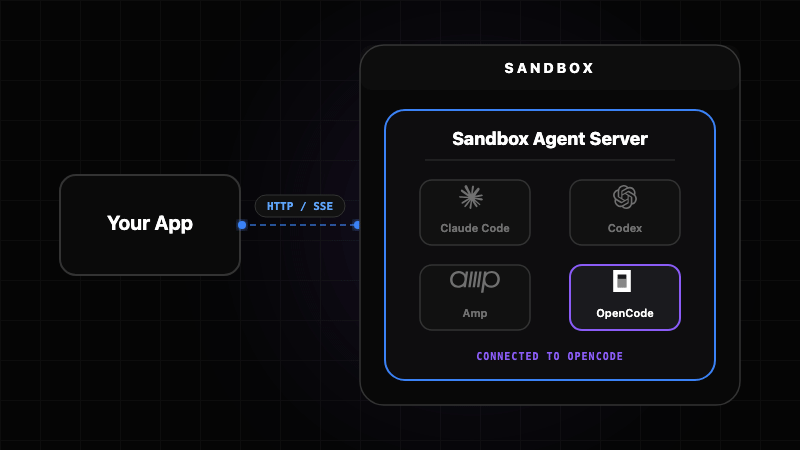 rivet-dev/sandbox-agent
Run Coding Agents in Sandboxes. Control Them Over HTTP. Supports Claude Code, Codex, OpenCode, and Amp.