
trappsec
 trappsec-dev/trappsec
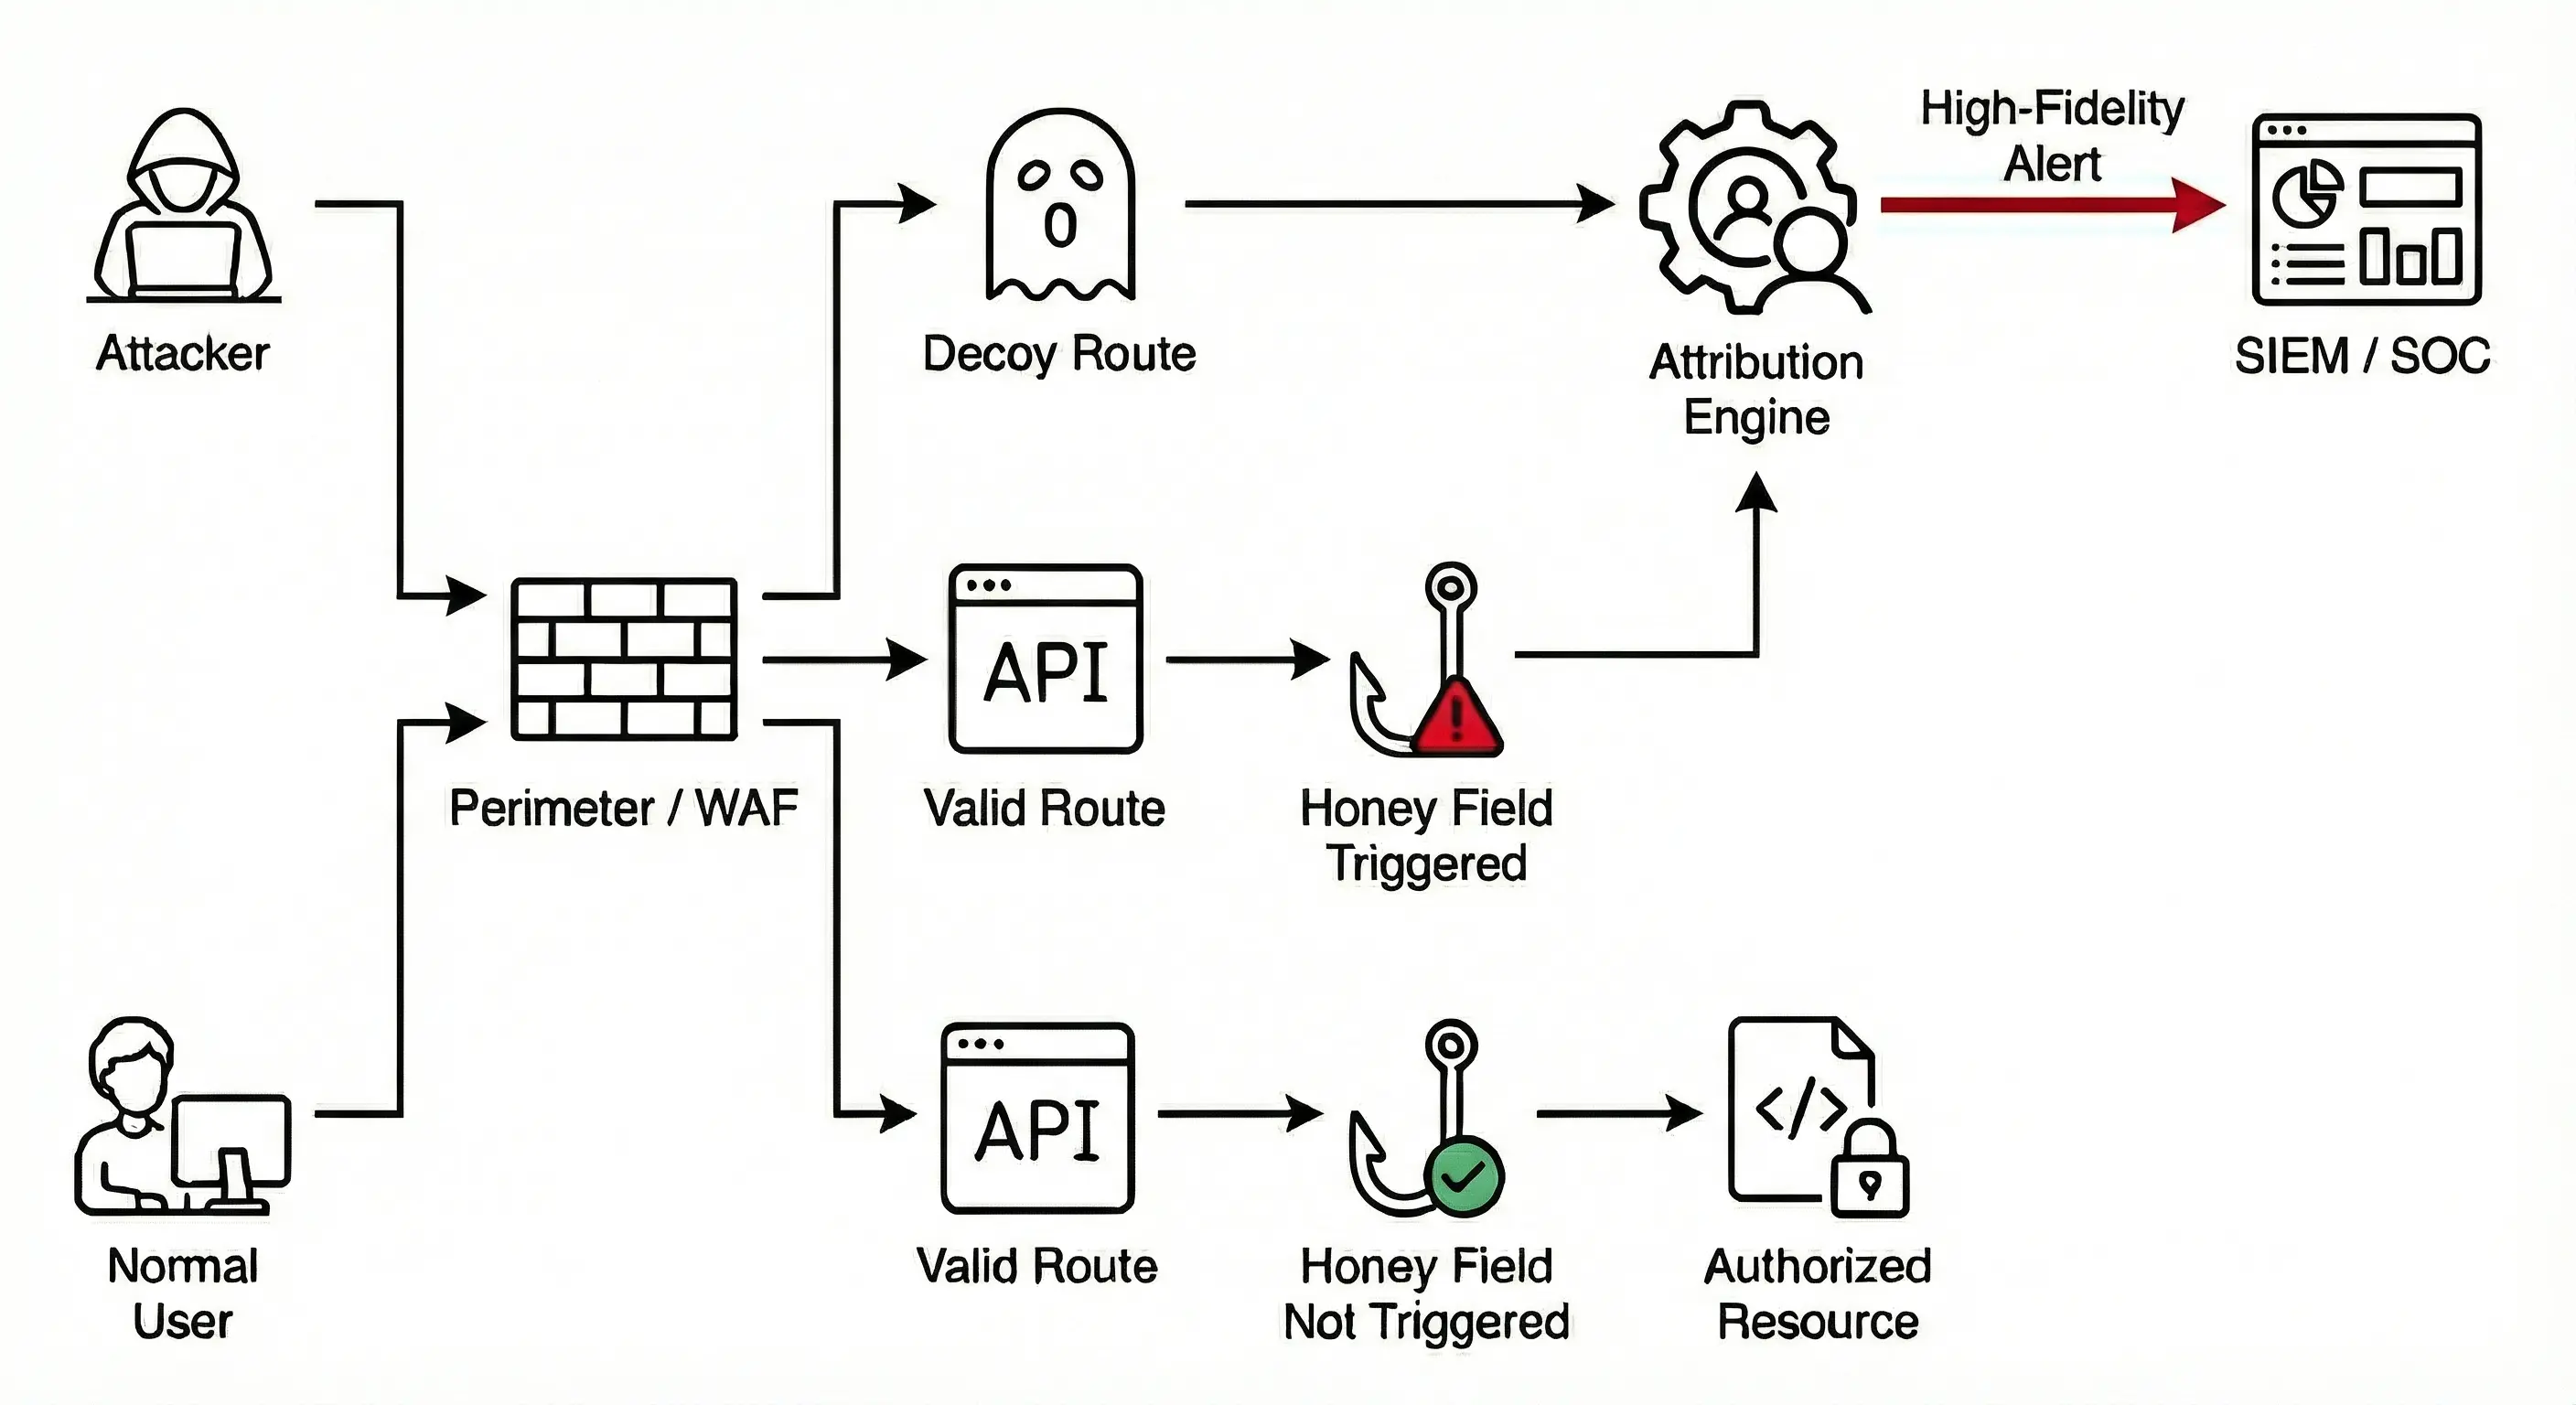
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
api-securitydefensive-toolsidentity-access-management+5
12
trappsec-dev/trappsecOpen-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 davkharrr/cve-2026-19478-poc
Proof-of-concept exploit for unauthenticated remote code injection in GitLab's GraphQL API, using crafted queries to modify or delete public projects…
 sublime-security/ics-phishing-toolkit
Open source tooling to stop ICS phishing (malicious calendar invites)
 zolderio/token-proxy
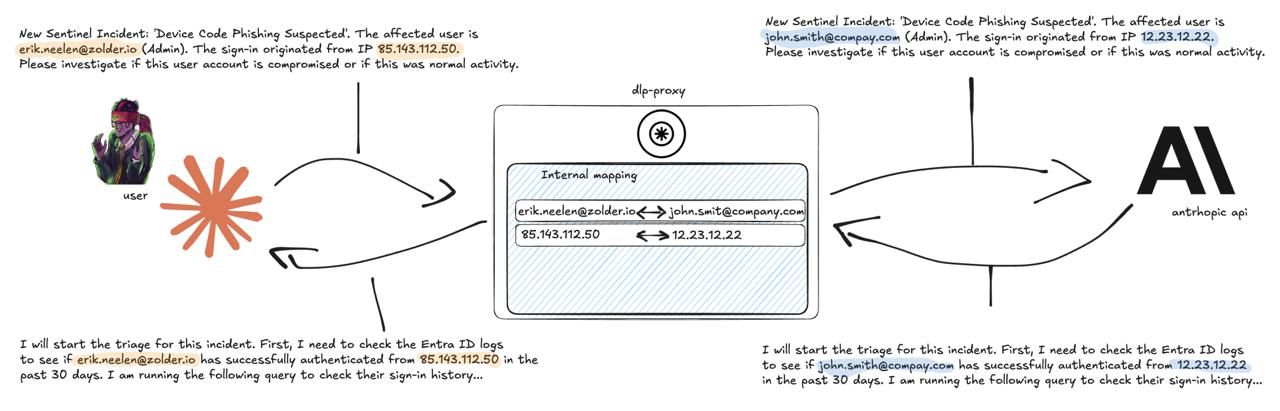
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 xvnpw/k8s-cve-2021-43557-poc
PoC for CVE-2021-43557
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 secnn/cve-2022-24112
Apache APISIX batch-requests RCE(CVE-2022-24112)
 vikasudasi/exfil-scan
Scan LLM outputs and AI-generated content for data exfiltration signals (EchoLeak, CVE-2025-32711) before they reach users or downstream systems
 qruiqai/leakish
Browser privacy-leak detector — eight detection modules, risk scoring, and per-account history, all in your browser.
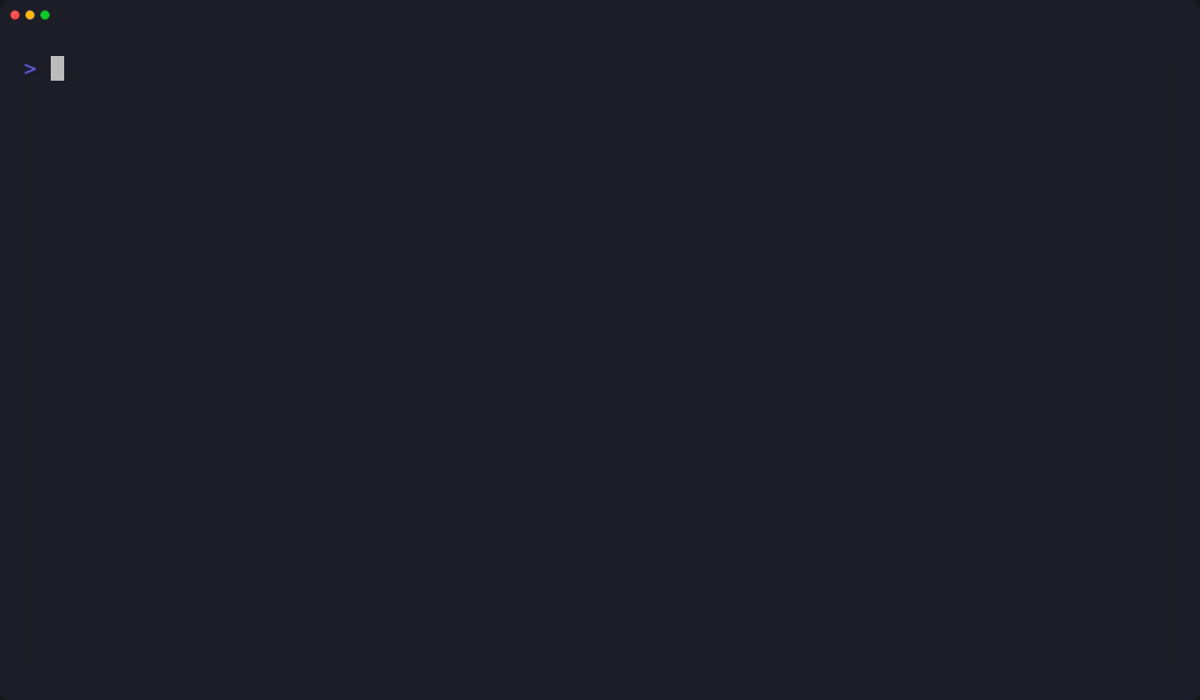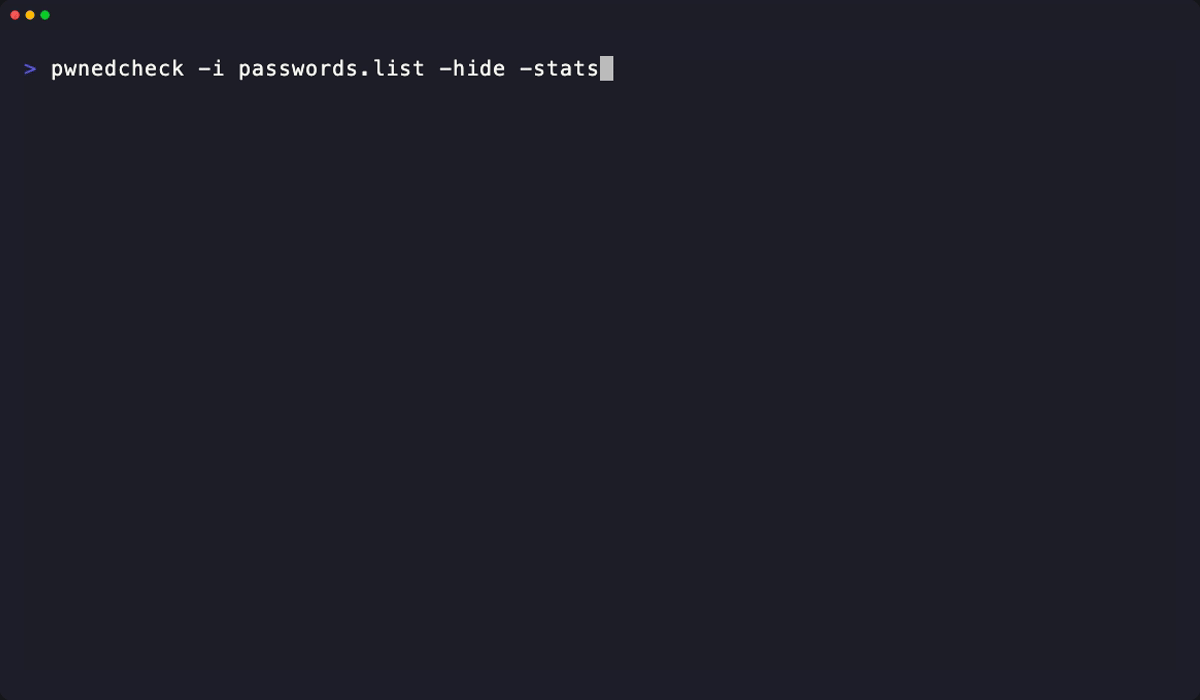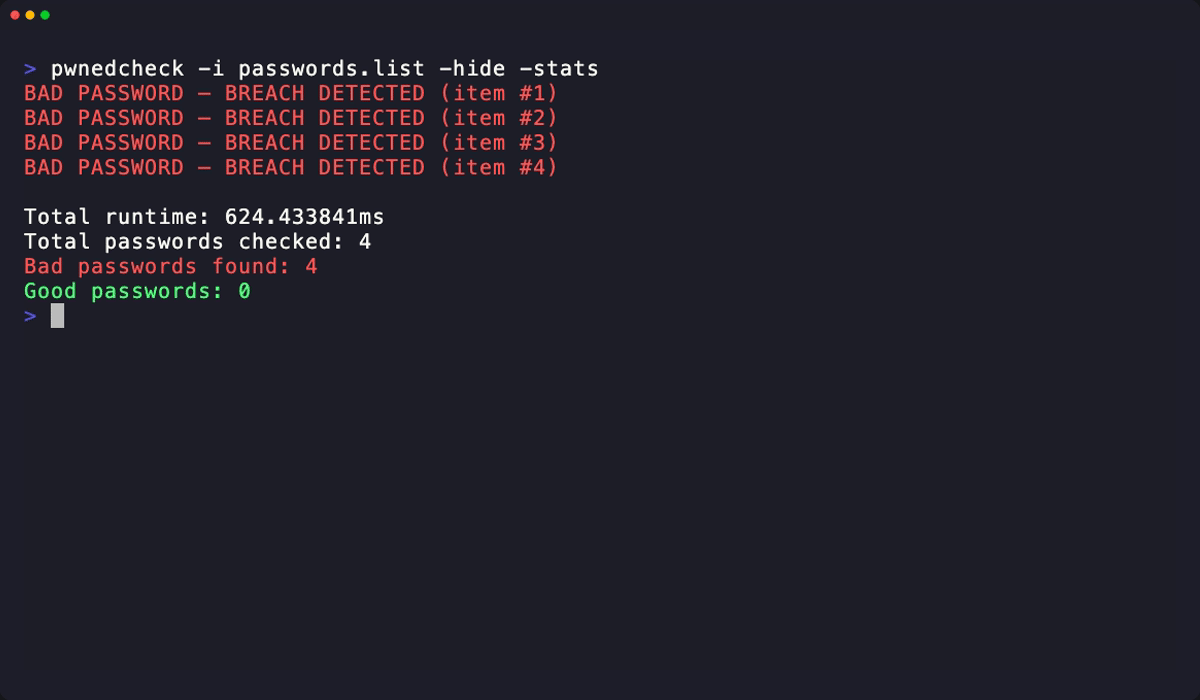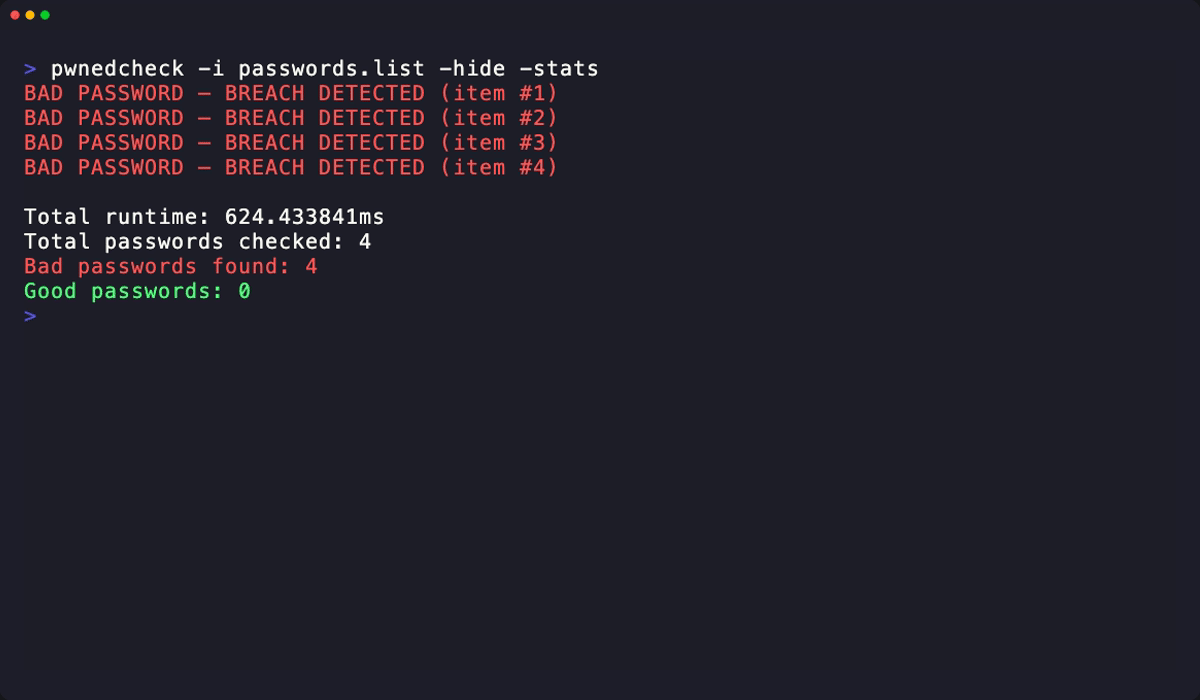 mohamedation/pwnedcheck
A command-line tool to check if passwords have been exposed in data breaches using the Have I Been Pwned (HIBP) API.
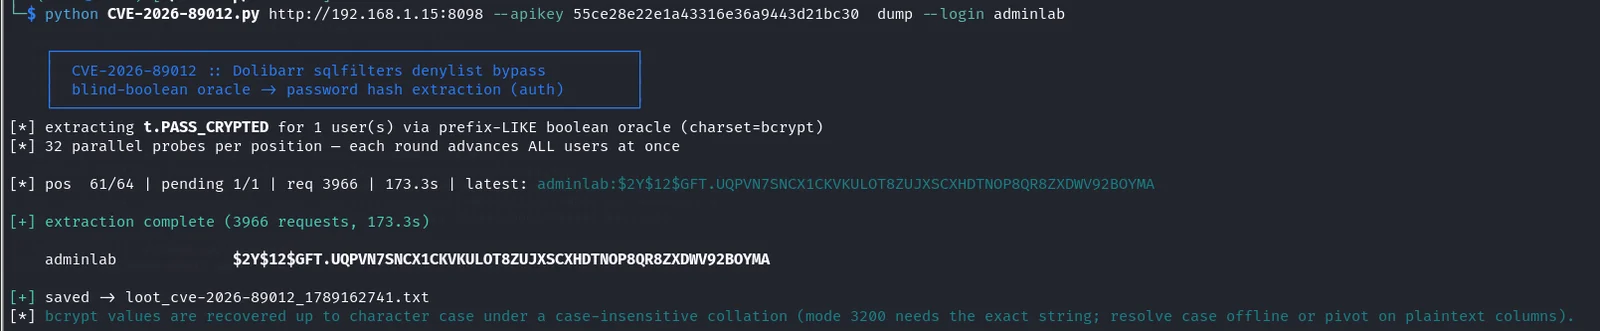 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 0xgh057r3c0n/cve-2025-48827
Critical Unauthenticated API Access in vBulletin
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.