

CVE-2022-24112
 secnn/cve-2022-24112
Apache APISIX batch-requests RCE(CVE-2022-24112)
api-securityexploitationremote-access-tool+2
secnn/cve-2022-24112Apache APISIX batch-requests RCE(CVE-2022-24112)
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 placeos/auth
PlaceOS authentication service and API gatekeeper.
 commonguy25/authproof-sdk
Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.
 0xrlawrence/pribado
Zero-knowledge privacy platform for confidential API key management, encrypted vault, and secure chat. Built on Oasis Sapphire TEEs
 rabbitsafe/cve-2021-37580
Proof-of-concept exploit for Apache ShenYu Admin JWT authentication bypass (CVE-2021-37580). Includes a scanning script to detect vulnerable…

 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
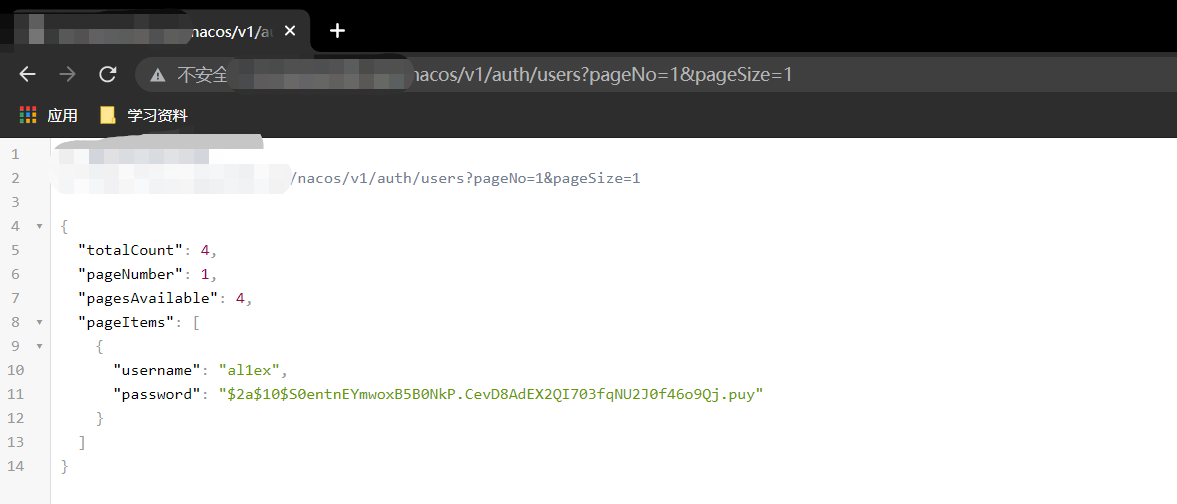 al1ex/alibab-nacos-unauthorized-reset-pwd
Alibab-Nacos-Unauthorized-Reset PWD
 k3ystr0k3r/cve-2026-31816
CVE-2026-31816 - Budibase Authentication Bypass to RCE
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 george0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection
POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
 george0papasotiriou/cve-2026-3456-oauth2-pkce-race-condition-account-takeover-
Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
 nel-droid/cve-2026-71204-poc
PoC: changedetection.io settings blind-merge mass assignment (CVE-2026-71204, Medium 6.3)