
APTS
 owasp/apts
OWASP Autonomous Penetration Testing Standard
api-securitycloud-securitycurated-resources+5
owasp/aptsOWASP Autonomous Penetration Testing Standard
 openbmc/bmcweb
A do everything Redfish, KVM, GUI, and DBus webserver for OpenBMC
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 h33tlit/secret-regex-list
List of regex for scraping secret API keys and juicy information.
 momenbasel/keyfinder
Passive API key and secret discovery browser extension for Chrome and Firefox. 80+ detection patterns, zero config.
 dolevf/graphw00f
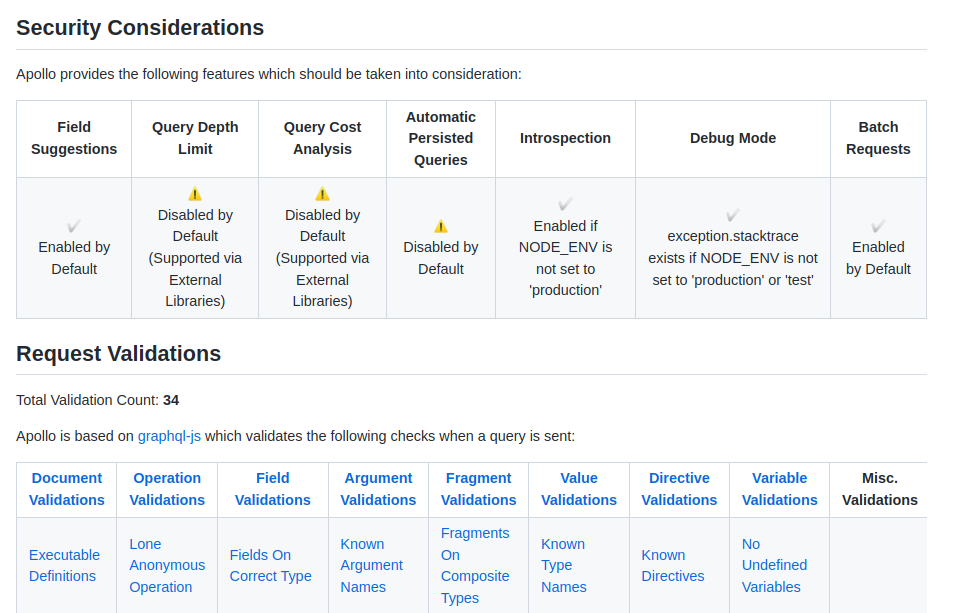
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 censys/censys-python
An easy-to-use and lightweight API wrapper for Censys APIs.
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
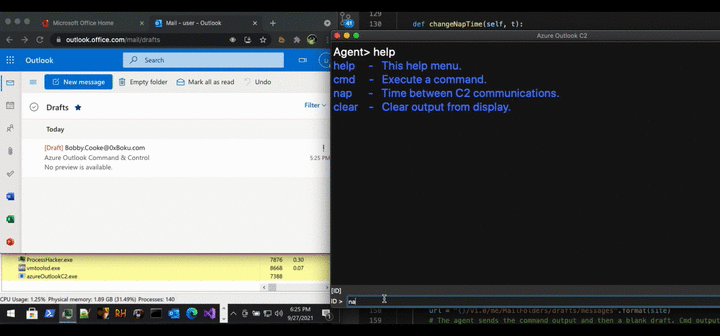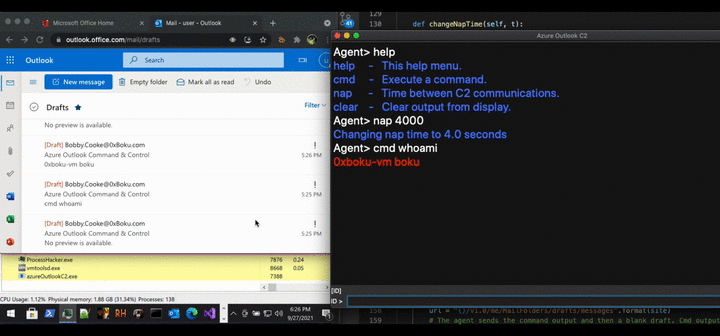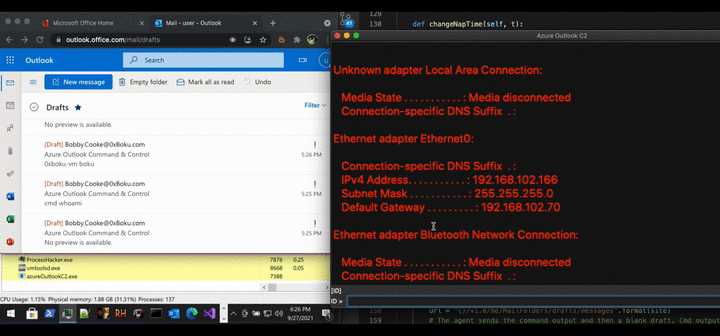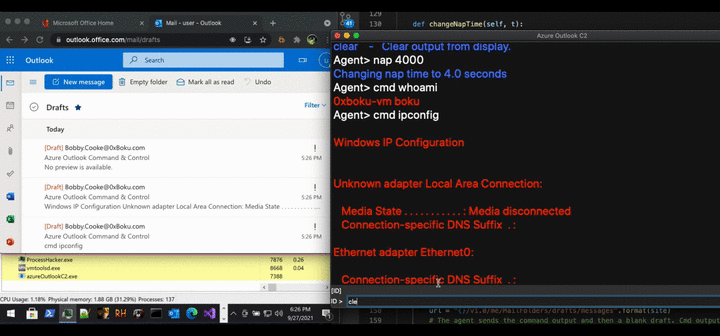 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
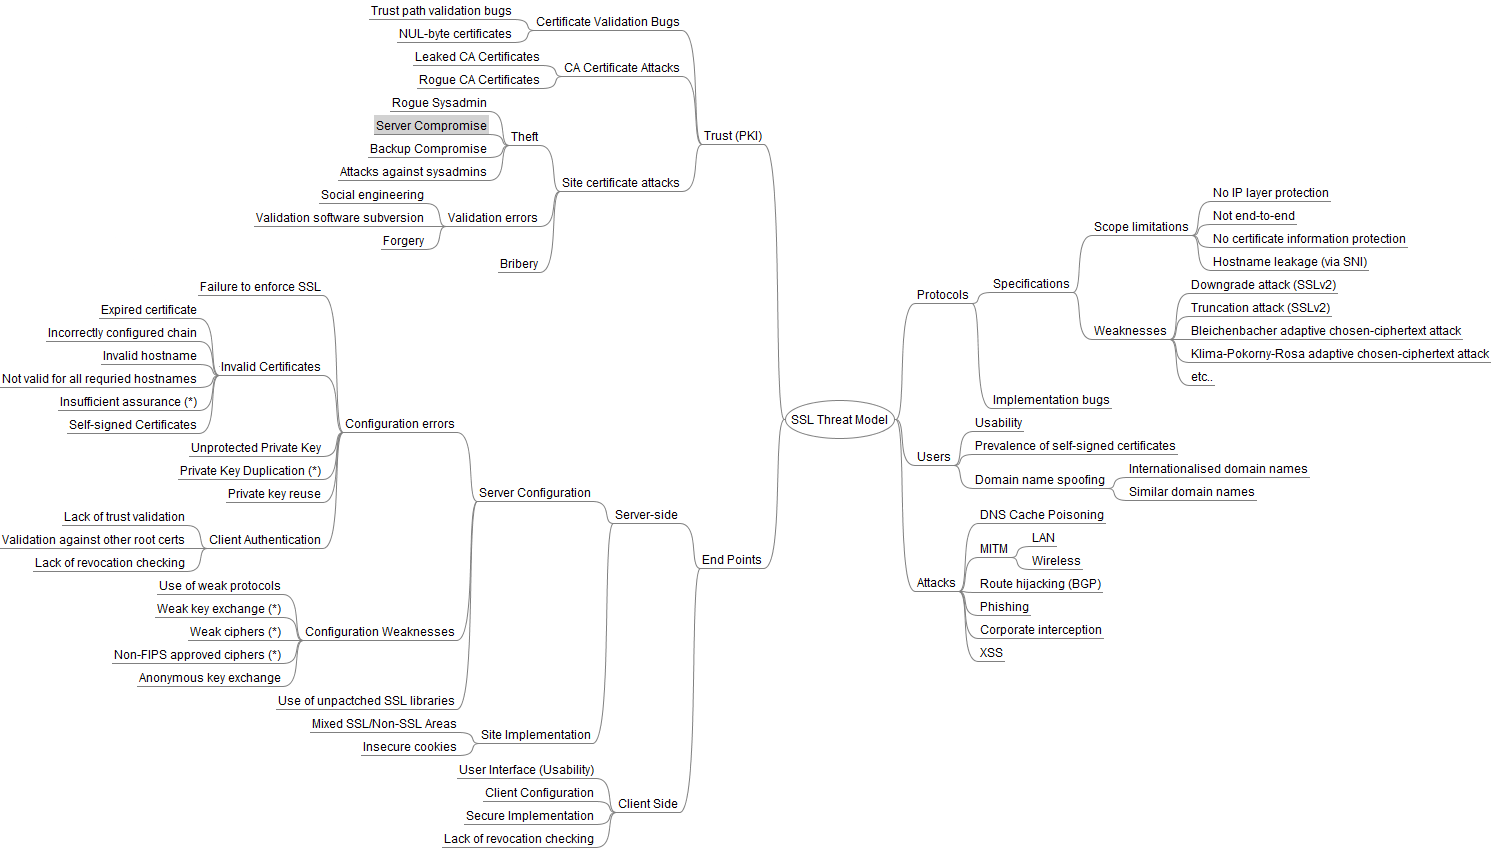 taleliyahu/threat_model_examples
A collection of real-world threat model examples across various technologies, providing practical insights into identifying and mitigating security…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
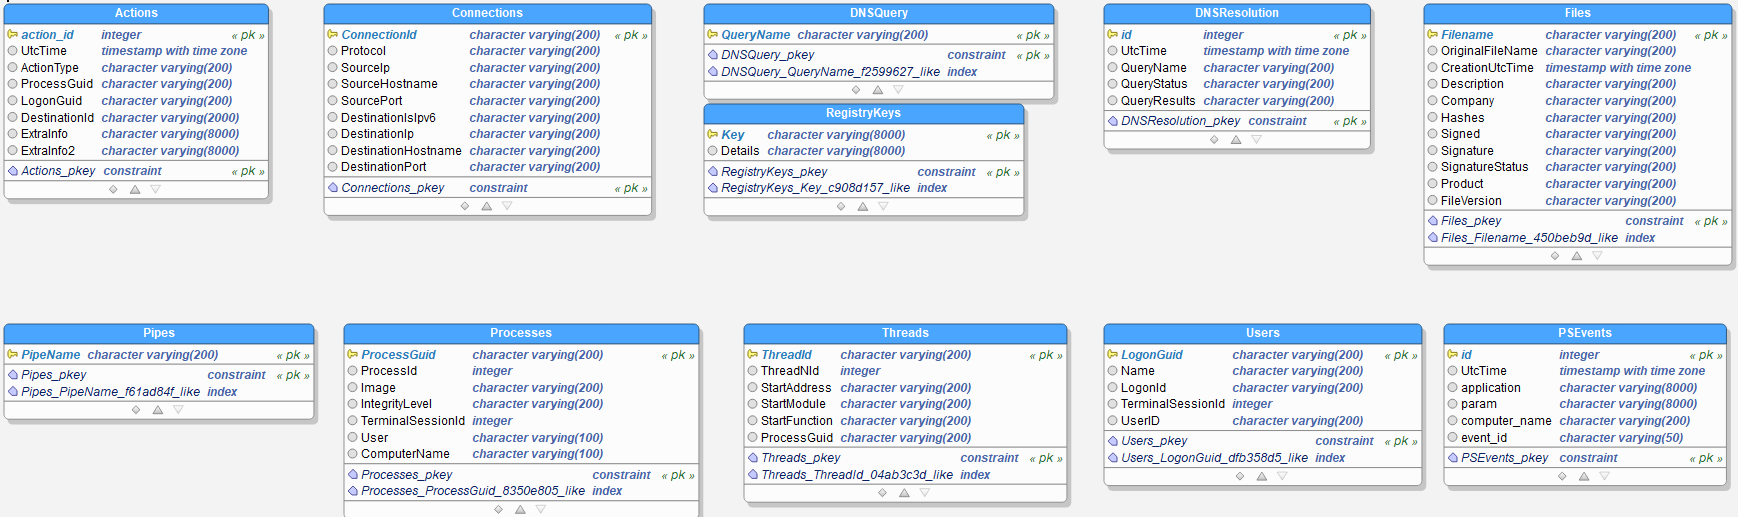 lucky-luk3/grafiki
Threat Hunting tool about Sysmon and graphs
 nicholasaleks/graphql-threat-matrix
GraphQL threat framework used by security professionals to research security gaps in GraphQL implementations
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project