CVE-2026-21020-Protobuf-Message-Parsing-Polymorphic-Deserialization-Vulnerability

PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…

PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…

Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…

Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.

CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.

Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…

Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…

Exploit tool for CVE-2026-1529, demonstrating unauthorized organization registration in Keycloak via JWT token manipulation. Includes token…

JetEngine <= 3.7.7 — Unauthenticated Stored Cross-Site Scripting via CCT REST API

Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…

Detector de CVE-2026-35616: identifica servidores FortiClient EMS vulnerables (7.4.5-7.4.6).

Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…

CVE-2025-55182 and CVE-2025-66478

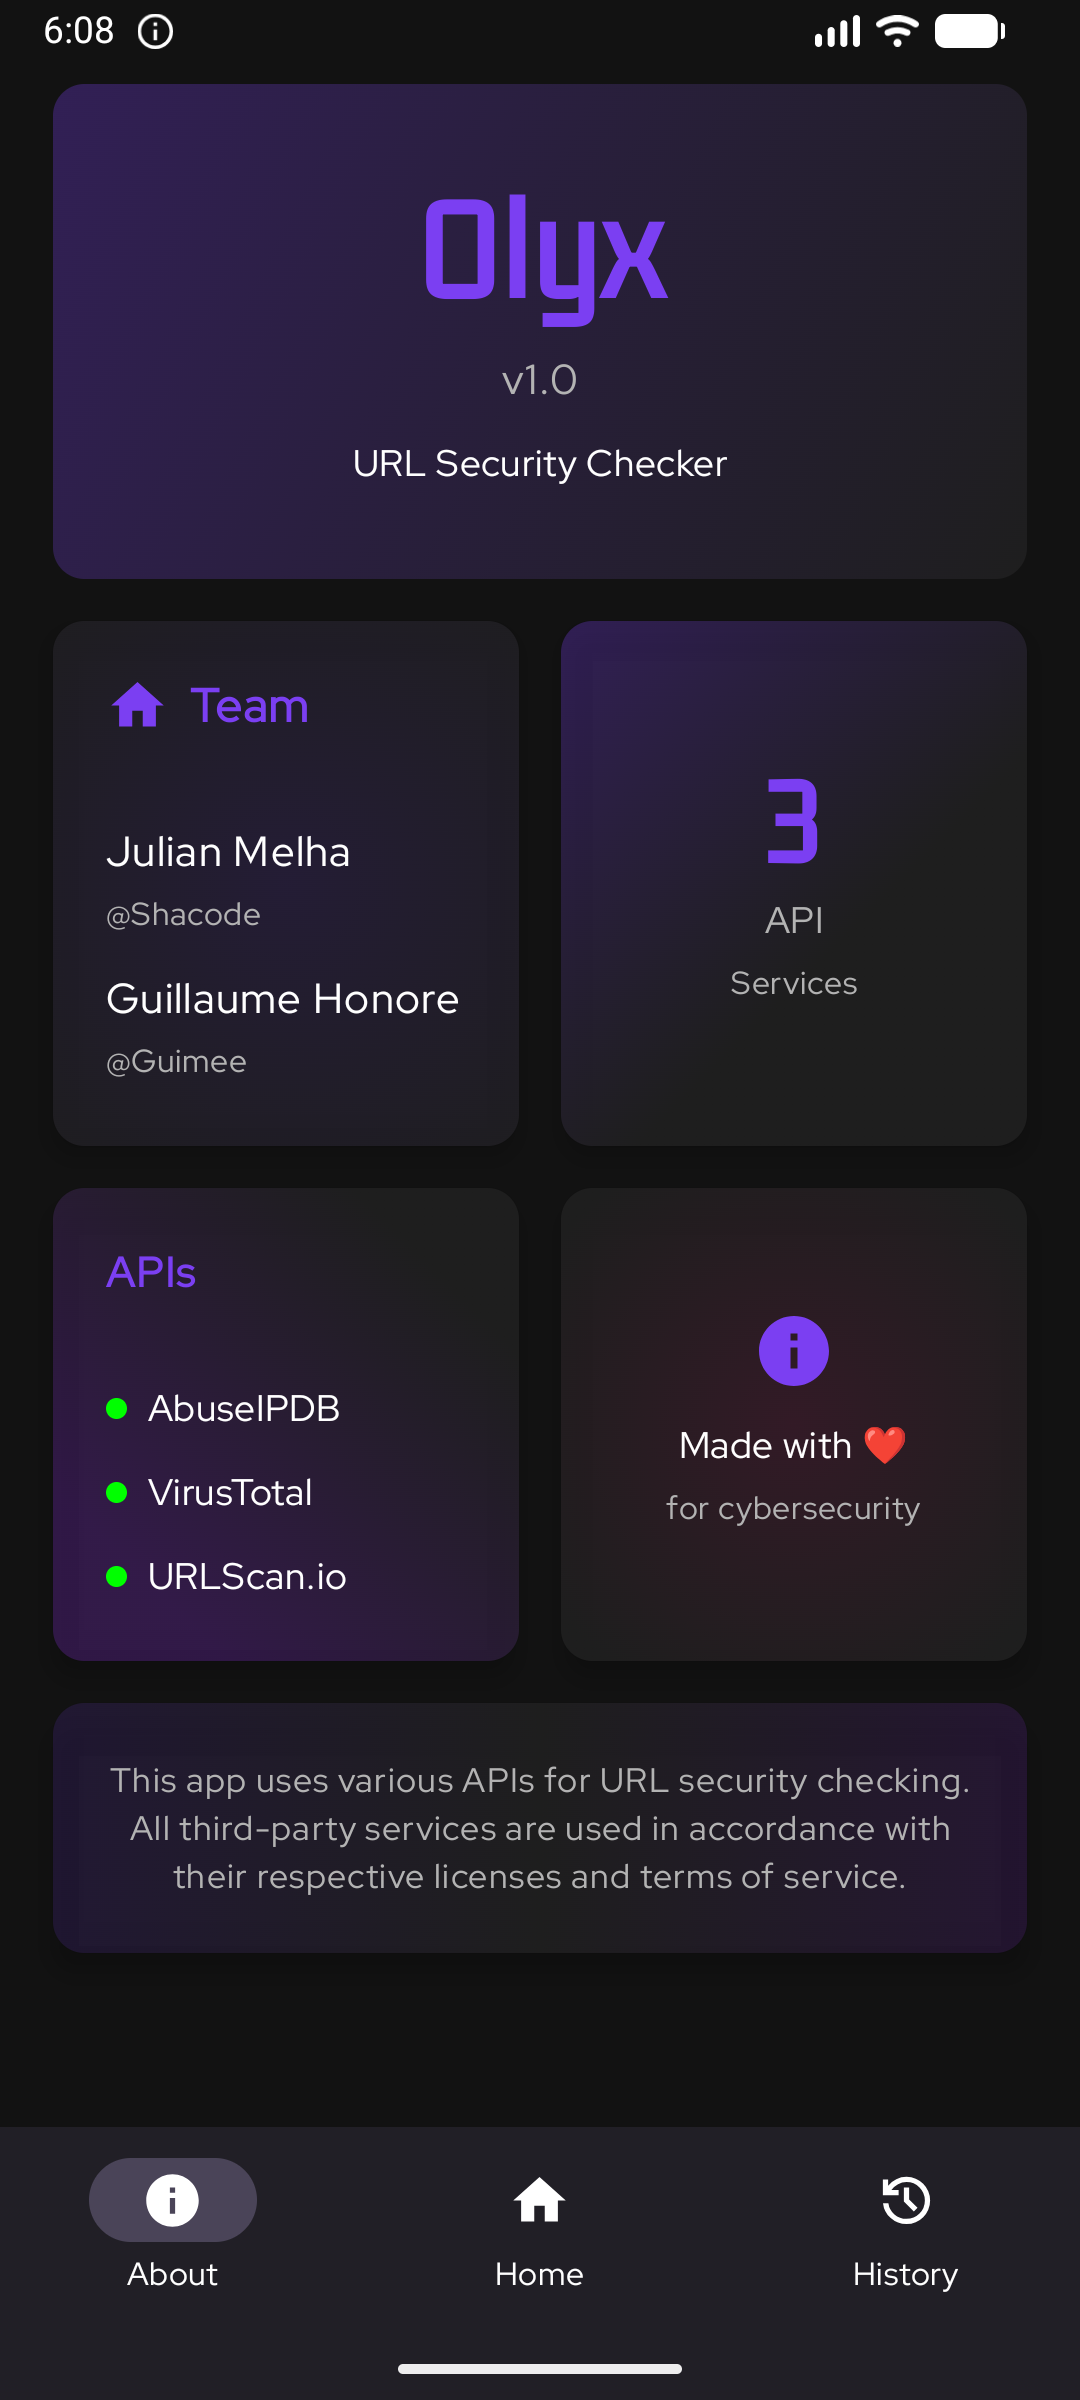
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…

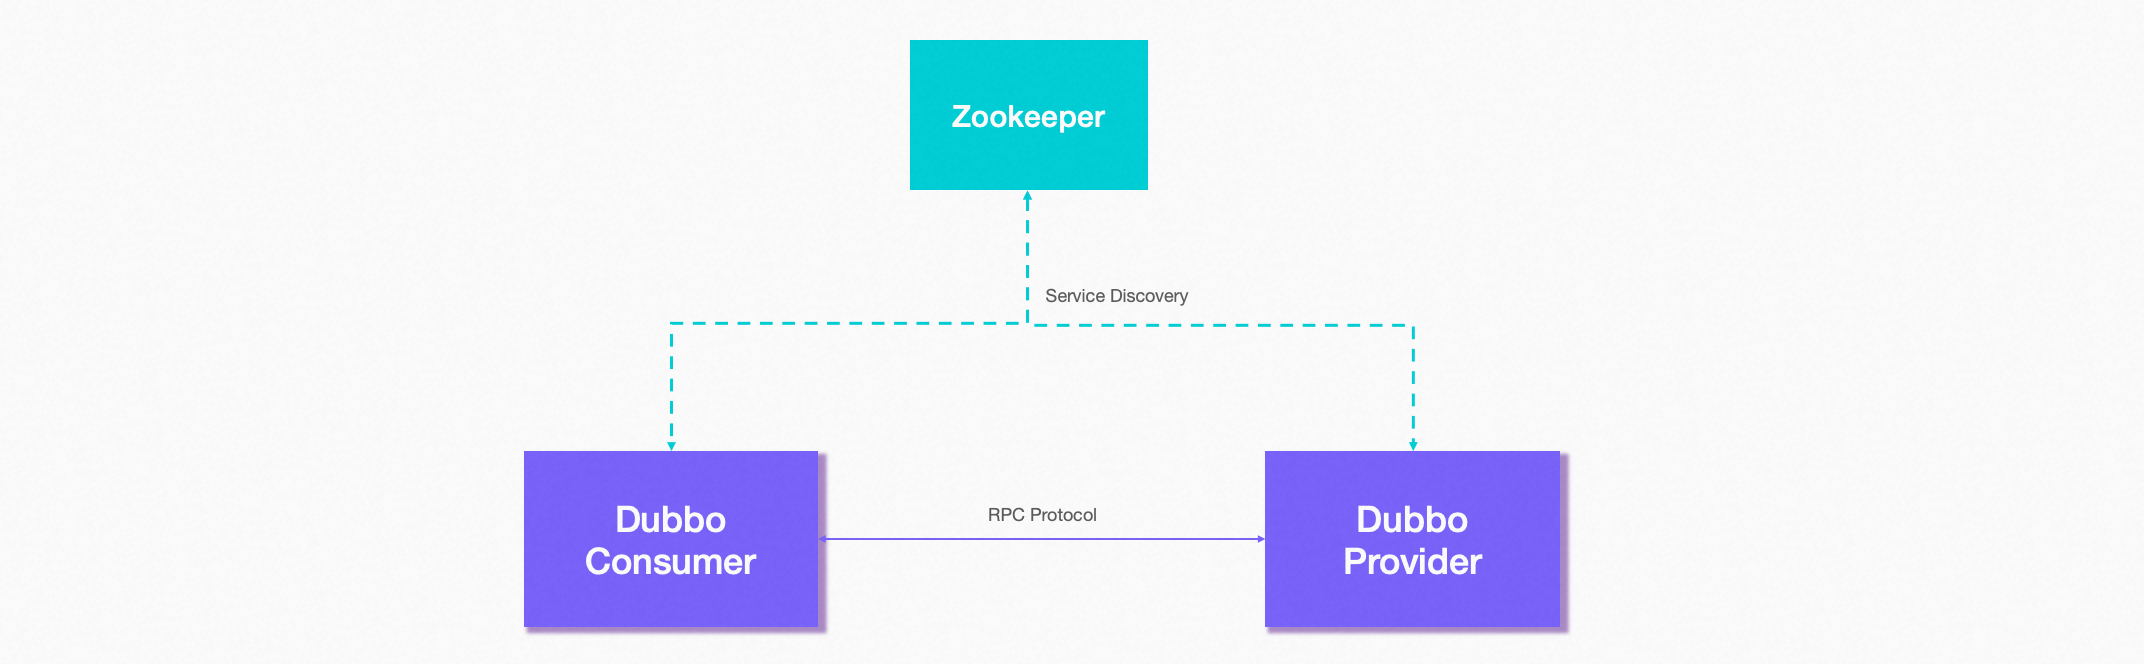
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.

Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…

Proof-of-concept exploit for CVE-2026-23745 targeting GraphQL endpoints, demonstrating the vulnerability and potential impact for security testing…

Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.

Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…