
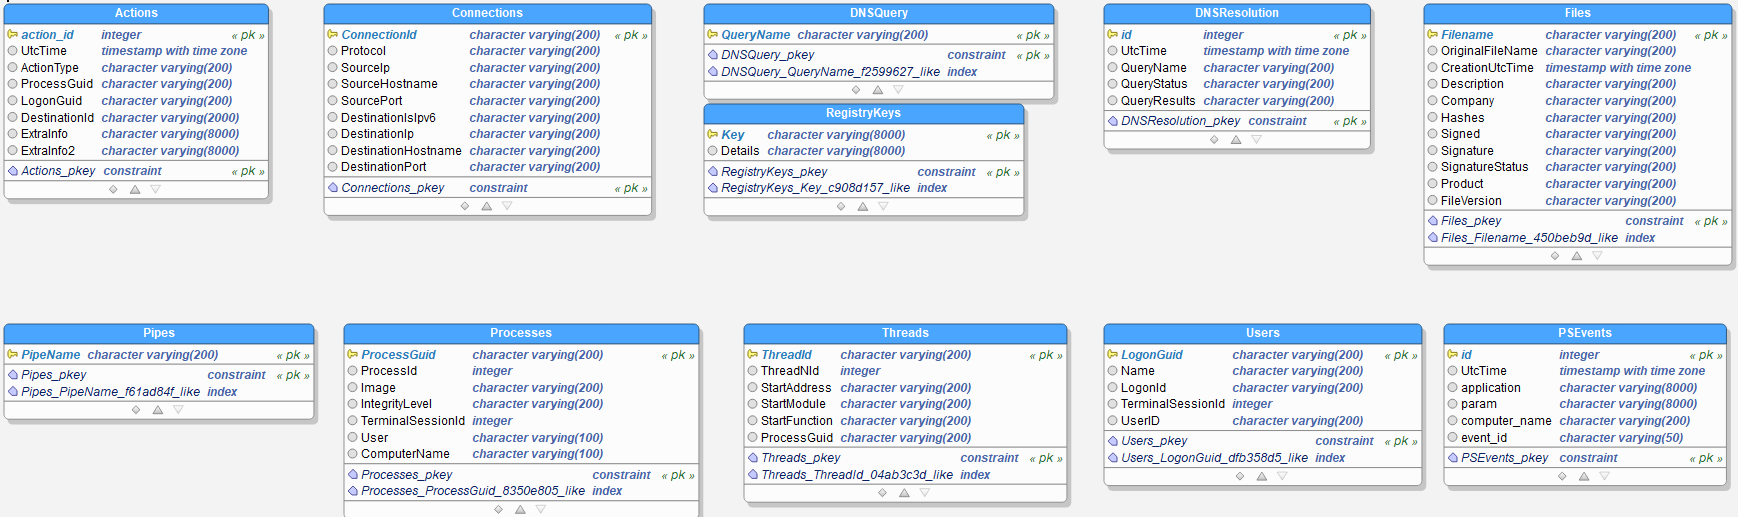
Grafiki
 lucky-luk3/grafiki
Threat Hunting tool about Sysmon and graphs
api-securityapi-security-testing
lucky-luk3/grafikiThreat Hunting tool about Sysmon and graphs
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
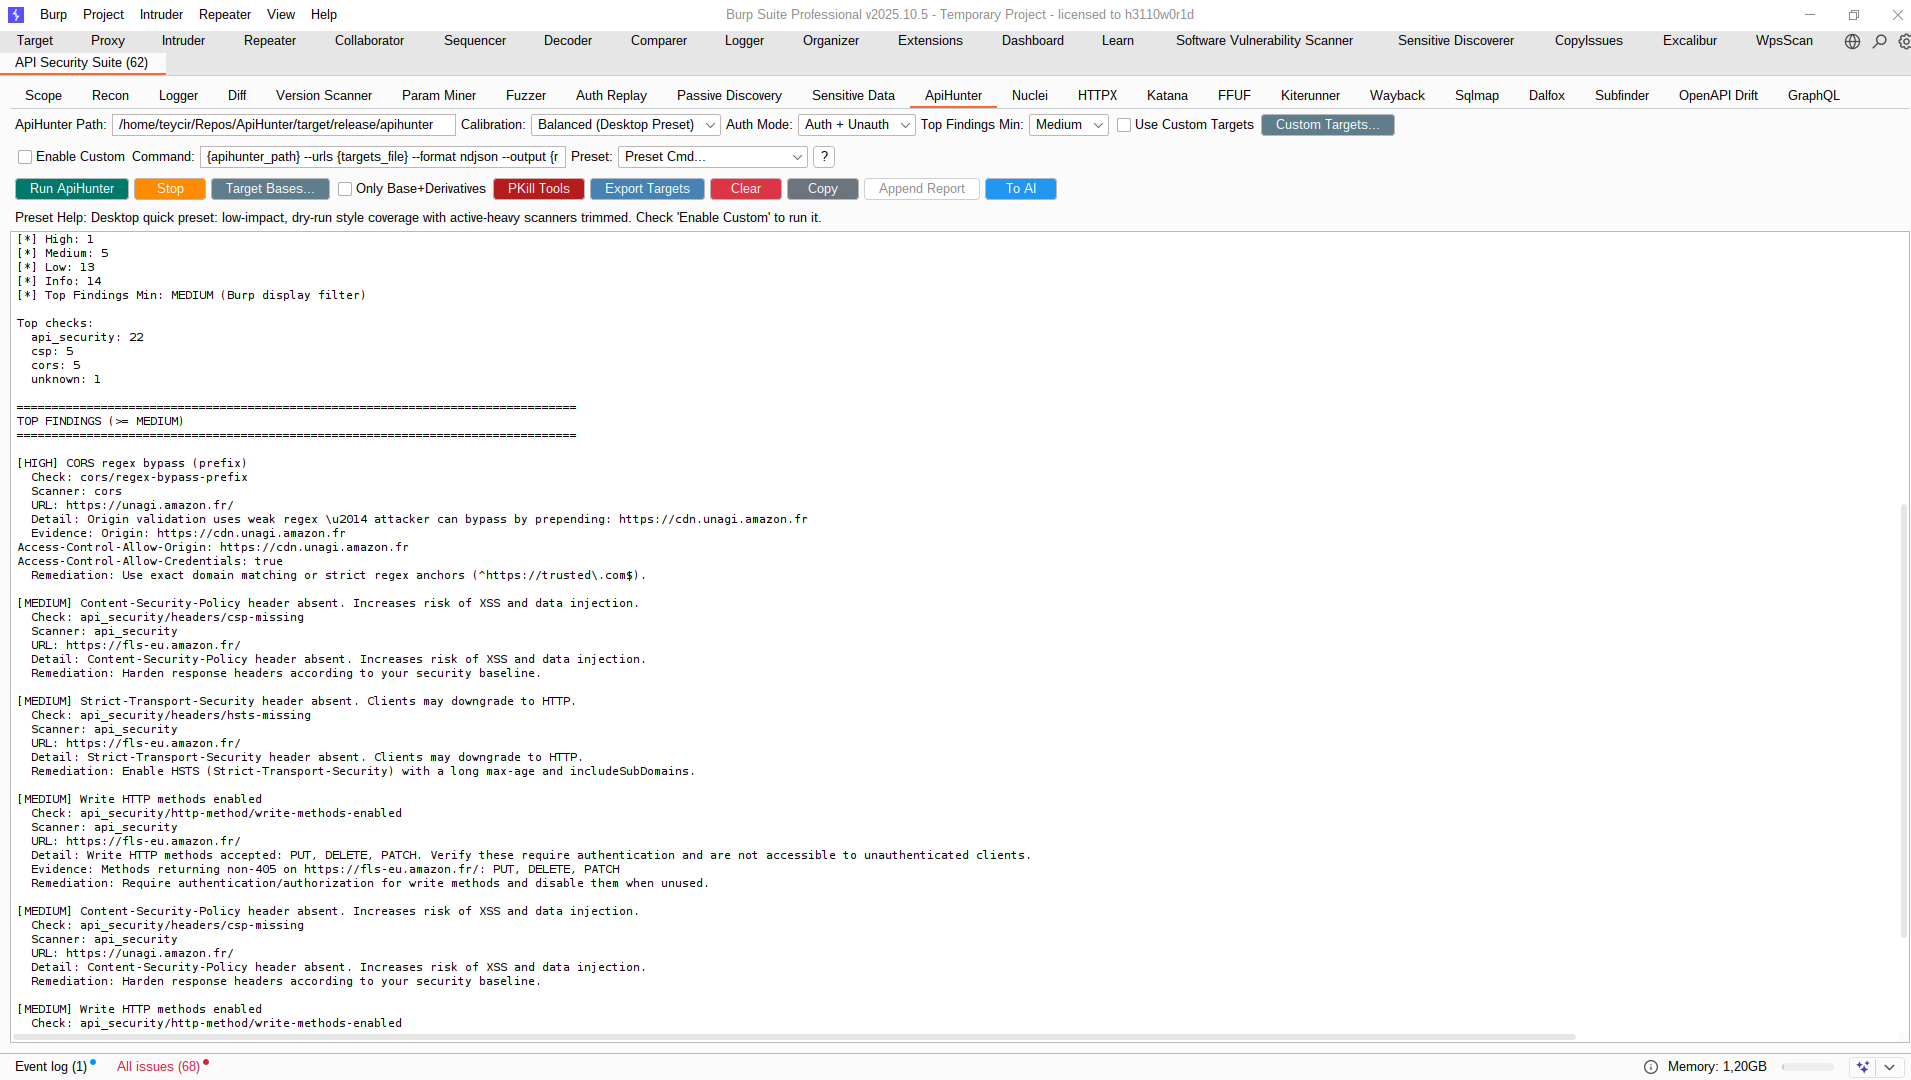 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 penteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth
Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
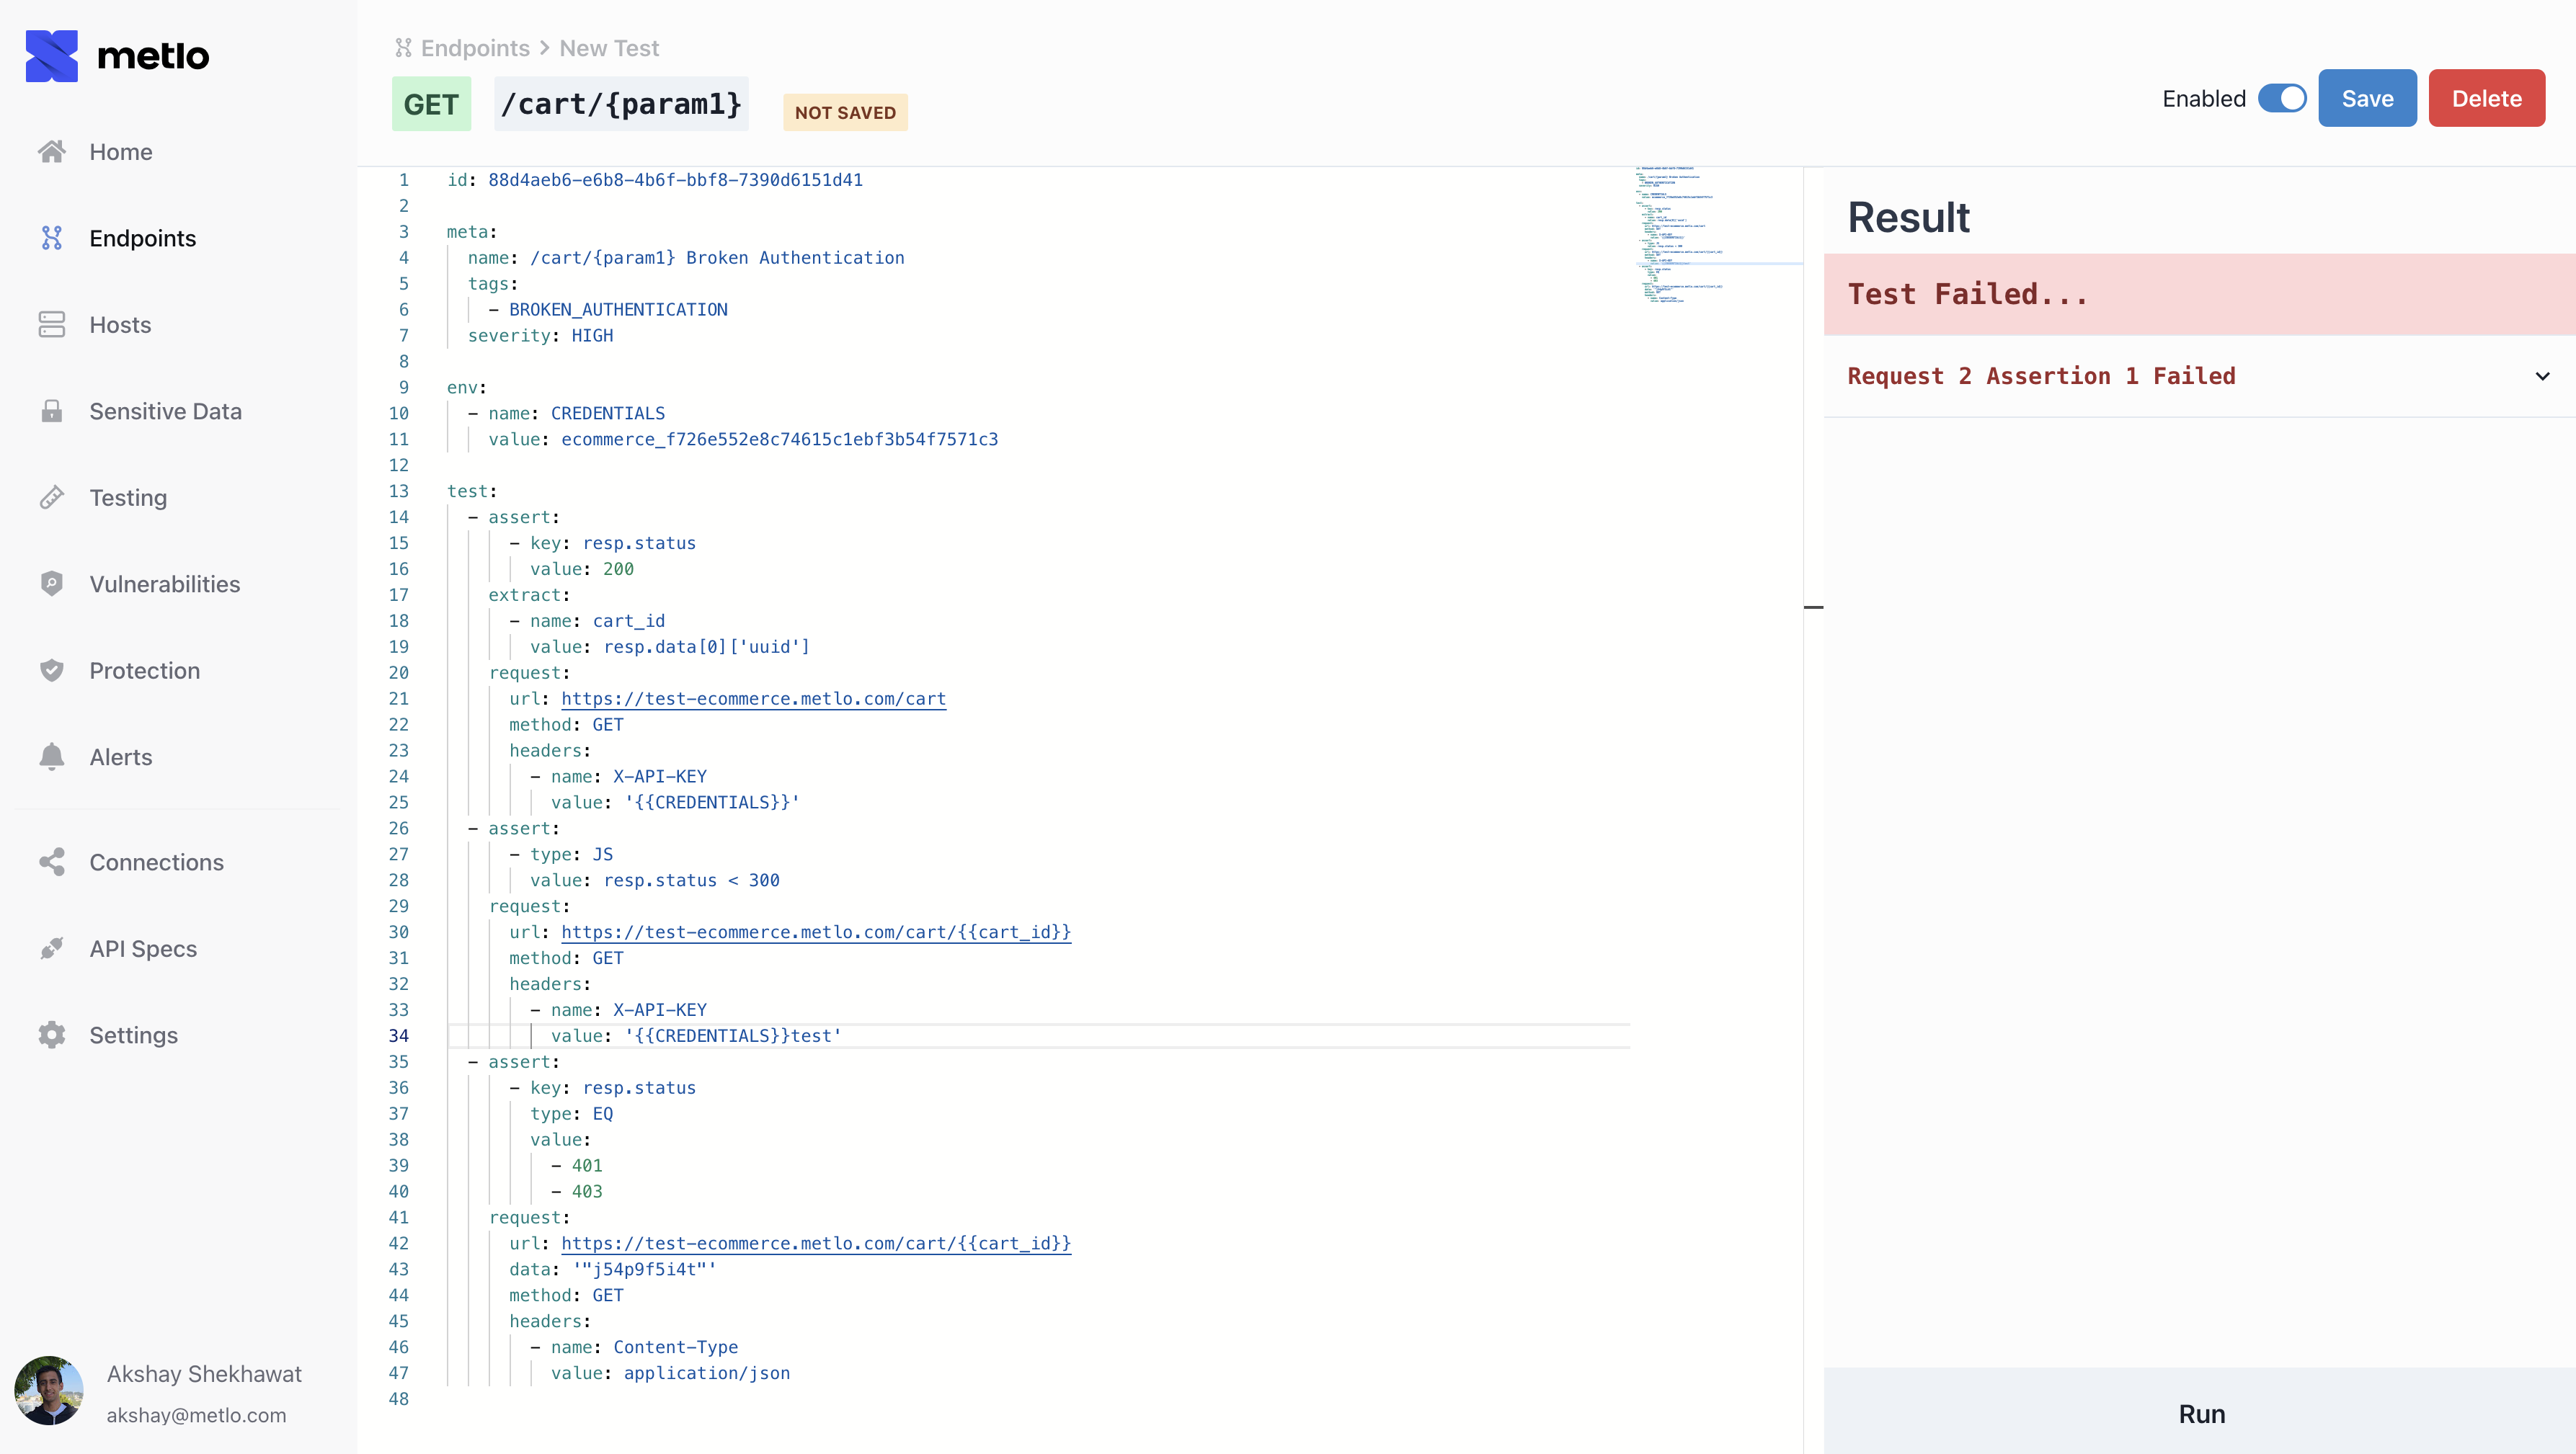 metlo-labs/metlo
Metlo is an open-source API security platform.
 elastic/agent-skills
Official Elastic Skills
 shoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6
Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 ch4n3-yoon/cve-2025-62727-demo
Proof of concept of CVE-2025-62727 that can cause denial-of-service in FastAPI (based Starlette <= 0.48.0)
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 oscerd/cve-2026-46726
Reproducer for CVE-2026-46726: Apache Camel camel-vertx-websocket unfiltered inbound header injection enabling SSRF and secret disclosure via…
 oscerd/cve-2026-46456
Reproducer for CVE-2026-46456 — Apache Camel camel-aws2-sqs inbound message-attribute header injection (Camel control-header injection via…
 oscerd/cve-2026-23552
CVE-2026-23552 - Cross-Realm Token Acceptance in camel-keycloak