

damn-vulnerable-MCP-server
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
ai-securityapi-securityctf+5
1.4k
harishsg993010/damn-vulnerable-mcp-serverDamn Vulnerable MCP Server
 owasp/apts
OWASP Autonomous Penetration Testing Standard
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 umputun/reproxy
Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…
 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
 p0pr0ck5/lua-resty-waf
High-performance WAF built on the OpenResty stack
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
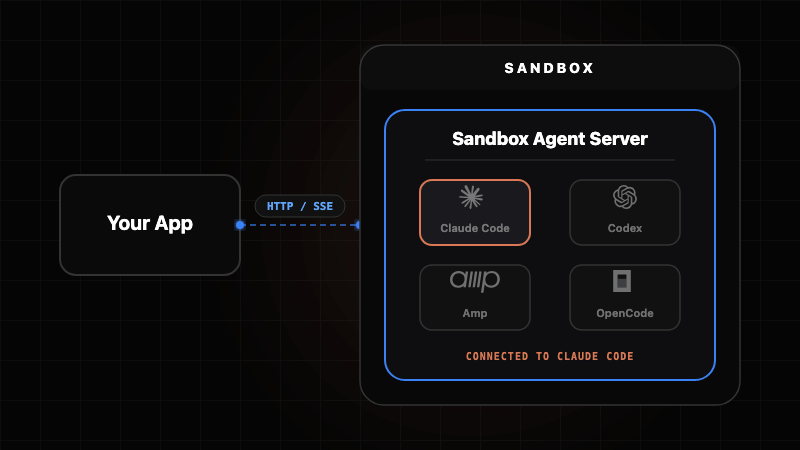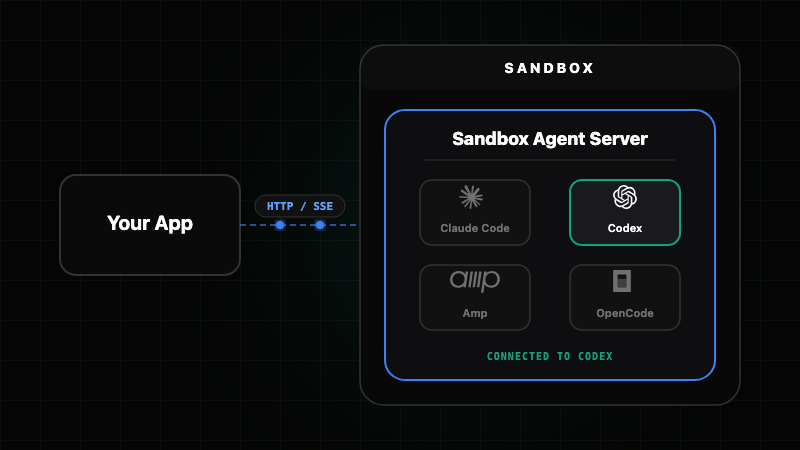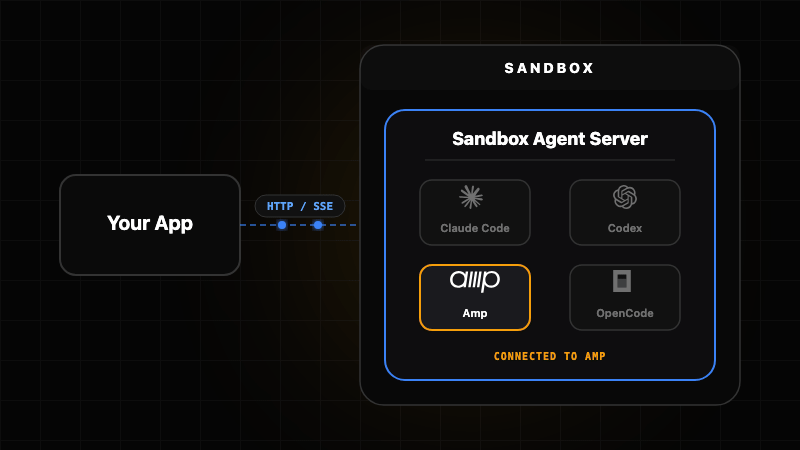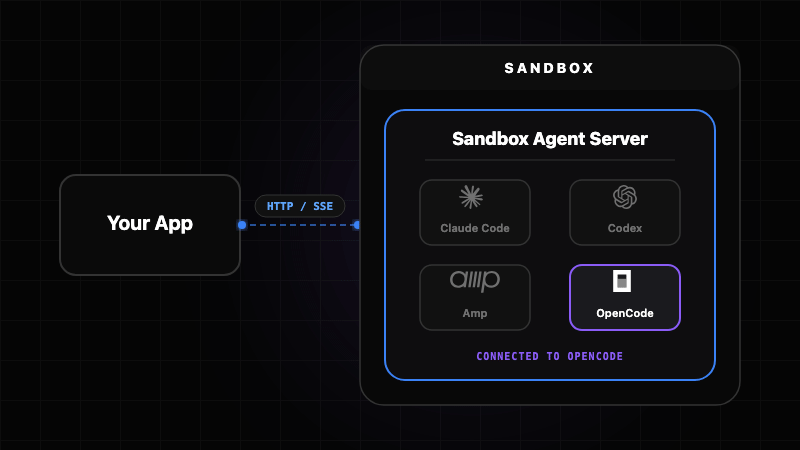 rivet-dev/sandbox-agent
Run Coding Agents in Sandboxes. Control Them Over HTTP. Supports Claude Code, Codex, OpenCode, and Amp.
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
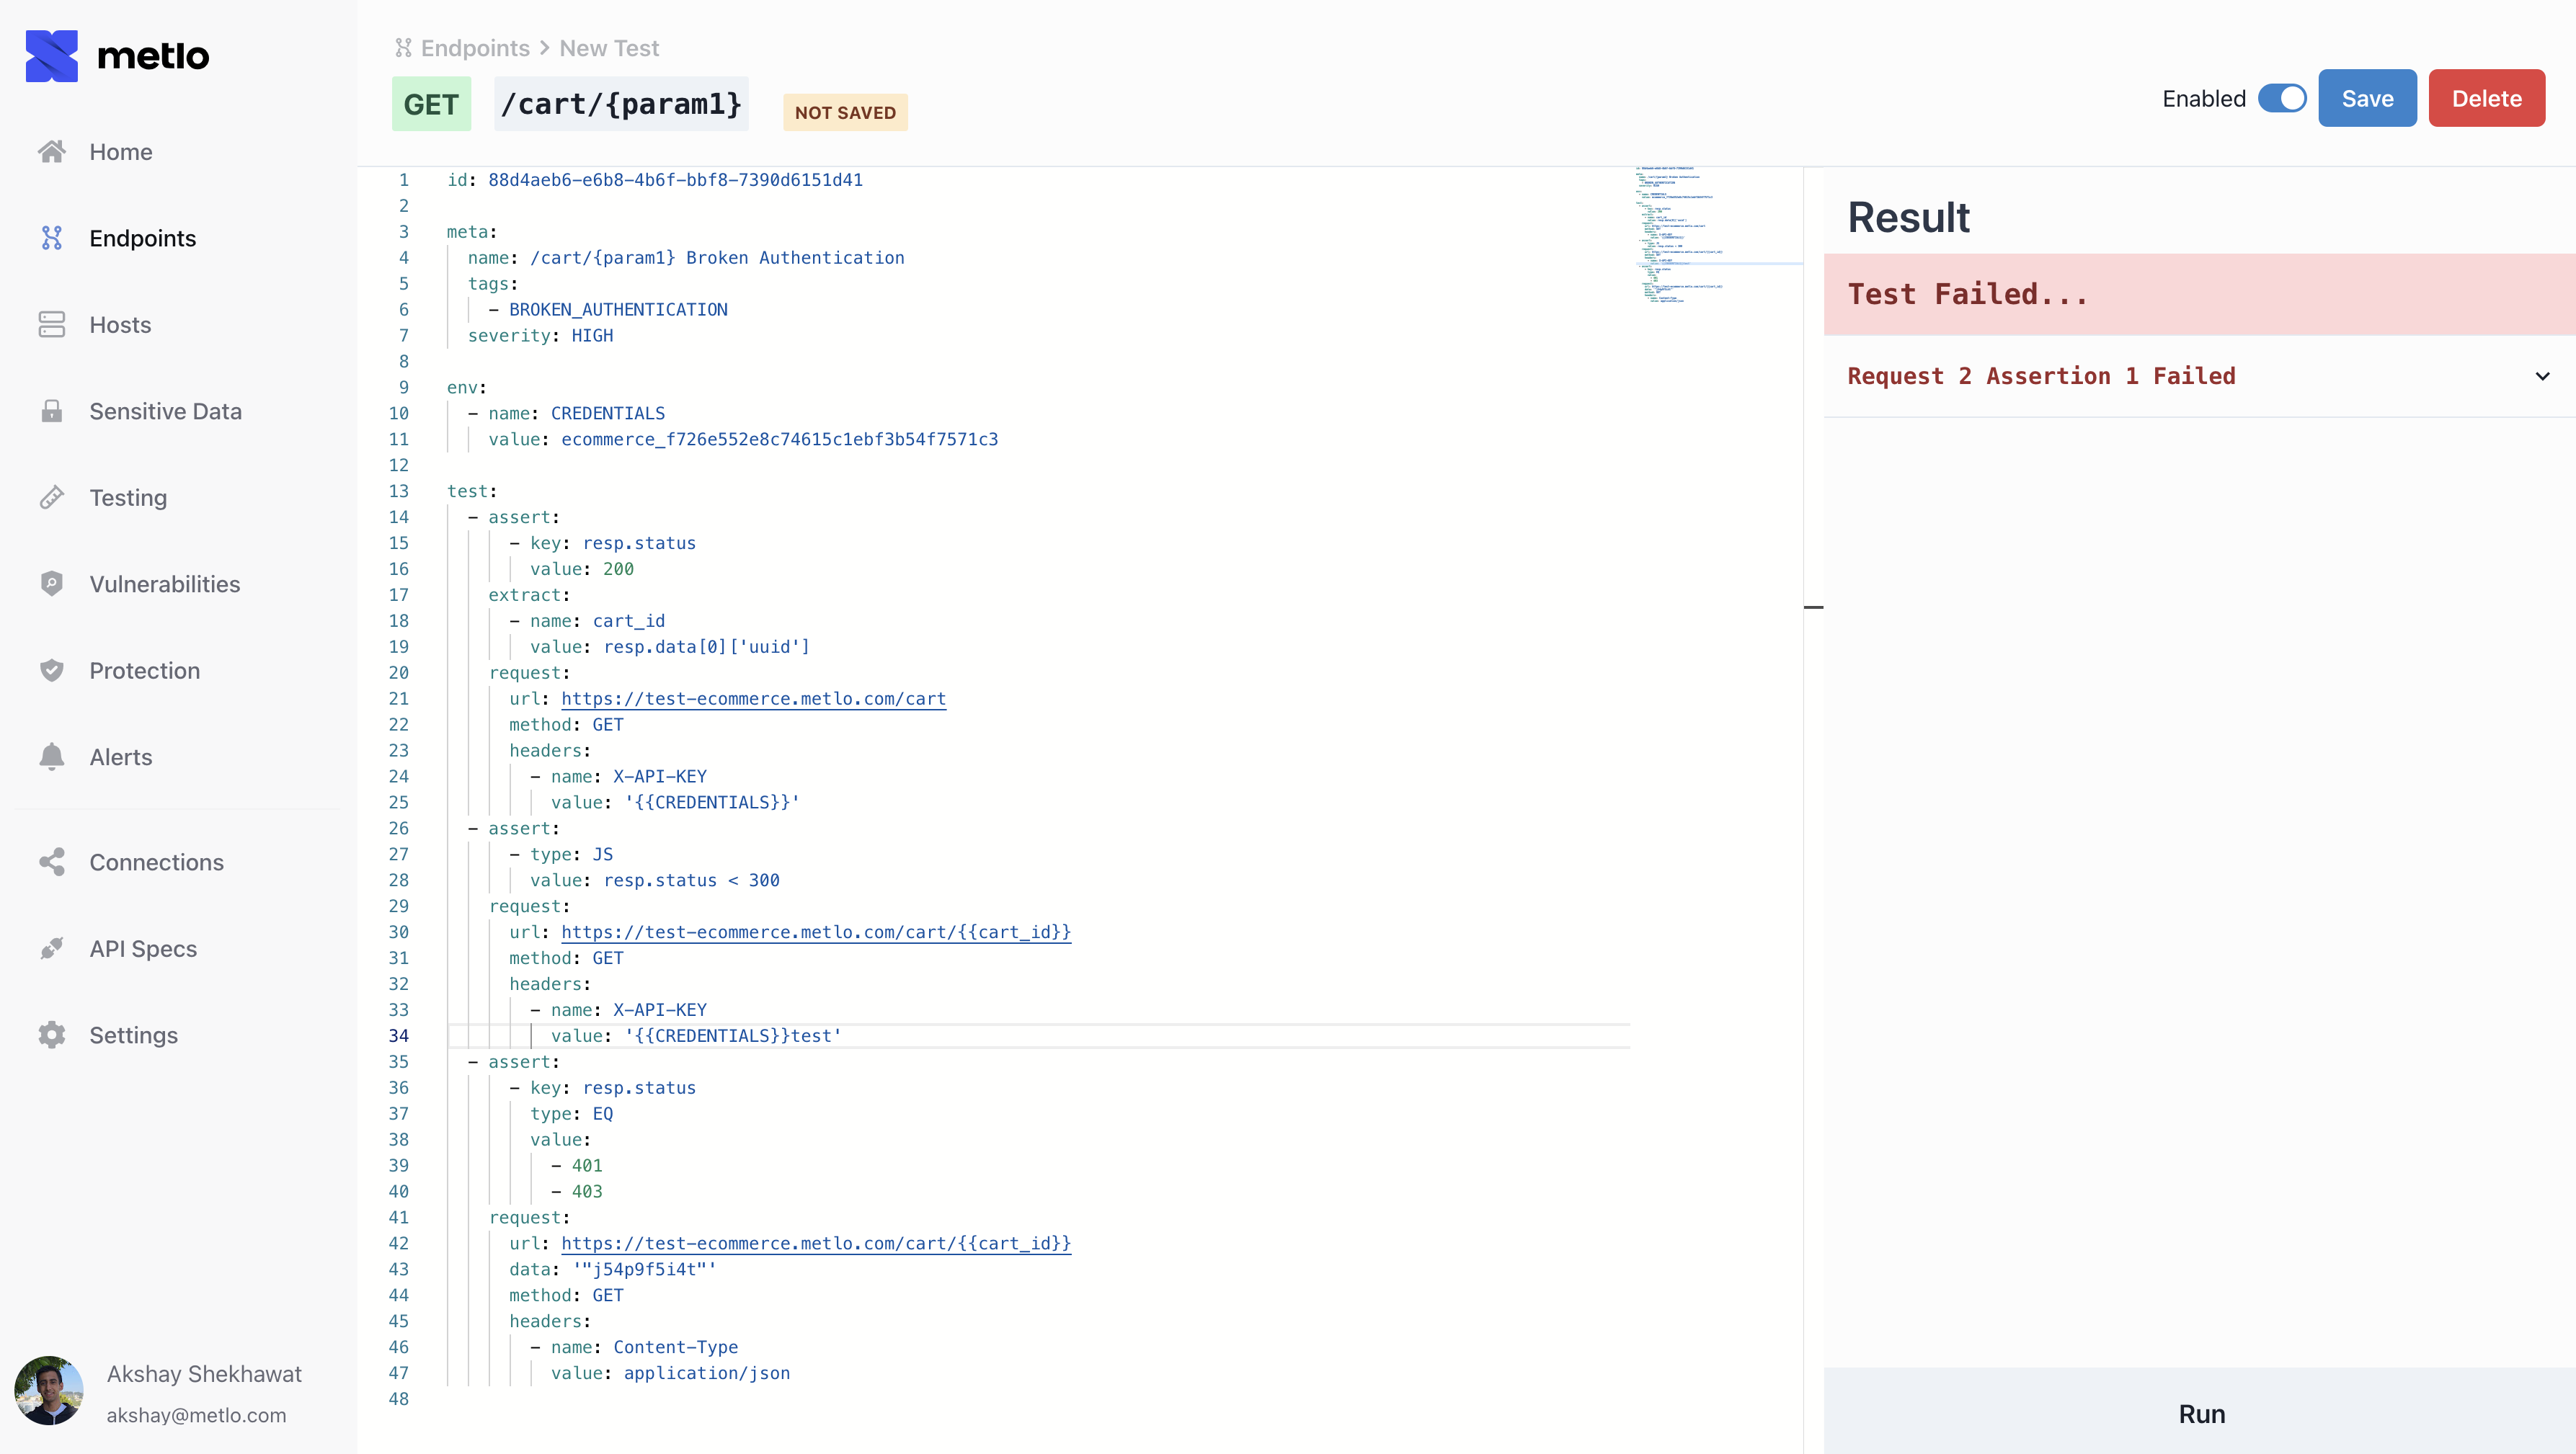 metlo-labs/metlo
Metlo is an open-source API security platform.

 momenbasel/keyfinder
Passive API key and secret discovery browser extension for Chrome and Firefox. 80+ detection patterns, zero config.